


Author: Gene Moody, Field CTO at Action1
AI can help us find vulnerabilities faster than ever. But what happens when the rest of the vulnerability management ecosystem can’t keep up?
When Vulnerability Volume Outpaces the System
In April, NIST released a statement regarding updates to NVD operations that reflects a necessary response to scale. CVE volume has grown beyond what the current enrichment model was designed to handle. As part of the change, roughly 30,000 vulnerabilities published before March 1, 2026, were reclassified as “Not Scheduled.”
Prioritization, automation, and selective processing are reasonable adjustments in principle. In practice, however, the shift introduces a set of risks that may not be fully understood, particularly for those responsible for defending enterprise environments.
The pressure is not theoretical. Action1’s 2026 Software Vulnerability Ratings Report found that disclosed vulnerabilities across the enterprise software categories analyzed increased 92% in 2025 compared with 2024. Critical and high-severity vulnerabilities increased 103% each, while vulnerabilities enabling remote code execution increased 128%.
Today, the volume of disclosures that must be validated, enriched, prioritized, and ultimately remediated is likely to place even greater pressure on systems designed for a slower era of vulnerability discovery.
The core issue is therefore not simply the existence of a backlog. Backlogs are an expected outcome in any system operating under rapid growth. The concern is how that backlog is managed and, more importantly, what signals are created by the decision to prioritize newer vulnerabilities over older, unprocessed ones.
What Happens When Enrichment Falls Behind
By focusing enrichment efforts only on recent CVEs, the system implicitly deprioritizes vulnerabilities that may already be known, confirmed, and, in some cases, actively discussed by vendors or researchers but lack full NVD context.
This creates an information asymmetry of a particularly difficult kind: partial intelligence without the second half that makes it readily actionable. Security teams that rely heavily on NVD as a normalized source of vulnerability information may see incomplete or delayed data.
Attackers, meanwhile, do not need to wait for standardized enrichment before correlating vendor advisories, security research, patch releases, exploit information, and public disclosures.
That gap matters because enrichment is not cosmetic. Structured metadata, affected-platform information, severity scoring, configuration details, and other contextual information allow defenders to determine whether a vulnerability actually applies to their environment and how urgently it should be addressed.
When that information is missing or delayed, organizations are often forced to either wait for additional context or make decisions using fragmented information. Neither outcome is ideal in a threat landscape where exploitation can move faster than internal validation and remediation processes.
But That’s Not All
There is also a second-order effect that is harder to quantify but equally important. A rolling backlog that is continuously fed while being selectively drained creates uncertainty about coverage. Without a clear commitment to processing older entries within a defined timeframe, the backlog becomes a semi-permanent condition.
Some vulnerabilities will be enriched quickly, others will remain in limbo, and there will be limited visibility into which category any given CVE falls into at a given moment.
For practitioners, this overly complicates prioritization. If affected-product information such as CPE data is incomplete or overly broad, organizations face a greater risk of false positives. Teams may spend time investigating vulnerabilities that do not apply to their environment while potentially overlooking risks that do.
Over time, this will certainly erode confidence in the dataset and push organizations to build alternative intelligence pipelines. That will lead to additional cost, tooling, and operational complexity. As well, as one may predict, increasing failure rates.
Action1’s 2026 Software Vulnerability Ratings Report found enterprise application exploitation surged 800% in the last year.
Explore which software categories saw the biggest shifts in vulnerabilities, severity, and attacker activity.
Vulnerability Management Is Changing
None of this suggests that NIST is acting irresponsibly. The scale problem is real, and the existing model was not designed for the volume of vulnerability information now entering the ecosystem.But the introduced trade-off pushes more responsibility downstream.
Organizations will need to rely less on a single authoritative source and more on correlation across multiple sources, including NVD, vendor advisories, independent vulnerability-intelligence providers, threat intelligence platforms, and internal asset inventories.
Zoom out, and the view is that vulnerability management is becoming less about consuming a curated list and more about synthesizing accurate intel from incomplete data in near real time. That requires maturity, tooling, and process discipline that not all organizations currently possess.
If this direction continues, the NVD will remain a critical component of the vulnerability-management ecosystem, but it will no longer function as a comprehensive baseline on its own. Instead, it becomes one input among many, and one that may lag significantly behind the realities of exploitation in the field.
The more important question then becomes not simply, “What vulnerabilities exist?” but “Which of them affect us, which represent the greatest risk, and how quickly can we act?”
How Defenders Should Adapt
The first lesson is that vulnerability management can no longer depend on any single source of enrichment. NVD remains enormously valuable, but security teams increasingly need to subscribe to cumulative works of vendors and organizations that aggregate the available data into usable intelligence
More importantly, collecting additional feeds is only part of the answer. More information can simply create another prioritization problem. The real objective is to turn fragmented vulnerability intelligence into a decision: Does this vulnerability affect us, how urgent is it, and what can we do about it now?
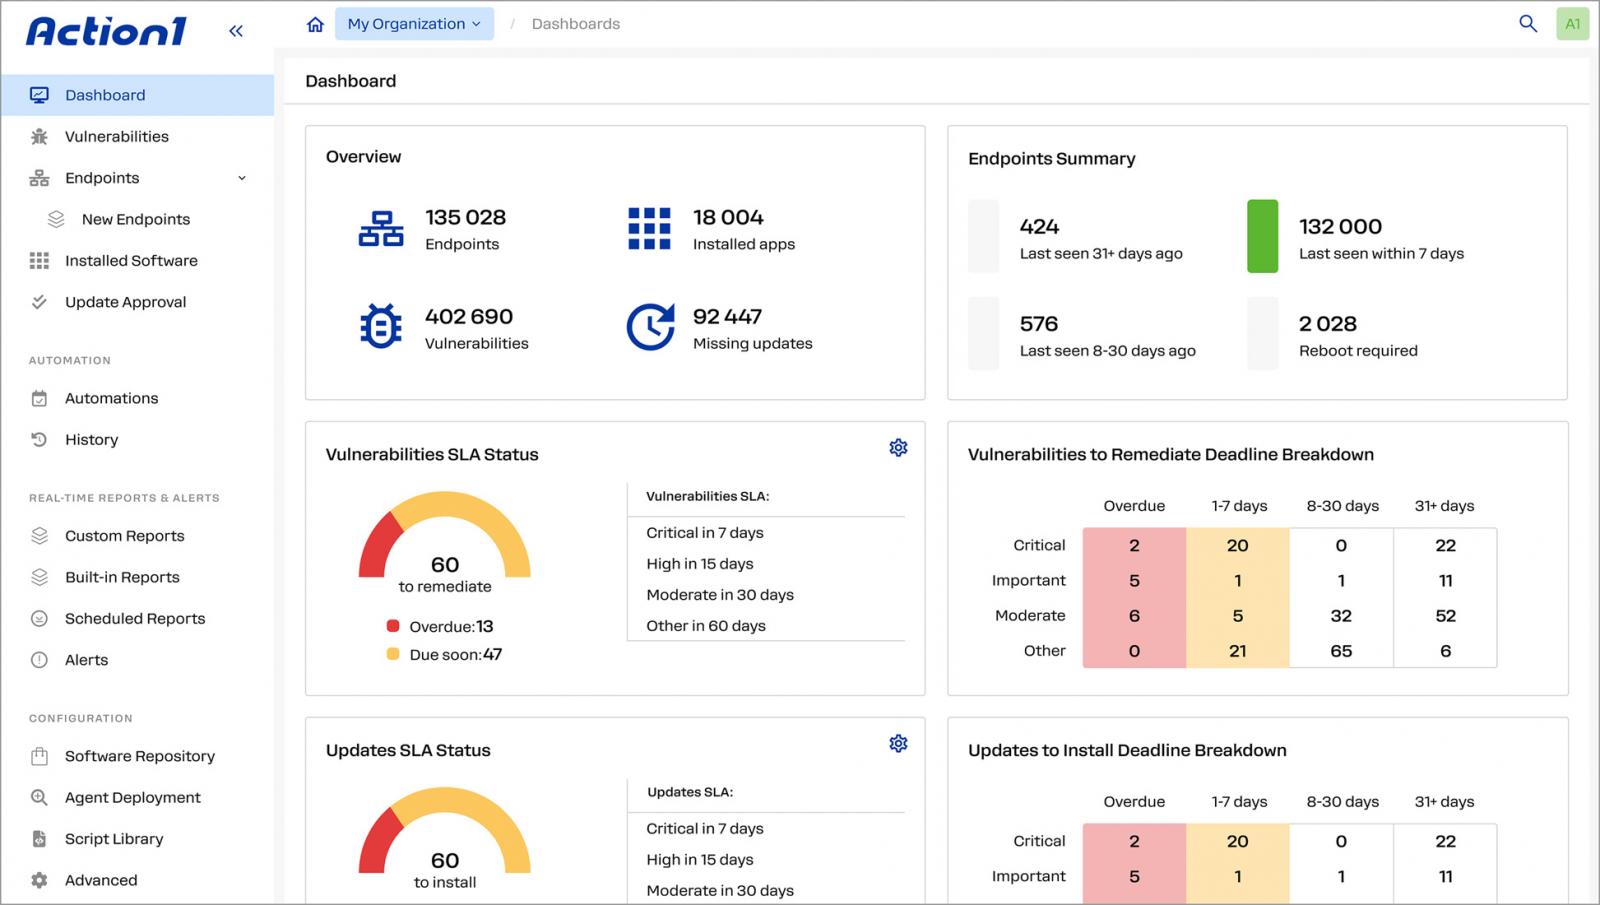
This is the model Action1 has adopted for vulnerability management. Rather than relying exclusively on NVD enrichment, Action1 combines intelligence from sources including VulnCheckNVD++, NIST NVD, CISA’s KEV Catalog, Microsoft’s own MSRC data, and vendor release notes, then scores each vulnerability based on CVE data, CVSS severity, CISA KEV status, and known usage in ransomware campaigns, providing initial prioritization in minutes.
That intelligence is correlated with real-time endpoint data so teams can determine which vulnerabilities actually affect software deployed in their environment and prioritize remediation accordingly.
Once an affected endpoint has been identified, remediation should not require another export, manual correlation exercise, or lengthy handoff before patching begins.
Action1 brings vulnerability assessment and remediation into the same workflow, allowingorganizations to move from learning that a vulnerability exists to reducing actual exposure much faster, all from a single console.
The AI vulnerability era will not be defined by how fast IT and security teams can find flaws, but by how quickly they can understand, prioritize, and patch them. Discovery is accelerating, soremediation must accelerate with it.
See how Action1 connects real-time OS and third-party vulnerability intelligence with automated remediation to help your team reduce exposure faster.
Start free and scale when you’re ready.
Sponsored and written by Action1.
