


A malware campaign dubbed ‘Midnight Mimosa’ has been discovered on low-cost Android smartphones that ship with malicious software embedded in their firmware, allowing attackers to silently install apps, perform ad fraud, and turn devices into residential proxies.
The malware is believed to have been introduced somewhere in the device supply chain, but it remains unclear who is responsible for modifying the firmware or at what stage the tampering occurred.
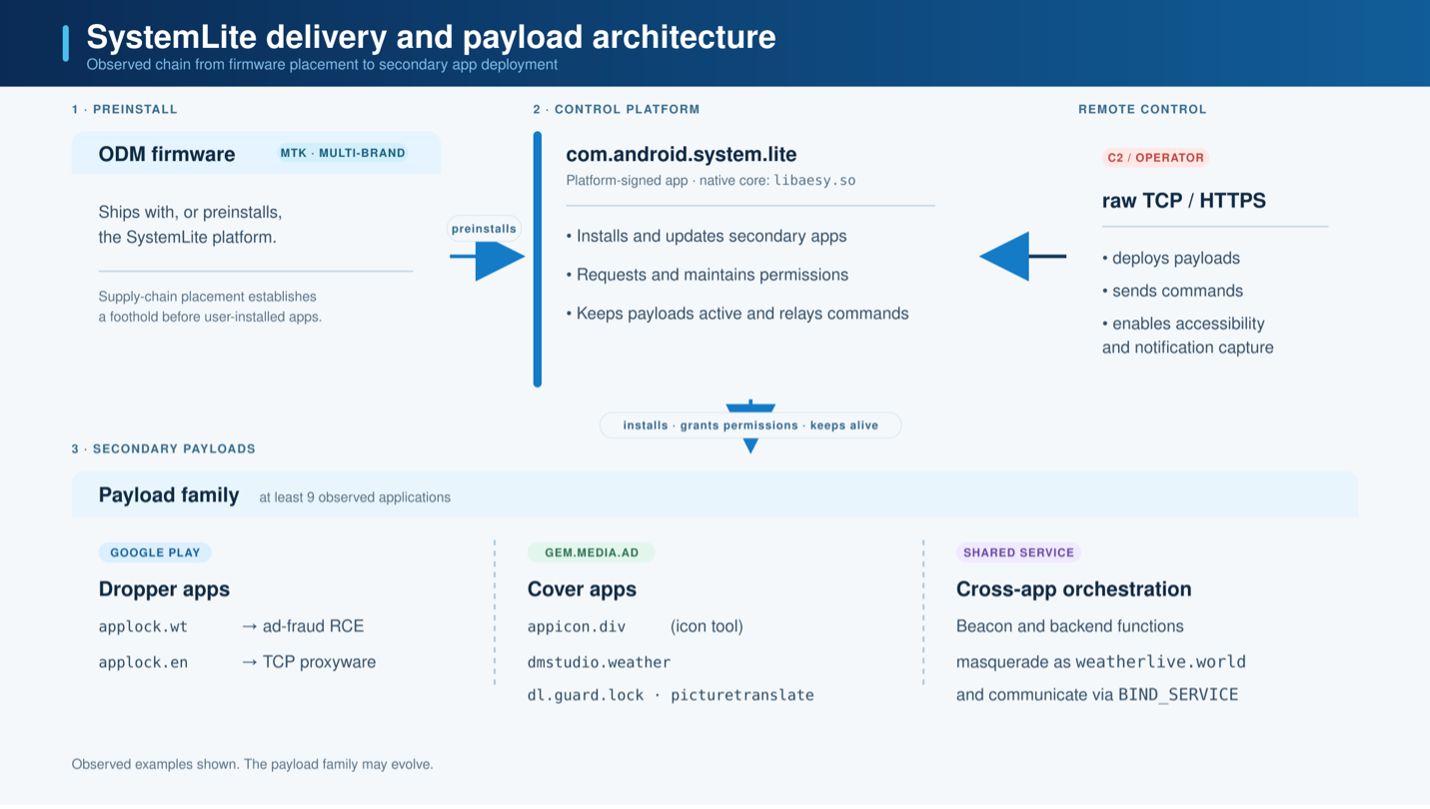
The malware is embedded directly into the firmware of low-cost Android devices using MediaTek chipsets, giving it system-level privileges that allow it to install and remove applications, grant sensitive permissions, and execute remotely downloaded code without user interaction.
According to Bitdefender researchers, the campaign affected thousands of devices across more than 150 countries over approximately two years, with the highest number of victims in Mexico, France, Italy, United States, Germany, Brazil, and Spain.
The researchers found preinstalled malware on devices with model names associated with legitimate manufacturers, including the Doogee S200 X and Cubot KINGKONG X, as well as phones impersonating Samsung and Apple products.
In an XDA forums post, owners of Cubot and Doogee smartphones reported finding suspicious applications that repeatedly reinstalled themselves after removal.
One Doogee Fire 3 Max owner also reported that an official firmware update infected the device with the malware, which disappeared after restoring an older firmware version but returned when the update was installed again.
Some users said the manufacturers released firmware updates that resolved the infections. However, the manufacturers have not publicly explained how the malicious software was introduced into the affected firmware.
Bitdefender also mentioned the XDA forum post in its report and said one of the malware packages reported by forum users, com.android.non.szcz, is part of the same malware family.
Pre-installed Android malware
Unlike typical Android malware that requires users to install a malicious application, Midnight Mimosa is already installed in the device’s system partition when customers receive their phones.
The malicious programs impersonate legitimate Android system packages, using names such as com.android.system.lite, com.android.sys.prot, and com.android.sys.gmsprot.
Because these applications are signed and run with elevated system privileges, they cannot be removed through Android’s normal application uninstall process.
Bitdefender discovered the campaign after its App Anomaly Detection technology flagged a suspicious system application named com.android.system.lite that was silently installing and removing other applications.
Further investigation determined that the application was part of a larger malware framework that downloads additional modules from command-and-control (C2) servers to perform different malicious activities.
The researchers identified approximately 32 applications distributed through the framework, including apps disguised as weather utilities, file managers, app lockers, OCR tools, and audio editors.
“The system app itself doesn’t register the fraudulent impressions and clicks,” explains Bitdefender.
“The revenue engine is driven by the dropped cover apps, including real-looking weather, app-lock, note, and OCR apps, which load genuine ads through a legitimate ad SDK. The goal is simple: to load an invisible window on top of apps that registers ads being shown.”
These applications are used to generate fraudulent advertising impressions and clicks, with some displaying advertisements in hidden windows or automatically interacting with ads without the device owner’s involvement.
The malware also employs techniques designed to evade Android’s security protections.
Before silently installing malicious applications, it temporarily disables the Google Play Store app, com.android.vending, which Bitdefender says is intended to prevent Google Play Protect from detecting the installation.
After the installation completes, the malware re-enables the Play Store to avoid raising suspicion.
Some malware variants also manipulate Android’s recorded installer information to make malicious applications appear to have been installed through Google Play, even though they were deployed directly by the malware.
The malware also includes features that turn infected Android phones into residential proxies that can relay network traffic.
Bitdefender identified a malicious application disguised as an app locker, com.mobile.applock.en, which contains a TCP proxy component that registers infected devices with a remote command server.
Once registered, the malware can be sent instructions to connect to specified hosts and forward traffic through the infected device.
This could allow attackers to route malicious traffic through the internet connections of phone owners, concealing the true origin of attacks or allowing access to devices reachable from the infected device.
Bitdefender confirmed that the proxy command-and-control infrastructure was operational and accepting device registrations.
However, during their tests, the researchers said their newly registered device did not receive any relay targets, so they could not confirm whether the attacker’s were actively forwarding traffic.
Source: Bitdefender
The researchers also discovered 13 Android applications distributed through the Google Play Store that contained the same advertising fraud code and communicated with known Midnight Mimosa infrastructure.
Unlike the preinstalled system components, these applications do not have elevated privileges needed to silently install other software.
However, they can still display advertisements outside their user interface, including when users are not using the phone.
The applications were distributed using 13 different signing certificates and at least two developer accounts, identified as fivedev and CPS Developer.
The researchers also found firmware signed using certificates associated with Chinese device manufacturer Shenzhen Zediel, but said it is unclear whether the company was involved in the malware’s campaign.
For affected consumers, removing the malware is difficult because the malware is installed as a high-privileged system application.
Bitdefender says removing the infection requires firmware-level cleanup or disabling the malicious component using Android Debug Bridge (ADB), which can be complicated for many users.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
