

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    UK’s 2 GW subsea power cable gets government’s approval

    November 2, 2026

    Profile – John Healey – BBC Sounds

    November 2, 2026

    NVIDIA Releases Auto Ontology: An Open Semantic Layer That Grounds AI Agent SQL

    November 2, 2026
    Facebook X (Twitter) Instagram
    Trending
    • UK’s 2 GW subsea power cable gets government’s approval
    • Profile – John Healey – BBC Sounds
    • NVIDIA Releases Auto Ontology: An Open Semantic Layer That Grounds AI Agent SQL
    • Ivanti patches two more Connect Secure zero-days chained in attacks
    • Hurricane Damage to a Florida Domestic Violence Shelter Shows Climate’s Stress on Vulnerable Groups
    • These midterms could effectively end the Trump era – but neither side is yet ready for what comes next | Nesrine Malik
    • Cambridge scientist Marta Shahbazi dies in Spanish train crash
    • Burnham declines to say net migration still too high as Mahmood prepares to unveil tougher settlement rules – UK politics live | Politics
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Monday, November 2
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Ivanti patches two more Connect Secure zero-days chained in attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKNovember 2, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ivanti released security updates to patch two more Connect Secure (ICS) remote access gateway flaws that have been chained in zero-day attacks since at least October 1.

    Threat actors exploited these two flaws (tracked as CVE-2026-111357 and CVE-2026-118527) alongside an authentication bypass vulnerability (CVE-2026-104935), which Ivanti patched last month to remove the main attack surface.

    CVE-2026-111357 is a high-severity privilege escalation flaw, and CVE-2026-118527 lets authenticated attackers upload files on an unpatched device.

    image

    When it released patches for CVE-2026-104935 in October, Ivanti urged admins to upgrade as soon as possible since it was aware of “limited exploitation in the wild.”

    “At the time of discovery of exploitation, Ivanti had a fix developed for CVE-2026-104935 which was already in QA for supported versions, and we made the decision to not delay getting a fix to customers that resolved the primary exploitation path when the LPE was discovered,” Ivanti added in an advisory updated on Thursday.

    “Because of this, our focus was initially centered on the disclosure of CVE-2026-104935 and providing protection for our customers as quickly as possible.”

    Cybersecurity firm Volexity, which found the flaw, reported at the time that a threat actor (UTA0576) was chaining the CVE-2026-104935 vulnerability since at least October 3 with two other flaws to gain unauthenticated root-level code execution on fully patched ICS devices.

    “Notably, UTA0576 deployed no malware or web shell. Instead, the threat actor re-exploited the device for every command it ran and tampered with logs to cover its tracks, evading Ivanti’s Integrity Checker Tool,” Volexity said.

    Threat intelligence firm Defused also confirmed Volexity’s report, saying that it spotted the first signs of active CVE-2026-104935 exploitation starting October 1.

    On Tuesday, the US Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-104935 to its catalog of actively exploited vulnerabilities and ordered federal agencies to patch their systems by Friday,

    Internet threat watchdog Shadowserver now tracks over 5,000 Internet-exposed ICS instances, but there is no information on how many have already been secured against ongoing attacks.
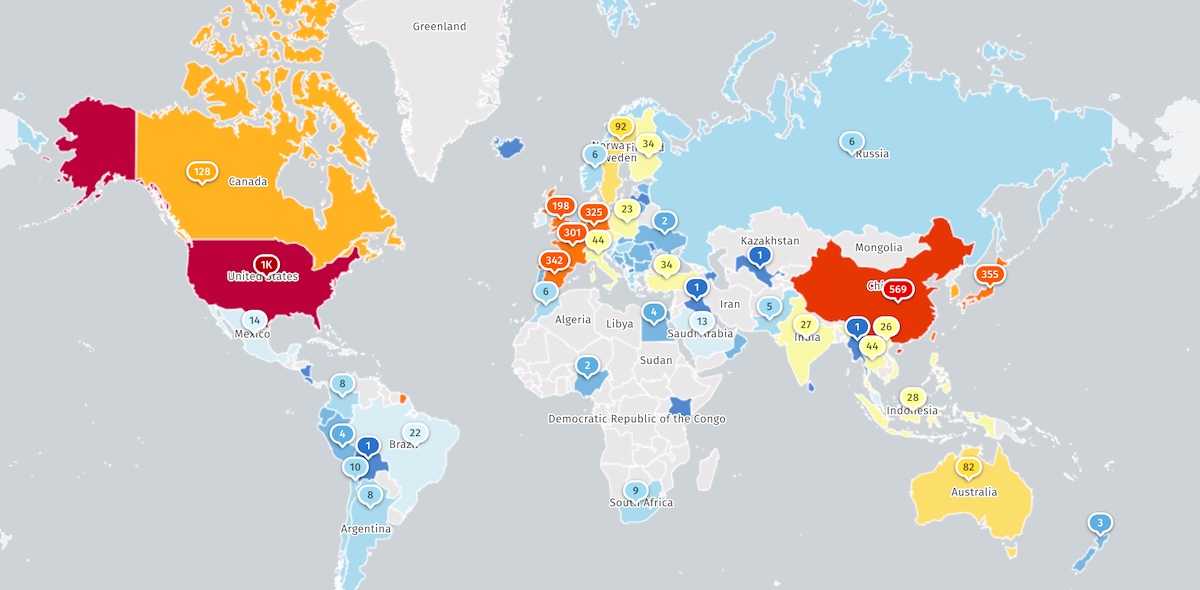
    Ivanti ICS instances exposed on the Internet
    Internet-exposed Ivanti ICS instances (Shadowserver)

    ​​Threat actors frequently target Ivanti vulnerabilities, often in zero-day attacks, because they provide a quick way into enterprise networks to steal sensitive corporate and customer data.

    Over the past several years, Ivanti has patched several other Connect Secure zero-days exploited in the wild, some of them chained in widespread attacks to deploy malware.

    It addressed a command injection (CVE-2024-21887) and an authentication bypass (CVE-2023-46805) in early January 2024, and a server-side request forgery (CVE-2024-21893) two weeks later.

    More recently, Ivanti has fixed a remote code execution (RCE) bug (CVE-2025-0282) in January 2025 and a second RCE flaw (CVE-2025-22457) exploited by China-linked state hackers since at least mid-March 2025.

    Ivanti has over 3,000 employees, a network of more than 7,000 partners, and over 40,000 customers using its IT asset management solutions worldwide.

    Since November 2021, CISA has flagged 38 Ivanti vulnerabilities as actively exploited in the wild, including 12 that have also been abused in ransomware attacks.


    article image

    Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.

    See what’s getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.

    Start your free email security scan.

    attacks Chained connect Ivanti Patches secure ZeroDays
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    FBI Flags Over 600 Addresses Tied to North Korea’s Binance Heist

    Ivanti Patches Two More Zero-Days Exploited in Connect Secure Attack Chain

    New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value

    FBI links $6.3 billion Binance crypto heist to North Korean hackers

    Alpine Linux rebuilds GitLab after attempted RCE attack

    OpenAI says it’s doubling Pro usage limits and bringing Work features to Chat

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    UK’s 2 GW subsea power cable gets government’s approval

    November 2, 2026

    Profile – John Healey – BBC Sounds

    November 2, 2026

    NVIDIA Releases Auto Ontology: An Open Semantic Layer That Grounds AI Agent SQL

    November 2, 2026

    Ivanti patches two more Connect Secure zero-days chained in attacks

    November 2, 2026
    Latest Posts

    Kog is going deeper to squeeze more inference out of GPUs

    August 17, 2026

    More women will die if domestic abusers leave prison early, victim’s parents warn | Domestic violence

    August 17, 2026

    Nothing less than radical whole-system change is required to fix the NHS’s maternity services | Julia Sanders

    August 17, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    UK’s 2 GW subsea power cable gets government’s approval

    November 2, 2026

    Profile – John Healey – BBC Sounds

    November 2, 2026

    NVIDIA Releases Auto Ontology: An Open Semantic Layer That Grounds AI Agent SQL

    November 2, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.