

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Russia arrests minor after US embassy warns of ‘credible threat of a mass casualty event’

    November 1, 2026

    Alpine Linux rebuilds GitLab after attempted RCE attack

    November 1, 2026

    Scientists discover a surprising brain benefit of eating peanuts every day

    November 1, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Russia arrests minor after US embassy warns of ‘credible threat of a mass casualty event’
    • Alpine Linux rebuilds GitLab after attempted RCE attack
    • Scientists discover a surprising brain benefit of eating peanuts every day
    • Radiologists warn cancer patients ‘deteriorating’ amid staff shortages
    • Russian strikes leave thousands without power in Ukraine, says Zelenskyy – POLITICO
    • Green party must avoid being taken over by hard left, says former leader | Green party
    • Kärcher boss: Less regulation, more action to get Europe and Germany fit again
    • Green Party at a “crossroads”, says former co-leader Adrian Ramsay
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Sunday, November 1
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Alpine Linux rebuilds GitLab after attempted RCE attack

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKNovember 1, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Hackers attempted to exploit a critical GitLab vulnerability in Alpine Linux’s development infrastructure on October 20–21, prompting the open-source project to rebuild its GitLab server and reset all passwords over concerns of a possible compromise.

    The attacks targeted CVE-2026-97229, a maximum-severity remote code execution flaw, repeatedly crashing GitLab processes, with some attempts coming close to succeeding.

    Although Alpine Linux found no evidence that attackers executed code or tampered with its software packages and releases, it could not rule out a successful compromise due to missing logs and a lack of outbound connection records.
    image

    “Because we cannot rule out code execution, and the evidence we would need to confirm it no longer exists, we took the harder route and rebuilt the GitLab instance from scratch,” explained the Alpine Linux team.

    Alpine Linux is a small, lightweight operating system widely used as the foundation for Docker container images that run applications and services.

    Their GitLab instance hosts development repositories, code reviews, and CI jobs, including the “aports” build recipes used to produce Alpine’s software packages.

    That makes it a valuable supply chain target, as tampering with their GitLab environment could affect downstream software.

    CVE-2026-97229 is a maximum-severity integer overflow vulnerability in GitLab’s CI/CD regular expression compiler Onigmo, bundled in Ruby, that could allow unauthenticated attackers to execute arbitrary code on the server.

    GitLab disclosed the flaw and made fixes available on October 12, warning that attackers can trigger it under certain conditions by submitting a specially crafted regular expression in a CI/CD pipeline configuration.

    Alpine initially installed GitLab 19.3.4 instead of the patched version, 19.3.5. A later upgrade to 19.3.6 also failed to close the flaw because the fix required a patch to Ruby, which GitLab bundled with its official packages but Alpine’s custom container image did not include.

    On October 20-21, the attacker submitted malicious CI configurations targeting the flaw, causing eight worker crashes; four were partially successful, though none seemed to go all the way.

    The Alpine Linux team found that the attackers downloaded its GitLab container image, suggesting they may have been preparing a supply-chain attack.

    After investigating, Alpine found no tampering in the repository commits, packages, or releases up to October 27. Also, no signing keys could have been exposed, as those aren’t stored on the GitLab server.
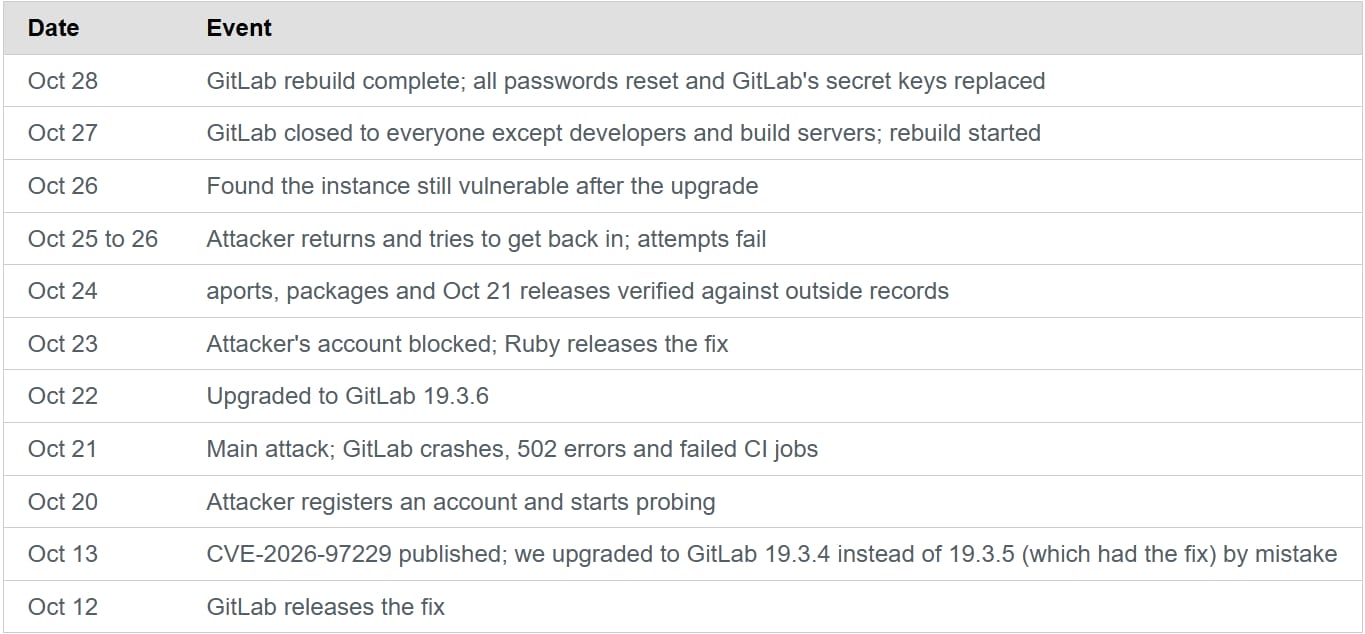
    Incident timeline
    Incident timeline

    Source: Alpine Linux

    If exploitation succeeded, potentially exposed information includes user details, password hashes, 2FA secrets, CI/CD secrets, integration credentials, and private project content, though no compromise of the above has been confirmed.

    Alpine advises users to reset their GitLab passwords and pull the alpinelinux/gitlab:19.3.6 image published on October 27, which contains Ruby 3.3.13 and addresses CVE-2026-97229.

    article image

    Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.

    See what’s getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.

    Start your free email security scan.

    alpine attack attempted GitLab Linux RCE rebuilds
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    OpenAI says it’s doubling Pro usage limits and bringing Work features to Chat

    Northstar Security Exits Stealth With $7M to Expose Toxic Risk Combinations

    Russia says ‘massive’ drone attack targeted ‘industrial enterprise’ amid reports oil refinery hit

    NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection

    FBI Links North Korea’s TraderTraitor to Record $6.43 Billion Binance Crypto Heist

    CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Russia arrests minor after US embassy warns of ‘credible threat of a mass casualty event’

    November 1, 2026

    Alpine Linux rebuilds GitLab after attempted RCE attack

    November 1, 2026

    Scientists discover a surprising brain benefit of eating peanuts every day

    November 1, 2026

    Radiologists warn cancer patients ‘deteriorating’ amid staff shortages

    November 1, 2026
    Latest Posts

    Kog is going deeper to squeeze more inference out of GPUs

    August 17, 2026

    More women will die if domestic abusers leave prison early, victim’s parents warn | Domestic violence

    August 17, 2026

    Nothing less than radical whole-system change is required to fix the NHS’s maternity services | Julia Sanders

    August 17, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Russia arrests minor after US embassy warns of ‘credible threat of a mass casualty event’

    November 1, 2026

    Alpine Linux rebuilds GitLab after attempted RCE attack

    November 1, 2026

    Scientists discover a surprising brain benefit of eating peanuts every day

    November 1, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.