

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Extractive industries threaten global goal to protect 30% of nature by 2030, report finds

    October 21, 2026

    A plan to ensure energy is affordable for all | Energy bills

    October 21, 2026

    Jeffrey Donaldson investigated over alleged rape in UK parliament | Northern Ireland

    October 21, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Extractive industries threaten global goal to protect 30% of nature by 2030, report finds
    • A plan to ensure energy is affordable for all | Energy bills
    • Jeffrey Donaldson investigated over alleged rape in UK parliament | Northern Ireland
    • Gas go-ahead ignites oily response from Trump, while speaker seems ready to blow | John Crace
    • Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
    • Tracks Along the Longest Drive on Another World
    • Pope does not need further treatment after lung cancer surgery
    • The Guardian view on the Republicans’ midterms struggle: Trump has circuses, but voters also want bread | US midterm elections 2026
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, October 21
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Chrome Web Store extensions caught stealing crypto, browser data

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 30, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Multiple extensions for Google Chrome and Microsoft Edge delivered a malware framework that deployed modules to steal cryptocurrency, sensitive data, and browser history, and to inject ClickFix lures.

    Researchers say all 16 malicious modules uncovered in the campaign serve distinct purposes and are designed to be “highly extensible.”

    The operation was uncovered by application security company Socket, and the investigation indicates that it may have been active since early 2024.
    image

    Socket says that when initially published on the Chrome Web Store, many of the extensions provided the advertised functionality and contained no malware.

    According to the researchers, five of the extensions were acquired from their original creators and injected with malware via updates delivered automatically.

    One example is the “Enable Right Click & Copy — Smart Unlock + OCR” extension, the only one in the campaign available for both Chrome and Edge, which had a Chrome user base of at least 70,000 when it turned malicious. The number of installs on Edge was 10,000 at the time.

    Google caught the threat early and removed the extension from its add-ons marketplace, but at the time of Socket publishing its report, the Edge version remained available.
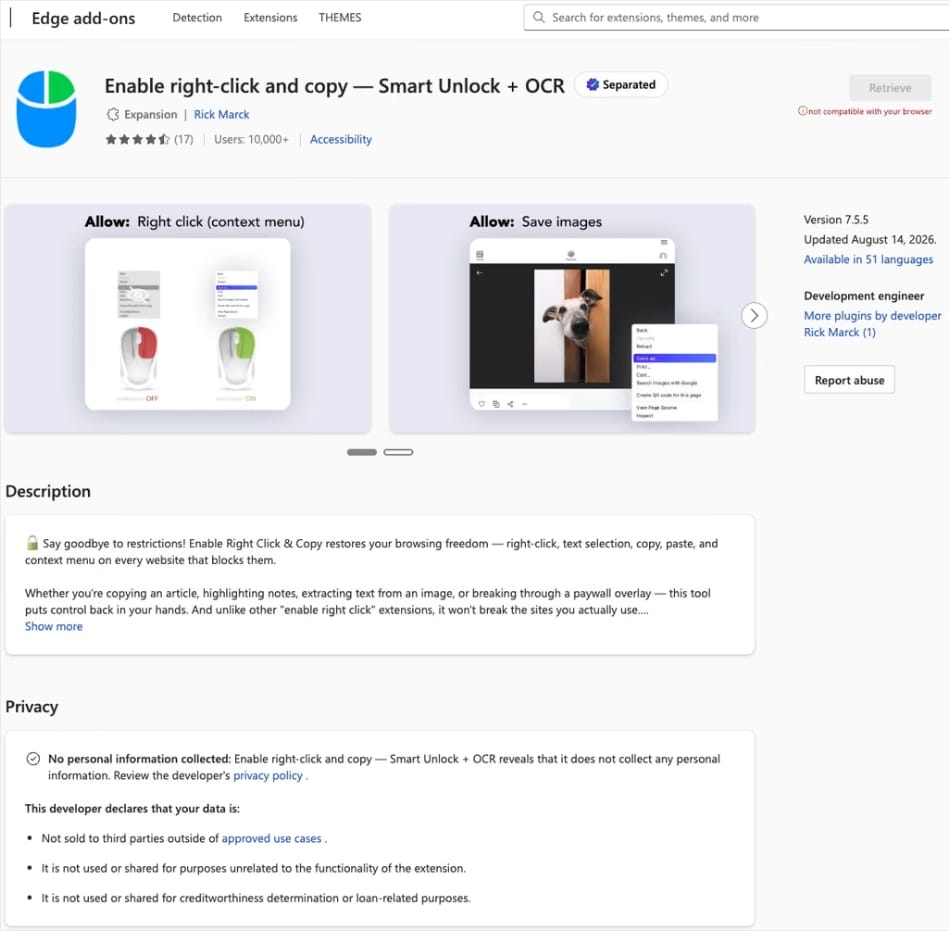
    Malicious extensions available on the Edge add-ons store
    Malicious extensions available on the Edge add-ons store
    Source: Socket

    Once installed, the malware establishes an encrypted WebSocket connection with command-and-control (C2) servers, downloads JavaScript modules, removes Content Security Policy (CSP) headers from every website visited, and injects malicious scripts into websites through hidden HTML elements.

    Socket observed malware modules with the following capabilities:

    • Draining EVM, Solana, and Tron wallets by hijacking legitimate “Connect Wallet” and “Swap” buttons
    • Replacing Ledger and Trezor websites with convincing seed-phrase phishing pages
    • Stealing sessions, tokens, account data, and balances from Coinbase, Binance, Kraken, OKX, MEXC, KuCoin, Bybit, and MetaMask
    • Recording credentials and form entries across websites
    • Harvesting Facebook and LinkedIn account information
    • Exfiltrating browser history
    • Displaying ClickFix-style fake browser updates that instruct victims to execute attacker-provided commands
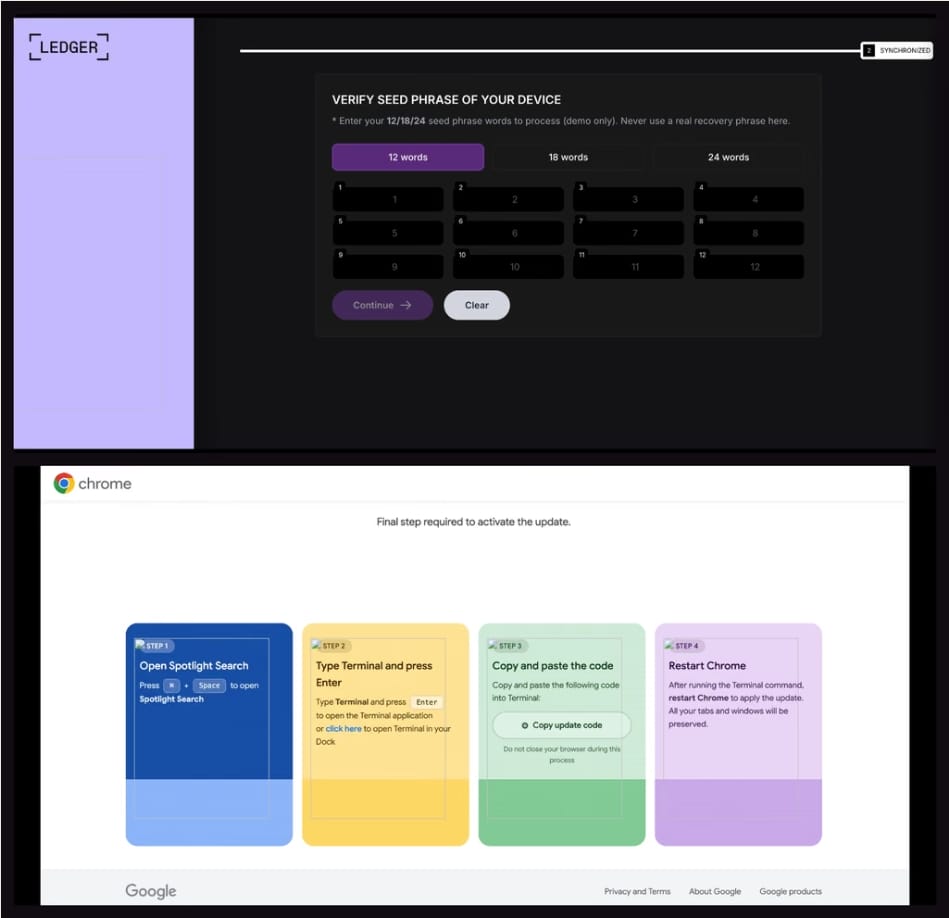
    Wallet seed theft page
    Crypto wallet seed theft page
    Source: Socket

    Socket warns that the malicious framework may have more modules and that as the malware evolves over time, new payloads are expected to be deployed.

    At the time of publishing, none of the malicious extensions are available in the Chrome Web Store.

    Socket’s report provides the full list of extension IDs uncovered in the campaign along with the domains used for C2 communication.

    Users who had any of the extensions installed should assume that their credentials have been compromised and change their login passwords.

    Cryptocurrency holders potentially impacted by this campaign are recommended to move their assets to a newly created wallet as soon as possible.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    browser caught Chrome Crypto data extensions stealing Store Web
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases

    CISA: Hackers chain Plex flaws in Plex2Shell attacks to breach servers

    Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections

    Optiv Launches CyberBOT Cybersecurity Awareness Training Program

    PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge

    14 ways attackers abuse cloud services to hack your enterprise

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Extractive industries threaten global goal to protect 30% of nature by 2030, report finds

    October 21, 2026

    A plan to ensure energy is affordable for all | Energy bills

    October 21, 2026

    Jeffrey Donaldson investigated over alleged rape in UK parliament | Northern Ireland

    October 21, 2026

    Gas go-ahead ignites oily response from Trump, while speaker seems ready to blow | John Crace

    October 21, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Extractive industries threaten global goal to protect 30% of nature by 2030, report finds

    October 21, 2026

    A plan to ensure energy is affordable for all | Energy bills

    October 21, 2026

    Jeffrey Donaldson investigated over alleged rape in UK parliament | Northern Ireland

    October 21, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.