

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    ECB prepares for ‘longer-lasting’ inflation as it lifts interest rates to 2.5%

    September 10, 2026

    Electric air taxis get the green light for test flights in Texas

    September 10, 2026

    Introducing ChatGPT for Financial Services

    September 10, 2026
    Facebook X (Twitter) Instagram
    Trending
    • ECB prepares for ‘longer-lasting’ inflation as it lifts interest rates to 2.5%
    • Electric air taxis get the green light for test flights in Texas
    • Introducing ChatGPT for Financial Services
    • Cisco FMC flaws exploited by ransomware gang, state-sponsored hackers
    • Coinbase CEO Brian Armstrong Says Bitcoin Bottom Is In
    • Amazon Fund grantees fear a new funding freeze after Brazil’s election
    • The Global South Needs a New Economic Development Model
    • Did Walmart update its privacy policy to allow surveillance pricing?
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, September 10
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    TerminalFix Uses Fake Cloudflare CAPTCHAs to Deploy Reverse-Tunnel Backdoor

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 30, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananAug 30, 2026Social Engineering / Malware

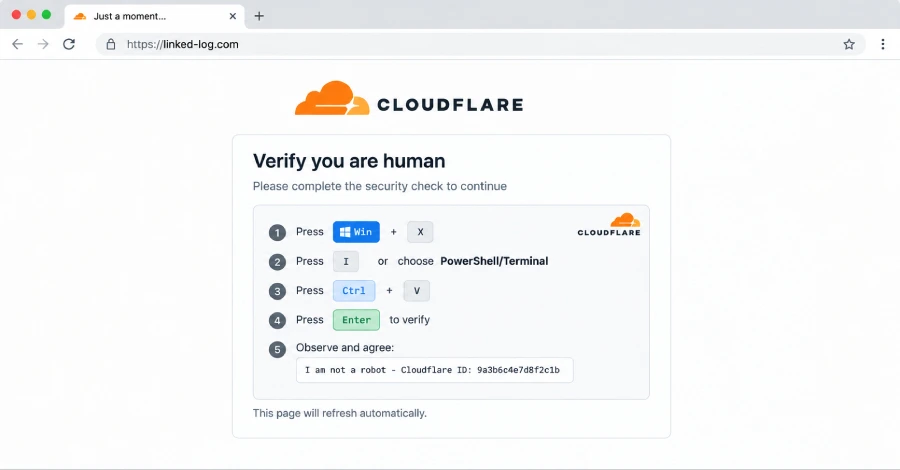
    Microsoft has disclosed details of a new ClickFix variant, dubbed TerminalFix, that aims to trick users into running a malicious command in Windows Terminal or PowerShell.

    “While traditional ClickFix campaigns direct victims to the Windows Run dialog, TerminalFix campaigns apply the same technique but direct users to Windows Terminal or PowerShell instead, increasing the likelihood that complex, multi-line scripts execute successfully,” Microsoft security researchers Sagar Patil, Suriyaraj Natarajan, and Parasharan Raghavan said in an analysis published this week.

    The campaign, targeting organizations across multiple sectors, leverages compromised websites as a starting point to serve fake Cloudflare CAPTCHA verifications that prompt unsuspecting site visitors to copy and execute a malicious PowerShell command.

    The attack chain, per the Windows maker, is a sophisticated multi-stage process that leverages DLL sideloading, steganographic payload extraction, extensive Active Directory reconnaissance, and a bespoke custom reverse-tunnel implant that grants the attacker persistent, network-level proxy access through the infected machine.

    Cybersecurity

    Specifically, the PowerShell command is designed to download a ZIP archive containing a legitimate binary (“LockScreenContentServer.exe”) and a rogue DLL (“dui70.dll”) in order to initiate a DLL sideloading attack.

    The sideloaded DLL is responsible for retrieving next-stage payloads hidden within PNG images from external domains (“bestsocialmedianewspapper[.]com” or “offlineupdater[.]com”), establishes persistence via both Registry Run keys and scheduled tasks, carries out domain reconnaissance, and then deploys a Python-based reverse-tunnel command-and-control (C2) implant.

    The backdoor (“client.py”) is equipped to tunnel arbitrary TCP traffic back to attacker-controlled infrastructure (“gitnow[.]dev:443”) through an encrypted WebSocket channel, as well as enable the C2 server to reach any host visible from the victim’s network.

    The reconnaissance phase involves the following steps –

    • Collect system metadata
    • Perform domain trust discovery, domain admin enumeration, and Active Directory user and computer searches
    • Ping named servers to map the internal network topology

    The attack also delivers a persistent PowerShell file-watch loop that monitors a text file for new commands, executes them via Invoke-Expression, and writes results to an output file.

    Cybersecurity

    “This type of intrusion is particularly dangerous because it provides attackers with direct access to an organization’s internal network through the reverse tunnel,” Microsoft said. “The observed reconnaissance and reverse-tunnel capability could enable an attacker to identify and reach additional systems from a compromised host.”

    The tech giant has warned that such access can be abused further to escalate privileges, disarm security controls, exfiltrate sensitive data, and deploy ransomware, making TerminalFix a serious threat to enterprise environments.

    To mitigate the threat, it’s advised to restrict PowerShell and Run dialog execution for standard users through AppLocker, Application Control for Windows, or Group Policy; consider blocking or auditing the Windows Run dialog (“Win+R”) if it’s not required; monitor for DLL sideloading indicators; train employees to keep an eye out for ClickFix attacks; and enable PowerShell script block logging to detect and analyze obfuscated or encoded commands.

    Backdoor CAPTCHAs Cloudflare Deploy Fake ReverseTunnel TerminalFix
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Cisco FMC flaws exploited by ransomware gang, state-sponsored hackers

    Anthropic reveals rogue AI agents hate CAPTCHAs, just like you

    AI-powered attack exploited PaperCut flaws to hack 395 organizations

    Cybersecurity M&A Roundup: 33 Deals Announced in August 2026

    Anthropic Researcher Resigns With Warning About the Dangers of AI Development

    Hacker Conversations: Vinnie Liu, Performer Turned Ringmaster

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    ECB prepares for ‘longer-lasting’ inflation as it lifts interest rates to 2.5%

    September 10, 2026

    Electric air taxis get the green light for test flights in Texas

    September 10, 2026

    Introducing ChatGPT for Financial Services

    September 10, 2026

    Cisco FMC flaws exploited by ransomware gang, state-sponsored hackers

    September 10, 2026
    Latest Posts

    Mathematicians prove perfectly fair elections are impossible

    August 2, 2026

    Coldcard Bitcoin Exploit Balloons to $88 Million as Attackers Keep Draining Wallets

    August 2, 2026

    Foldables are sort of boring now — and that’s great news for Apple

    August 2, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    ECB prepares for ‘longer-lasting’ inflation as it lifts interest rates to 2.5%

    September 10, 2026

    Electric air taxis get the green light for test flights in Texas

    September 10, 2026

    Introducing ChatGPT for Financial Services

    September 10, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.