


Threat actors associated with Aurora (aka Aur0ra) ransomware have been observed using SpaceX’s artificial intelligence (AI)-powered coding assistant Cursor to break into target networks, according to findings from CloudSEK and Gambit Security.
The two independent analyses are based on exposed infrastructure associated with the Russian-speaking cybercrime group, leading to the discovery of its toolkit, shell history, and encryptor. CloudSEK said the exposed open directory leaked “months of activity” that was active against more than 20 organizations across nine countries between April and July 2026. Four of those victims have since been listed on its data leak site.
“The operator used Cursor, an agentic coding assistant, to plan attacks in Russian, while excluding CIS [Commonwealth of Independent States] ranges and CIS-country domains, without exception,” CloudSEK noted.
Details about Aurora first emerged in late May 2026, with CYFIRMA highlighting attacks primarily targeting Windows systems and its continued technical development through incremental updates and feature expansion. Data from Ransomware.Live lists 33 victims located in the U.S., Germany, the Netherlands, Canada, and the U.K.
In one case detailed by Black Hills Information Security earlier this month, initial access was achieved via aggressive email bombing followed by making phone calls to employees by posing as IT help desk personnel to assist them in dealing with the issue, only to establish remote access using an open-source utility called Xray-core.
The attack chain subsequently involves lateral movement via SMB, LDAP, WinRM, RDP, and RPC, obtaining access to high-privilege administrator accounts, and abusing them to evade detection by clearing logs and disabling Microsoft Defender before harvesting and exfiltrating sensitive data and deploying the encryptor.

CloudSEK said it identified both Windows and Linux versions of Aurora written in Zig, adding the operator’s recovered chat history shows heavy use of Cursor for planning various phases of the attack. This includes a full Active Directory Certificate Services (AD CS) exploitation plan written in Russian.
“Both encryptor binaries, the Windows sap.exe and the Linux/ESXi encrypt.out, are static builds from a single Zig codebase, compiled for different targets rather than written twice,” the company noted. “The Windows binary even carries the Linux build’s usage examples inside it, a leftover from sharing one source tree across both platforms.”
The Windows variant is also equipped to inhibit system recovery through the deletion of volume shadow copies and disabling System Restore directly via the Registry. The Linux and ESXi variant, on the other hand, attempts to forcefully kill every single virtual machine on the host prior to starting encryption.
Furthermore, a key recovered from the Aurora encryptor is said to have granted access to a ransom negotiation between the threat actor and an unspecified victim, and a cluster of four cryptocurrency wallets that show varying splits between affiliates and the main operators. Affiliates have been found to get a cut anywhere between 54% and 79%, while the rest goes to the administrators.
This indicates that the affiliate cut of the ransom amount is decided per victim and depends on the ransom amount demanded and the victim’s revenue figures. The illicit funds and then laundered and cashed out.

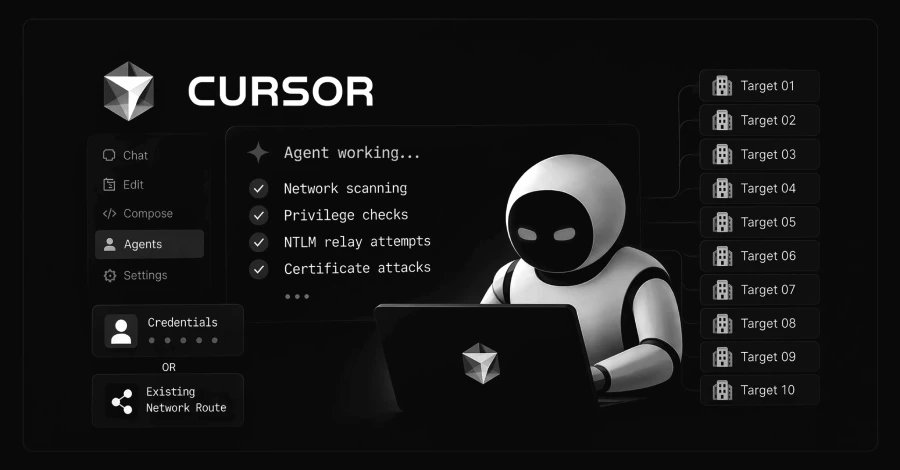
Gambit Security, which released its own insights into the activity, said it observed the Aurora operator using Cursor Agent, running Anthropic’s Claude Sonnet, to help with hands-on exploitation against 10 targets between April 8 and May 21, 2026.
“In these cases the agent was given credentials or an existing route into the victim organization,” Eyal Sela, director of threat intelligence at Gambit Security, said. “Then it was tasked with various exploitation activities.”
“The agent was tasked with standard exploitation tasks. In some cases, the attacker only asked the agent to achieve an objective, such as ‘tell me what rights the user has,’ while in others, they told the agent which exploitation tool to use or instructed it to follow a previously generated attack plan. In some cases, the Agent gave a list of potential next steps – and all the attacker did was reply with a number corresponding to one of them.”
Some of the tasks offloaded to the agent are listed below –
- Installing a VPN client or proxychains, then configuring it and connecting to a victim with supplied credentials or an existing SOCKS tunnel
- Scanning the internal subnets for hosts with Nmap or NetExec
- Enumerating the domain to report which privileges a supplied user holds, using NetExec’s BloodHound collector
Attempting NTLM relay attacks by coercing authentication with PetitPotam, Coerce Plus, and PrinterBug, and using Impacket ntlmrelayx to relay the resulting authentication
Running certificate attacks with Certipy
“The majority of the commands failed to achieve the stated objective on the first attempt, resulting in multiple refinements and changes to the commands and scripts used for each task,” Gambit said. “Some eventually succeeded in achieving the objective, while others failed and returned only a report of the attempts to the attacker.”
In addition, attacks involving the Linux version have leveraged a Python script (“esxi_finder.py”) to scan for VMware ESXi hypervisors and vCenter servers inside a victim network.
The development is the latest example of how bad actors are relying on commercial AI tools to carry out cyber attacks, even as model providers implement more guardrails to prevent misuse. The names of the affected companies were not disclosed, but Reuters said they were Christeyns, Teckentrup, Helideck Certification Agency, Bayou Title, an Argentine pharmaceutical distributor, and an Italian manufacturer.
Gryxa Toolkit Emerges
It also follows the discovery of a new AI-assisted toolkit dubbed Gryxa that’s used by a financially motivated threat actor to run an initial-access operation targeting 324 hosts. ReliaQuest said Gryxa represents the first case it has observed where AI has been used to build the entire operation, right from the toolkit to the console it’s run from.
“Gryxa turns legitimate remote monitoring and management (RMM) software into covert access, keeps the access alive through several restart mechanisms that operate independently of each other, and then steals credentials saved in Chromium-based browsers,” it said.
“It also escalates against endpoint protection when the connection to the actor is interrupted, disabling or attempting to uninstall the security agent. Together, these capabilities give the actor durable access to a host and allow them to steal cryptocurrency wallets.”

Evidence indicates that the threat actor behind the operation jailbroke an AI coding agent by passing off the whole development process as an “authorized internal deployment.” Gryxa is likely delivered via phishing emails.
Once executed on a compromised host, it sets up persistence using scheduled tasks and can bypass Chromium’s app-bound encryption (ABE) protections to steal credentials from web browsers. The harvested credentials are transmitted through Telegram.
Perhaps the most unusual aspect of Gryxa is that it records remediation efforts and reports them back to the threat actor. Specifically, after the visible RMM implant is removed, a hidden malware component collects Windows logs and host artifacts and uploads them to attacker-controlled infrastructure.
On top of that, if the actor’s relay becomes unreachable, Gryxa attempts to disable and uninstall any endpoint protection agents like Microsoft Defender and others within roughly 10-13 minutes. Once the relay is accessible, the toolkit re-enables Defender.
“The Gryxa component only gathered and uploaded; it didn’t examine what it took,” ReliaQuest said. “The actor draws any conclusion about which tool performed the removal, which account ran it, and in what order after receiving the archive.”
“The actor’s console includes a ready-made job named collect-forensics, which indicates this is a routine capability rather than a response to one incident. Gryxa rotates its log files when they exceed 200KB, meaning recent activity is preserved for a responder who acts quickly.”
