

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Dads are dying after their kids are born, and almost no one is tracking it

    October 8, 2026

    Mum blamed for baby’s death at Telford hospital calls for change in NHS

    October 8, 2026

    Invading the globe: Bird flu now threatens Australia and Oceania

    October 8, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Dads are dying after their kids are born, and almost no one is tracking it
    • Mum blamed for baby’s death at Telford hospital calls for change in NHS
    • Invading the globe: Bird flu now threatens Australia and Oceania
    • Here’s what connects the Cornell alleged rape case to those before: accused men not being held to serious account | Emma Brockes
    • Most UK diplomats to leave East Jerusalem consulate, Israel says, as Miliband says ‘vital services’ to remain
    • Polanski’s final pitch in Holborn by-election: I’ll keep Burnham honest – POLITICO
    • British consulate in East Jerusalem will stay open as UK mission, says Ed Miliband | Foreign policy
    • Interview with Corriere della Sera
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 8
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 8, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananOct 08, 2026Artificial Intelligence / Cloud Security

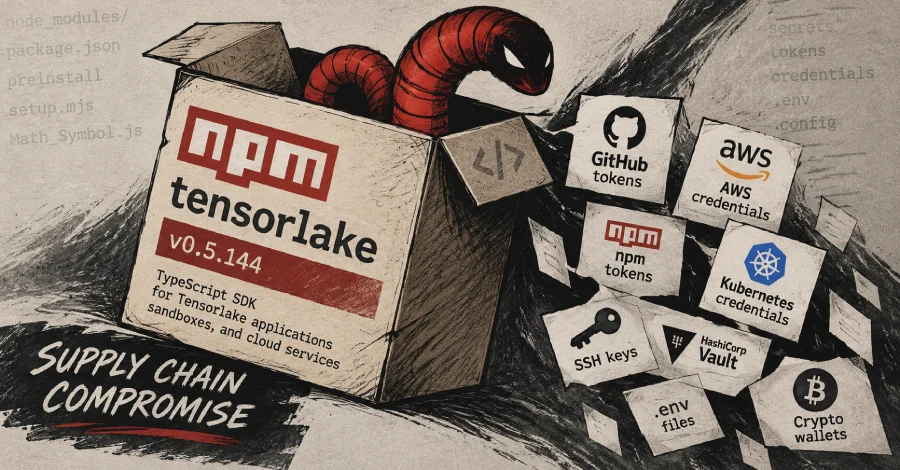
    The npm package known as “tensorlake,” a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack.

    The malicious version 0.5.144 “contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes remotely supplied code,” Socket said. Version 0.5.144 is no longer available for download from the npm package registry.

    An analysis of the compromised release shows that it contains a preinstall hook designed to launch a JavaScript file (“package/lib/setup.mjs”), an obfuscated loader that launches the main credential-stealing and self-propagating worm (“package/lib/Math_Symbol.js”) using the Bun runtime.

    The stealer malware is designed to harvest credentials across local files, CI environments, Kubernetes, and Vault sources. It also drops the HackBrowserData binary, exfiltrates the collected data, establishes persistence on the host, and facilitates the execution of remotely-supplied code.

    Cybersecurity

    “That combination extends the risk beyond a single stolen API key,” Socket said. “Any secrets accessible to the executing process may be exposed, and persistence can retain attacker access after the affected dependency is removed.”

    The types of data stolen by the malware are below –

    • npm tokens
    • GitHub tokens
    • Amazon Web Services (AWS) credentials and secrets
    • HashiCorp Vault
    • Kubernetes credentials
    • SSH keys
    • .env files
    • Cryptocurrency wallets
    • Messaging app data
    • Configuration and MCP files associated with Anthropic Claude, Cursor, Kiro, Windsurf, and Zed

    “To propagate, the worm enumerates packages associated with the victim’s publishing identity, builds Sigstore provenance, and republishes compromised versions,” Socket explained. “Strings referencing a fake Copilot/Dependabot workflow suggest it also plants GitHub Actions workflows.”

    The malware also makes use of an Ethereum contract to resolve its command-and-control (C2) endpoint (“iseekaigogo[.]com”), with GitHub acting as a fallback mechanism to stage the encrypted stolen data in a public repository with the description “Shai-Hulud: Here We Go Again.”

    In addition, there exists a “hostage token” component that uses a PowerShell monitor to repeatedly poll “api.github.com/user” using the stolen GitHub token to check if the token is valid. Should the victim take steps to revoke the token, the monitor proceeds to execute an attacker-supplied handler through the “Invoke-Expression” cmdlet to execute PowerShell code designed to likely trigger a destructive routine – a tactic observed in earlier Shai-Hulud waves.

    According to StepSecurity, the malicious files were pushed to the main branch of tensorlakeai/tensorlake under a maintainer’s name, after which the package was released from that same repository. The first rogue commit took place on October 7, 2026, at 01:20 a.m. UTC. A day later, the repository’s release workflow published 0.5.144 to npm

    Cybersecurity

    “The malware also writes .claude/settings.json and .vscode/tasks.json files into repos it can reach, so it runs again when someone opens the project in Claude Code or VS Code,” StepSecurity’s Ashish Kurmi said.

    ChainDrop was first documented in early August 2026 in connection with the compromise of hundreds of npm packages, including Keyv and Cacheable, that were found to contain a Mini Shai-Hulud variant with a self-propagating credential-stealing worm delivered through an obfuscated Bun-based JavaScript payload.

    The development extends the supply chain attack to artificial intelligence (AI) agent infrastructure, once again highlighting how threat actors are increasingly targeting AI tools and services to extract valuable data from enterprises. Users who have installed the malicious version are advised to remove it immediately and rotate their credentials.

    Compromised CredentialStealing deliver npm package ShaiHulud Tensorlake Worm
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Hackers hijack Google domains after breaching ccTLD registries

    FBI Warns FortiBleed Remains Active After Amassing 86,644 Fortinet Device Credentials

    PoeLLM Malware Infects 3,400+ Servers to Expand Crypto Mining Botnet

    Unpatched Critical LMCache Flaw Lets Unauthenticated Attackers Run Code Remotely

    SonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Appliances

    Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealer

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Dads are dying after their kids are born, and almost no one is tracking it

    October 8, 2026

    Mum blamed for baby’s death at Telford hospital calls for change in NHS

    October 8, 2026

    Invading the globe: Bird flu now threatens Australia and Oceania

    October 8, 2026

    Here’s what connects the Cornell alleged rape case to those before: accused men not being held to serious account | Emma Brockes

    October 8, 2026
    Latest Posts

    British national shot dead in Kashmir by Pakistani security forces | Kashmir

    August 10, 2026

    Climate change doubled likelihood of Canada’s extreme fire weather, study finds

    August 10, 2026

    Scientists say just 7 days of meditation can rewire your brain

    August 10, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Dads are dying after their kids are born, and almost no one is tracking it

    October 8, 2026

    Mum blamed for baby’s death at Telford hospital calls for change in NHS

    October 8, 2026

    Invading the globe: Bird flu now threatens Australia and Oceania

    October 8, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.