


In July, South Korea’s government-backed startup support platform, Modu-ui Changup (모두의창업), suffered a data breach. The incident later revealed a critical encryption key management failure, demonstrating how encrypted data can still become exposed when organizations fail to protect encryption keys properly.
The platform supports a nationwide startup audition program overseen by South Korea’s Ministry of SMEs and Startups (MSS), and it stores participants’ personal information, including startup ideas, email addresses, and names.
One month before the reported data breach, concerns had already been raised that applicants’ personal information could be structured and exposed through API responses within the platform. The government stated that it took immediate action. However, it did not disclose whether it had improved the platform’s underlying security architecture.
On June 18, the Ministry of SMEs and Startups announced that personal information and summaries of startup ideas had been leaked. It subsequently launched a detailed investigation together with the National Intelligence Service, the Cyber Security Center, and the National Police Agency.
On July 31, authorities confirmed that the decisive cause of the personal information and startup idea leak was the exposure of an encryption key through an API.
How the Data Breach Occurred
The leaked data had already been encrypted. However, encrypted data requires an encryption key for decryption.
In this incident, the encryption key was exposed together with the API data, resulting in the disclosure of email addresses, evaluation comments, and startup idea summaries belonging to about 5,000 successful applicants.
The Ministry of SMEs and Startups explained that the encryption key had been included within the API. According to the ministry, an external party collected API data through methods such as web crawling, which led to the exposure of the key.
In particular, email addresses configured as private were not visible on the public-facing interface. Nevertheless, investigators determined that they could be obtained through AI-based web crawling.
This case also illustrates the risks of hard-coding encryption keys as fixed values within application code, configuration files, databases, or similar environments.
When organizations use this approach, the keys themselves can become exposed along with the systems or data they are supposed to protect. In other words, the fundamental cause of this incident can be viewed as a security architecture that failed to incorporate proper encryption key management.
Authorities identified 39 IP addresses involved in accessing the leaked information, all of which originated in South Korea. They also stated that investigations were continuing into further details, including possible connections to AI solution providers.
As in this case, when an encryption key becomes externally exposed, simply revoking the compromised key and issuing a new one is not enough. Organizations must also re-encrypt all existing data protected by the compromised key and analyze key access logs to determine the full scope of the breach.
In addition, they need to reassess access permissions across APIs, servers, and internal storage systems. They must also notify affected data subjects and implement continuous monitoring.
Once an encryption key is compromised, organizations may have to invest substantial time and resources to redesign their security architecture.
Powered by 30 years of expertise, D.AMO delivers complete data protection and bulletproof key management.
D.AMO DSP offers encryption, key management, and control center as a single platform.
Why Encryption Key Management Matters
As the South Korean government startup platform breach demonstrates, encryption alone provides little meaningful protection if an organization does not separate encryption keys from the data they protect. Without secure encryption key management, encrypted information remains exposed.
If an encryption key is compromised, an attacker may gain the ability to access data within the system in real time. Furthermore, the attacker may be able to impersonate legitimate users and gain control over the system. The effectiveness of data encryption directly depends on the security of its key management.
For encryption to provide genuine protection, organizations should store encryption keys in a dedicated Key Management System (KMS) that remains physically or logically separated from databases and applications.
Applications should request access to a key from the KMS only when they need to read or process protected data. They should not store the key themselves.
Encryption is also essential for meeting regulatory requirements such as the GDPR, Cyber Resilience Act (CRA), and HIPAA. However, inadequate key management can allow encrypted data to be decrypted immediately after a key is compromised, undermining the effectiveness of encryption and preventing organizations from achieving the intended level of regulatory compliance.
Therefore, organizations seeking to meet global security and compliance requirements should consider cybersecurity solutions from specialized vendors such as Penta Security, which has extensive expertise in both encryption and encryption key management.
D.AMO Key Management: Effective Protection For 30 Years
D.AMO, Penta Security’s data security platform, provides encryption-based data protection together with secure key management and access control, backed by nearly 30 years of cybersecurity expertise. D.AMO provides integrated encryption, access control, backup, and recovery capabilities across an organization’s entire infrastructure, including both on-premises and cloud environments.
Penta Security’s Data Security Platform has been deployed by more than 10,000 customers across industries including finance, government, and the private sector. Its extensive deployment history and technical expertise demonstrate the reliability of the platform.
In addition, D.AMO can apply NIST-standardized post-quantum cryptography (PQC) algorithms to key management, helping organizations prepare their data security architecture for the quantum computing era.
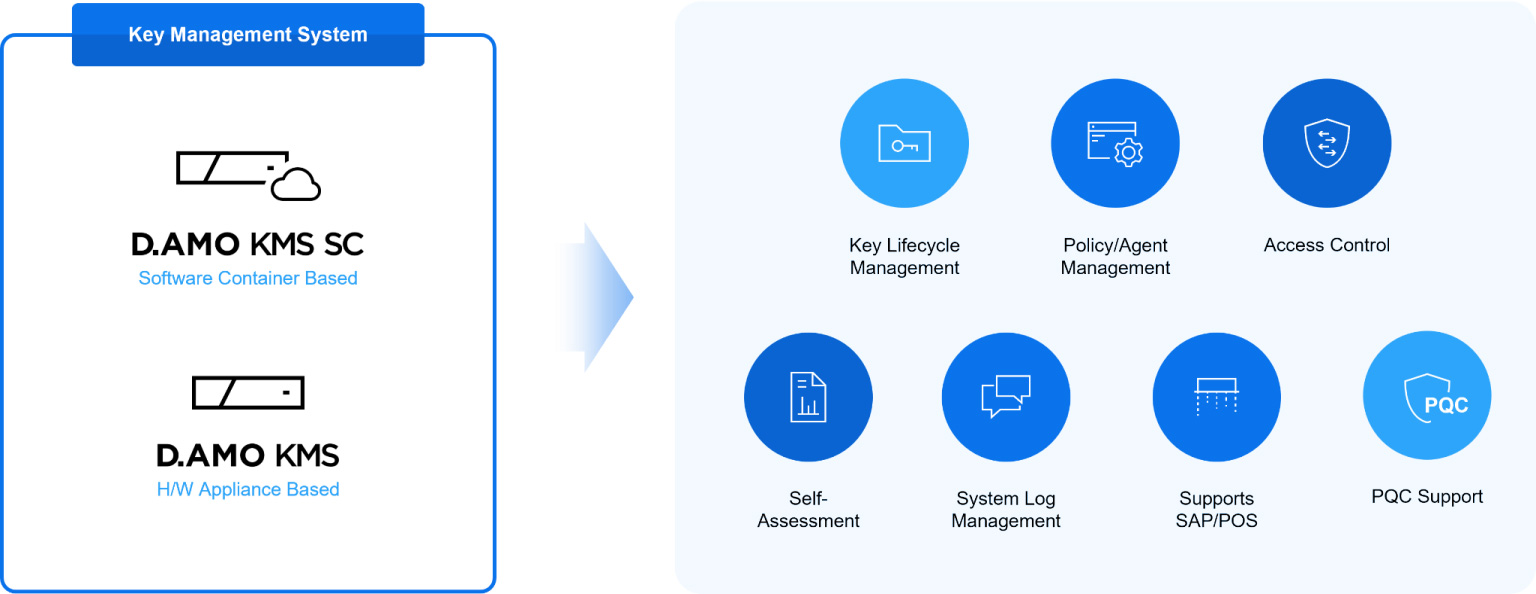
The D.AMO Key Management System (D.AMO KMS) physically and logically separates encryption and decryption keys from the data they protect.
Moreover, it manages the entire key lifecycle and performs log integrity checks, enabling organizations to quickly investigate key-related activity when a security incident occurs.
If D.AMO had been implemented on the South Korean government startup platform, the data breach caused by inadequate encryption key management could have been prevented.
Enterprises and public institutions need to shift their approach to data security from post-incident response to proactive prevention. Most importantly, they should protect sensitive data with both strong encryption and secure, centralized encryption key management.
Learn more about Penta Security DSP: D.AMO
Sponsored and written by Penta Security.
