



Security researchers developed an attack that lets hackers with privileged access register a rogue external MFA provider that steals users’ passwords during legitimate login attempts.
The technique, dubbed TrustSink by Varonis Threat Labs, can work with any provider that relies on this external authentication model, though the researchers demonstrated the attack using Microsoft Entra.
Microsoft Entra supports external MFA providers, which allow organizations to use third-party authentication services to satisfy multifactor authentication requests.
According to Microsoft, when a user signs in with a first factor, such as a password, Entra can redirect them to an external MFA provider to complete the required second factor.
If the provider returns a valid signed token indicating that the second factor was completed, Entra considers the MFA requirement satisfied.
Varonis found that an attacker who has already compromised a highly privileged Entra account can register a rogue External Authentication Method (EAM) as one of these external MFA providers and use it to insert a convincing Microsoft password prompt into the legitimate authentication flow.
The fake prompt captures the user’s password in plaintext before the malicious provider returns a valid signed token to Entra, causing the login to complete without displaying an error.
“In our test tenant, every sign-in completed normally while our server received passwords with timestamps and source IP addresses,” explains Varonis.
“Resetting a captured password did not remove the rogue provider. It remained in the authentication flow and captured the replacement password at the user’s next sign-in.”
It is important to note that TrustSink is not an initial-access attack and requires an attacker to already control a highly privileged Entra account.
Abusing an external MFA provider
TrustSink abuses the trust Microsoft places in a configured external MFA provider.
Varonis created a malicious provider that appeared to Entra as a legitimate external MFA provider but displayed a copy of Microsoft’s password page to the user.
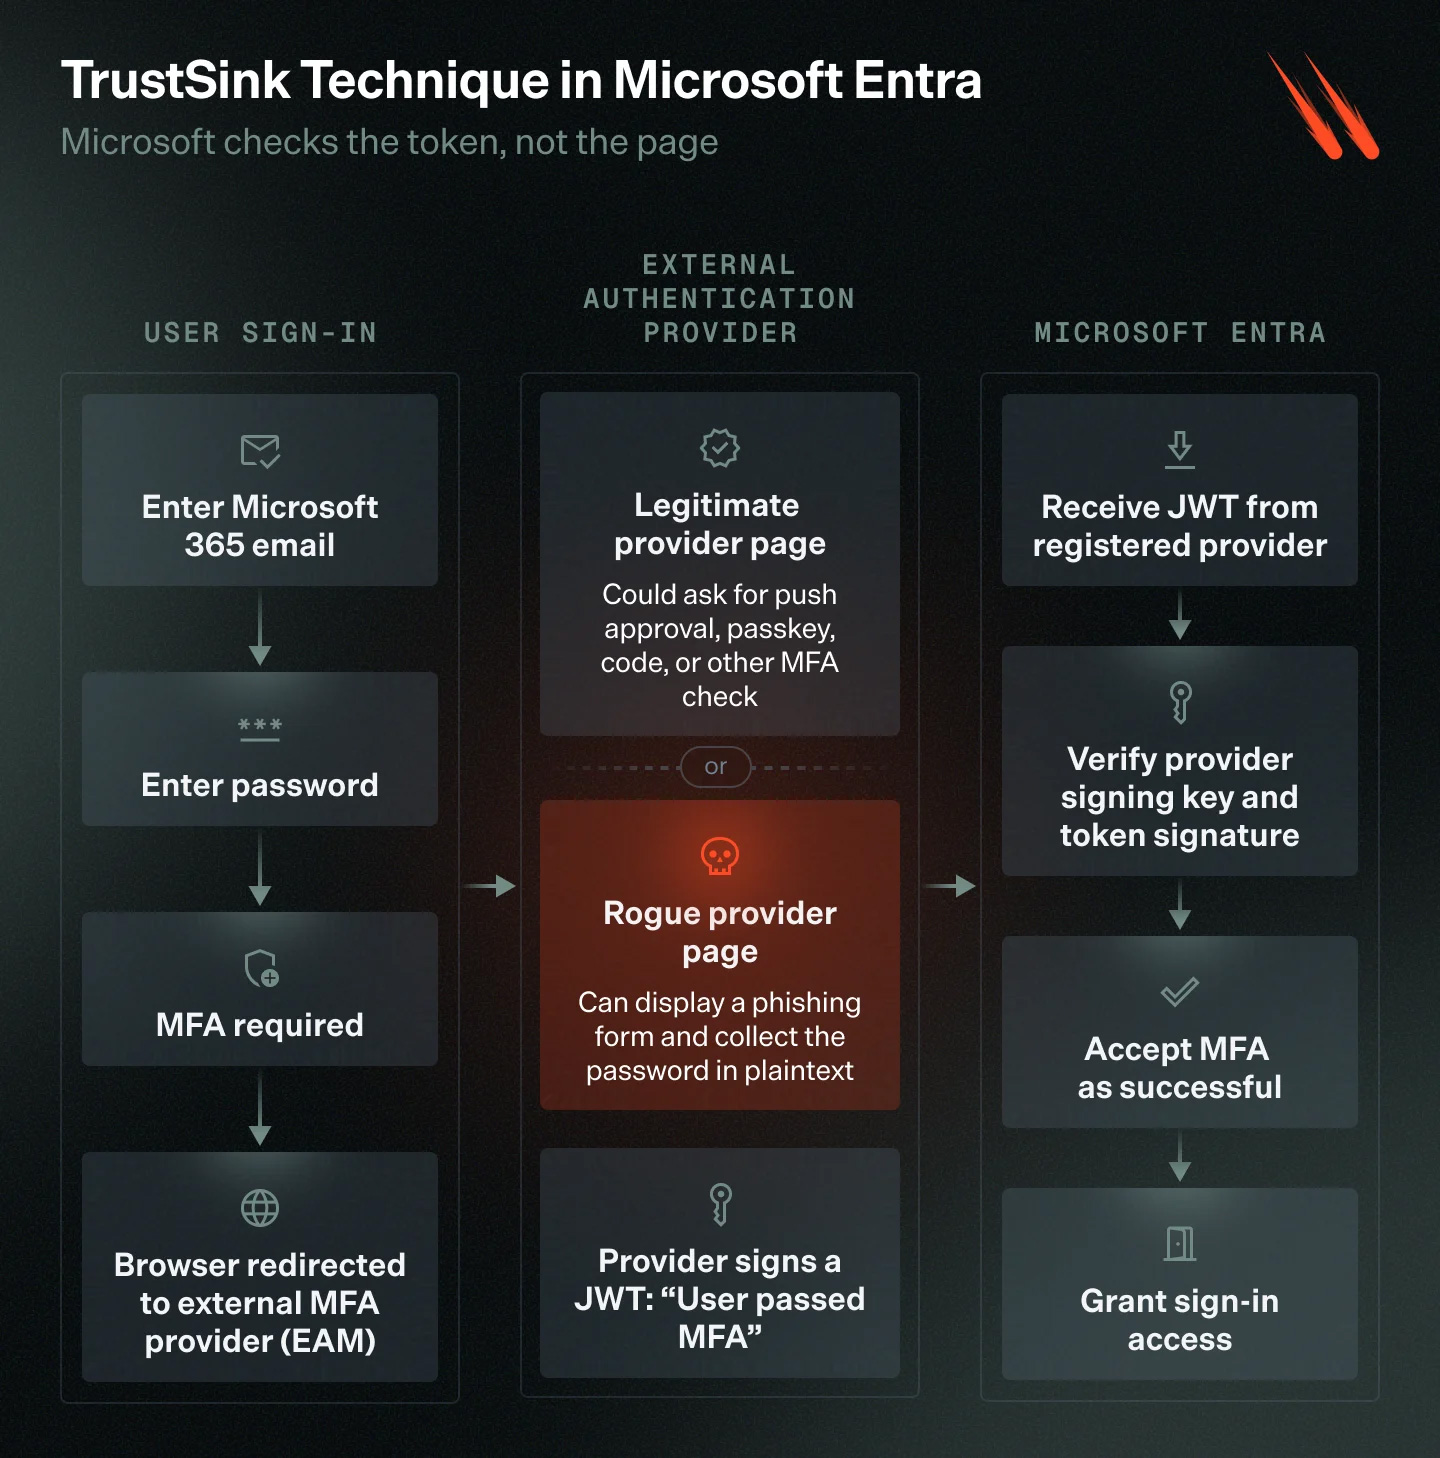
During the proof-of-concept attack, the login initially proceeds normally, with the user entering their email address and password on Microsoft’s legitimate login.microsoftonline.com site.
When MFA is triggered, Entra redirects the browser to the attacker’s external MFA provider for the second authentication step.
Instead of presenting a legitimate second-factor challenge, the malicious provider displays a copy of Microsoft’s password prompt.
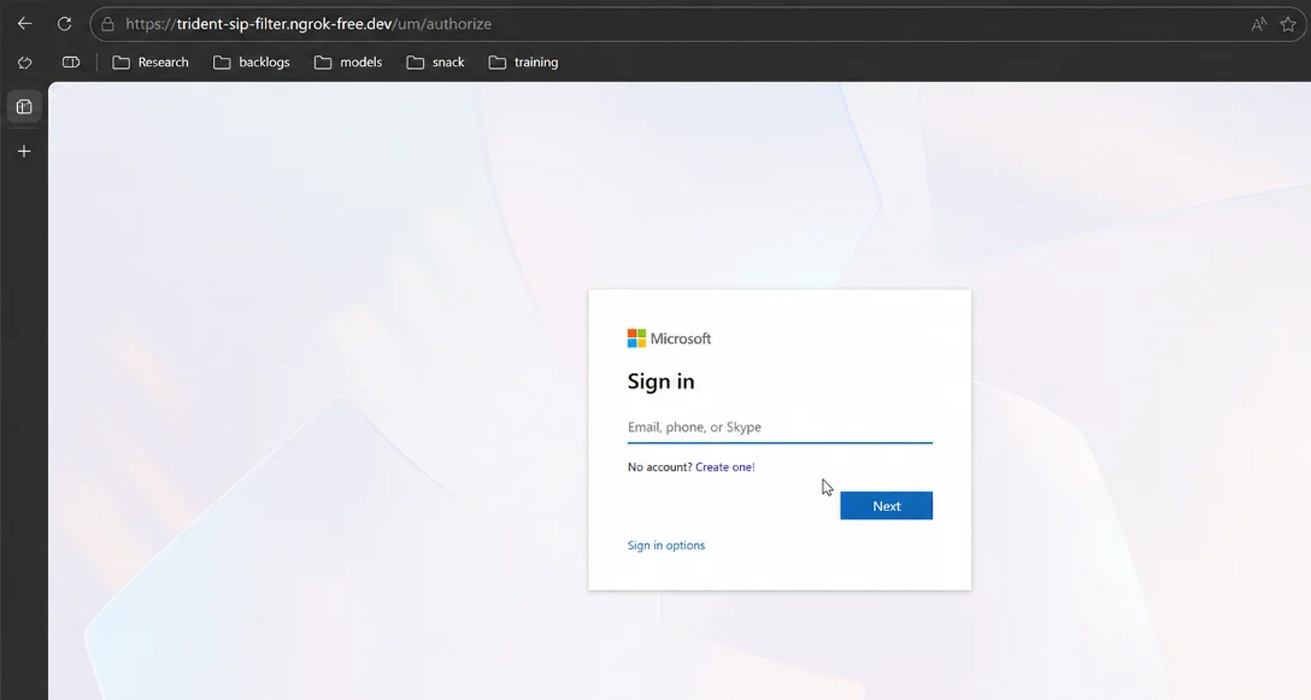
Source: Varonis
If the victim enters their password again, believing Microsoft is requesting it as part of the authentication process, the credential is sent to the attacker-controlled server.
The rogue provider then generates a signed token stating the MFA prompt was completed and returns it to Entra, allowing the user to continue to the application they originally attempted to access.
From the victim’s perspective, the sign-in appears to have completed normally.
Varonis says the attack is convincing because the fake password prompt appears when the user already expects another authentication step.
The researchers say the page uses the same fonts, layout, and button design as Microsoft’s legitimate login page and appears immediately after the victim enters their real password on Microsoft’s domain.
Varonis says TrustSink builds on previous research by security researcher Dirk-Jan Mollema, presented at x33fcon 2025 in a talk titled “Bringing Your Own Identity in Entra ID.”
Mollema showed how a rogue registered external MFA provider could satisfy an MFA requirement by returning a signed JWT claiming authentication had succeeded without actually performing the expected authentication check.
TrustSink abuses the same attack for credential theft.
Varonis says registering the malicious external method requires modifying the Authentication Methods Policy and creating an application, service principal, and consent grant.
Those actions require a Global Administrator or Authentication Policy Administrator account, making TrustSink a post-compromise technique.
Once installed, however, the rogue provider can remain in the authentication path for targeted users across subsequent logins.
Because the rogue MFA provider remains registered in the tenant’s Authentication Methods Policy, even if a user changes their password, it will be recaptured on the next log in attempt.
Varonis therefore warns administrators to remove the malicious provider before rotating affected credentials.
Varonis recommends removing suspicious external MFA providers and their associated applications, keys, and redirect URIs before resetting affected users’ passwords.
Organizations should also monitor changes to the Authentication Methods Policy, limit standing Global Administrator and Authentication Policy Administrator privileges, and use phishing-resistant authentication methods such as FIDO2 or Windows Hello for Business.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
