


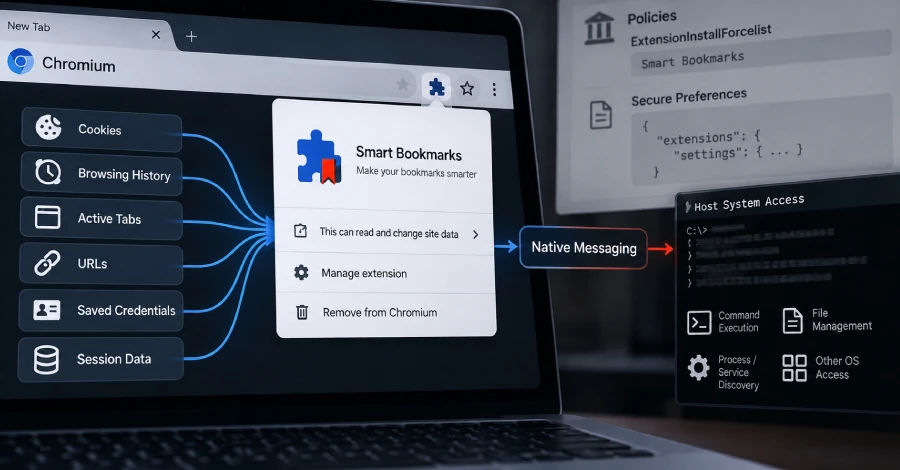
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser.
“Requiring prior administrative or code execution access, its installer injects the extension directly into Chrome/Edge profiles, bypassing Web Store checks and user prompts by forging Chromium’s own Secure Preferences integrity values,” SOCRadar said. “A native-messaging tool then extends it beyond browser telemetry to host-level command execution and file management.”
Once installed, the PEEP “extension” agent polls its command-and-control (C2) server (“206.237.30[.]232” or “xfjcc[.]fun“) every 30 seconds over plaintext HTTP for new commands, while exfiltrating browsing history, active-tab metadata, and session cookies. It also functions as a remote access and browser monitoring toolkit that runs host commands, steals credentials, hijacks sessions, and alters web pages.
PEEP is built on the foundations of an open-source, browser data analysis and red teaming framework called RedExt, which has also been put to use in prior GlassWorm attacks. However, it expands on the toolkit with dedicated installation routines, a native host bridge, heartbeat telemetry, an update channel, and a broader command set. This, in turn, makes PEEP a derivative of RedExt.
PEEP is described as a post-compromise framework as it lacks an initial access vector itself, meaning it requires the operator to breach a machine through some other means and deploy the malware. The activity remains unattributed, although the presence of Chinese-language artifacts in the source code points to a Chinese-speaking threat actor.

The extension masquerades as “Smart Bookmarks” (ID: ejkndncpkdcjcikfhiamcdehdoegilbj). It’s the main agent responsible for executing the beacon loop by polling “/api/commands,” harvesting browser data, receiving additional tasking, and sending the results back.
The browser add-on also invokes an auxiliary executable (“nm_host.exe”) when said task requires operating system access, while browser-based commands (e.g., screenshots, clipboard, or JavaScript injection) are run locally. The use of the Native Messaging Host binary transforms the malware from a basic credential stealer to a remote-access tool.
“Operating in the user context, the extension extracts browser artifacts and uses com.peep.lab/nm_host.exe to run shell commands, manage files, and discover processes and services,” SOCRadar said. “Bypassing Web Store checks, PEEP maintains persistence via sideloading, enterprise force-install policies, preference-integrity manipulation, and a ScriptCache fallback.”

Also used by the extension are several other endpoints –
- “/api/register” to register the infection
- “/api/agents/
/heartbeat” to send details about the browser’s User-Agent string, operating system, and time zone - “/api/extension_update/” and “/api/extension_crx/” to update the extension itself
- “/api/agents/
/task_result” to post the results of the command execution - “/api/exfil” to post auto-collected data, such as cookies, recent history, open tabs, active URL, public IP address, locale, and time zone
- “/health” to serve internal system status without requiring login credentials
- “/login” to serve a login interface for the C2 panel at port 5001
Another defining aspect of PEEP is its ability to modify the Secure Preferences file to ensure that the extension is auto-enabled upon launching the browser. Given that the extension is not available on the Chrome Web Store and other official extension marketplaces, it also leverages the ExtensionInstallForcelist or ExtensionSettings policies and sideloading tricks for delivery.
To aid in this tampering, the malware makes use of two PowerShell scripts –
- install_silent.ps1, which enables Developer Mode to sideload arbitrary extensions
- patch_secure_prefs.ps1, which patches the Secure Preferences file
- force_enable.ps1, which removes the extension from Preferences’s external_uninstalls, places the CRX at %LOCALAPPDATA%PEEPcrx, re-registers via the HKCU Extensions key and an External Extensions JSON manifest, and restarts the browser
There also exists a Python script “patch_secure_prefs_linux.py” indicating that the threat actor behind the operation is replicating the behavior to also target Linux environments.

Once initialized, the extension parses a configuration file to extract C2 information and activate automated data harvesting, while a companion content script (“content.js”) is embedded across all active web pages.
SOCRadar said it identified a number of references to “Authorized CTF” use, raising the possibility that the threat actor may have used the framing to lower the safety guardrails of AI tools and assist in malware development. There are currently no signs as to who is being targeted, but the “/health” endpoint shows 34 agent entries, 10 active sessions, and 507 data records. That said, there is no way to differentiate actual infected hosts from test entries or verified deployments.
“PEEP builds on existing host compromises, using a native-messaging bridge to convert Chrome/Edge into a persistent backdoor that crosses the browser sandbox to reach the OS,” SOCRadar said. “Because its logic runs inside the signed browser process, it slips past detection of keys on new or unsigned binaries. Consequently, the browser acts as an endpoint pivot for credential theft, session abuse, and command execution.”
