

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

    October 18, 2026

    Nearly 90% of countries adopt biodiversity targets, but most remain off track

    October 18, 2026

    Scientists discover how deep sleep builds muscle, burns fat, and boosts the brain

    October 18, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing
    • Nearly 90% of countries adopt biodiversity targets, but most remain off track
    • Scientists discover how deep sleep builds muscle, burns fat, and boosts the brain
    • NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks
    • A 24-year study uncovers a surprising climate benefit beneath forests
    • Kmart used to sell pet monkeys in the 1960s. It wasn’t alone
    • Yvette Cooper pledges £140m to boost urgent care as NHS faces ‘tough’ winter | NHS
    • Meet Kyutai REKI: The 2.4B VLA Model Bringing Efficient Memory to Robot Manipulation
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Sunday, October 18
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Hackers exploit new MikroTik RouterOS flaws to hijack routers

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 7, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

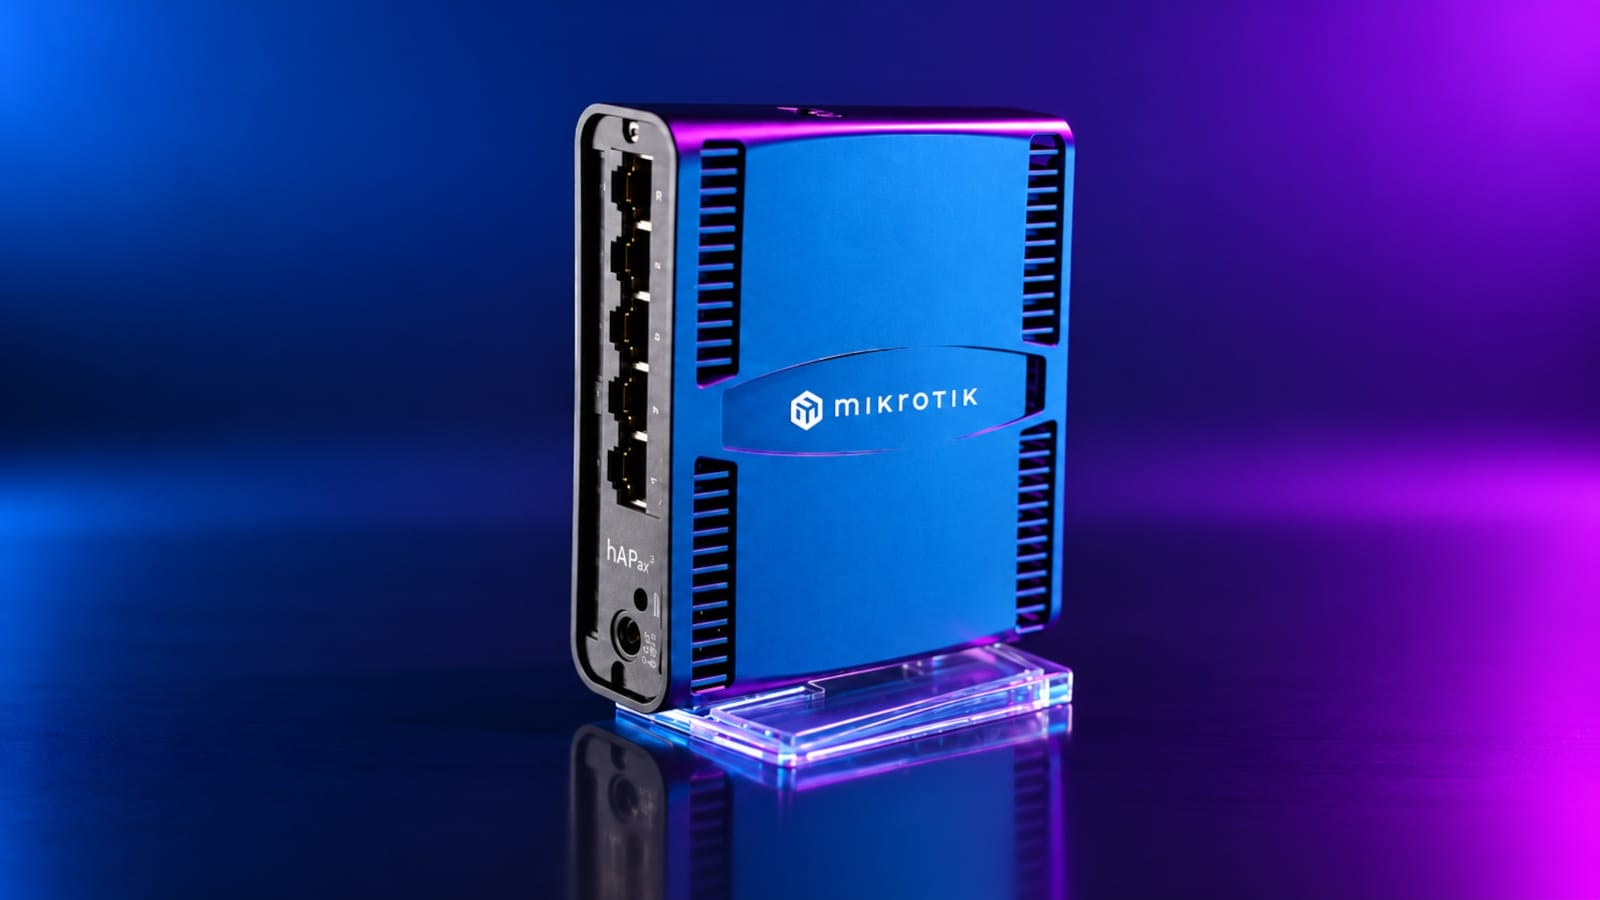
    Hackers are exploiting a chain of two recently disclosed vulnerabilities in MikroTik routers to take control of devices with SSH services exposed to the internet.

    One of the security issues, tracked as CVE-2026-67276, is an SSH authentication bypass flaw in MikroTik RouterOS caused by incomplete validation of RSA public keys.

    An attacker who knows a username and the public modulus of that user’s key can exploit it by crafting a different key and logging in without the legitimate private key.

    The second security issue is identified as CVE-2026-86060. It is an SSH privilege escalation flaw in MikroTik RouterOS due to improper handling of specially crafted usernames.

    Hackers can leverage it using a specially crafted username to manipulate the SSH session so that the attacker obtains full administrative privileges.

    Both vulnerabilities were discovered by Poland’s CERT agency with the help of GPT-5.5-cyber and GPT-5.6-sol and received a critical severity rating.

    The Polish agency dubbed the exploit chain “MikroTrick,” and warned that it is now actively exploited in the wild.

    “In recent days we have been observing attacks against RouterOS devices accessible from the internet,” Poland’s CERT warns.

    “We have obtained confirmation that the attackers are exploiting this combination of vulnerabilities to take full control of devices whose SSH service is accessible from public networks.”

    The Polish CERT also highlighted a third flaw, CVE-2026-67277, which affects the RouterOS bandwidth-test service and allows unauthenticated attackers to leak kernel memory or to remotely crash/restart the router.

    MikroTik fixed the vulnerabilities in RouterOS 7.25beta3, 7.24.2, 7.23.4, and 6.49.21, released on September 3, and Poland’s CERT validated the fixes.

    In its advisory, the vendor notes that not all configurations are affected, but did not disclose any details to give users time to apply the security updates.

    The updates add a compromise-detection mechanism to the routers that looks for known signs of unauthorized configuration changes at startup, disables malicious entries, and logs a critical warning.

    However, the CERT notes that the absence of a marker indicating compromise should not be taken as a guarantee that a router has not been compromised.

    The CERT shared the following indicators of compromise (IoCs):

    • Log entries: ‘login failure for user -2 from via ssh’ and ‘user added by ssh:-2@’
    • Presence of a highly privileged ops account
    • 82.192.72.4 — linked to confirmed successful attacks
    • 103.102.31.18 — observed attempting to exploit MikroTrick

    If compromise is suspected, the Polish agency recommends isolating the router, preserving logs and configuration, then factory-resetting the device and rebuilding it from a trusted configuration while rotating passwords, keys, and other secrets.

    For those unable to apply the updates immediately, one recommendation is to restrict or disable externally accessible SSH, WWW/WWW-SSL, and bandwidth-test services, and avoid the built-in SSH clients and outbound TLS connections over untrusted networks.

    As of September 5, there were 122,500 MikroTik devices with an exposed SSH interface, according to data provided by The ShadowServer Foundation. The exact number of devices vulnerable the MikroTik exploit was not determined, though.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    exploit flaws hackers hijack MikroTik RouterOS routers
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

    NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks

    Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks

    Drupal patches critical RCE flaws, warns exploits may emerge soon

    OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract

    Hackers breach Microsoft 365 tenants via ConnectWise supply-chain attack

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

    October 18, 2026

    Nearly 90% of countries adopt biodiversity targets, but most remain off track

    October 18, 2026

    Scientists discover how deep sleep builds muscle, burns fat, and boosts the brain

    October 18, 2026

    NGINX Fixes 5 Flaws, Including Possible RCE and a TLS Bug That May Skip Client-Cert Checks

    October 18, 2026
    Latest Posts

    The Guardian view on Japan’s yen: Trump wants to keep the easy-money machine running | Editorial

    August 12, 2026

    Minesto reshapes organization to drive commercial expansion of tidal technology

    August 12, 2026

    Corpus Christi Puts Industrial Water Charge on November Ballot

    August 12, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Next.js Ships Out-of-Band Patch for Two Critical RCE Flaws in Caching and SVG Processing

    October 18, 2026

    Nearly 90% of countries adopt biodiversity targets, but most remain off track

    October 18, 2026

    Scientists discover how deep sleep builds muscle, burns fat, and boosts the brain

    October 18, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.