

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Rubio’s India Trip Focuses on Business

    October 21, 2026

    Are ‘Texas Transgender Student Union’ mailers from legitimate civil rights group? It’s unlikely

    October 21, 2026

    AfD’s Alice Weidel urges quick Ukraine talks and a return to cheap Russian energy – POLITICO

    October 21, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Rubio’s India Trip Focuses on Business
    • Are ‘Texas Transgender Student Union’ mailers from legitimate civil rights group? It’s unlikely
    • AfD’s Alice Weidel urges quick Ukraine talks and a return to cheap Russian energy – POLITICO
    • Holocaust school lessons to be improved after ‘shocking’ antisemitism review
    • Marvell, Microsoft & Oracle Work to Standardize Data Centers
    • Astronauts’ hearts just passed a surprising test for Mars
    • Extractive industries threaten global goal to protect 30% of nature by 2030, report finds
    • A plan to ensure energy is affordable for all | Energy bills
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, October 21
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Over 8,300 Gitea servers vulnerable to code execution attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 28, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Over 8,300 Internet-exposed Gitea instances are still unpatched against a critical security flaw exploited in ongoing remote code execution attacks, according to cybersecurity watchdog Shadowserver.

    The code injection vulnerability (CVE-2026-60004) targeted in these attacks was reported by Salesforce security researcher Shai Rod, and it allows authenticated attackers to execute arbitrary shell commands with the privileges of the Gitea service account by submitting malicious patches via the diffpatch API endpoint.

    While successful exploitation requires repository write access to repositories hosted on vulnerable servers, Gitea comes with self-registration enabled by default, allowing unauthenticated attackers to register an account, create a new repository, and trigger the vulnerability without prior credentials.
    image

    “Gitea’s diffpatch endpoint can be abused to install and execute a Git hook from repository-controlled content. An attacker with ordinary write access to a repository can execute arbitrary shell commands as the Gitea OS user,” Gitea’s security team explains. “With default open registration, an unauthenticated visitor can obtain the required write access by registering an account and creating a repository.”

    Gitea released version 1.27.1 on July 27 to address CVE-2026-60004 and advised users to upgrade their servers as soon as possible.

    On Friday, Internet security watchdog group Shadowserver warned that nearly 8,400 Gitea servers exposed online are still unsecured and remain vulnerable to ongoing attacks.

    “We are scanning/reporting Gitea instances vulnerable to CVE-2026-60004 (code injection), with 8393 IPs found vulnerable on 2026-08-27,” Shadowserver said.
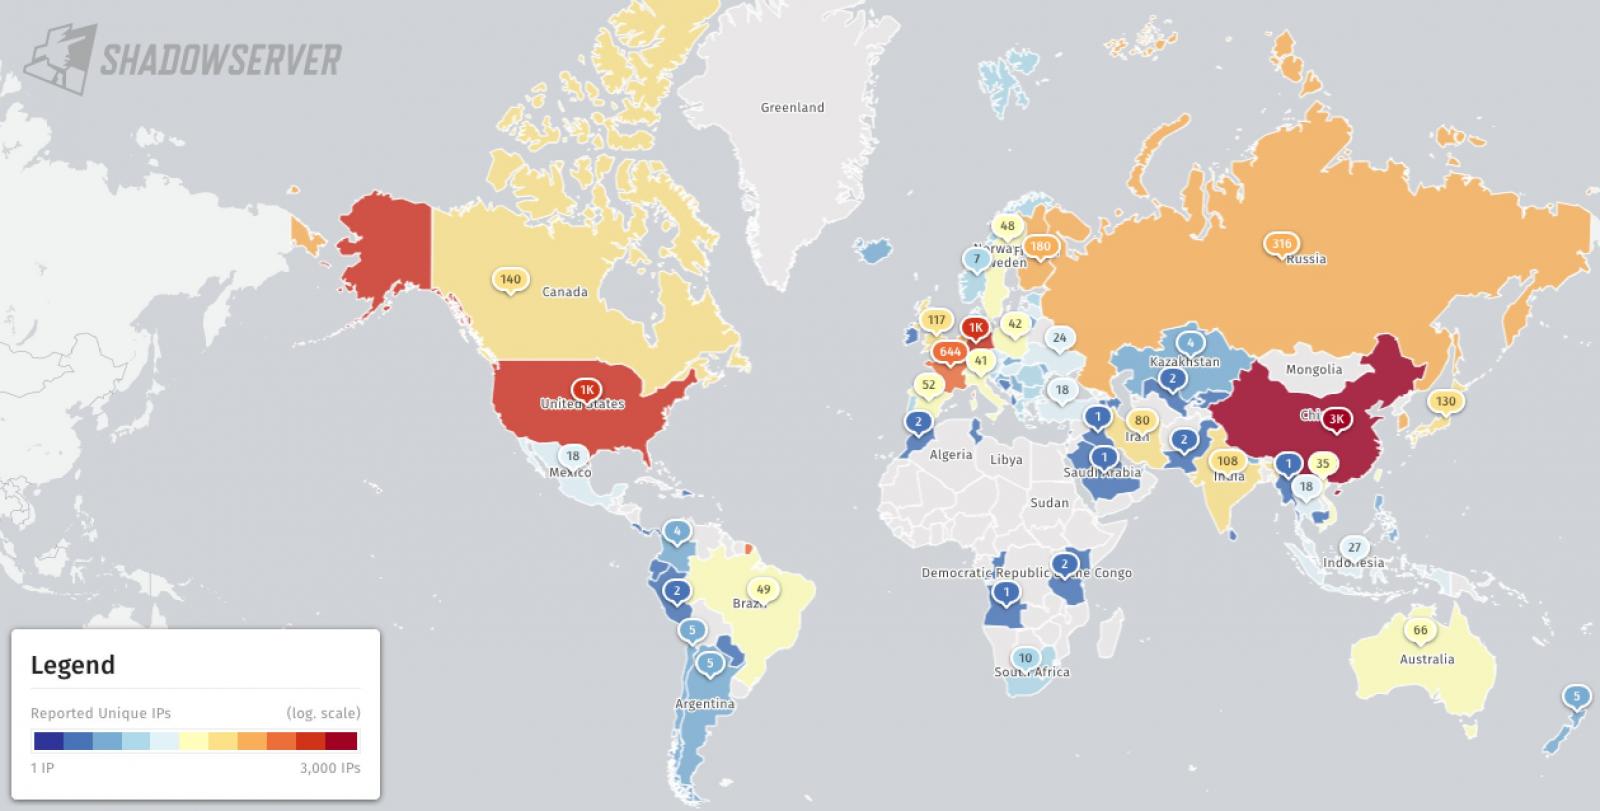
    Vulnerable Gitea intsances
    Vulnerable Gitea instances (Shadowserver)

    ​On Tuesday, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) also added the vulnerability to its catalog of actively exploited flaws and ordered U.S. Federal Civilian Executive Branch (FCEB) agencies to patch their servers within three days, by August 28, as mandated by Binding Operational Directive (BOD) 26-04.

    While the cybersecurity agency has yet to share further details on attacks targeting this flaw, the move was likely prompted by reports of in-the-wild exploitation, in which the attackers are deploying cryptocurrency mining malware on unpatched Gitea servers.

    “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise,” CISA warned.

    In July, threat actors were also spotted abusing another critical vulnerability (CVE-2026-20896) in the official Gitea Docker image, an authentication bypass flaw affecting Gitea instances with reverse proxy authentication headers enabled.

    Gitea is a self-hosted alternative to cloud-hosted GitHub, GitLab, and Bitbucket code hosting and DevOps platforms, with more than 400,000 installations and nearly 1,500 contributors.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    attacks Code Execution Gitea Servers vulnerable
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Marvell, Microsoft & Oracle Work to Standardize Data Centers

    Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases

    CISA: Hackers chain Plex flaws in Plex2Shell attacks to breach servers

    Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections

    Optiv Launches CyberBOT Cybersecurity Awareness Training Program

    PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Rubio’s India Trip Focuses on Business

    October 21, 2026

    Are ‘Texas Transgender Student Union’ mailers from legitimate civil rights group? It’s unlikely

    October 21, 2026

    AfD’s Alice Weidel urges quick Ukraine talks and a return to cheap Russian energy – POLITICO

    October 21, 2026

    Holocaust school lessons to be improved after ‘shocking’ antisemitism review

    October 21, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Rubio’s India Trip Focuses on Business

    October 21, 2026

    Are ‘Texas Transgender Student Union’ mailers from legitimate civil rights group? It’s unlikely

    October 21, 2026

    AfD’s Alice Weidel urges quick Ukraine talks and a return to cheap Russian energy – POLITICO

    October 21, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.