

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    The Guardian view on Barack Obama’s new podcast: all the president’s books | Editorial

    October 2, 2026

    Woman at centre of Cornell rape inquiry ‘failed’ by officials, says New York governor

    October 2, 2026

    Polanski’s Greens look for their next opening – POLITICO

    October 2, 2026
    Facebook X (Twitter) Instagram
    Trending
    • The Guardian view on Barack Obama’s new podcast: all the president’s books | Editorial
    • Woman at centre of Cornell rape inquiry ‘failed’ by officials, says New York governor
    • Polanski’s Greens look for their next opening – POLITICO
    • At Brighton, Polanski raised his arms in triumph. It felt more like a wave goodbye | John Crace
    • Widdecombe suspect charged with planning acts of terror against Farage
    • Resilience, integration and competitiveness: building the future of European banking
    • This Shoe Company’s Instagram Ad With a Frat Is Pissing People Off
    • NVIDIA Announces DGX Spark 64GB: A 1-PetaFLOP Grace Blackwell Desktop for Local AI Agents, Fine-Tuning, and Inference
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, October 2
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Max severity SAP Commerce Cloud flaw now targeted in attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 15, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A maximum-severity SAP Commerce Cloud remote code execution vulnerability patched three days ago is already being targeted in attacks, according to threat intelligence company Defused.

    Commerce Cloud (formerly known as SAP Hybris) is a cloud-based e-commerce platform used by online stores owned by high-profile global brands and large retailers.

    Tracked as CVE-2026-58231, this critical flaw stems from an improper authorization weakness in the core Data Hub Adapter extension for Commerce Cloud that threat actors without privileges can exploit in low-complexity attacks to execute arbitrary code.
    image

    “SAP Commerce Cloud allows an unauthenticated attacker to abuse a default authentication client and submit specially crafted input to certain functions lacking sufficient validation,” SAP explains.

    “Successful exploitation could enable arbitrary code execution and compromise internal components, resulting in high impact on confidentiality, integrity, and availability of the application.”

    While SAP has yet to flag this security flaw as actively exploited in a security advisory issued this Tuesday, Defused security researchers confirmed earlier today that CVE-2026-58231 is now being targeted in the wild.
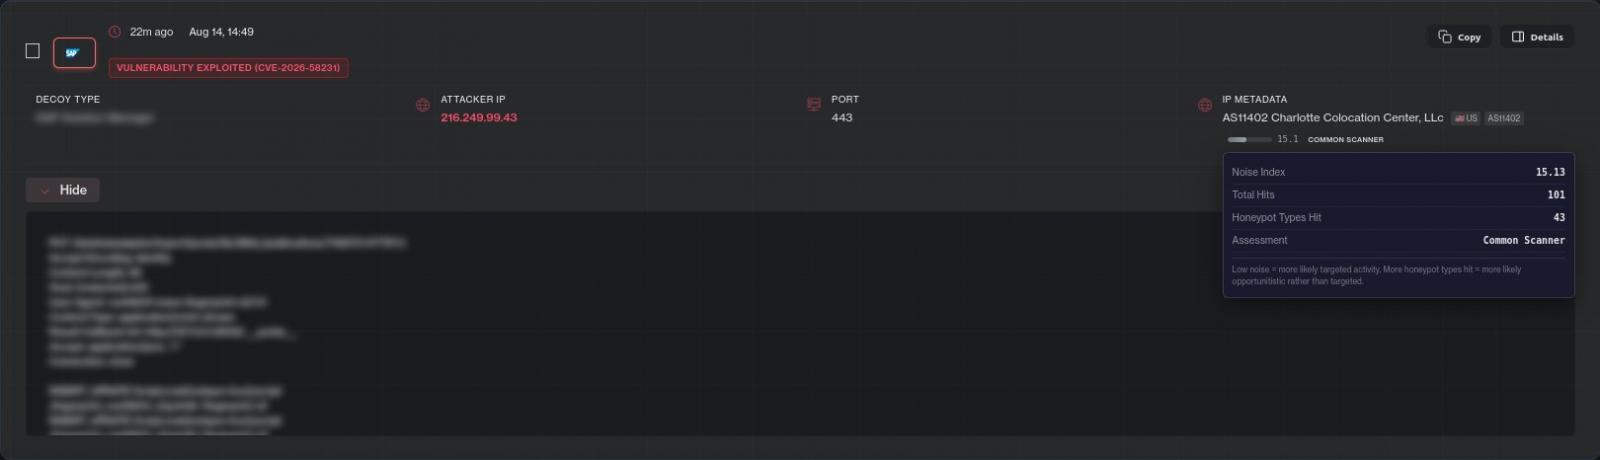
    CVE-2026-58231 exploitation attempt
    CVE-2026-58231 exploitation attempt (Defused)

    ​”First exploitation attempts against CVE-2026-58231 (unauth RCE in SAP Commerce Cloud, CVSS 10.0) is now hitting our honeypots – 3 days after patch day,” Defused warned in a Friday tweet. “This vulnerability has no public PoC and is not known to be exploited.”

    A SAP spokesperson told BleepingComputer that the company is aware of and investigating this issue when asked to confirm Defused’s report.

    “A security note https://me.sap.com/notes/3771065 is published and available for SAP customers and partners and was released on SAP’s August Patch Day. We recommend customers and partners patch their systems with immediate effect,” the spokesperson added.

    Internet security watchdog group Shadowserver tracks over 4,200 IP addresses with a SAP Commerce Cloud fingerprint, most of them from Europe and North America.

    However, there is no information on how many of them are honeypots or have already been secured against CVE-2026-58231 attacks.
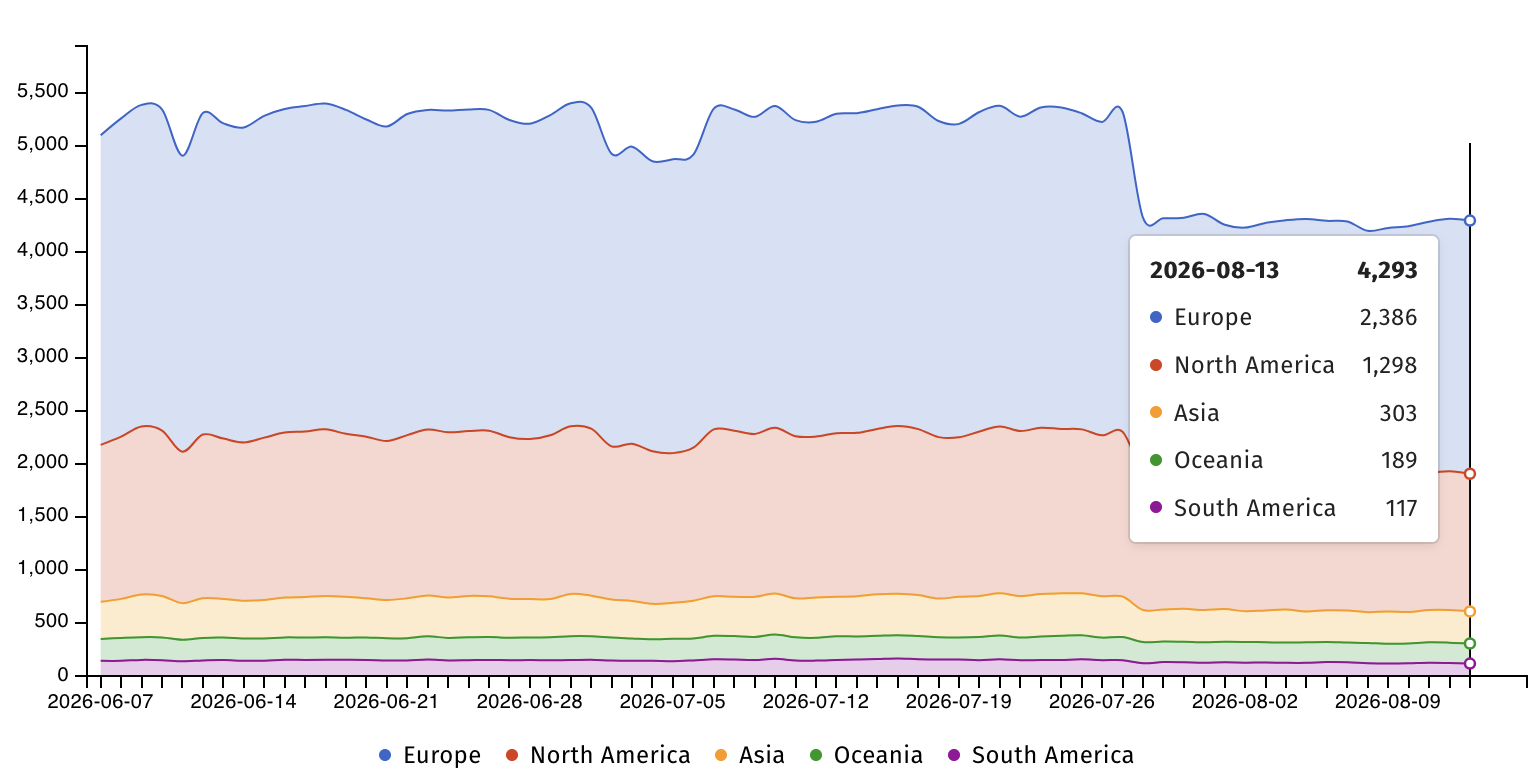
    Internet-exposed SAP Commerce Cloud instances
    Internet-exposed SAP Commerce Cloud instances (Shadowserver)

    ​Most recently, SAP fixed 16 vulnerabilities in its July 2026 Security Patch package and 30 more vulnerabilities in June and May, including three more critical security flaws (CVE-2026-44761, CVE-2026-22732, and CVE-2026-34263) affecting the Commerce Cloud enterprise-grade e-commerce platform.

    In April, cybersecurity companies Aikido and Socket also reported that attackers aiming to steal credentials from developers’ systems compromised multiple official SAP npm packages in a supply chain attack.

    Since November 2021, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added 14 SAP vulnerabilities to its Known Exploited Vulnerabilities catalog, including three that were abused in ransomware attacks.

    SAP is a German multinational software corporation that serves 99 of the 100 largest companies worldwide and has reported total revenues exceeding €36 billion in fiscal year 2025.

    Update August 14, 11:51 EDT: Added SAP statement.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    attacks cloud commerce Flaw Max SAP severity targeted
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers

    SWIFT Banking & Government Middleware Enables RCE

    In Other News: $15K iCloud Spoofing Bugs, AI Policy Experts Phished, Adblocker Spies on AI Chats

    US sanctions Tren de Aragua gang members in ATM hacks crackdown

    Vulnerability Backlogs Are an Ownership Problem

    macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    The Guardian view on Barack Obama’s new podcast: all the president’s books | Editorial

    October 2, 2026

    Woman at centre of Cornell rape inquiry ‘failed’ by officials, says New York governor

    October 2, 2026

    Polanski’s Greens look for their next opening – POLITICO

    October 2, 2026

    At Brighton, Polanski raised his arms in triumph. It felt more like a wave goodbye | John Crace

    October 2, 2026
    Latest Posts

    Lime bikes hurtling around the city: is this the revenge of a priced-out generation? | Andy Beckett

    August 8, 2026

    Clarity Act Delayed Until September, Trump Praises Bitcoin

    August 8, 2026

    North Carolina Ports confirms cyberattack disrupting operations

    August 8, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    The Guardian view on Barack Obama’s new podcast: all the president’s books | Editorial

    October 2, 2026

    Woman at centre of Cornell rape inquiry ‘failed’ by officials, says New York governor

    October 2, 2026

    Polanski’s Greens look for their next opening – POLITICO

    October 2, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.