

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Abercynon woman, 93, waits 10 hours on floor for an ambulance

    October 24, 2026

    Almost 1,000 arrested as clashes follow another day of mass protests across France

    October 24, 2026

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    October 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Abercynon woman, 93, waits 10 hours on floor for an ambulance
    • Almost 1,000 arrested as clashes follow another day of mass protests across France
    • Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads
    • Scientists discover a hidden switch that burns fat and blocks new fat cells
    • Mass sloth deaths prompt US bill calling for import ban
    • Brussels shops boarded up amid fears of repeat of last week’s looting
    • Your blood could reveal inflammatory bowel disease 10 years before diagnosis
    • Sri Lanka mourns iconic tusker amid renewed calls to address human-elephant conflict
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Crypto & Blockchain

    Ledger patched critical signing bugs months after writing the fixes

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 28, 2026 Crypto & Blockchain No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Crypto wallet maker Ledger is urging its Ethereum app users to update again after two signing flaws remained in its previous security release.

    The hardware-wallet maker published Ethereum app version 1.22.3 on Aug. 25, closing vulnerabilities that could hide operations from a device review or authorize a token approval in place of an expected payment.

    The update follows controversy over a separate Ethereum signing flaw reproduced by rival wallet maker OneKey. That issue, tracked as LSB-023, affected older versions and allowed a compromised host to interleave commands so that transaction parameters could change after being displayed but before signing.

    Ledger said OneKey demonstrated the bug against version 1.22.1 after the company had already fixed it in Ethereum app 1.22.2, released Aug. 13.

    Related Reading

    Ledger patched an Ethereum app bug that could show one transaction and sign another

    “No Ledger user was hacked,” Ledger’s security team said, describing the demonstration as a laboratory reproduction involving outdated software. The company said it had found no evidence of exploitation in the wild.

    Ledger Chief Technology Officer Charles Guillemet made the same distinction, saying reproducing an already-patched flaw did not amount to “hacking Ledger.”

    Version 1.22.2, however, did not close every known Ethereum-app vulnerability on Ledger. Instead, two separate flaws, LSB-024 and LSB-025, remained until the release of 1.22.3.

    Two additional signing paths remained exposed

    LSB-024 affected how the Ethereum app processed arrays of operations during clear signing.

    The app read the number of operations using a 16-bit value but stored the remaining count in an 8-bit field. In Ledger’s proof of concept, an array containing 257 operations wrapped the counter back to one, causing the device to display only the final operation even though its signature authorized the entire batch.

    Exploitation required a compromised host and an unusually large attacker-controlled operation array. Ledger tested the scenario on a private network fork and reported no real-user losses.

    The Daily Brief

    The signal, before the noise.

    Start your day with the crypto stories moving markets, decoded by CryptoSlate’s editors.

    One email. Everything that matters.

    Free to join. Unsubscribe any time.

    Whoops, looks like there was a problem. Please try again.

    You’re on the list. Your next Daily Brief is on its way.

    The second vulnerability, LSB-025, affected the token-payment path used by Ledger’s Exchange application during swaps.
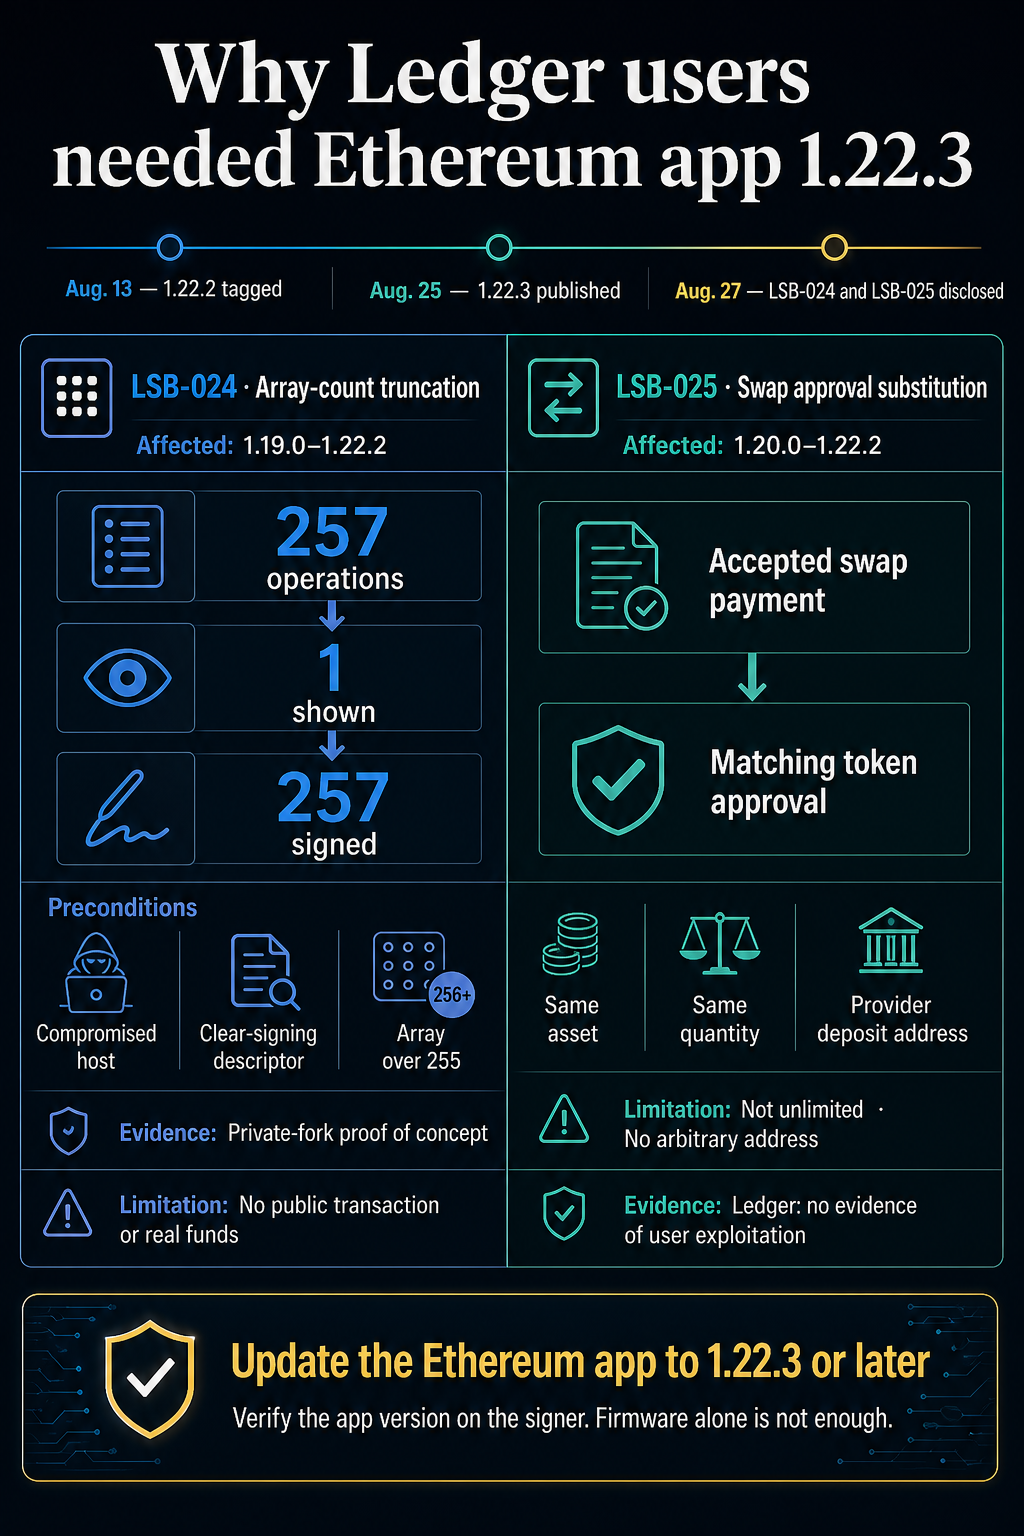
    Comparison of Ledger Ethereum app flaws LSB-024 and LSB-025, their affected versions, narrow trigger conditions, and the update to version 1.22.3

    Ledger’s app checked the token, quantity, and destination but did not verify that the requested action was actually a payment. A malicious or compromised swap provider could therefore substitute a token approval matching those same parameters and have it signed without an additional device prompt.

    The flaw could not create an unlimited approval, switch to another token, or grant permission to an arbitrary address. An approval also does not itself transfer funds, requiring a subsequent transaction before the approved assets could move.

    Ledger said it found no evidence that the swap vulnerability was exploited.

    The release history raises a separate question. Ledger’s records show the fix for the array-count issue was merged on May 5 and the swap-validation correction on May 25, months before version 1.22.2 was released. Its security bulletins do not explain why those changes were absent from that update.

    Ledger defended its broader approach by pointing to updateability as central to hardware wallet security. Its security team said it continuously identifies vulnerabilities through internal research and external bug-bounty programs, then patches them through software releases.

    For users, the distinction between the three vulnerabilities is important. Version 1.22.2 fixed the command-interleaving flaw later reproduced by OneKey, while version 1.22.3 is required to address the two additional signing bugs disclosed Aug. 27.

    Ledger recommends installing Ethereum app 1.22.3 or later through Ledger Live and verifying the version on the device. Updating the hardware wallet firmware alone does not replace the affected Ethereum application.

    Bugs critical Fixes Ledger months Patched signing writing
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloud

    Attackers Exploit Third Arista VCO Zero-Day in Four Months

    Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

    BlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing Revocations

    Potholes, bus fares and headphone dodgers: will Burnham’s strategy of ‘everyday fixes’ succeed? | Labour

    Critical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted Image

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Abercynon woman, 93, waits 10 hours on floor for an ambulance

    October 24, 2026

    Almost 1,000 arrested as clashes follow another day of mass protests across France

    October 24, 2026

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    October 24, 2026

    Scientists discover a hidden switch that burns fat and blocks new fat cells

    October 24, 2026
    Latest Posts

    Google AI health coach to use Abbott glucose data

    August 14, 2026

    CMF hit the balance between cheap and good clip earbuds

    August 14, 2026

    David Hearn’s Lawyers Ask Court to Bar Future Reflecting Pool Charges

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Abercynon woman, 93, waits 10 hours on floor for an ambulance

    October 24, 2026

    Almost 1,000 arrested as clashes follow another day of mass protests across France

    October 24, 2026

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    October 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.