



Update: Added statement from Falcon extortion gang below.
A recent wave of cyberattacks targeting hedge funds, private-equity firms, and other financial organizations has been linked to UNC6671, an extortion group reportedly associated with the BlackFile threat actors.
The attribution comes after Reuters and Bloomberg reported that Point72 Asset Management, Millennium Management, Two Sigma Investments, Citadel, and several private-equity firms were targeted in recent attacks that relied on voice phishing (vishing) to trick employees into granting the attackers access to corporate systems.
Point72 reportedly told investors that it had been attacked but had not found evidence that client data was stolen, while Two Sigma said it had blocked an attempted intrusion and found no indication that its systems or data were affected.
Millennium declined to comment in response to questions from BleepingComputer. Citadel also declined to comment and referred BleepingComputer to Bloomberg’s reporting. Point72 and Two Sigma did not respond to requests for comment.
In response to questions from BleepingComputer, Austin Larsen, a principal threat analyst at Google’s Threat Intelligence Group (GTIG), said the company tracks the vishing activity as UNC6671.
“While previously operating under the public brand ‘BlackFile,’ UNC6671 has diversified its extortion operations across multiple public brands, including Redact, Pink, Helix, and Falcon,” Larsen told BleepingComputer.
“GTIG assesses that a single core intrusion group is driving the helpdesk vishing and cloud data theft across these various public extortion brands.”
BlackFile is a data theft extortion group that first emerged in February 2025 when it conducted a wave of attacks targeting retail and hospitality organizations.
According to Mandiant’s report, the group’s targeting switched in July 2026 toward private-equity firms, hedge funds, major law firms, and financial-rating agencies after previously targeting organizations in the manufacturing, healthcare, real-estate, technology, transportation, and hospitality sectors.
“Between January and May 2026, GTIG tracked over $10.6 million USD in Bitcoin payments to group wallets. While initial demands reach upwards of $3 million, operators routinely settle for around $750,000 USD after negotiations,” Larsen said.
After publishing our story, the Falcon extortion group released a statement on their data leak site disputing some of Mandiant’s reporting.
“Falcon is a Redact affiliate. We are exclusively a Redact affiliate. We are not affiliated with, connected to, or under the same umbrella as Helix, Pink, or any other group named in Mandiant’s reporting,” the threat actors posted on their data leak site.
“We share no operators, infrastructure, tooling, negotiation channels, or proceeds with any group other than Redact.”
In May 2026, BlackFile announced on its data leak site that it was rebranding under the name Redact, under which it would continue its operations.
Vishing attacks target cloud environments
UNC6671 operators typically contact employees on their personal mobile phones while spoofing corporate helpdesks and claiming that workers need to enroll in passkeys or update their multi-factor authentication settings.
Victims are then directed to domains impersonating the targeted employee’s company that host adversary-in-the-middle phishing kits designed to steal credentials and session cookies in real time.
After stealing Microsoft 365 or Okta single-sign-on accounts, the attackers log into the SSO dashboard, which gives access to all the cloud platforms that are linked to the account.
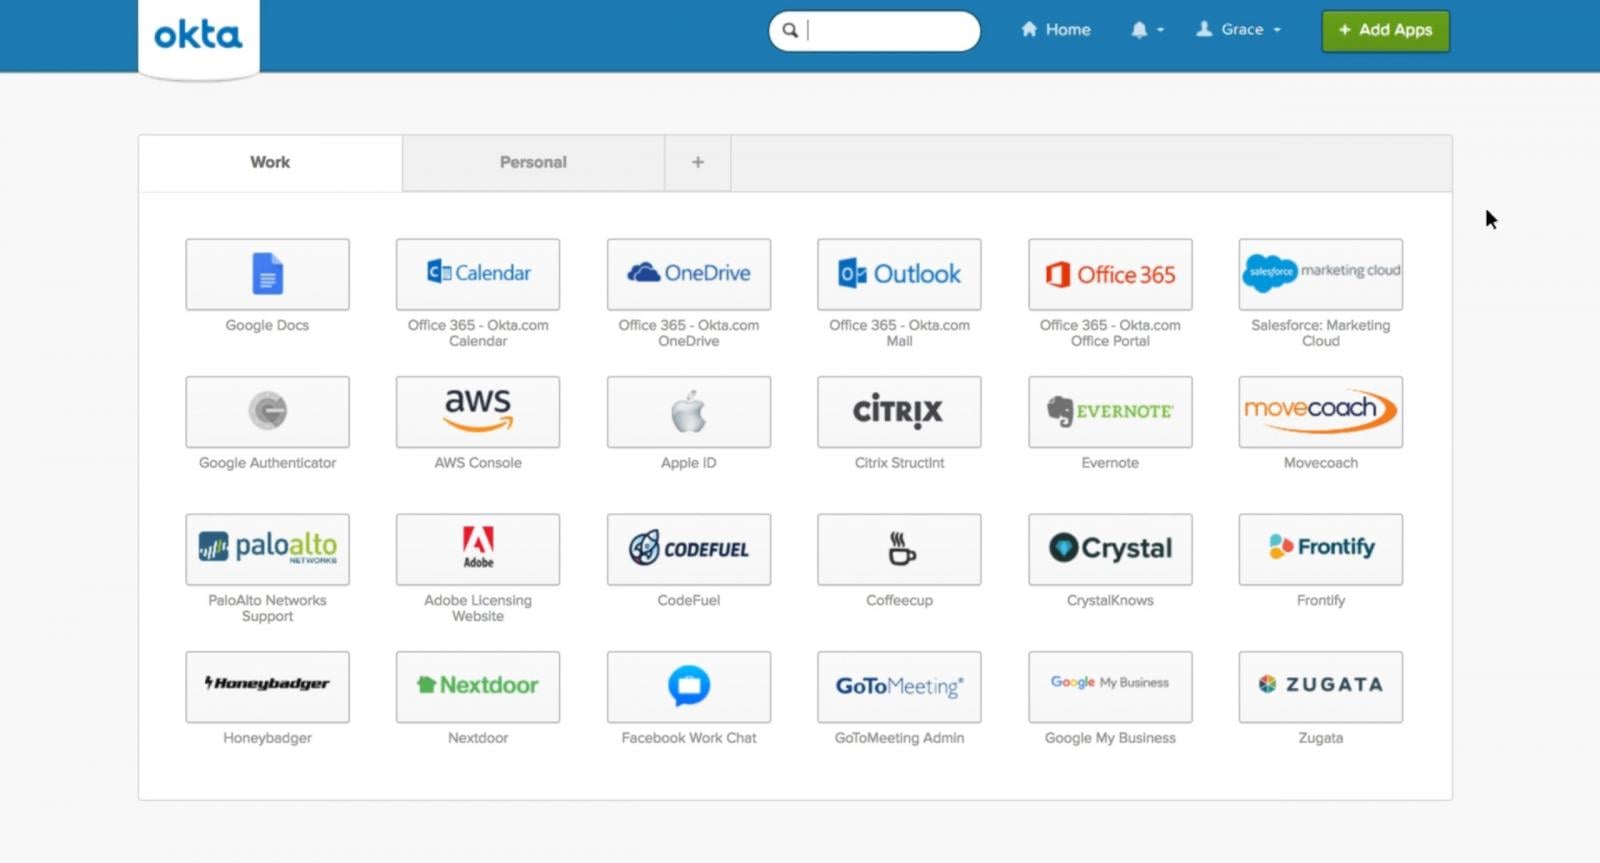
The hackers then use automated tools to steal data from all cloud services they gain access to and delete security notifications and password-reset emails from compromised inboxes.
Mandiant says the infrastructure and extortion network used in these attacks differ from those associated with Scattered Spider, which has historically employed similar helpdesk social-engineering tactics.
“While the helpdesk vishing and Adversary-in-the-Middle authentication interception share similarities with methods historically associated with Scattered Spider (UNC3944), GTIG tracks this specific infrastructure, domain registration pattern, and multi-brand extortion network as UNC6671,” Larsen told BleepingComputer.
Mandiant says it is currently assisting several dozen organizations compromised by UNC6671.

Security teams log 54% of successful attacks and alert on just 14%. The rest move through your environment unseen.
The Picus whitepaper shows how breach and attack simulation tests your SIEM and EDR rules so threats stop slipping by detection.
