

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    NASA’s Perseverance Offers Clues to Protect Crews From Mars Dust

    October 26, 2026

    Organized crime is growing along highway in a pristine section of the Amazon: Study

    October 26, 2026

    As students we never sought power – here’s how we reclaimed Serbia | Novak Simin

    October 26, 2026
    Facebook X (Twitter) Instagram
    Trending
    • NASA’s Perseverance Offers Clues to Protect Crews From Mars Dust
    • Organized crime is growing along highway in a pristine section of the Amazon: Study
    • As students we never sought power – here’s how we reclaimed Serbia | Novak Simin
    • ‘Yes Bibi or No Bibi’: Netanyahu’s political future overshadows Israel’s election
    • Healey is expected to shield low-income pensioners from income tax – but how will it work? | Pensions
    • Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento
    • Claude helped a scientist plan potentially risky bird flu research
    • Brazil Election: Lula Defeats Flávio Bolsonaro in Historic Victory
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Monday, October 26
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 26, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananOct 26, 2026Malware / Web Security

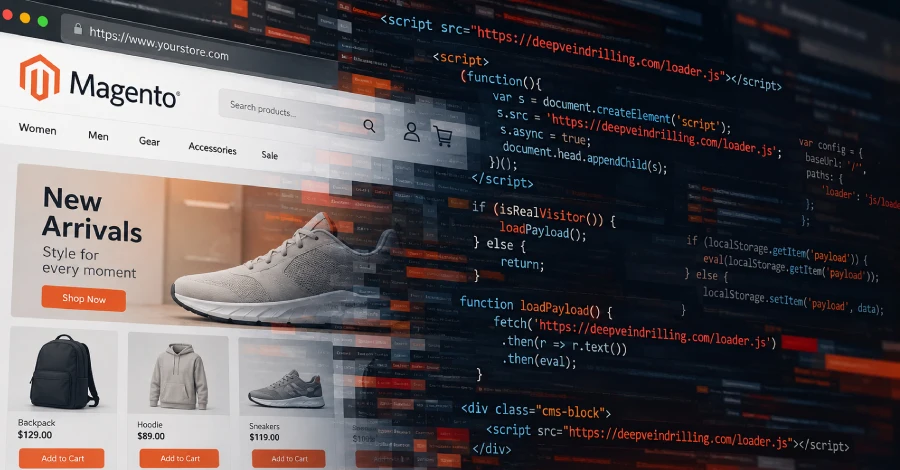
    An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.

    According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store’s pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks.

    “When you visit, that code makes your browser ask the group’s server what to do next,” Sansec said. “The server first checks whether you are a real shopper or a security scanner, so scanners get nothing.”

    No less than five distinct domains have been observed over time in connection with the campaign –

    • manulfie[.]click, first seen in July 2025
    • neswnsssn[.]click, first seen in December 2025
    • lanhd6549tdhse[.]top, first seen in March 2026
    • additionalver[.]com, first seen in June 2026
    • deepveindrilling[.]com, first seen in October 2026

    Sansec said it found deepveindrilling[.]com in the CMS blocks of 83 online stores since the domain was registered on October 6, 2026.

    The latest JavaScript loader domain is hosted behind Cloudflare and only responds to script requests from real visitors of infected stores. The loader is staged within Magento’s cms_block database table, which is used to render static content into storefront pages.

    Cybersecurity

    The ultimate objective of the attack is to launch the attack-controlled code when the CMS block is rendered after a shopper opens the compromised website.

    While Sansec does not disclose whether the threat actor modifies an existing CMS block (such as header, footer, or promotional banner) or creates a new block, the attacker can adopt either of the approaches to run the loader.

    Two different versions of the loader have been spotted. In one version, the external JavaScript loaded from the attacker’s domain stores the payload in the browser’s localStorage. This causes the stashed code to be run again on subsequent visits, even if the external domain becomes unavailable.

    The second version expands on this behavior by incorporating browser fingerprinting checks to filter out bots and security scanners, while ensuring that only real shoppers are exposed to the malicious code. The exact nature of the final payload remains unknown.

    Early iterations of the campaign have also been observed using Keitaro, an advertising tracker and analytics platform, as a traffic distribution system (TDS), to route visitors to different responses – i.e., return a payload, a redirect or nothing – based on their characteristics.

    Sansec said requesting the additionalver[.]com script as a Windows desktop visitor returned as response “QWE=123;,” which does nothing apart from setting a cookie that marks the visitor for 24 hours. The deepveindrilling[.]com domain, on the other hand, drops the Keitaro component and integrates the bot-filtering logic into the loader itself.

    As for the initial access vector, 471 Magento stores are estimated to have been injected with the loader through the PolyShell (aka CVE-2026-48356) vulnerability. Another 102 stores saw files uploaded through the PolyShell or SessionReaper (aka CVE-2025-54236) vulnerabilities.

    “One store on Magento 2.4.7-p1 had PolyShell webshells disguised as PNG images in pub/media/custom_options/quote/, next to the additionalver.com loader in a CMS block,” Sansec said. “The block switched to deepveindrilling[.]com on October 7. The store still lacks APSB26-73, Adobe’s PolyShell fix for supported release lines.”

    Cybersecurity

    In another case, an e-commerce store running Magento 2.4.7-p10 with no missing core patches was compromised to add a rogue administrator account and then use it to inject the code.

    Site owners are advised to audit their sites for suspicious accounts and unexpected CMS blocks in the cms_block and cms_page tables. It’s also advised to keep the sites up-to-date and enforce strong passwords.

    The disclosure comes against the backdrop of PHP2Shell, a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosure last week.

    However, Perplexity researcher Adel Karimi has recorded what appears to be the first in-the-wild successful exploitation of the vulnerabilities to run shell commands on honeypot servers. These commands have been observed using wget, curl, or PHP CLI to fetch additional payloads from a remote server (“162.35.99[.]94:80”).No downloaded second-stage artifacts have been observed so far.

    hackers infect JavaScript Magento online ScannerEvading stores
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    DreamHost forces password resets in ongoing “incident”

    Industrial Vendors Check Products for PHP2Shell Vulnerabilities

    Microsoft releases emergency .NET patches for critical Brotli flaw

    Critical ‘HTTP2Shell’ Brotli vulnerability triggers emergency patches

    ⚡ Weekly Recap: This2Shell, That2Shell, Everything’s an RCE? Rogue AI, Supply Chain Chaos and More

    When an AI Agent Is the Incident, the Identity Record Is the Evidence

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    NASA’s Perseverance Offers Clues to Protect Crews From Mars Dust

    October 26, 2026

    Organized crime is growing along highway in a pristine section of the Amazon: Study

    October 26, 2026

    As students we never sought power – here’s how we reclaimed Serbia | Novak Simin

    October 26, 2026

    ‘Yes Bibi or No Bibi’: Netanyahu’s political future overshadows Israel’s election

    October 26, 2026
    Latest Posts

    Talks to sell PayPal to Stripe and Advent are heating up

    August 14, 2026

    Burnham announces £65m for drought-hit farmers after Labour pressure | Farming

    August 14, 2026

    Trump dismisses concerns about USS Abraham Lincoln, saying its record-breaking 250 days at sea ‘not nearly enough’ – live | US news

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    NASA’s Perseverance Offers Clues to Protect Crews From Mars Dust

    October 26, 2026

    Organized crime is growing along highway in a pristine section of the Amazon: Study

    October 26, 2026

    As students we never sought power – here’s how we reclaimed Serbia | Novak Simin

    October 26, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.