


Threat actors are abusing npm and its mirrors to host malicious HTML pages that impersonate Cloudflare CAPTCHAs to redirect visitors to attacker-controlled websites.
The technique was previously spotted in July by security researcher inf0stache, who found a ‘china_airlines’ npm package that used a fake Cloudflare verification page to redirect visitors to a malicious domain, and was also reported by IntelFusions.
In a later report, OX Security discovered 24 npm packages containing the same malicious HTML page hosted on npm and various mirrors.
However, unlike the typical npm supply-chain attacks we’ve seen lately, installing the packages does not infect a developer’s computer with malware or infostealers.
Instead, attackers use the npm registry as free storage for malicious HTML pages, which are then copied by mirroring platforms like UNPKG and npmmirror.
Because some of these platforms let individual files in npm packages be accessed directly in a browser, they effectively turn these developer sites into free web hosting for phishing pages.
“While the malware is simply a single HTML page inside the npm package, and while downloading it wouldn’t do harm, the threat actor’s use of npm isn’t to infect developers who install it, but to use the registry and its mirrors as a safe, validated storage for the malware,” explains OX Security.
BleepingComputer examined one of the packages identified in the campaign and found that it contained only two files, an index.html page and a package.json file that declared the HTML file as the package’s main file.
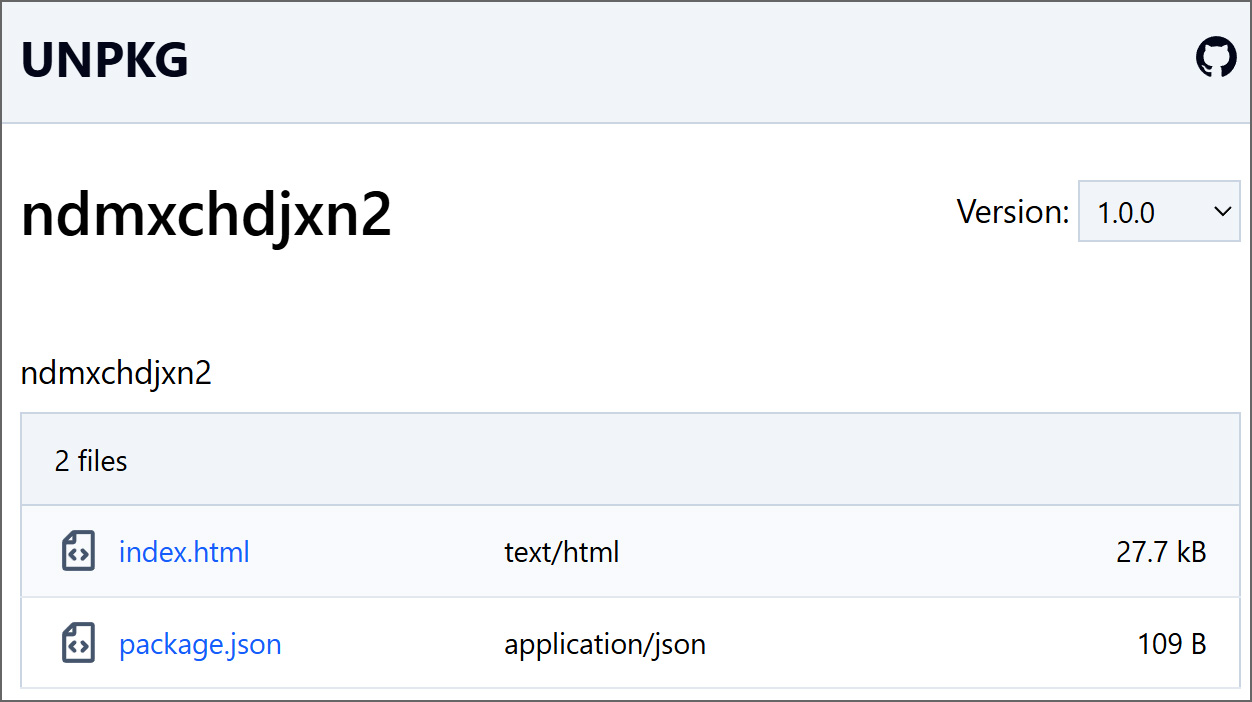
Source: BleepingComputer
When UNPKG mirrors the package, the HTML file can be opened directly in a browser using a URL such as https://unpkg[.]com/ndmxchdjxn2@1.0.0/index[.]html.
This causes the attacker’s HTML to be rendered in the browser from the legitimate unpkg.com domain rather than from infrastructure controlled by the threat actor, potentially bypassing security software that may have blocked a malicious site.
OX says this technique effectively turns npm mirrors into “free frontend hosts for malicious HTML pages and potentially other payloads as well.”
Malicious HTML acts as a redirector
The malicious HTML impersonates a Cloudflare security verification page that embeds Cloudflare’s legitimate Turnstile CAPTCHA service.
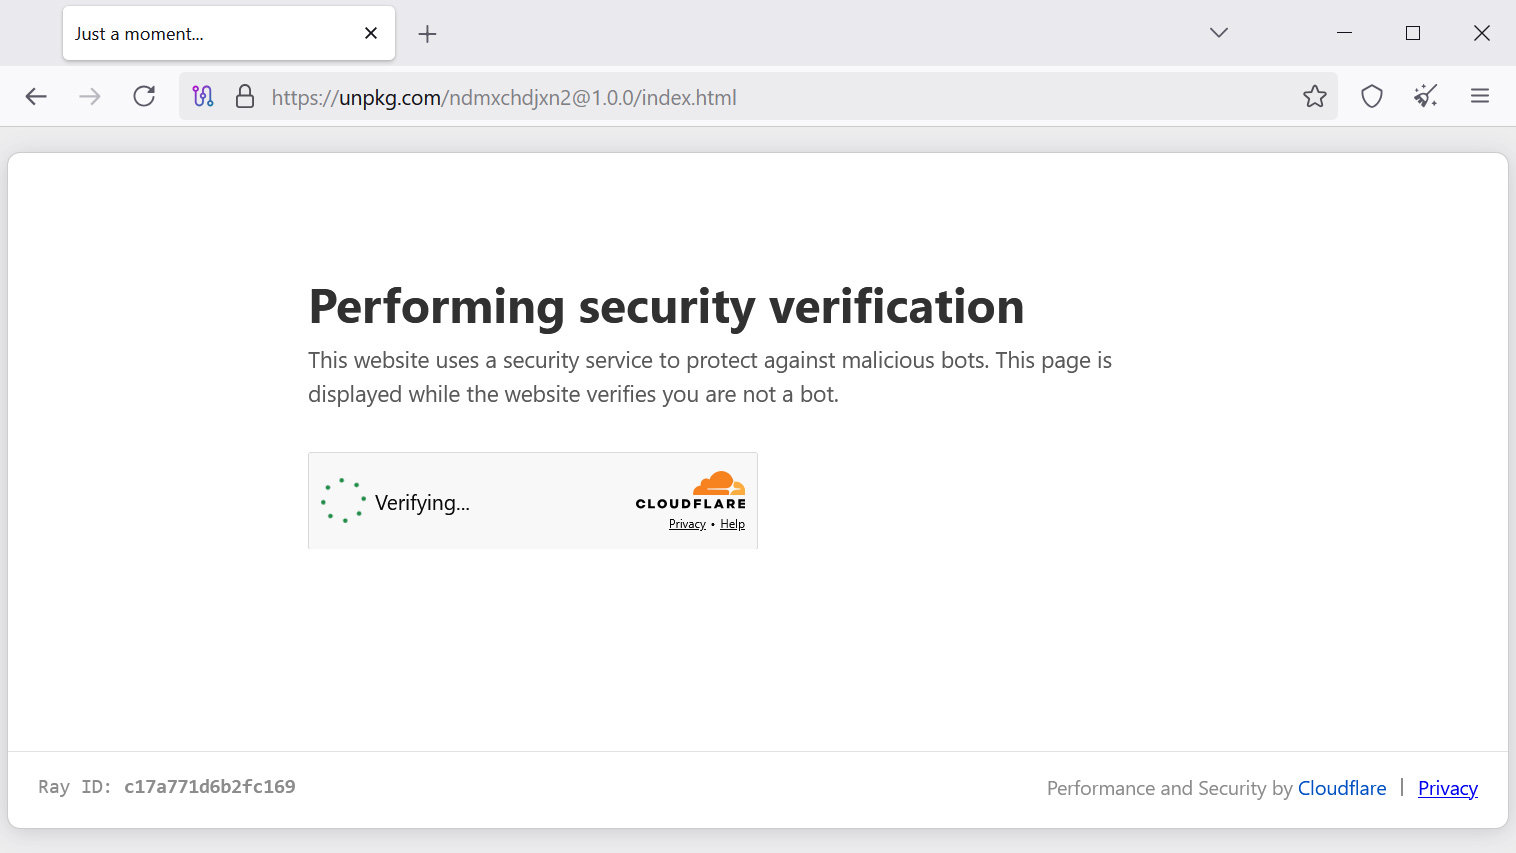
Source: BleepingComputer
Regardless of whether the verification succeeds, the page executes heavily obfuscated JavaScript that redirects the visitor to another site.
OX Security research team lead Moshe Siman Tov Bustan told BleepingComputer that earlier versions redirected to microcloud[.]homes in July and login[.]microsofte[.]live in August. The researchers said some of the earliest July redirects ultimately resolved to the legitimate Microsoft Outlook mail login site (https://outlook.office.com/mail).
BleepingComputer tested one of the malicious pages hosted through UNPKG and confirmed that it still redirects visitors to that domain.
This domain is not currently live, but it may be used to host a fake Microsoft login page.
The researchers say other packages switched to a different redirect method that uses api.keyval.org, a legitimate platform for storing key-value pairs.
According to the researchers, the newer code retrieves an encrypted value from the service, decrypts it in the browser, and then redirects the visitor to the decrypted URL.
This lets the attackers change the redirect URL remotely without modifying or republishing the npm package. At the time of OX’s research, the remotely configured destination redirected visitors to the legitimate ChatGPT website.
While OX says the value could be changed at any time to point to ClickFix or other phishing pages, the npm-hosted HTML reviewed by BleepingComputer does not perform a ClickFix attack.
These pages could also redirect visitors to phishing pages, malware downloads, or other attacker-controlled destinations.
OX also warns that npm packages may remain on mirrors after being removed from the official npm registry.
“Threat actors keep finding and using new and novel techniques not just to deliver malware, but to use legitimate infrastructure to store their payloads and data,” concluded OX.
The researchers recommend treating direct HTML requests to npm mirror domains as potentially suspicious.

Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
