

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Just two drinks a day may be far riskier than you think

    October 25, 2026

    Suspected Trappes gunman moved to police psychiatric unit

    October 25, 2026

    Rayner backs Burnham call for debate on return to free movement with EU | Labour

    October 25, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Just two drinks a day may be far riskier than you think
    • Suspected Trappes gunman moved to police psychiatric unit
    • Rayner backs Burnham call for debate on return to free movement with EU | Labour
    • In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuilding macOS Ransomware
    • Scientists reveal the hidden danger of missing blood pressure medication
    • Health board still paying for research with ‘unclear’ patient benefit
    • As a young man, magazines were my window to the world. That wonder will be lost when all the shops have gone | John Harris
    • 128 arrested after night of unrest and looting in Barcelona
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Sunday, October 25
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 26, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Swati KhandelwalAug 25, 2026Vulnerability / AI Security

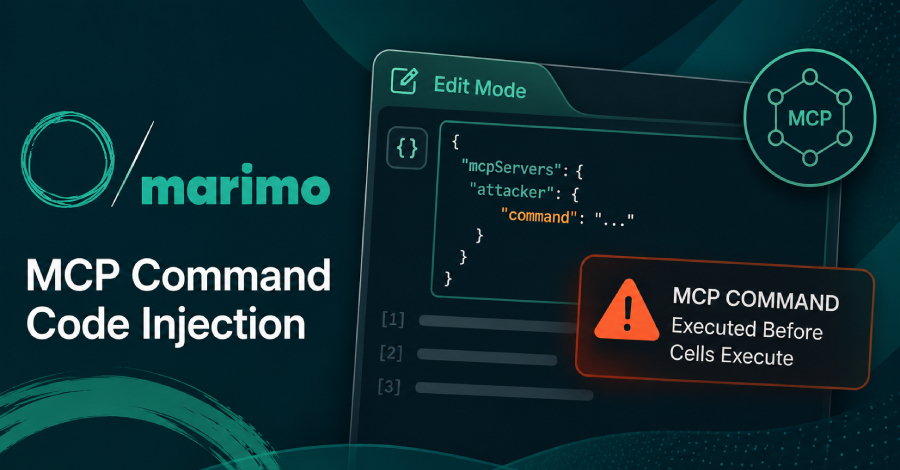
    Marimo has addressed a high-severity security flaw in its notebook software that allowed an attacker to execute an attacker-supplied Model Context Protocol (MCP) command in a specially crafted notebook, according to VulnCheck’s CVE Numbering Authority (CNA) record.

    The CNA record says the command can run as a local subprocess when the notebook is opened in edit mode.

    The vulnerability, tracked as CVE-2026-75149, is a code injection issue affecting versions prior to 0.23.15. VulnCheck’s CVE Numbering Authority (CNA) record assigns it a CVSS v4 score of 8.7 and a CVSS v3.1 score of 8.8, with user interaction required and no attacker authentication required.

    Marimo has addressed the issue in version 0.23.15. The CVE was published on August 19. Users running an affected release should move to a version outside the affected range.

    According to OSV’s CVE import, a crafted notebook can supply an attacker-controlled MCP server command through notebook configuration.

    Cybersecurity

    The victim opens the notebook in edit mode. The CNA record says the specified command is launched as a local subprocess before any notebook cell is executed.

    Marimo’s PEP 723 hardening patch treats notebook metadata as attacker-controlled and passes notebook-supplied configuration through an allowlist.

    The following notebook-supplied configuration sections are removed –

    • ai
    • mcp
    • completion
    • secrets
    • server

    The patch’s MCP regression case uses an attacker-controlled URL and verifies that the mcp section is removed. The CNA record supplies the separate command-to-subprocess behavior described for CVE-2026-75149.

    The Hacker News confirmed on August 25 that the current PyPI release is version 0.24.0, released August 17. Marimo’s version 0.23.15 release was published on July 23, 2026. Marimo’s security policy says security patches are provided for the latest stable release and encourages users to stay current.

    The CVE record credits Gregory Tan, who uses the handle Grg0rry, with discovering the flaw. The same handle also appears as a co-author on Marimo’s PEP 723 hardening commit.

    The same configuration boundary was addressed in VulnCheck’s separate CVE-2026-67618 advisory (CVSS score: 7.1), disclosed on August 4, 2026. That flaw affects Marimo versions before 0.23.15 and involves an attacker-controlled artificial intelligence (AI) base_url supplied through notebook metadata.

    For CVE-2026-67618, an operator opens the malicious notebook. The operator later makes an AI request. The configured endpoint then receives the operator’s API key without requiring a notebook cell to be executed.

    Cybersecurity

    CVE-2026-75149 is separate from the earlier CVE-2026-39987 flaw in Marimo. Marimo’s advisory for that vulnerability states that versions 0.20.4 and earlier were affected by a missing authentication validation on the /terminal/ws endpoint.

    Requests reaching that endpoint could obtain a full pseudo-terminal (PTY) shell. The shell could then execute arbitrary commands. Marimo lists version 0.23.0 as the patched version for the earlier flaw.

    cells Commands Edit Execute Flaw Marimo MCP mode notebook Run
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuilding macOS Ransomware

    Former Unit 8200 Officers Raise $34 Million for Agentic SecOps Startup Mave

    OpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox Communication

    Railway Says Intruder May Have Accessed Customer Secrets, Urges Credential Rotation

    How to Run Underdog Saluki 27B: 2-Bit Qwen3.8-27B Tool-Calling Guide

    Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Just two drinks a day may be far riskier than you think

    October 25, 2026

    Suspected Trappes gunman moved to police psychiatric unit

    October 25, 2026

    Rayner backs Burnham call for debate on return to free movement with EU | Labour

    October 25, 2026

    In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuilding macOS Ransomware

    October 25, 2026
    Latest Posts

    New studies portray Amazon as surprisingly resilient, but tipping point looms

    August 14, 2026

    How a brutal drought may have helped unleash yellow fever in Brazil

    August 14, 2026

    UK Authorities Continue Probe into Nigel Farage’s Crypto ‘Gifts’ after By-Election Win

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Just two drinks a day may be far riskier than you think

    October 25, 2026

    Suspected Trappes gunman moved to police psychiatric unit

    October 25, 2026

    Rayner backs Burnham call for debate on return to free movement with EU | Labour

    October 25, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.