


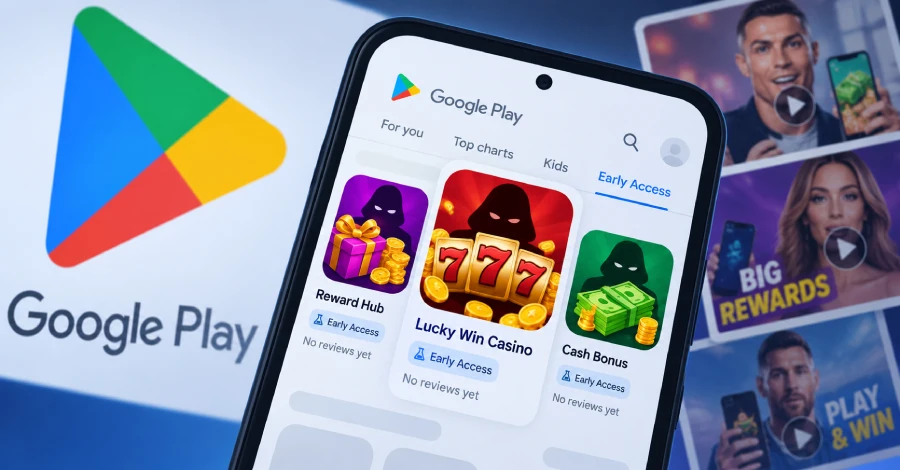
Bad actors are misusing Google Play’s Early Access program to push deceptive apps that claim to offer money, rewards, casino winnings, and premium content.
Early Access apps are apps that haven’t been released on the official Android app marketplace. The main idea behind the program is for developers to solicit user feedback for new applications or features they may be working on before their release.
One aspect worth highlighting is that users cannot leave public reviews or star ratings for apps that are available in Early Access. This has opened the door to a new kind of abuse where threat actors are pushing thousands of Early Access applications with deceptive content, including fake casino games and reward apps, as well as misleading utilities and titles that may infringe on third-party trademarks.
Among the identified apps is a Grand Theft Auto imitator named “Vice Streets: Open World” (APK package:com.gamblechaos.withfriends.game), which has more than 1 million downloads. The game has no reviews or ratings. It’s currently no longer available on the Google Play Store, although it’s not clear if it was taken down by Google or by the uploader themselves.
“The same feature that shields developers from unfair criticism also strips users of the earliest warning that an app cannot be trusted,” Bitdefender said in a statement.

Because users cannot leave critical reviews or poor ratings, the traditional trust signals no longer apply, allowing such apps to gain traction. These apps are said to be promoted through TikTok, Facebook, and other social media platforms using bogus ads that include videos featuring celebrity deepfakes generated using artificial intelligence (AI).
“A recurring pattern among suspicious Early Access apps involves promising cash rewards, PayPal payouts, cryptocurrency earnings, gift cards, free spins or casino jackpot,” the Romanian cybersecurity company said in a report shared with The Hacker News.
“Many of these applications rely on the same engagement loop. The user installs the app after watching an advertisement on TikTok or Facebook. They might even receive generous virtual rewards almost immediately, but when they reach a withdrawal threshold, progression slows dramatically. The promised payout will never arrive.”
The end goal is to generate illicit revenue by serving ad after ad. Another advantage that these Early Access casino-oriented apps have is that they allow them to sidestep many of the regulatory requirements legitimate gambling applications are required to comply with.
To get around the licensing, geofencing, and age verification restrictions, the casino-style apps masquerade as casual slot and puzzle games and are aggressively promoted via ads on social media platforms that lead unsuspecting users to Early Access apps in the Google Play Store or directly to various gambling websites.
Further analysis indicates that the lures used for these apps go beyond casino games, slot machines, and fake reward apps to include PDF readers, QR scanners, phone trackers, utility apps, and trademark-themed games.

“Google’s Early Access program remains a valuable tool for developers testing new ideas,” Bitdefender said. “Removing the comments and ratings protects legitimate developers from unfair review bombing, but it also removes one of the community’s strongest defenses against deceptive software.”
The Hacker News has contacted Google for comment, and we will update the story if we hear back.

The disclosure coincides with the emergence of multiple malware families targeting Android –
- Hagaseca, a remote access trojan spread via the THost9 loader that contains a worm component, which scans exposed Android Debug Bridge (ADB) services and installs the malware for persistence and remote control through shell execution, file transfers, tunneling, and downloadable modules.
- Mantax Otax, a hybrid mobile malware that brings together comprehensive spyware capabilities and ransomware functionality, allowing the operator to steal sensitive data, encrypt it on targeted older Android versions (Android 9 or earlier), and demand a ransom payment by locking the device screen. Language indicators and files from the victims suggest the activity is primarily focused on Indonesian targets.
- StreamRat, which abuses Android’s accessibility services and the MediaProjection API to control infected devices, serve overlays, and harvest sensitive data. The malware targets Spanish-speaking users through Meta and TikTok ads to direct users to counterfeit sites by masquerading as a free TV-streaming service named StreamTV Esp.
The development also coincides with GoldFactory’s use of the Gigabud banking trojan to install a companion Android app called Vwork, a weaponized fork of Shelter, to clone a target app inside a work profile with the goal of conducting financial fraud. Similar vi
“With full remote control, and where relevant a cloned banking app in place, the operator carries out transactions directly on the victim’s phone while a black screen hides what is happening,” Group-IB said. “A cloned environment is used to evade fraud protection controls.”
