

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Blackstone’s Jas Khaira joins Disrupt 2026

    October 2, 2026

    SWIFT Banking & Government Middleware Enables RCE

    October 2, 2026

    Bitcoin Price Surges Above $87,000 On Jobs Data

    October 2, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Blackstone’s Jas Khaira joins Disrupt 2026
    • SWIFT Banking & Government Middleware Enables RCE
    • Bitcoin Price Surges Above $87,000 On Jobs Data
    • La NASA abre solicitudes para próxima promoción de directores de vuelo
    • UNDP’s Alexander De Croo on Building Infrastructure in Ukraine, Afghanistan, and Gaza
    • Government wrong to claim over 14.5 million children used free bus scheme – Full Fact
    • How the Banco Master scandal injected chaos into Brazil’s presidential race | Elections News
    • Burnham to pass law scrapping pension triple lock before next election | Andy Burnham
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, October 2
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    CISA: Microsoft SharePoint flaw now exploited in ransomware attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 11, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    CISA confirmed today that ransomware gangs have begun abusing a high-severity Microsoft SharePoint remote code execution vulnerability, which has been flagged as actively exploited since early July.

    Tracked as CVE-2026-45659, this security flaw stems from a deserialization of untrusted data weakness and allows attackers with low privileges to execute arbitrary code on unpatched SharePoint servers.

    It can also be exploited in low-complexity attacks because (as Microsoft explained in May when it released security updates for SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition) “an attacker does not require significant prior knowledge of the system and can achieve repeatable success with the payload against the vulnerable component.”
    image

    The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the vulnerability to its Known Exploited Vulnerabilities Catalog (KEV) on July 1, ordering Federal Civilian Executive Branch (FCEB) agencies to secure their servers within three days.

    “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise,” the U.S. cybersecurity agency warned at the time.

    In a subsequent advisory, the cybersecurity agency also urged security teams to monitor affected servers for signs of exploitation, apply Microsoft’s latest patches, verify successful installation, and shorten patching cycles.

    It also recommended enabling Windows Antimalware Scan Interface (AMSI integration for SharePoint web applications and using Microsoft Defender Antivirus (MDAV) detections to detect and remediate compromise.

    Internet security watchdog group Shadowserver currently tracks over 8,500 Microsoft SharePoint servers exposed online, with over 200 of them unpatched against the CVE-2026-45659 vulnerability.
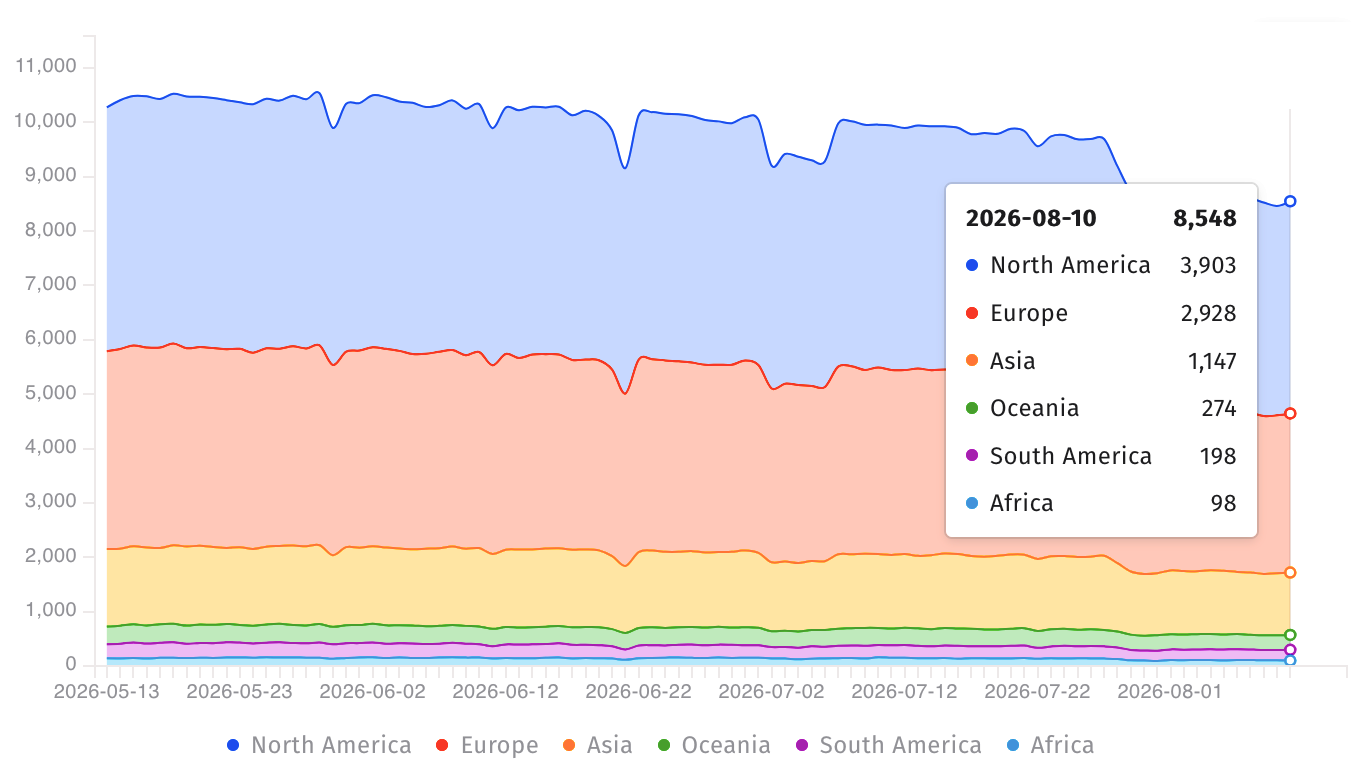
    Internet-exposed SharePoint servers
    Internet-exposed SharePoint servers (Shadowserver)

    While Microsoft has yet to update the CVE-2026-45659 advisory to tag it as exploited, CISA has now also flagged it as abused by ransomware gangs in a Tuesday update to the KEV Catalog.

    Since November 2021, the cybersecurity agency has flagged 14 actively exploited Microsoft SharePoint vulnerabilities, with eight of them also exploited in ransomware attacks.

    In June, CISA also confirmed that ransomware gangs now exploit a high-severity Microsoft Defender privilege escalation vulnerability (dubbed BlueHammer), which was also targeted as a zero-day to access the Security Account Manager (SAM) database, which contains password hashes for local accounts.

    The security flaw (tracked CVE-2026-33825) was leaked by a security researcher known as “Nightmare Eclipse” in early April, together with proof-of-concept exploit code.

    However, as with CVE-2026-45659, Microsoft has yet to confirm that the CVE-2026-33825 security flaw is being exploited in the wild.

    article image

    Security teams log 54% of successful attacks and alert on just 14%. The rest move through your environment unseen.

    The Picus whitepaper shows how breach and attack simulation tests your SIEM and EDR rules so threats stop slipping by detection.

    Get the whitepaper

    attacks CISA Exploited Flaw Microsoft ransomware SharePoint
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    SWIFT Banking & Government Middleware Enables RCE

    In Other News: $15K iCloud Spoofing Bugs, AI Policy Experts Phished, Adblocker Spies on AI Chats

    US sanctions Tren de Aragua gang members in ATM hacks crackdown

    Vulnerability Backlogs Are an Ownership Problem

    macOS Users Targeted by Fake Zoom Installer Carrying CloudSyncD Backdoor

    Ukraine calls for tighter sanctions as Russian attacks spark Kyiv gridlock | Russia-Ukraine war News

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Blackstone’s Jas Khaira joins Disrupt 2026

    October 2, 2026

    SWIFT Banking & Government Middleware Enables RCE

    October 2, 2026

    Bitcoin Price Surges Above $87,000 On Jobs Data

    October 2, 2026

    La NASA abre solicitudes para próxima promoción de directores de vuelo

    October 2, 2026
    Latest Posts

    Lime bikes hurtling around the city: is this the revenge of a priced-out generation? | Andy Beckett

    August 8, 2026

    Clarity Act Delayed Until September, Trump Praises Bitcoin

    August 8, 2026

    North Carolina Ports confirms cyberattack disrupting operations

    August 8, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Blackstone’s Jas Khaira joins Disrupt 2026

    October 2, 2026

    SWIFT Banking & Government Middleware Enables RCE

    October 2, 2026

    Bitcoin Price Surges Above $87,000 On Jobs Data

    October 2, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.