

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Farage aide caught in donor sting attended Egypt retreat with JL Partners – POLITICO

    September 17, 2026

    Plaid warned not to cut help for poorer children if it wants Labour to back budget

    September 17, 2026

    HSBC axes $38,000 school fee perk for new Hong Kong bankers

    September 17, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Farage aide caught in donor sting attended Egypt retreat with JL Partners – POLITICO
    • Plaid warned not to cut help for poorer children if it wants Labour to back budget
    • HSBC axes $38,000 school fee perk for new Hong Kong bankers
    • The streamers are fighting over Halloween
    • Google Research Introduces Retrieve-for-Train (R4T): An RL-Compiled Diffusion Retriever for 12× to 20× Faster Query Fan-Out
    • Chinese hackers use SparroWocky malware in govt espionage attacks
    • Bitcoin holds $76,000 after Fed rate hike, but 4 demand signals flash warning
    • NASA Visits Schools Strengthening Florida’s Skilled Workforce
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, September 17
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Chinese hackers use SparroWocky malware in govt espionage attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 17, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    The China-linked espionage group FamousSparrow has been using a new backdoor named SparroWocky in attacks on government organizations in Latin America.

    The operations have been ongoing for more than a year, with the new malware replacing the previously used SparrowDoor custom backdoor.

    ESET researchers observed SparroWocky in attacks targeting organizations in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.

    The researchers believe the threat actor’s objective was to collect intelligence on Latin American governments’ responses to increasing U.S. pressure on Chinese economic interests.
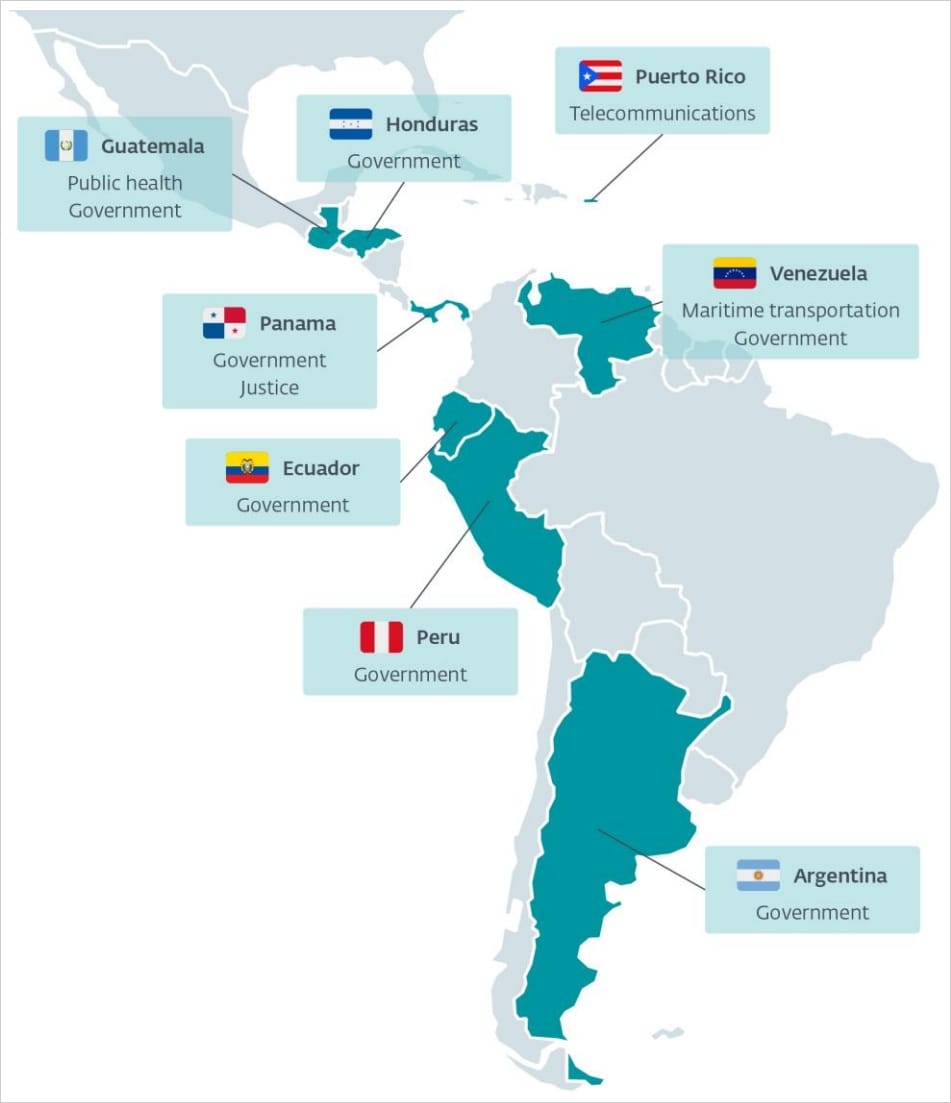
    FamousSparrow victims
    FamousSparrow victims
    Source: ESET

    ESET’s analysis revealed that SparroWocky is a modular, full-blown C++ backdoor that includes code from open-source projects.

    The malware features anti-analysis mechanisms, like manipulating low-level structures in memory and patching code at runtime. SparroWocky’s capabilities include:

    • run commands and executable files
    • load and execute Beacon Object Files in memory
    • collect system, network, user, domain, and Windows-version details
    • enumerate drives, directories, files, displays, and active user sessions
    • upload, download, copy, move, rename, and delete files
    • capture screenshots every 500 milliseconds, transmitting only changed screen regions after the first full-screen image
    • create processes in another logged-in user’s session
    • operate as a TCP proxy and forward connections
    • remove its persistence and delete its own files

    According to the researchers, the malware is deployed via DLL side-loading after a loader decrypts the RC4-encoded payload contained in a .dat file and maps it directly in memory for evasion.

    The malware features several evasion mechanisms, including call stack and threat origin spoofing, dynamic API resolving, and disguising malicious in-memory code and DLLs as legitimate Windows components.

    To hide from security solutions, SparroWocky is intercepting the Windows thread creation process to alter the start address.

    “SparroWocky uses the MinHook library to hook the CreateThread function in order to conceal the original lpStartAddress parameter from security products.

    “Essentially, any thread created by SparroWocky would have AnimateWindow as the starting address, which would likely be considered legitimate by a security product,” ESET explains.

    SparroWocky establishes persistence either through a Windows service (ProcAuditManager) or by adding a Windows registry key (SnapCart) under HKLM or HKCU, depending on the available privileges.

    The researchers note that the malware’s architecture and evasion techniques “indicate strong knowledge of anti-analysis tricks and Windows internals,” which aligns with their attribution to a well-resourced and experienced threat group.

    While analyzing the attacks, ESET found at least 18 command-and-control (C2) addresses communicating with the malware directly over port 443 or 8080, or through HTTP and SOCKS5 proxies.

    ESET’s telemetry indicates that from mid-2025, FamousSparrow’s focus has been primarily on targets in the Latin America region.

    The company’s report includes a technical analysis of the SparroWocky backdoor and shares a list of indicators of compromise (IoCs) associated with this activity.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    attacks Chinese Espionage govt hackers Malware SparroWocky
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    16 governance tools for securing your AI fleet

    Cisco warns of max severity ISE zero-day exploited in attacks

    Parallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install Fix

    Cyber Op Targets South Korean Media & Automotive Sectors

    BragJack Attack Can Turn a Browser’s Agentic AI Against It

    Attacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 Repositories

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Farage aide caught in donor sting attended Egypt retreat with JL Partners – POLITICO

    September 17, 2026

    Plaid warned not to cut help for poorer children if it wants Labour to back budget

    September 17, 2026

    HSBC axes $38,000 school fee perk for new Hong Kong bankers

    September 17, 2026

    The streamers are fighting over Halloween

    September 17, 2026
    Latest Posts

    What is Trump Media’s Truth API and why is it controversial?

    August 4, 2026

    How ProPublica Tested Hundreds of Omaha Homes for Lead — ProPublica

    August 4, 2026

    Golar LNG raises $600 million loan with FLNG business expansion in mind

    August 4, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Farage aide caught in donor sting attended Egypt retreat with JL Partners – POLITICO

    September 17, 2026

    Plaid warned not to cut help for poorer children if it wants Labour to back budget

    September 17, 2026

    HSBC axes $38,000 school fee perk for new Hong Kong bankers

    September 17, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.