

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Mozambique safari operator wins conservation award at COP17

    October 23, 2026

    Israel’s Netanyahu Orders Large-Scale Military Operation in West Bank City of Hebron

    October 23, 2026

    Alaska Ad Missing Context in Attacking Peltola’s Border Votes

    October 23, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Mozambique safari operator wins conservation award at COP17
    • Israel’s Netanyahu Orders Large-Scale Military Operation in West Bank City of Hebron
    • Alaska Ad Missing Context in Attacking Peltola’s Border Votes
    • Jihadists reportedly urge attacks during protests in Portugal and Spain
    • Abandoned Popcorn Time app exposed millions of devices to RCE attacks
    • A tiny defect in a crystal reveals a big quantum surprise
    • A Homeowner’s Last Stand Against Alabama Power
    • The Guardian view on Europe’s protests: the social contract has broken – and young people want solutions | Editorial
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Friday, October 23
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Abandoned Popcorn Time app exposed millions of devices to RCE attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 23, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Researchers remotely disabled a vulnerable updater in the abandoned Time4Popcorn app, a fork of the Popcorn Time BitTorrent client, closing a security flaw that could have allowed attackers to execute malicious code with elevated privileges on millions of computers.

    The vulnerability, tracked as CVE-2026-30612, affects Windows and macOS updaters that contacted the app’s abandoned domain (popcorntimeupd.xyz) over unencrypted HTTP and accepted executables without verifying digital signatures.

    Anyone controlling the update domain could manipulate HTTP traffic and execute code as SYSTEM on Windows and as root on macOS.

    The Popcorn Time app featured a Netflix-style interface that integrated BitTorrent downloads, allowing users to consume illegal content right directly inside the app.

    The project was abandoned for legal reasons but later relaunched as a legitimate content-streaming app. However, forks such as Time4Popcorn emerged under the Popcorn Time name, quickly attracting millions of users.

    Researchers at Eye Security discovered the security risk after registering the popcorntimeupd.xyz domain and observed up to 3 million Windows and 350,000 macOS client connections to Time4Popcorn.
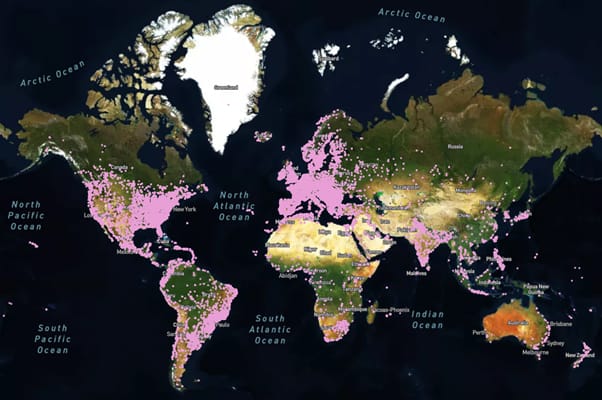
    Location of users
    Location of Time4Popcorn ​​​​users

    Source: Eye Security

    Connections came from residential ISPs and corporate, government, and military networks. However, none of the users appeared to be actively using the app, suggesting it had been installed and forgotten.

    “If we were able to send an update, we could potentially get code execution on millions of systems,” Eye Securit notes, adding that “the impact would be severe if this were to fall into the wrong hands.”

    Following this discovery, the researchers registered 14 more domains associated with the service.

    Securing the systems

    Between November 2025 and March 2026, Eye used the vulnerable update mechanism to deliver remediation code that stopped and disabled the updater.

    Their payload collected no host data or telemetry, and deleted no files on the users’ computers, keeping their actions within a fully legal context.

    Eye explains that it had to modify its payload during testing to evade antivirus products that flagged it for disabling a service.

    After deploying the remediation, Eye recorded 2 million update downloads, and by March 1 this year, requests to its update domain dropped by 98%.

    Following the successful completion of the remediation operation, domain ownership was passed to the non-profit security organization The Shadowserver Foundation.

    Despite this success, the researchers warned that the risk is not fully eliminated for users of the app.

    First, Android users remain exposed as installing an update would require user interaction, and researchers could not disable the updater remotely for the mobile platform.

    Second, the Time4Popcorn app uses a severely outdated Chrome engine from 2014, with no sandbox protections, which could be exploited in attacks.

    The best course of action would be for users to remove the software entirely from their systems.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    abandoned app attacks devices exposed millions Popcorn RCE time
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Jihadists reportedly urge attacks during protests in Portugal and Spain

    In Other News: Tor Exit Relays Hijacked, Banks Spot Rogue AI Agents, Self-Rebuilding macOS Ransomware

    BlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing Revocations

    Microsoft: Windows Server 2016 reaches end of support in January

    Dual BIOS: The laptop security feature SMBs don’t know they need

    Cyber Insurance’s New Reality: Underwriting Isn’t Enough

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Mozambique safari operator wins conservation award at COP17

    October 23, 2026

    Israel’s Netanyahu Orders Large-Scale Military Operation in West Bank City of Hebron

    October 23, 2026

    Alaska Ad Missing Context in Attacking Peltola’s Border Votes

    October 23, 2026

    Jihadists reportedly urge attacks during protests in Portugal and Spain

    October 23, 2026
    Latest Posts

    ‘This is hell’: British widow ‘sick’ with worry over threat of being removed from Sweden | Sweden

    August 14, 2026

    Prichard Colon dies from boxing injury that resulted in 221-day coma | Boxing News

    August 14, 2026

    Weather forecasts once gave Britons something safe to chat about. Not any more | Andy Beckett

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Mozambique safari operator wins conservation award at COP17

    October 23, 2026

    Israel’s Netanyahu Orders Large-Scale Military Operation in West Bank City of Hebron

    October 23, 2026

    Alaska Ad Missing Context in Attacking Peltola’s Border Votes

    October 23, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.