

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment

    November 2, 2026

    Melting permafrost has birthed a new type of large landslide

    November 2, 2026

    Berlin unveils blueprint to catch up on AI – POLITICO

    November 2, 2026
    Facebook X (Twitter) Instagram
    Trending
    • DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment
    • Melting permafrost has birthed a new type of large landslide
    • Berlin unveils blueprint to catch up on AI – POLITICO
    • No 10 defends flight to Caribbean going via Manchester to pick up Burnham | Andy Burnham
    • Hackers disrupt refrigeration systems at European supermarkets
    • IceCube detects ghost particles with 10 billion times the energy of solar neutrinos
    • Shell and Hornbeck Offshore seal multiple deals for deepwater services
    • Did Trump say US is ‘making money’ like it never has before while downplaying high gas prices?
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Monday, November 2
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Over 1,000 GitLab servers vulnerable to ongoing RCE attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKNovember 2, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Over 1,000 Internet-exposed GitLab servers are still unpatched against a maximum-severity flaw actively exploited in remote code execution attacks.

    Tracked as CVE-2026-97229, this vulnerability stems from an integer overflow weakness and was discovered in the CI/CD Regular Expression Compiler, which parses and evaluates regular expressions in pipeline configuration files.

    “GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary code on the GitLab server via a specially crafted regular expression in a CI/CD configuration, due to insufficient regular expression validation,” the company explained on October 12 when it released security patches to address the security issue in GitLab Community Edition (CE) and Enterprise Edition (EE) versions 19.4.2, 19.3.5, and 19.2.8.

    image

    “These versions contain important bug and security fixes, and we strongly recommend that all self-managed GitLab installations be upgraded to one of these versions immediately. GitLab.com is already running the patched version. GitLab Dedicated customers do not need to take action,” it added.

    On Friday, the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed that attackers have begun exploiting the flaw in the wild and added CVE-2026-97229 to its Known Exploited Vulnerabilities (KEV) Catalog, ordering federal agencies to secure their servers by Sunday.

    Although GitLab released patches three weeks ago, threat watchdog Shadowserver revealed over the weekend that it tracks more than 1,000 unpatched GitLab servers exposed to ongoing attacks.
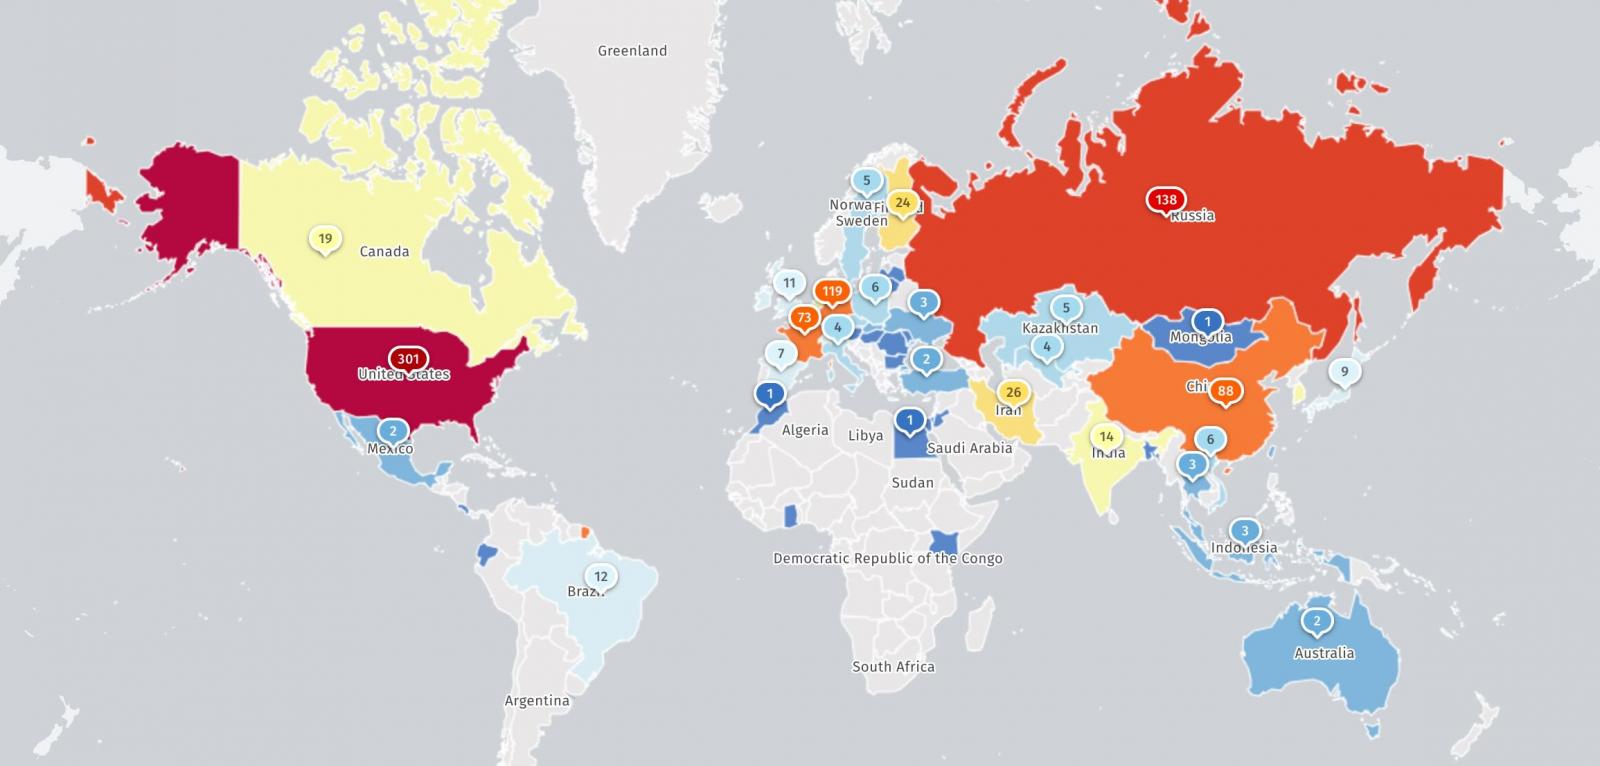
    Vulnerable GitLab instances exposed online
    Vulnerable GitLab instances exposed online (Shadowserver)

    ​​CVE-2026-97229 is the latest in a series of GitLab security issues addressed since the start of the year. In January, GitLab fixed a high-severity flaw (CVE-2026-0723) that lets attackers bypass two-factor authentication, and in September, a maximum-severity vulnerability (CVE-2026-85706) in the repository commits API that can be exploited to steal credentials and other secrets.

    CISA also flagged CVE-2026-85706 as actively abused in the wild after cybersecurity firm watchTowr reported that attackers had already begun scanning for vulnerable GitLab servers.

    Last month, it addressed another maximum-severity Regular Expression Compiler bug (CVE-2026-110264) that lets threat actors run arbitrary code on targeted instances.

    “We are currently tracking over 1000 GitLab instances vulnerable to CVE-2026-97229 (on @CISACyber KEV) and over 11300 instances vulnerable to CVE-2026-110264 (out of around 39K GitLab instances we see daily),” Shadowserver said on Sunday.

    Since November 2021, CISA has added six GitLab flaws to its catalog of actively exploited vulnerabilities, one of which has also been used in ransomware attacks.

    GitLab says its DevSecOps platform has over 70 million registered users and is used by more than 50% of Fortune 100 companies worldwide.


    article image

    Adaptive Security’s AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.

    See what’s getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.

    Start your free email security scan.

    attacks GitLab ongoing RCE Servers vulnerable
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment

    Hackers disrupt refrigeration systems at European supermarkets

    Malicious Claude Code Extension Served in Cursor Supply Chain Attack

    Chainalysis Discloses Data Breach Following AI-Driven Cyberattack

    Ivanti patches two more Connect Secure zero-days chained in attacks

    Hurricane Damage to a Florida Domestic Violence Shelter Shows Climate’s Stress on Vulnerable Groups

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment

    November 2, 2026

    Melting permafrost has birthed a new type of large landslide

    November 2, 2026

    Berlin unveils blueprint to catch up on AI – POLITICO

    November 2, 2026

    No 10 defends flight to Caribbean going via Manchester to pick up Burnham | Andy Burnham

    November 2, 2026
    Latest Posts

    Is the world experiencing more earthquakes now than before? | Earthquakes News

    August 17, 2026

    Disabled creatives like me are behind many of your favourite shows – so why has our work support been withdrawn? | Annalisa Dinnella

    August 17, 2026

    A little-known protein may be fueling Alzheimer’s — and scientists found a way to block it

    August 17, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment

    November 2, 2026

    Melting permafrost has birthed a new type of large landslide

    November 2, 2026

    Berlin unveils blueprint to catch up on AI – POLITICO

    November 2, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.