

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    France says EU’s ‘Made in Europe’ law should not include the UK | European Union

    September 24, 2026

    Ministers reject dog ownership licence scheme

    September 24, 2026

    Google’s Gemini Can Now Make Calls for You on Pixel Phones

    September 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • France says EU’s ‘Made in Europe’ law should not include the UK | European Union
    • Ministers reject dog ownership licence scheme
    • Google’s Gemini Can Now Make Calls for You on Pixel Phones
    • Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer
    • Institutions Held Their Bitcoin Through Crash: Report
    • US-India Satellite Captures Time-lapse Video of Volcanic Eruption
    • A Bill to Abolish Watchdog Group Is Making Its Way Through Congress
    • The Guardian view on a supersized El Niño: a natural phenomenon and human folly are a lethal combination | Editorial
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, September 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 24, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    The “third-party[.]com” domain, commonly used as a documentation placeholder, has been observed serving a ClickFix lure to Windows browsers while displaying a harmless decoy to other users.

    “third-party[.]com has been a generic documentation placeholder for years, the same role example.com plays,” Manifold Security’s Head of Research, Ax Sharma, said. “Unlike ‘example[.]com,’ third-party[.]com is not IANA-reserved. Anyone could register it, and someone did. Every doc, test, and skill that hard-coded it now points readers at attacker infrastructure.”

    As of writing, the domain has been marked as malicious and unsafe on both VirusTotal and Google’s Safe Browsing list.

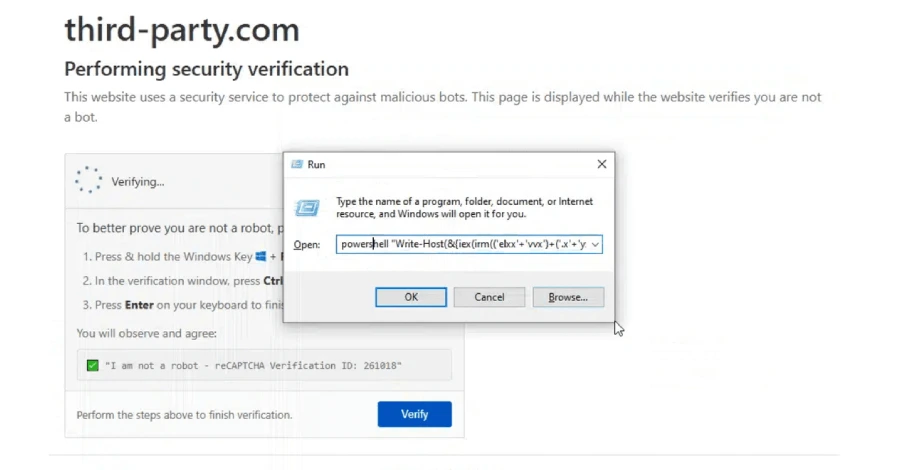
    ClickFix is a social engineering attack technique in which either malicious or legitimate-but-compromised websites display error messages, browser alerts, or CAPTCHA verification prompts, tricking users into copying and executing hidden commands via the Windows Run dialog or Terminal to “fix” the issue.

    Cybersecurity

    Often, web pages using ClickFix rely on clipboard hijacking to automatically inject malicious script or commands into the victim’s clipboard for subsequent pasting on Windows Run dialog or macOS Terminal. This approach is also sometimes referred to as pastejacking.

    According to Manifold Security, the domain has been serving the ClickFix lure since at least June 2026. Windows users visiting the page are shown a Cloudflare check that poisons the victim’s clipboard and instructs them to paste and run the command via the Windows Run dialog. The pasted command is designed to extract and run a remote PowerShell payload.

    When a macOS user visits the same page, the fake security verification prompt shows an error: “macOS is not supported. This website requires a Windows PC to access. Please try again from a Windows device.”

    A search on GitHub shows that the domain is referenced in over 1,700 public repositories, including those related to AI agent skills and MCP-server docs that cite “third-party[.]com” as an example endpoint.

    “In every one of those places it is exactly what it looks like: a placeholder, an example, a stand-in, and entirely reasonable use by the teams involved,” Sharma noted. “It is also, now, a live pointer to a ClickFix server.”

    This weaponization of a blindly trusted domain, in turn, can open up avenues for prompt injection and other unintended behaviors.

    To counter the threat, it’s advised to audit their documentation and treat non-reserved placeholder domains (e.g., yourcompany[.]com, mycompany[.]com, your-api[.]com, and their lookalikes) as squattable and open to abuse by threat actors, who can register them and serve malicious content.

    Developers working on skills, documentation, or test cases are recommended to use reserved placeholders like “example[.]com” (or “example[.]org,” “example[.]net”) only and avoid using plausible-sounding domains that are not under their control.

    “You can scan the skill, read the file, resolve the domain from your analysis box, and conclude it is fine, and be completely wrong about what a Windows user’s agent receives when it follows the same link,” Manifold Security pointed out. “A file scan cannot see what a website decides to send. The tell only appears at request time, from the caller that matters.”

    The disclosure comes as Manifold said it has since identified 13 more placeholder domains that are not IANA-reserved, with two of them – yoursite[.]com and your-domain[.]com – serving scams and scareware to macOS visitors and an ordinary parking page to other users.

    Cybersecurity

    “On a macOS browser, your-domain[.]com showed a fake ‘MacOS Security Center’ claiming four viruses and selling a counterfeit McAfee renewal at 55% off,” security researcher Cody Nash said. “On another macOS render, yoursite[.]com showed a counterfeit ZDF news article advertising an investment scheme.”

    The complete list of domains, each of them are pass static checks, is as follows –

    • your-domain[.]com
    • yourdomain[.]com
    • your-site[.]com
    • yoursite[.]com
    • your-app[.]com
    • yourapp[.]com
    • myapp[.]com
    • mysite[.]com
    • acme[.]com
    • company[.]com
    • mycompany[.]com
    • vendor[.]com
    • foo[.]com

    To make matters worse, the two scam-scarware-serving sites are present in hundreds of thousands of GitHub files and hundreds of agent skills. “Scareware and investment fraud are a lower threat than clipboard malware, the exposure they ride on is far larger, and none of it showed up in any static check we ran,” Nash said.

    Content Malicious Placeholder Referenced Repositories serves thirdparty.com
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer

    Kontext Security Emerges With $4 Million for AI Agent Runtime Controls

    OpenAI Agents Probed Websites for Vulnerabilities While Fetching Public Data

    Corp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects Calls

    Windows 11 KB5124010 update released with 46 changes and fixes

    CISA: Ransomware gangs now exploiting critical TeamCity flaw

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    France says EU’s ‘Made in Europe’ law should not include the UK | European Union

    September 24, 2026

    Ministers reject dog ownership licence scheme

    September 24, 2026

    Google’s Gemini Can Now Make Calls for You on Pixel Phones

    September 24, 2026

    Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer

    September 24, 2026
    Latest Posts

    Spain’s Pedro Sánchez is a progressive outlier in Europe – and over Ceuta, he is being made to pay for it | Eoghan Gilmartin

    August 6, 2026

    Putin Signs Law For Russia To Regulate Crypto Exchanges

    August 6, 2026

    Canadian pleads guilty to Snowflake cloud data-theft attacks

    August 6, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    France says EU’s ‘Made in Europe’ law should not include the UK | European Union

    September 24, 2026

    Ministers reject dog ownership licence scheme

    September 24, 2026

    Google’s Gemini Can Now Make Calls for You on Pixel Phones

    September 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.