

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Diesel surge costs European drivers €203mn per day

    September 23, 2026

    ‘We’re already fighting yesterday’s battle’: Greece’s prime minister gets candid about AI

    September 23, 2026

    OpenAI Releases GPT-6 Sol and Luna: 50% Cheaper API Pricing and Benchmarks

    September 23, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Diesel surge costs European drivers €203mn per day
    • ‘We’re already fighting yesterday’s battle’: Greece’s prime minister gets candid about AI
    • OpenAI Releases GPT-6 Sol and Luna: 50% Cheaper API Pricing and Benchmarks
    • Check Point warns of Management Server zero-day exploited in attacks
    • White-Hat Hackers Route Coldcard Exploit Bitcoin Into ‘Recovery Trust’
    • Boom Year for Desert Blooms
    • Open wounds and eyes that can’t close – women warn about cheap bleph eyelid surgery
    • Western Vacillation Encourages Putin’s Aggression
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, September 23
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 23, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananSep 22, 2026Supply Chain Attack / Malware

    Cybersecurity researchers have disclosed details of a malicious npm package named “tw-pkgprobe-7731” that masquerades as a security tool targeting developers integrating Twilio into their applications, while stealthily attempting to harvest sensitive data.

    The package, named “tw-pkgprobe-7731,” was first uploaded to the npm registry in mid-August 2026 by an npm account named “twdepprobe7731.” In total, 11 versions of the package were published in quick succession on the same day over an approximately 45-minute time period. The npm user account no longer exists as of writing.

    “The first version of tw-pkgprobe-7731 posed as an authorized security research probe,” ReversingLabs researcher Lucija Valentić said in a report published today.

    “Comments inside the package describe it as an ‘Authorized bug-bounty research probe (Twilio HackerOne program)’ that ‘runs only inside Twilio’s serverless packager sandbox’ and ‘collects local process/host context and writes it next to itself; no destructive action.'”

    Upon execution, the package first checks if the current environment is a Twilio developer environment. It immediately exits if that’s not the case.

    Cybersecurity

    Should the check pass, the malware proceeds to extract environment variables along with system details like mounts, temporary folders, and various configurations. The gathered information is then exfiltrated via a webhook.

    Subsequent versions of the npm package (viz., versions 1.0.1, 1.0.2, and 1.0.3) have been found to focus on developers using Twilio APIs, specifically searching for folders tied to specific Twilio account String Identifiers (SIDs). Most importantly, it avoids taking any action if there exists a folder with a specific SID name.

    “Otherwise, if matching target folders were found, it scanned installed npm packages and node_modules to inject a custom npm PoC package, creating package.json and index.js inside,” ReversingLabs explained.

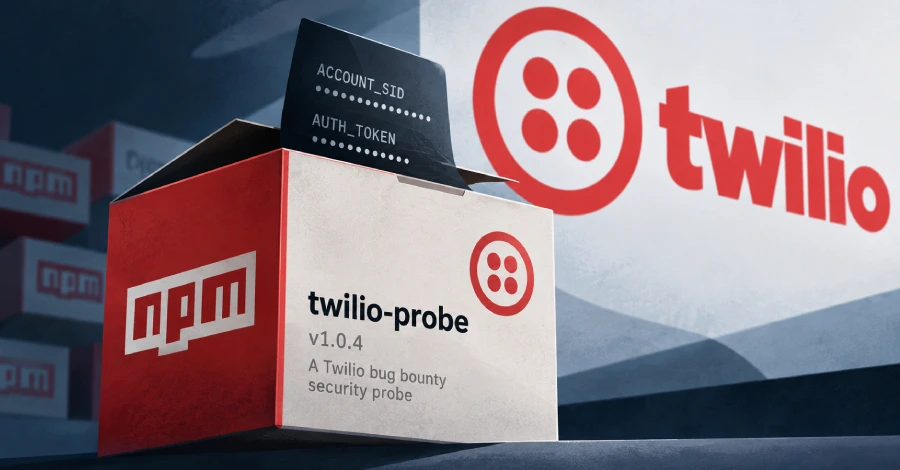
    Version 1.0.4 is said to have introduced an added capability to exfiltrate process.env.ACCOUNT_SID and process.env.AUTH_TOKEN, effectively compromising the victim’s Twilio credentials and potentially allowing the threat actor to authorize billing and trigger communication.

    However, the final three versions (i.e., 1.0.8, 1.1.0, and 1.1.1) “reverted to the basic probing profile of the package seen in version 1.0.0,” dropping the malicious functionality incorporated in prior iterations.

    In addition, the last two versions have been found to conduct OSINT gathering by probing various Twilio-related hosts, such as support-api.us1.twilio[.]com, kafka-ui.au1.twilio[.]com and litellm.ai-services.corp.twilio[.]com, even fetching AWS metadata located at “169.254.169[.]254/latest/meta-data/.”

    Cybersecurity

    Given these unusual course reversals, it’s unclear what the end goals are and if it was published as part of a bug bounty program. However, ReversingLabs said the package versions did not follow Twilio’s bug hunting guidelines listed on HackerOne.

    “In other words, these packages clearly violate the basic security research guidelines Twilio established, which suggests that the packages had malicious intent,” Valentić said. “While the threat actor behind the campaign attempted to mask malicious features in certain releases by surrounding them with seemingly benign features and code, they made no real effort to obscure the malicious code or hide their activity.

    “There is no obfuscation, typosquatting, or attempt to make the publishing npm account look legitimate – tactics we’ve routinely seen in previous campaigns. This suggests that a less sophisticated threat actor is responsible for the malicious campaign targeting Twilio developers.”

    BugBounty Credentials Exfiltrate Malicious npm package poses probe Twilio
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Check Point warns of Management Server zero-day exploited in attacks

    Only 13% of OT Network Segments Are Fully Isolated: Analysis

    ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach

    Sweden fines Miljödata $183,000 over breach affecting 2.2 million

    Rogue external MFA providers can steal passwords during logins

    WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Diesel surge costs European drivers €203mn per day

    September 23, 2026

    ‘We’re already fighting yesterday’s battle’: Greece’s prime minister gets candid about AI

    September 23, 2026

    OpenAI Releases GPT-6 Sol and Luna: 50% Cheaper API Pricing and Benchmarks

    September 23, 2026

    Check Point warns of Management Server zero-day exploited in attacks

    September 23, 2026
    Latest Posts

    COLDCARD security audit phishing attack installs remote access tool

    August 5, 2026

    Reddit aims to make ‘karma’ less important for first-time posters with shift to AI moderation tools

    August 5, 2026

    Right turn on green: is the Telegraph changing its tune on the climate? | Daily Telegraph

    August 5, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Diesel surge costs European drivers €203mn per day

    September 23, 2026

    ‘We’re already fighting yesterday’s battle’: Greece’s prime minister gets candid about AI

    September 23, 2026

    OpenAI Releases GPT-6 Sol and Luna: 50% Cheaper API Pricing and Benchmarks

    September 23, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.