


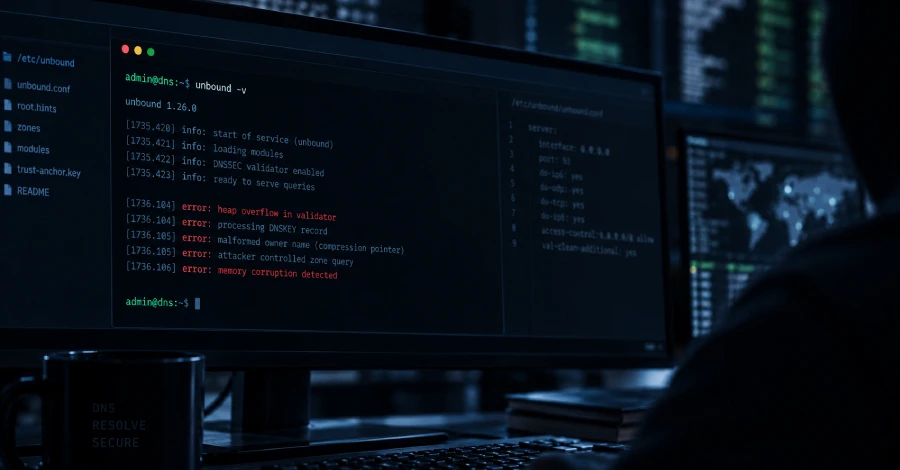
Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday.
An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling remote code execution.
Unbound 1.26.1, released the same day, fixes the bug, tracked as CVE-2026-81642, along with eight other flaws. One of the eight, CVE-2026-82717, is a heap corruption bug in CNAME synthesis reported by Ben Morris of Anthropic. It could also lead to remote code execution “under certain systems and compilation options,” NLnet Labs said.
NLnet Labs has not reported exploitation of either bug, and CISA’s entry for CVE-2026-81642 marked exploitation as “none” on Wednesday.
NLnet Labs rates the DNSKEY flaw Critical, with a CVSS score of 4.0 (9.1), and its scoring lists a network attack vector requiring no privileges or user interaction. NVD listed the CVE as “Awaiting Analysis” on Wednesday, so the 9.1 is the maintainer’s own score.
The overflow happens while the validator digests a DNSKEY record whose owner name is a compression pointer into the record’s own data. The impact NLnet Labs lists is denial of service, with remote code execution possible “through attacker controlled data.”

Every version up to and including 1.26.0 is affected. That includes 1.25.2, the security release from July, and 1.26.0, released on August 4. The Critical validator bug NLnet Labs fixed in May, CVE-2026-33278, is a different flaw, and the 1.25.1 update that fixed it does not fix this one.
NLnet Labs attaches no configuration condition to that range, and it has not said whether a resolver with DNSSEC validation switched off is reachable.
Upgrade or Patch
Unbound 1.26.1 is available as source, with checksums and a PGP signature, and as Windows installers and binaries. If you cannot upgrade, the advisory gives two ways to patch the source tree:
- Apply the minimal patch or the complete patch for CVE-2026-81642 alone with patch -p1, for example patch -p1 < patch_CVE-2026-81642_with.diff, then run make install.
- Apply the combined patch for all nine fixes instead. A minimal version of it also exists.
NLnet Labs says the standalone patches for CVE-2026-81642 and CVE-2026-82717 have been tested and work on 1.26.0. Its security policy is to patch the latest released version.

Debian’s security tracker listed unbound 1.26.1-1 as fixed in unstable on Thursday, with the bookworm, trixie, and forky branches still listed as vulnerable.
The Nine Fixes
The release notes name nine CVEs. The table gives each one’s affected range and trigger condition in NLnet Labs’ wording.
| CVE | Severity | Affected versions | Needs | Impact |
|---|---|---|---|---|
| CVE-2026-81642 | Critical | Up to and including 1.26.0 | An attacker who controls a malicious zone and queries the resolver | Denial of service, possible remote code execution |
| CVE-2026-82717 | High | Up to and including 1.26.0 | CNAME synthesis during an upstream response. Code execution “under certain systems and compilation options” | Denial of service, possible remote code execution |
| CVE-2026-81634 | High | Up to and including 1.26.0 | A 255-length query name with a large TCP response, from a malicious name server or a tampered response | Denial of service |
| CVE-2026-77955 | Medium | 1.13.2 up to and including 1.26.0 | Zones with zonemd-check: yes located below, but not at, a trust anchor | Denial of service, a window where tampered zone data is served before the ZONEMD check |
| CVE-2026-78227 | Medium | 1.22.0 up to and including 1.26.0 | Built with –with-libngtcp2 and quic-port configured | Denial of service |
| CVE-2026-80225 | Medium | Up to and including 1.26.0 | A sustained stream of distinct uncached names over one TCP or DoT connection | Degradation of service |
| CVE-2026-82720 | Medium | 1.12.0 up to and including 1.26.0 | Built with –with-libnghttp2 and https-port configured. NLnet Labs calls the impact limited | Denial of service |
| CVE-2026-85501 | Medium | Up to and including 1.26.0 | Malicious zones serving the ReTrap algorithmic complexity attacks (TagTrap, DelegationTrap, NsecTrap, AdditionalTrap) | Degradation of service |
| CVE-2026-77860 | Low | 1.20.0 up to and including 1.26.0 |
The serve-expired code path, bypassing a countermeasure added for DNSBomb |
Could take part in a pulsing DoS amplification attack |
The ReTrap fix also changes a default: val-clean-additional is now off, so Unbound no longer validates DNSSEC data in the additional section of a response by default.
The bug was reported to NLnet Labs on August 11 by Yuqi Qiu, who found it with Xiang Li at Nankai University’s AOSP Lab, according to the timeline in the CVE record. NLnet Labs shared a patch the next day and the reporter verified it on August 13. The fix shipped five weeks later in the 1.26.1 batch.
NLnet Labs’ security policy says that for issues not yet public it aims to release fixes “in the order of weeks.”
