

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Who is new Chancellor John Healey? Labour veteran who quit as defence secretary

    October 20, 2026

    Google Open-Sources TorchTPU, a Native PyTorch Backend for Cloud TPUs

    October 20, 2026

    Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution

    October 20, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Who is new Chancellor John Healey? Labour veteran who quit as defence secretary
    • Google Open-Sources TorchTPU, a Native PyTorch Backend for Cloud TPUs
    • Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution
    • NASA Provides Progress Update on Moon Base Rovers
    • Recycled glass offers a potential new tool to restore a vanishing coastline
    • Lindsey Graham, James Clyburn Were Under Scrutiny in FBI Bribery Probe — ProPublica
    • Data Centers Are Key Targets in Today’s Wars
    • Uncovering the facts behind 13 rumors about Trump renaming things
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Tuesday, October 20
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Hackers breached over 270 Zimbra servers in ongoing attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 25, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Threat actors have already compromised over 270 Zimbra instances in remote code execution attacks targeting a high-severity Zimbra Collaboration Suite (ZCS) vulnerability.

    The ZCS email and collaboration suite is used by hundreds of millions of people and organizations, including thousands of businesses and hundreds of government agencies worldwide.

    Synacor patched the security flaw (tracked as CVE-2026-73570), which allows unauthenticated attackers to gain code execution remotely by exploiting a command injection weakness in the SNMP monitoring component when SNMP notifications are enabled, with the release of ZCS version 10.1.20 on July 20.
    image

    CERT Polska, the Polish Computer Emergency Response Team (CERT), first flagged the vulnerability as targeted in the wild last Monday, when it also warned security teams to check their logs for suspicious activity, including the Zimbra service restarting unexpectedly, and for files created in the /opt/zimbra/jetty/webapps/, /opt/zimbra/jetty_base/webapps/, and /tmp/ folders by user zimbra over the last 30 days.

    The Cybersecurity and Infrastructure Security Agency (CISA) also added the flaw to its KEV catalog following CERT Polska’s warning and ordered U.S. Federal Civilian Executive Branch (FCEB) agencies to patch their systems within three days, by August 24.

    On Monday, threat security watchdog Shadowserver reported that it spotted hundreds of Internet-exposed Zimbra instances that have already been breached in attacks exploiting the CVE-2026-73570 flaw.
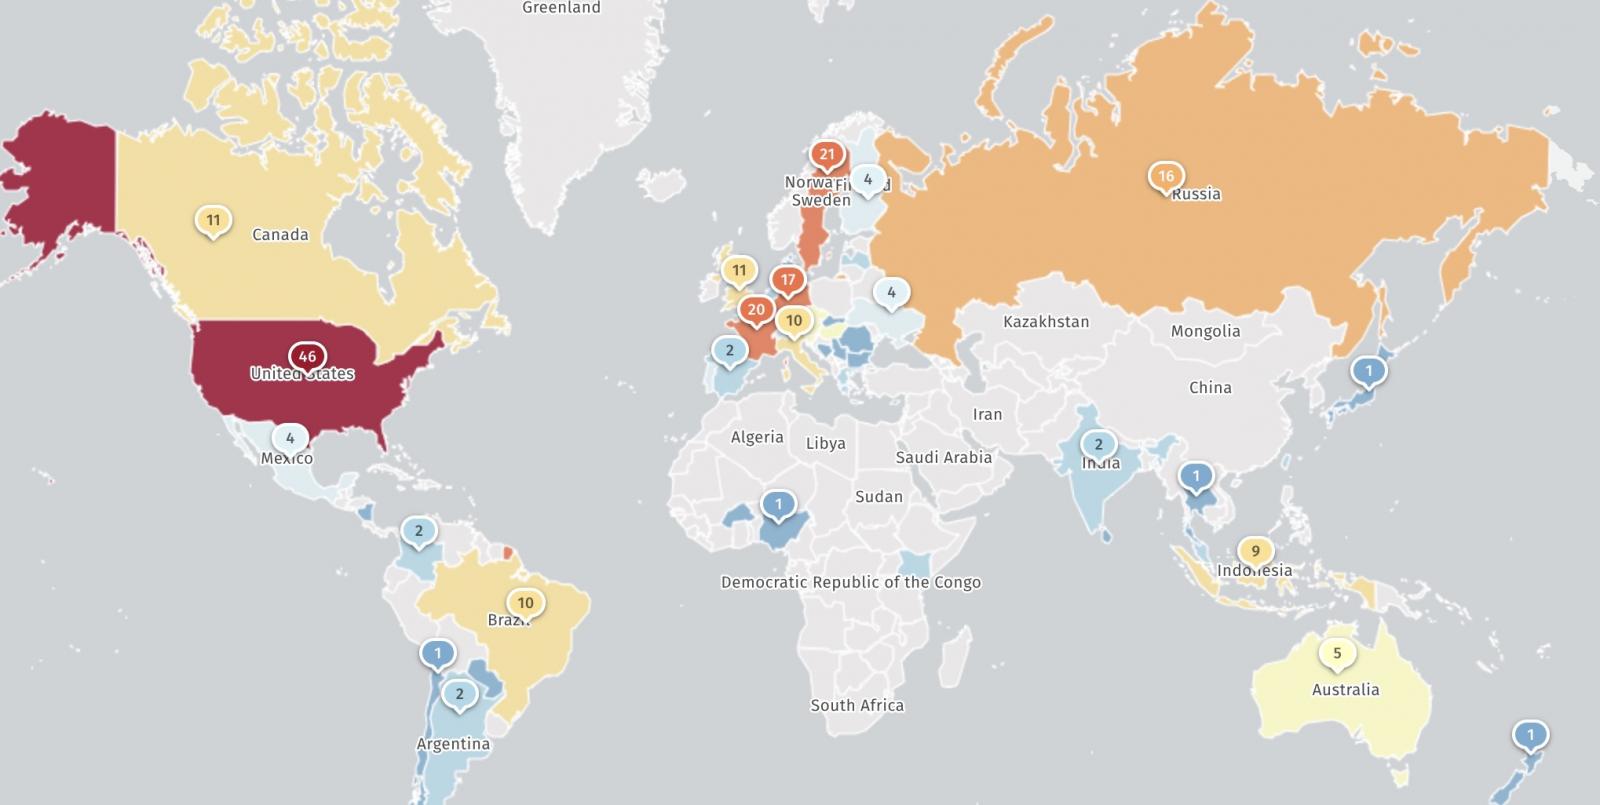
    Map of compromised Zimbra instances
    Map of compromised Zimbra instances (Shadowserver)

    “Zimbra compromises associated with CVE-2026-73570 exploitation are spreading. 274 instances seen compromised in our scans for exploitation artifacts on 2026-08-22,” Shadowserver warned.

    “We also see at least 8200 CVE-2026-73570 unpatched instances (this does not mean exploitable as the vuln is in a non default config).”

    Zimbra vulnerabilities are often targeted by cybercriminals and state-sponsored hacking groups, and have been frequently exploited to steal emails containing sensitive data from vulnerable servers in recent years.

    Most recently, in March, Seqrite Labs researchers spotted APT28 Russian military intelligence hackers abusing a stored cross-site scripting (XSS) Zimbra vulnerability to breach Ukrainian government servers.

    U.S. and UK cyber agencies also warned in October 2024 that Russian Foreign Intelligence Service hackers (tracked as APT29, Midnight Blizzard, and Cozy Bear) compromised Zimbra servers using a ZCS flaw previously exploited to steal email account credentials.

    Russian Winter Vivern cyber spies also exploited a reflected Cross-Site Scripting (XSS) vulnerability to steal emails from NATO-aligned email accounts in attacks targeting Zimbra webmail portals.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    attacks breached hackers ongoing Servers Zimbra
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution

    DHS bans DeepSeek products across US federal civilian agencies

    CJIS v6.1 Compliance: 5 Practical Priorities for Agencies

    Ahold Delhaize Restoring Services Disrupted by Cyberattack

    Six new calves offer hope amid ongoing threats to Cambodia’s Irrawaddy dolphins

    UK to deploy fighter jets to protect Saudi Arabia from Houthi attacks | Defence policy

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Who is new Chancellor John Healey? Labour veteran who quit as defence secretary

    October 20, 2026

    Google Open-Sources TorchTPU, a Native PyTorch Backend for Cloud TPUs

    October 20, 2026

    Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution

    October 20, 2026

    NASA Provides Progress Update on Moon Base Rovers

    October 20, 2026
    Latest Posts

    How AAU Failed to Protect Young Athletes From Sexual Abuse — ProPublica

    August 13, 2026

    So Much Solar: Digging Into the List of Every US Power Plant That Went Online This Year

    August 13, 2026

    Dogs can tell fear from sadness — and scientists saw it in their brains

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Who is new Chancellor John Healey? Labour veteran who quit as defence secretary

    October 20, 2026

    Google Open-Sources TorchTPU, a Native PyTorch Backend for Cloud TPUs

    October 20, 2026

    Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution

    October 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.