

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    This bird flies thousands of miles, but its wings have a catch

    October 17, 2026

    Nigeria drove thousands of gold miners from a national park. But can it keep them out?

    October 17, 2026

    SNP says campaign for next referendum on independence ‘has already begun’ | Scottish National party (SNP)

    October 17, 2026
    Facebook X (Twitter) Instagram
    Trending
    • This bird flies thousands of miles, but its wings have a catch
    • Nigeria drove thousands of gold miners from a national park. But can it keep them out?
    • SNP says campaign for next referendum on independence ‘has already begun’ | Scottish National party (SNP)
    • Plug-in solar is legal in these 10 states now – how it could save you money
    • UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing
    • NASA’s Roman Space Telescope exceeds expectations by nearly 30%
    • Groundwater Cleanup Set to Begin This Fall at North Florida Site, Decades After Superfund Designation
    • These 12 Automatic Cat Feeders Were the Best We Tested in 2026
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 17
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 17, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananOct 16, 2026Phishing / Artificial Intelligence

    Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor authentication (MFA) codes.

    The activity is being tracked by Cisco Talos under the moniker UAT-11985, describing it as likely fueled by artificial intelligence (AI)-assisted content generation so as to quickly craft bespoke lures aimed at different targets within the confines of a common social engineering framework. The campaign was first observed in mid-2026.

    “The operation leveraged legitimate public event themes and impersonated reputable academic and policy institutions to establish credibility,” Talos researcher Joey Chen said in an analysis.

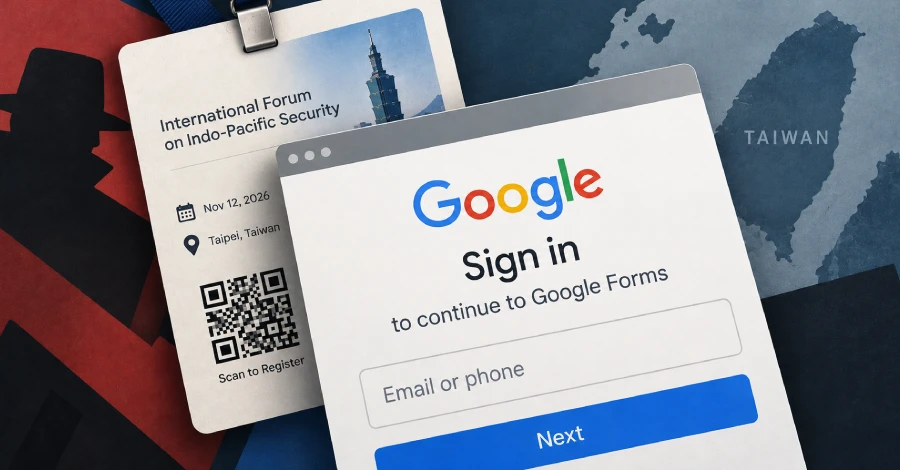
    “Beyond traditional email phishing, the actor incorporated QR code phishing (quishing) techniques by modifying legitimate event posters with malicious QR codes, expanding the attack surface beyond email recipients to secondary victims who may encounter printed materials.”

    Central to the operation is the use of legitimate or plausible public event information in spear-phishing emails and embedding within them a URL that points to attacker-controlled infrastructure, while hovering over the hyperlink displays a legitimate-looking Google Forms URL.

    Cybersecurity

    These invitation emails feature nearly identical syntactic structures despite the breadth of geopolitical topics being discussed, indicating the content was mass-produced from a reusable prompt template rather than painstakingly crafted for each target.

    Specifically, the emails follow a three-part structure –

    • The opening section offers a “polished (but overly elaborate) description” of the geopolitical or policy context.
    • The second section is tailored to the recipient and paints them in a flattering light in an attempt to trigger engagement.
    • The third and final section provides details of event logistics, including the topic, date, venue, and registration instructions.

    The threat actor has been found to impersonate legitimate Taiwan-based institutions like the Taiwan European Union Centre, NCCU Institute of International Relations, and Taiwan Research Institute, fabricating the sender identities to make the messages appear more convincing.

    “Taken together, the reuse of an almost-identical narrative structure, rhetorical style, personalized flattery, institutional impersonation, and deceptive registration mechanism strongly suggests a coordinated and carefully targeted spear-phishing campaign rather than three independent invitations,” Talos said.

    In a subset of cases, the phishing emails incorporate legitimate event posters scraped from legitimate websites, but with the QR codes modified to trick victims into scanning the malicious QR code to “register” for the event.

    The phishing site imitates the look of a legitimate Google Form, but the primary goal of the site is to serve a pop-up that prompts the victim to sign-in with their Google account to complete the form. Doing so takes them to a bogus site featuring a spoofed Google login panel to capture their credentials and authentication challenges.

    The pixel-perfect replica site is an adversary-in-the-middle (AitM) proxy that uses obfuscated JavaScript to gather and exfiltrate the entered information in real-time over a WebSocket connection, while simultaneously forwarding it to legitimate Google authentication servers.

    Cybersecurity

    Prior to establishing the WebSocket connection, the JavaScript payload collects device and browser information, including the locale, user agent, screen dimensions, and mobile-device status, which are then reported to the command-and-control (C2) server via a “google_login_start” request.

    When the victim submits the password, the phishing page transmits the password, along with the account identifier and browser user-agent information, to the actor’s HTTP C2 server through a “google_login_check” request. The threat actor’s server, placed in an AitM position, then forwards the credentials to the actual Google authentication service.

    “The spoofed Google login panels only support Simplified Chinese (zh-CN), Traditional Chinese (zh-TW), and English locales, with region detection based on the victim’s browser ‘navigator.languages,’ strongly suggesting targeting of Chinese-speaking users,” Chen explained.

    “By deliberately splitting one-shot uploads with POST requests from low-latency state updates with WebSocket connection, the threat actor has engineered a seamless credential-harvesting relay. This allows the threat actor to mirror Google’s dynamic authentication state in real time, ultimately achieving full account takeover without raising the victim’s suspicion.”

    Affiliates AitM Event Fake Google invites Phishing research Taiwan Target UAT11985
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    MALFEX npm Package ‘imgdecode’ Hides Shellcode Loader in Windows Native Addon

    Hackers hijack D-Link, Ubiquiti devices to resell your stolen bandwidth

    BAE Systems cyberattack disrupts US federal court operations

    Israeli Ad Firm Doubled as Candiru’s Zero-Click Spyware Delivery Channel

    Microsoft: October Windows update may break Smart App Control

    Hackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 Tenants

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    This bird flies thousands of miles, but its wings have a catch

    October 17, 2026

    Nigeria drove thousands of gold miners from a national park. But can it keep them out?

    October 17, 2026

    SNP says campaign for next referendum on independence ‘has already begun’ | Scottish National party (SNP)

    October 17, 2026

    Plug-in solar is legal in these 10 states now – how it could save you money

    October 17, 2026
    Latest Posts

    The Guardian view on Japan’s yen: Trump wants to keep the easy-money machine running | Editorial

    August 12, 2026

    Minesto reshapes organization to drive commercial expansion of tidal technology

    August 12, 2026

    Corpus Christi Puts Industrial Water Charge on November Ballot

    August 12, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    This bird flies thousands of miles, but its wings have a catch

    October 17, 2026

    Nigeria drove thousands of gold miners from a national park. But can it keep them out?

    October 17, 2026

    SNP says campaign for next referendum on independence ‘has already begun’ | Scottish National party (SNP)

    October 17, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.