

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Your aging brain may be trading memory for something more valuable

    October 21, 2026

    Talarico passes Ossoff as top fundraiser while Democrats dominate latest FEC reports • OpenSecrets

    October 21, 2026

    U.S.-China Competition Can Be Kept in Limits

    October 21, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Your aging brain may be trading memory for something more valuable
    • Talarico passes Ossoff as top fundraiser while Democrats dominate latest FEC reports • OpenSecrets
    • U.S.-China Competition Can Be Kept in Limits
    • Lisbon police arrest 55 housing protesters and clear Rossio tent camp
    • Stolen UpdraftCentral keys used to backdoor WordPress sites
    • Scientists discover a way to kill dangerous gut bacteria without killing the good
    • The Secret Terms of Trump’s Venezuelan Oil Deal — ProPublica
    • Like it or not, we have all benefited from the slave trade | Slavery
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, October 21
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Stolen UpdraftCentral keys used to backdoor WordPress sites

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 21, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A threat actor breached TeamUpdraft’s website, a developer of popular WordPress backup and security plugins, potentially compromising UpdraftCentral connection keys that can send commands to connected websites.

    TeamUpdraft detected unauthorized access to its infrastructure over the weekend and believes that the hacker accessed the customer database.

    The developer offers several WordPress tools for backup, storage, and site management:

    • UpdraftPlus: website backup and restoration plugin with more than 4 million downloads
    • UpdraftCentral: for managing multiple sites remotely
    • UpdraftVault: for cloud backup storage
    • UpdraftClone: for creating staging websites

    “Over the weekend of 17-18 October we identified unauthorised access to the teamupdraft.com website,” TeamUpdraft said in an advisory yesterday.

    “Our team responded straight away and worked through the night to contain it – we closed the access route, signed out every account and replaced the keys and credentials that could have been affected.”

    The vendor says it believes the threat actor accessed its customer database, which included details about the customer and billing, order history, as well as more sensitive information:

    • password hashes
    • two-factor authentication settings
    • connection keys for UpdraftCentral, UpdraftVault, and UpdraftClone services

    The vendor said it did not store any payment details and noted that UpdraftPlus plugin files and downloads remain unaffected. Self-hosted UpdraftCentral instances are not impacted.

    Even if backups in customers’ own remote storage are unaffected, the company recommends that users rotate storage credentials and reauthorize connections if they accessed their site through UpdraftCentral.

    Massive blast radius

    An estimated 10% of sites using UpdraftPlus have an UpdraftCentral or Migrator key, potentially exposing around 400,000 websites to the attack.

    According to Patchstack lead researcher Oliver Sild, attackers have begun using stolen access keys to backdoor sites connected to UpdraftCentral, saying the campaign may be more severe than the “wp2shell” attack.

    The WordPress plugin security company says that the attacks started on October 18 at 15:32 UTC to execute arbitrary code and add accounts with full administrator privileges.

    The researchers logged at least 99 malicious backdoor plugins with distinct names disguised as WordPress maintenance and optimization tools, such as “Site Health Cache.”
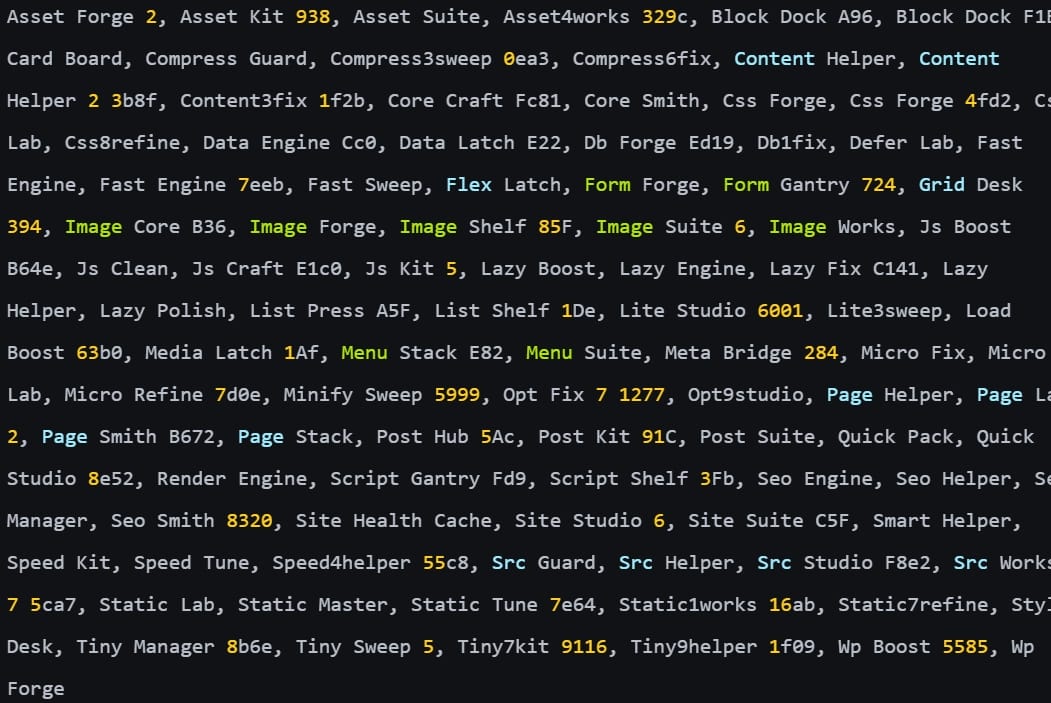
    Backdoor plugin names
    Backdoor plugin names
    Source: Patchstack

    Although Patchstack describes an early variant of the backdoor plugin that is broken due to a coding error, a report from web application security firm Nethemba documents a newer version that lets attackers create privileged accounts or log in as existing administrators.

    Nethemba says three of its own WordPress websites were targeted through UpdraftCentral, with malicious plugins successfully installed on two of them.

    “All three sites ran the current WordPress 7.1.3 and UpdraftPlus 2.26.11, which is patched against the June vulnerability CVE-2026-10795,” Nethemba says.

    “The attacker did not break into our servers and did not exploit any weakness in our configuration. The attacker came in through the UpdraftCentral remote management channel and signed the commands with valid private dashboard keys”

    Nethemba reports that the vendor’s initial 1.26.12/2.26.12 release was meant to remove UpdraftCentral Cloud keys, but a bug prevented it from doing so.

    Users are recommended to update UpdraftPlus to 1.26.13 (free) / 2.26.13 (Premium) or later.

    After updating, it is recommended to log into each WordPress site and delete the UpdraftCentral connection keys from Settings → UpdraftPlus Backups → Advanced Tools → UpdraftCentral → Manage existing keys.

    Administrators should inspect logs and files for indicators of compromise provided by TeamUpdraft, Patchstack, and Nethemba.

    If compromise is confirmed, it is recommended to restore sites from clean backups, change the TeamUpdraft account password, revoke all sessions, and reset the two-factor authentication protection method.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    Backdoor keys sites stolen UpdraftCentral WordPress
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Eight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and Software

    AI Platform Cairn Abused to Hack Over 100 Organizations

    The Key to AI Software Security Isn’t Speed, It’s Maturity

    AOMEI Backupper Compromised in Short-Burst Supply Chain Campaign

    AI Pen-Test Tool Cairn Abused to Automate Massive Attack Spree

    Close Identity Gaps in Software Development Before Unleashing AI

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Your aging brain may be trading memory for something more valuable

    October 21, 2026

    Talarico passes Ossoff as top fundraiser while Democrats dominate latest FEC reports • OpenSecrets

    October 21, 2026

    U.S.-China Competition Can Be Kept in Limits

    October 21, 2026

    Lisbon police arrest 55 housing protesters and clear Rossio tent camp

    October 21, 2026
    Latest Posts

    How AAU Failed to Protect Young Athletes From Sexual Abuse — ProPublica

    August 13, 2026

    So Much Solar: Digging Into the List of Every US Power Plant That Went Online This Year

    August 13, 2026

    Dogs can tell fear from sadness — and scientists saw it in their brains

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Your aging brain may be trading memory for something more valuable

    October 21, 2026

    Talarico passes Ossoff as top fundraiser while Democrats dominate latest FEC reports • OpenSecrets

    October 21, 2026

    U.S.-China Competition Can Be Kept in Limits

    October 21, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.