


The ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 flaw, allowing the threat actors to resume widespread exploitation of a flaw on vulnerable servers.
Google’s Mandiant and Threat Intelligence Group (GTIG) say this new technique has allowed the threat actor to once again target PeopleSoft servers that had not applied security updates and instead blocked access to the vulnerable PSEMHUB endpoint using a WAF.
On June 10, BleepingComputer first reported that the ShinyHunters extortion gang was targeting Oracle PeopleSoft servers using a zero-day vulnerability, allowing them to steal data from 100 organizations.
The next day, Oracle fixed the PeopleSoft zero-day as CVE-2026-35273, stating that it allows unauthenticated remote code execution.
Google also reported that same day that ShinyHunters, whom they track as UNC6240, was exploiting the CVE-2026-35273 flaw in attacks on the education sector, confirming BleepingComputer’s reporting.
At the time, Mandiant advised organizations that could not immediately install the security updates or disable the Environment Management Hub to block external access to the vulnerable `/PSEMHUB/*` endpoint.
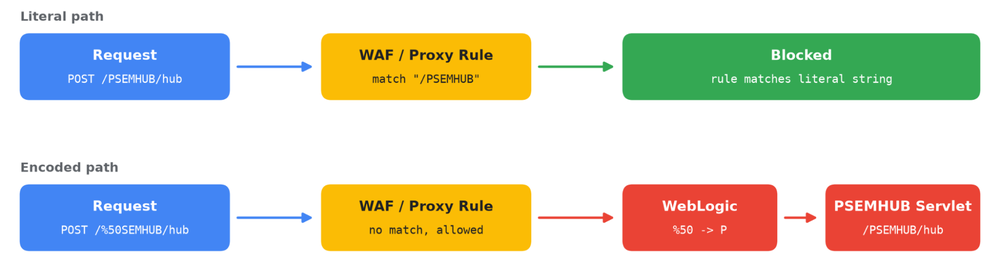
However, in a new report, Google says ShinyHunters has now modified its exploit to bypass WAF rules that look for this literal path, rather than encoded versions of it.
For example, instead of sending requests to:
/PSEMHUB/
the attackers are requesting:
/%50SEMHUB/
The ‘%50’ sequence is the percent-encoded version of the letter ‘P’.
Mandiant says many WAFs and reverse proxies compare the literal request path before decoding it, causing rules designed to block ‘/PSEMHUB/’ to miss the encoded version.
Oracle WebLogic, on the other hand, decodes the encoded ‘P’ and routes the request to the vulnerable endpoint, bypassing the WAF rule.
“This allows the threat actor to reach the endpoint on systems whose operators may have believed their WAF rules had mitigated the exposure,” Mandiant explains.
Source: Mandiant
Google warns ShinyHunters may not always use the ‘%50’ bypass variation, and could switch to other percent-encoded, mixed-case, or other variations of ‘/PSEMHUB/’ to bypass WAFs.
Instead of relying on a web application firewall, Mandiant urges organizations to install the latest security update to protect against CVE-2026-35273.
Organizations are also advised to search WebLogic access logs for requests to ‘/PSEMHUB/’ and encoded variants such as ‘/%50SEMHUB/’ to detect signs of exploitation.
WAF bypass leads to new data-theft attacks
Google says the new wave of attacks has deployed web shells on dozens of systems worldwide within higher education, technology, IT services, healthcare, agriculture, transportation, and government organizations.
“Mandiant recommends that organizations running Oracle PeopleSoft take the following immediate actions. Additional remediation and hardening guidance is included later in this post,” warns Mandiant.
Before attempting exploitation, the attackers typically send between five and 15 POST requests to `/%50SEMHUB/hub` containing serialized Java objects.
On vulnerable systems, these requests return information about the host operating system without writing files or disrupting the service, allowing ShinyHunters to determine whether a server can be exploited quietly.
Once they determine a system is vulnerable, the threat actors exploit the flaw again to execute commands directly in memory or deploy JSP web shells.
Google says the attackers deploy an ‘x.jsp’ web shell for command execution and ‘u.jsp’ and ‘u2.jsp’ shells for uploading larger files.
On compromised Windows servers, ShinyHunters used these shells to deploy an executable named ‘Ple64.exe’, which masquerades as a signed Light Alloy media player installer but installs a backdoor tracked by Google as SIDEEYE.
The SIDEEYE malware is used to steal credentials, for process and file management, to create interactive reverse shells, and for reverse proxy functionality.
The threat actors also deployed the open-source Neo-reGeorg tunneling toolkit via the ‘tunnel.jsp’ and ‘tunnel.jspx’ files.
This toolkit allows SOCKS5 proxy traffic to be tunneled over normal HTTP and HTTPS connections, letting the compromised PeopleSoft server be used to spread laterally into the internal network.
Mandiant also observed ShinyHunters using the legitimate MeshAgent remote management software to maintain access to compromised Linux systems.
ShinyHunters previously claimed a new PeopleSoft zero-day
These new attacks come after ShinyHunters claimed that they breached FBI systems using what they described as a new Oracle PeopleSoft zero-day vulnerability.
ShinyHunters told BleepingComputer on September 22 that the alleged vulnerability allowed remote code execution and was used to access the FBI Jobs platform, then spread laterally into the FBI’s AWS GovCloud infrastructure.
The group claimed it stole between 2TB and 3TB of data related to current and former FBI employees, job applicants, and other internal systems.
At the time, BleepingComputer could not independently verify the alleged zero-day, the claimed lateral movement, or the amount of data reportedly stolen.
The FBI confirmed that it was investigating claims of unauthorized activity affecting FBIjobs.gov but did not confirm that its systems had been breached or that data was stolen.
It is currently unclear whether the vulnerability ShinyHunters described as a new PeopleSoft zero-day was actually CVE-2026-35273 exploited through the newly documented WAF bypass.
However, ShinyHunters told BleepingComputer at the time that they were using this allegedly new zero-day in attacks against other organizations, including Fortune 500 companies.
BleepingComputer has contacted ShinyHunters to confirm whether this bypass is what they previously called a zero-day in the alleged FBI attack.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
