

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    GP appointment time ‘making it harder to do cancer checks’

    October 5, 2026

    Sabine Schoppe who built a refuge for Palawan’s forest turtles has died

    October 5, 2026

    The Guardian view on sexual abuse in schools: teachers cannot deal with this alone | Editorial

    October 5, 2026
    Facebook X (Twitter) Instagram
    Trending
    • GP appointment time ‘making it harder to do cancer checks’
    • Sabine Schoppe who built a refuge for Palawan’s forest turtles has died
    • The Guardian view on sexual abuse in schools: teachers cannot deal with this alone | Editorial
    • Donald Trump says a ‘threat’ led US to move bombers from RAF Fairford
    • Sánchez bets it all on housing ahead of Spain’s snap election – POLITICO
    • Jeffrey Archer: Best-selling author and former politician dies aged 86
    • Jeffrey Archer, former Conservative politician and novelist, dies aged 86 | Jeffrey Archer
    • Astronomers Confirm Discovery of the Youngest Known Exoplanet Ever
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Monday, October 5
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Rejetto HFS servers now actively scanned for critical RCE flaw

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 5, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026-61500, that allows session forgery, account takeover, and remote code execution (RCE).

    VulnCheck VP of Security Research Caitlin Condon posted on LinkedIn over the weekend that the company’s Canary Intelligence honeypots had observed probes targeting CVE-2026-61500.

    Condon said the observed activity appears to be small-scale reconnaissance from a single China Telecom IP address probing deployments in Japan and the United States.

    Rejetto HFS (HTTP File Server) is a free and open-source file-sharing server tool used for self-hosted file sharing on Windows, Linux, and macOS.

    CVE-2026-61500, first published on July 13, 2026, is a session-cookie signing weakness and leakage issue fixed in Rejetto HFS  version 3.2.1.

    “Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs of the same generator to unauthenticated clients during login,” reads the flaw description on the NIST NVD.

    “A remote attacker can collect a small number of login responses, reconstruct the generator’s state, recover the signing key, and forge a valid administrator session cookie, leading to full administrative access and remote code execution via the server_code configuration feature.”

    Horizon3 researchers discovered the flaw using Anthropic’s Mythos model, which identified both the weak signing-key generation and the leak that enabled key recovery.

    Horizon3 published more details about the flaw and a proof-of-concept (PoC) exploit in a write-up on September 30, 2026.

    “Mythos didn’t just flag the insecure PRNG in isolation – it simultaneously identified that the application leaked raw Math.random() outputs through a separate code path, recognized those two facts as a chain, and determined the leak produced exactly the observations needed to make state recovery feasible,” explained Horizon3.
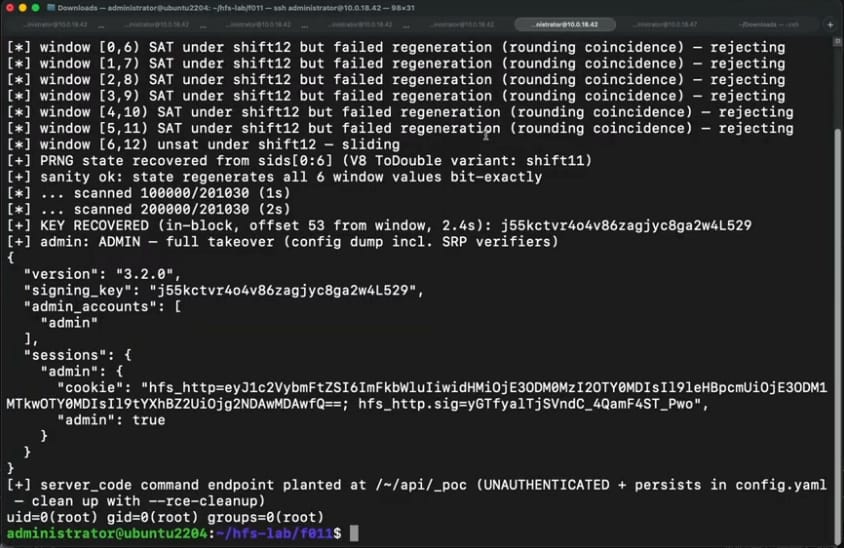
    Recovering the session key
    Recovering the session key
    Source: Horizon3

    The researchers’ exploit demonstrates the chain to abuse HFS’s built-in ability to execute custom server-side JavaScript to achieve remote code execution.

    The release of these technical details may have prompted the probing activity targeting CVE-2026-61500.

    Possible attack scenarios include accessing, stealing, or deleting HFS files, installing malware on the server, or using the compromised host to access internal systems.

    However, VulnCheck has not shared details on successful exploitation or any post-exploitation activity.

    Users of Rejetto HFS are recommended to upgrade to version 3.2.1 or, ideally, the latest stable release, 3.3.4, as soon as possible.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    actively critical Flaw HFS RCE Rejetto scanned Servers
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    ⚡ Weekly Recap: NetScaler and FortiMail 0-Days, AI Coding Leaks, Spectre v2 and Ransomware Arrests

    Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users’ Mailboxes

    IQVIA fined $7.8 million for failing to properly anonymize health data

    Need for Speed: AI-Driven Attacks Change Security Strategies

    Senate Passes Bipartisan Bill to Strengthen Healthcare Cybersecurity

    Google Narrows Open Source Bug Bounty Amid Wave of Invalid Automated Reports

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    GP appointment time ‘making it harder to do cancer checks’

    October 5, 2026

    Sabine Schoppe who built a refuge for Palawan’s forest turtles has died

    October 5, 2026

    The Guardian view on sexual abuse in schools: teachers cannot deal with this alone | Editorial

    October 5, 2026

    Donald Trump says a ‘threat’ led US to move bombers from RAF Fairford

    October 5, 2026
    Latest Posts

    What do cybersecurity leaders want in staff? These 3 skills beat certifications and experience

    August 9, 2026

    Britain is paying the price for failing to invest in its young people | Richard Partington

    August 9, 2026

    A Democratic Socialist Spreads the Word, Even in Hostile Territory

    August 9, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    GP appointment time ‘making it harder to do cancer checks’

    October 5, 2026

    Sabine Schoppe who built a refuge for Palawan’s forest turtles has died

    October 5, 2026

    The Guardian view on sexual abuse in schools: teachers cannot deal with this alone | Editorial

    October 5, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.