

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Googly-eyed buoys and kites help keep seabirds out of fishing nets, study finds

    October 24, 2026

    Obama Returns to the Trail, Setting Up Dueling Midterm Appearances With Trump

    October 24, 2026

    PHP shares mitigation for new RCE vulnerability with no patch

    October 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Googly-eyed buoys and kites help keep seabirds out of fishing nets, study finds
    • Obama Returns to the Trail, Setting Up Dueling Midterm Appearances With Trump
    • PHP shares mitigation for new RCE vulnerability with no patch
    • Yes, There Is Some Global Action on Phasing Out Fossil Fuels
    • 70,000 police forces deployed in France for tense day of protests – POLITICO
    • Between quick wins and big dreams lies Burnham’s biggest test, starting with the Budget
    • No unions, low taxes: why some of Britain’s top chefs are opening outposts in Gulf states | Restaurants
    • Stateful Agentic Engineering Copilots with Letta: Core Memory, Shared State, Semantic Retrieval, Custom Tools, Streaming, and Portable Agent Workflows
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    PHP shares mitigation for new RCE vulnerability with no patch

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 24, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    The PHP security team has shared mitigation measures for a new remote code execution vulnerability that affects systems with non-default configurations and has no patch.

    PHP is an open-source web development language used by nearly 70% of all websites on the Internet. According to VirusTotal estimates, more than 5.1 million PHP hosts are exposed online, and roughly 3.8 million have at least one port open to attacks.

    According to a Friday advisory, this security flaw (tracked as CVE-2026-115560) can only be exploited when targeting systems “with an unusual combination of configuration and application code.”

    “An application must set session.serialize_handler to php_binary or php_serialize in its configuration and then switch it to php at runtime with ini_set() before calling session_start(). Session upload progress must also still be enabled,” the PHP team explained.

    “Applications that never change the serialize handler at runtime can keep the feature enabled. Since this setup is unlikely in practice, we are handling it in the regular release cycle and will publish a full advisory for CVE-2026-115560 with the next release.”

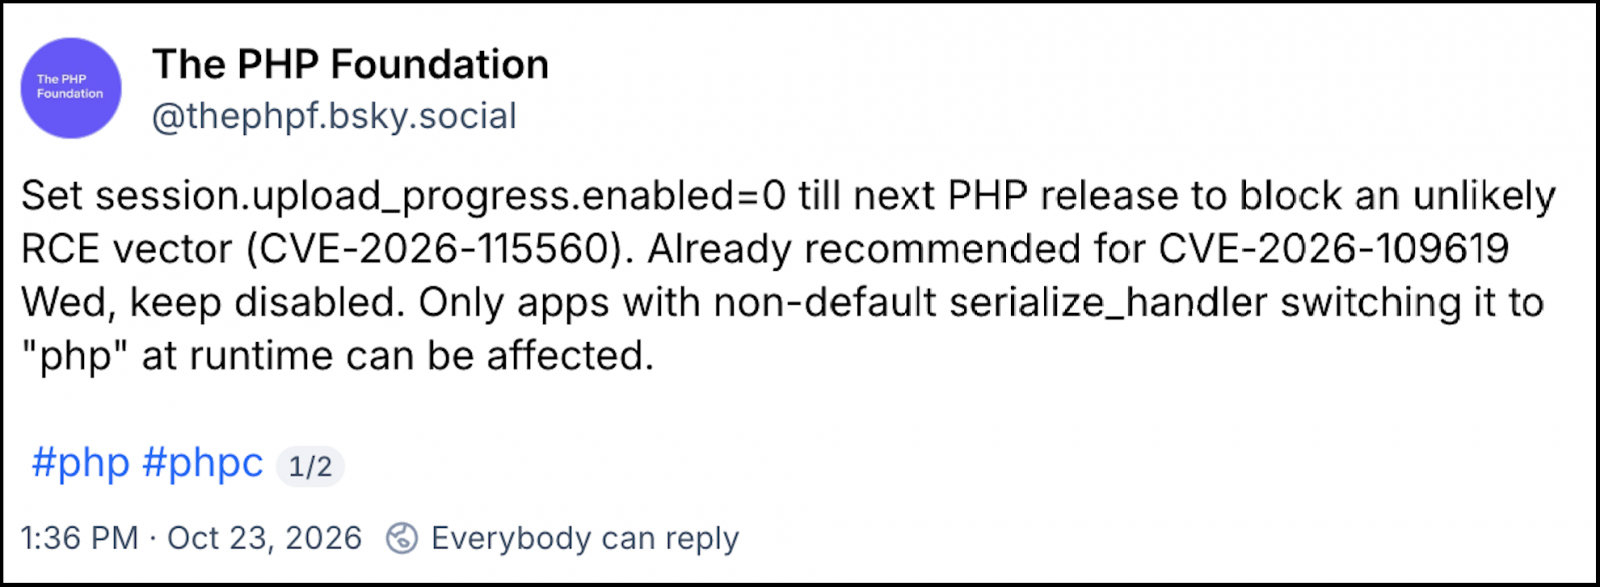
    Until a security patch is available, the PHP devs suggested setting session.upload_progress.enabled=0, adding that “If you applied it then, keep it in place and no further action is needed.”

    This mitigation should have already been applied on Wednesday, before patching two other critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell.
    CVE-2026-115560 PHP post

    PHP2Shell flaws now targeted in attacks

    The PHP security team patched the PHP2Shell vulnerabilities one day after urging admins to prepare to install the updates as soon as they became available.

    While some proof-of-concept (PoC) code was published before the patches went live, the PHP security team said none were functional.

    However, multiple cybersecurity companies (including Cloudflare, watchTowr, Previdian, Hadrian, and Patchstack) detected unsuccessful exploitation attempts before public disclosure, after some details on the PHP2Shell security flaws (including the CVE IDs and mitigation advice provided to some critical infrastructure providers) leaked online.

    Security researchers at Amazon Threat Intelligence also said that attackers began targeting the PHP2Shell vulnerabilities four days before security patches were released on Wednesday.

    “The actual payloads and choices in anonymization infrastructure varied, suggesting these were multiple actors. Technical analysis is ongoing, and it’s unclear if any of these attempts would have succeeded in real-world systems,” said AWS chief information security officer CJ Moses.

    “PHP2Shell is now seeing broad exploitation attempts in the wild,” he added, though it’s unclear how many attacks (if any) have succeeded.

    Dataminr’s Threat Research and Cyber Engineering (TRACE) team also said in a Thursday report that “observed activity since vulnerability disclosure remains limited to scanning, fingerprinting, and use of non-working exploits, with no known compromises,” but noted that “it remains only a matter of time for working POCs or successful exploitation activity to emerge.”


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    Mitigation patch PHP RCE shares Vulnerability
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Quest Diagnostics confirms data breach exposed patient records

    Researchers Push Over 2 Million Updates to Remotely Disable Popcorn Time Updater That Could Fuel a Botnet

    Atlassian Patches 75 Flaws in Data Center and Server Products

    Microsoft Teams to get AI-powered, context-aware phishing detection

    CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloud

    Quest Diagnostics Data Breach Exposed ‘Certain Patient Records’

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Googly-eyed buoys and kites help keep seabirds out of fishing nets, study finds

    October 24, 2026

    Obama Returns to the Trail, Setting Up Dueling Midterm Appearances With Trump

    October 24, 2026

    PHP shares mitigation for new RCE vulnerability with no patch

    October 24, 2026

    Yes, There Is Some Global Action on Phasing Out Fossil Fuels

    October 24, 2026
    Latest Posts

    Google AI health coach to use Abbott glucose data

    August 14, 2026

    CMF hit the balance between cheap and good clip earbuds

    August 14, 2026

    David Hearn’s Lawyers Ask Court to Bar Future Reflecting Pool Charges

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Googly-eyed buoys and kites help keep seabirds out of fishing nets, study finds

    October 24, 2026

    Obama Returns to the Trail, Setting Up Dueling Midterm Appearances With Trump

    October 24, 2026

    PHP shares mitigation for new RCE vulnerability with no patch

    October 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.