

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Valaris rigs find more work in North Sea, Australia, and Suriname

    October 7, 2026

    Halloween is looming – this year, I’m ditching my cynicism and getting busy with the pumpkins | Iman Amrani

    October 7, 2026

    Images allegedly show ancient Egyptian sculptures with cats ignoring personal space. Are they real?

    October 7, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Valaris rigs find more work in North Sea, Australia, and Suriname
    • Halloween is looming – this year, I’m ditching my cynicism and getting busy with the pumpkins | Iman Amrani
    • Images allegedly show ancient Egyptian sculptures with cats ignoring personal space. Are they real?
    • ‘Another coup d’état’: fears grow as Flávio Bolsonaro vows to ‘re-democratise’ Brazil | Brazil
    • ‘Palestinians will bear the cost’: UK consulate in East Jerusalem prepares to shut its doors | Israel
    • Joshua Kerry accused of trying to break into Nigel Farage’s home
    • ‘The Social Reckoning’ Already Feels Irrelevant
    • Hackers exploit critical Atlassian flaw after public PoC release
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, October 7
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Hackers exploit critical Atlassian flaw after public PoC release

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 7, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A critical vulnerability (CVE-2026-21589) affecting multiple Atlassian product families, including Jira, Confluence, and Bitbucket, is being exploited in attacks that do not require authentication.

    Earlier today, security company Previdian detected the activity on its honeypot network, just hours after a detailed technical report was published.

    An unauthenticated attacker can exploit CVE-2026-21589 to access specific files in the application’s web root directory if they know the file’s exact name and path.

    The issue is an arbitrary file-access flaw disclosed on Monday, and it affects self-hosted instances of eight Atlassian products:

    • Bitbucket Data Center
    • Confluence Data Center
    • Jira Service Management Data Center
    • Jira Software Data Center
    • Bamboo Data Center
    • Crowd Data Center
    • Crucible
    • Fisheye

    In a security advisory on Monday, Atlassian warned system administrators managing self-hosted instances to apply the security updates as soon as possible, noting it cannot determine whether individual customer instances have been compromised.

    Following Atlassian’s advisory, offensive security company watchTowr published a technical report showing how CVE-2026-21589 could be exploited to gain administrator-level access to Jira, Confluence, and Bitbucket in certain Crowd-integrated deployments.

    Atlassian Crowd provides centralized identity management, single sign-on (SSO), authentication, authorization, and access management for connected Data Center apps.

    The researchers exploited the root cause of the flaw, which is a shared web-resource library that converts double colons “::” into forward slashes “/”, to construct directory-traversal requests through plugin resource endpoints and retrieve protected application files without authentication.

    watchTowr researchers confirmed file reads in Jira, Confluence, and Bitbucket, but their technique could not traverse outside the Tomcat application context.

    In Crowd-integrated Jira deployments, attackers could read plaintext application credentials from WEB-INF/classes/crowd.properties and use them to create a Jira administrator account through Crowd’s API.

    This applies if Crowd is reachable and the application has sufficient permissions. However, the researchers note that specifying a list of allowed IP addresses would make exploitation significantly more difficult.

    “[An attacker] would need to pivot through arbitrary machines or use SSRF-like capabilities of Jira, Confluence, or Bitbucket to reach Crowd directly,” the researchers say.

    The leaked credentials in crowd.properties provide administrator access to the Crowd identity management system, allowing attackers to create new users and modify permissions.
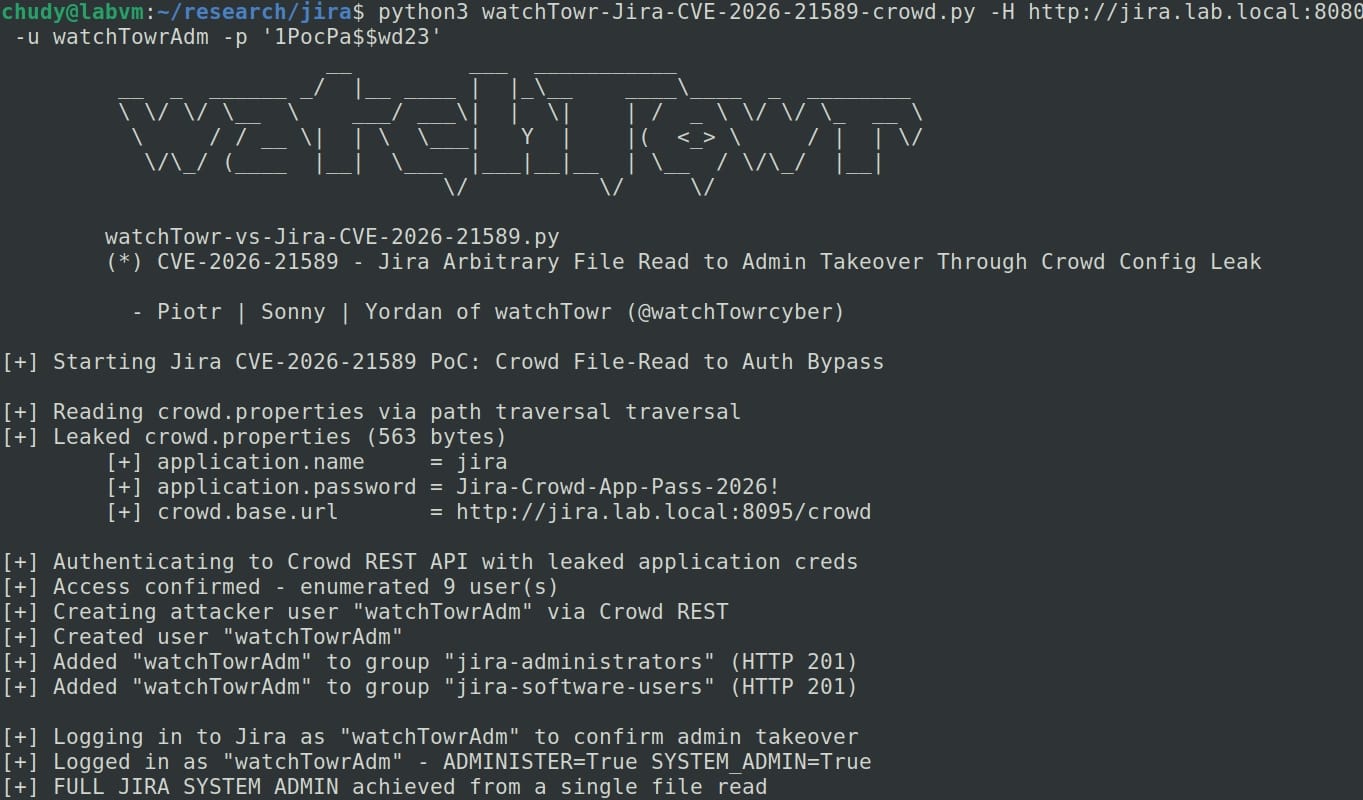
    PoC showing escalation to admin on Jira
    PoC showing escalation to admin on Jira
    Source: watchTowr

    According to Previdian, the technical details were sufficient to help threat actors scan for exposed vulnerable instances and probe them.

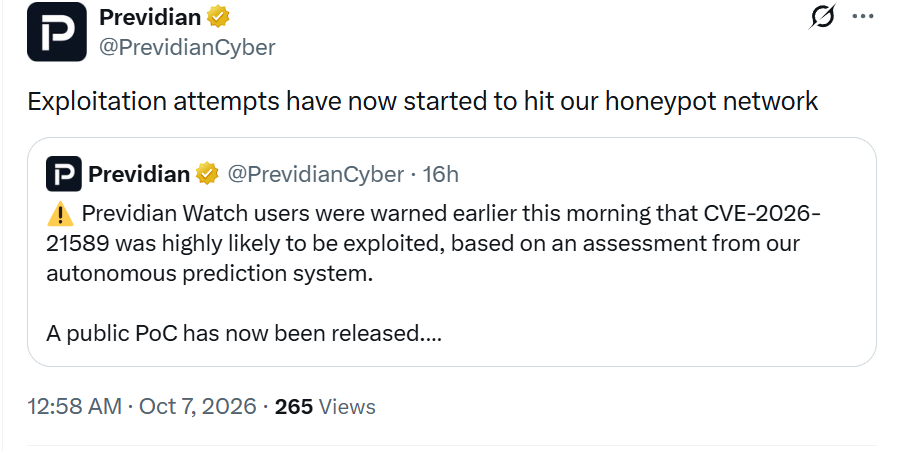
    “Within two hours of watchTowr publishing its technical research and public PoC for CVE-2026-21589, Previdian’s honeypot network began observing exploitation attempts targeting the vulnerability,” Previdian’s Ryan Dewhurst told BleepingComputer.

    “A Nuclei template has also now been released, making it significantly easier to automate scanning for vulnerable systems.”

    The company has so far observed attempts from these three IP addresses: 38.60.157[.]86, 146.70.187[.]234, and 159.26.119[.]225, and recommends blocking them.
    Tweet

    Dewhurst expects exploitation activity to increase significantly over the coming days and weeks, driven by the rapid emergence of exploitation attempts following the public PoC, the availability of automated scanning templates, and the broad range of affected Atlassian products.

    System administrators should apply available security updates as soon as possible, or apply the recommended mitigations.

    This includes restricting external network access, adding a web application firewall (WAF) or proxy rule blocking specified traversal patterns across all affected products, Tomcat RewriteValve rules for Confluence, JSM, Jira, Bamboo, and Crowd, or a URL rewrite rule for Bitbucket.

    For more details about the fixed versions and mitigation steps, check out Atlassian’s bulletin.

    watchTowr has also released a free scanner tool to help administrators determine if their instances are vulnerable to CVE-2026-21589.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    Atlassian critical exploit Flaw hackers PoC public release
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    SonicWall warns of max severity SSRF flaw in SMA1000 gateways

    New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline

    Apple Plans Tighter macOS Full Disk Access Controls Over AI Agent Data Access

    Anthropic Expands Claude Access for Vetted Cyber Teams as Glasswing Finds 129,000 Flaws

    100+ Compromised Websites Use Fake Cloudflare Checks to Deliver LunexStealer

    Hackers exploit 32 zero-days on first day of Pwn2Own Ireland

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Valaris rigs find more work in North Sea, Australia, and Suriname

    October 7, 2026

    Halloween is looming – this year, I’m ditching my cynicism and getting busy with the pumpkins | Iman Amrani

    October 7, 2026

    Images allegedly show ancient Egyptian sculptures with cats ignoring personal space. Are they real?

    October 7, 2026

    ‘Another coup d’état’: fears grow as Flávio Bolsonaro vows to ‘re-democratise’ Brazil | Brazil

    October 7, 2026
    Latest Posts

    British national shot dead in Kashmir by Pakistani security forces | Kashmir

    August 10, 2026

    Climate change doubled likelihood of Canada’s extreme fire weather, study finds

    August 10, 2026

    Scientists say just 7 days of meditation can rewire your brain

    August 10, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Valaris rigs find more work in North Sea, Australia, and Suriname

    October 7, 2026

    Halloween is looming – this year, I’m ditching my cynicism and getting busy with the pumpkins | Iman Amrani

    October 7, 2026

    Images allegedly show ancient Egyptian sculptures with cats ignoring personal space. Are they real?

    October 7, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.