

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    The DOE Keeps Appealing Claims by Sick Hanford Nuclear Site Workers — ProPublica

    October 22, 2026

    Bolsonaro Win Could Bring U.S. Military to Brazil

    October 22, 2026

    Why do we carve pumpkins for Halloween? Tracing the history

    October 22, 2026
    Facebook X (Twitter) Instagram
    Trending
    • The DOE Keeps Appealing Claims by Sick Hanford Nuclear Site Workers — ProPublica
    • Bolsonaro Win Could Bring U.S. Military to Brazil
    • Why do we carve pumpkins for Halloween? Tracing the history
    • French weekend protests to be limited to union demos only, says Macron
    • Ten Ashfield Independent councillors quit after leader’s fraud conviction
    • Tax online sales more heavily to save high streets, Burnham urged | Budget 2026
    • GitLab warns of new max severity code execution vulnerability
    • Birds are more afraid of women than men. Scientists have no idea why
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 22
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 28, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Swati KhandelwalAug 27, 2026Malware / Phishing

    Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at an unnamed communications organization in Venezuela.

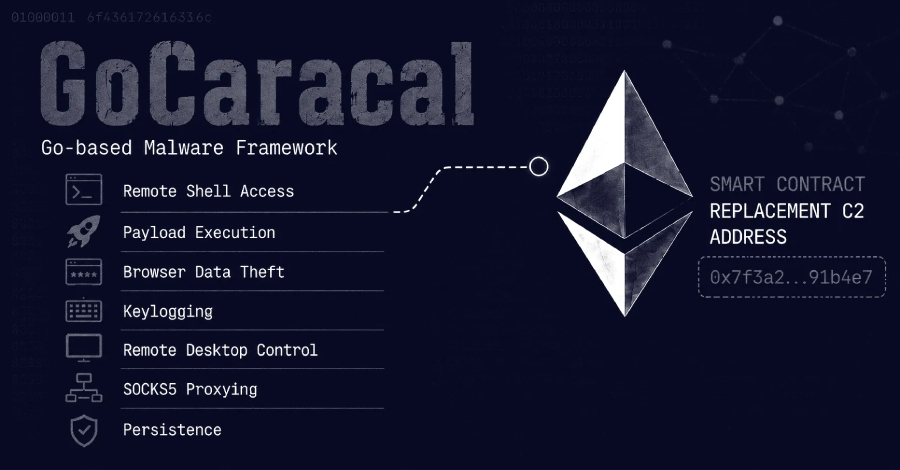
    GoCaracal provides operators with remote shell access and payload execution, while the extended profile adds browser data theft, keylogging, remote desktop control, and SOCKS5 proxying.

    Arctic Wolf also published a YARA rule and representative indicators of compromise (IoCs) that defenders can use to hunt for the malware.

    “We assess with medium confidence that this activity is linked to Dark Caracal,” Arctic Wolf said.

    Arctic Wolf based the assessment on Bandook use, recurring Delphi-loader characteristics, Spanish-language financial lures, malicious SVGs, URL shorteners, document-themed infrastructure, hosting-provider preferences, and Latin American targeting.

    Cybersecurity

    In its technical analysis of GoCaracal, Arctic Wolf said the malware appeared in lightweight and extended profiles during the investigated intrusion.

    Bandook was subsequently deployed alongside the lightweight profile. It was used in parallel with GoCaracal, and Arctic Wolf said current evidence does not establish GoCaracal as a replacement for Bandook.

    The lightweight profile supports host profiling, an encrypted command-and-control (C2) channel, interactive shell access, payload retrieval and execution, and shellcode loading and injection.

    The extended profile adds system and file discovery, command execution, browser cookie and login-database collection, keylogging, targeted file search, Web Real-Time Communication (WebRTC) remote desktop, hidden browser interaction, SOCKS5 proxying, and persistence-related functionality.

    Arctic Wolf assesses phishing as the delivery mechanism, although it did not recover the original phishing email or Scalable Vector Graphics (SVG) attachment from the victim. The firm based that assessment on financial and tax-themed artifact naming, the established campaign pattern, and more than 100 related SVG files that communicated with the same malicious hosting site.

    The extended GoCaracal profile first attempts to communicate with its configured primary C2 server. After repeated failures, it sends an eth_getStorageAt request to a public Ethereum JSON-RPC endpoint.

    The response provides a replacement address stored in the configured smart contract. GoCaracal writes that address to its in-memory configuration. It then retries conventional off-chain C2 communication using the replacement address.

    Multiple public RPC endpoints can be used to read the same contract state, reducing dependence on a single fallback access point. “This mechanism does not place the malware’s full command-and-control channel on Ethereum,” Arctic Wolf said.

    The smart-contract mechanism lets the operator change the replacement C2 address without shipping a new GoCaracal binary.

    Arctic Wolf’s public report does not show a host in the June intrusion that invoked the fallback and successfully reconnected through the replacement address.

    Dark Caracal has a documented history of operating in Latin America. The Hacker News covered the original Dark Caracal disclosure in 2018, followed by retooled Bandook malware in 2020 and Bandook attacks in Venezuela in 2021.

    Arctic Wolf said related artifacts and infrastructure were associated with Brazil, Ecuador, Chile, Colombia, El Salvador, and Uruguay, assessing that broader regional activity with moderate confidence. Arctic Wolf does not identify those locations as confirmed victim countries.

    The public report provides no broader confirmed count of organizations compromised with GoCaracal.

    Cybersecurity

    The Hacker News contacted Arctic Wolf for clarification on whether the Ethereum fallback was observed executing on an infected host and on the confirmed scope of the campaign; Arctic Wolf had not responded at the time of publication.

    Arctic Wolf shared the following indicators of compromise (IoCs) –

    • A YARA rule for the lightweight GoCaracal profile.
    • Representative SHA-256 hashes and related domains and IP addresses.
    • Ethereum contract and wallet indicators.
    • Host paths associated with the malware.

    The company said the public indicators are referential and that the full set is available to Arctic Wolf customers.

    address contract Ethereum Fetch GoCaracal Malware Replacement Smart
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    GitLab warns of new max severity code execution vulnerability

    Splunk, SolarWinds Release Fresh Security Updates

    Japan’s Onamae Desktop Cloud hacked, up to 27,000 servers affected

    LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release

    Authorities disrupt nearly 11,000 cybercrime networks in Africa

    Google Chrome Adds ClickFix Warnings to Stop Users From Running Malicious Commands

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    The DOE Keeps Appealing Claims by Sick Hanford Nuclear Site Workers — ProPublica

    October 22, 2026

    Bolsonaro Win Could Bring U.S. Military to Brazil

    October 22, 2026

    Why do we carve pumpkins for Halloween? Tracing the history

    October 22, 2026

    French weekend protests to be limited to union demos only, says Macron

    October 22, 2026
    Latest Posts

    Big Bear Valley’s beloved bald eagle Jackie is dead

    August 14, 2026

    Cascade Volcanoes Shrouded in Smoke

    August 14, 2026

    Bit Digital pledged 74% of its staked Ethereum position to a loan that can trigger a 24-hour collateral call

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    The DOE Keeps Appealing Claims by Sick Hanford Nuclear Site Workers — ProPublica

    October 22, 2026

    Bolsonaro Win Could Bring U.S. Military to Brazil

    October 22, 2026

    Why do we carve pumpkins for Halloween? Tracing the history

    October 22, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.