

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    TB 26-08 Complex Modes in Lightly Damped Structural Systems: A Two-Mode Interaction Perspective

    October 14, 2026

    Winning entries for Wildlife Photographer of the Year 2026

    October 14, 2026

    Talarico’s Campaign-Trail Absence Sparks False Rumor

    October 14, 2026
    Facebook X (Twitter) Instagram
    Trending
    • TB 26-08 Complex Modes in Lightly Damped Structural Systems: A Two-Mode Interaction Perspective
    • Winning entries for Wildlife Photographer of the Year 2026
    • Talarico’s Campaign-Trail Absence Sparks False Rumor
    • Arsenal thrash Lille as Atletico Madrid beat Manchester United
    • Man rescued after being trapped in Sardinian cave for 26 hours
    • Apple’s HomeView ad is confusing to everyone except parents
    • Ghostscript flaw lets hackers hijack servers via PDF uploads
    • Tokenized Stocks Hit $3.3B as After-Hours Trading Grows
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, October 14
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Ghostscript flaw lets hackers hijack servers via PDF uploads

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKOctober 13, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files.

    The flaw was discovered on August 23 by researchers at Defiant’s platform Wordfence using their Argus AI-powered system.

    Ghostscript is a PostScript and PDF interpreter that can render PDFs as images, generate thumbnails for previews, and optimize PDF files by compressing embedded images and removing unnecessary font data.

    When generating a PDF thumbnail, WordPress can use the PHP Imagick extension to call ImageMagick, which launches Ghostscript.

    A specially crafted PDF file containing a JPEG 2000 image can trigger incorrect handling of low-bit-depth samples and mismatched component resolutions.

    Using Argus, the researchers developed two exploits for CVE-2026-39919 that force Ghostscript to write 1,024 bytes into a 256-byte buffer, corrupting nearby memory and leading to unauthenticated remote code execution in a WordPress deployment.

    Wordfence focused on WordPress systems, but notes that the flaw affects any online system running Ghostscript 9.21 through 10.07.1 and is exploitable if the payload is adjusted to the environment.

    The researchers tested ten Linux environments, including Debian, Ubuntu, Fedora, Alpine, and AlmaLinux, as well as an official WordPress Docker image snapshot, and found that all contained the vulnerable code.
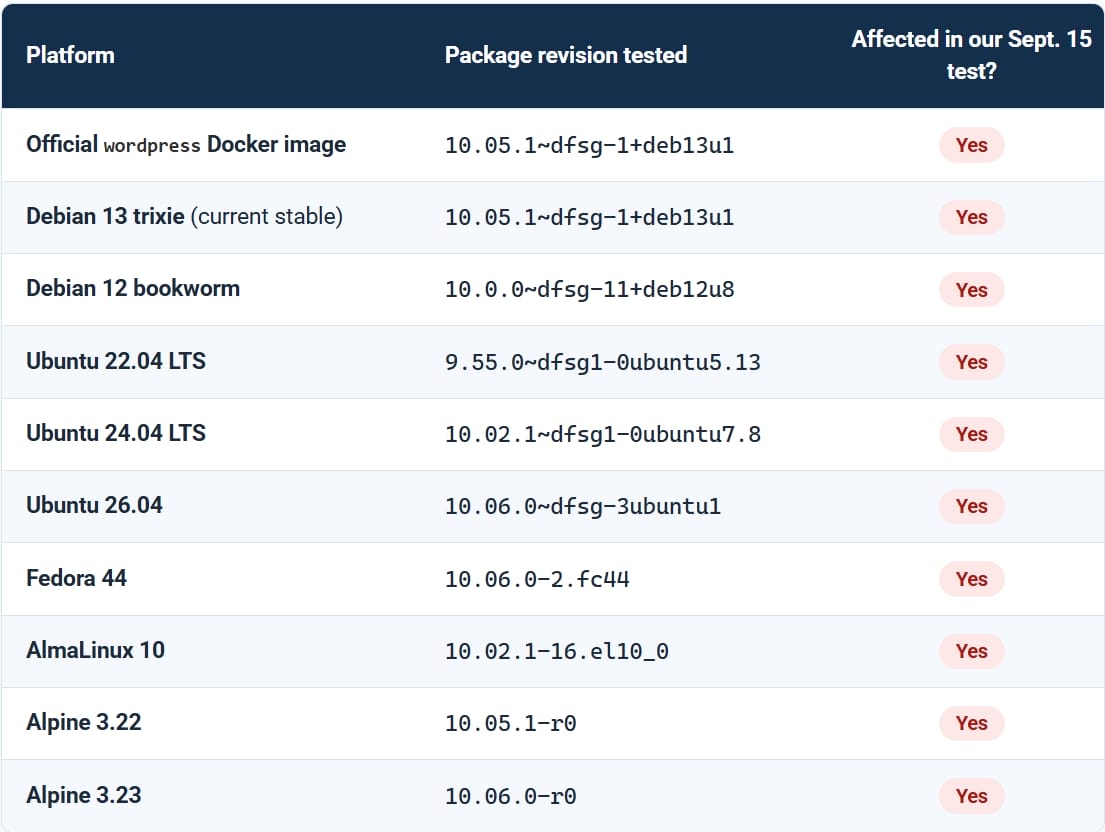
    Tested environments
    Tested environments
    Source: Wordfence

    The researchers tested two proof-of-concept (PoC) exploits and found that their ability to trigger the vulnerability depended on the target environment.

    In a lab testbed, they executed the exploits 10,240 times against Linux packages but failed to achieve remote code execution. However, they successfully executed code remotely on a purpose-built test server.

    The researchers found that modifying the PDF’s fonts, language settings, font configuration, and one core system library enabled the exploit to succeed, although not reliably.

    In WordPress environments specifically, successful exploitation has four prerequisites:

    1. An attacker can upload a PDF, anonymously or through a low-privileged account.
    2. The site processes that PDF to generate a preview or thumbnail.
    3. The processing chain reaches Ghostscript, with the necessary software and policy settings permitting PDF rendering.
    4. Ghostscript contains the unpatched vulnerable decoding code.

    Wordfence noted that stock WordPress does not permit anonymous Media Library uploads.

    More generally, any application that renders attacker-supplied PDFs through affected Ghostscript code may expose the flaw, and authentication requirements for exploitation depend on the application.

    Artifex, the maintainer of Ghostscript, rolled out a fix on September 8, in version 10.08.0 of the interpreter.

    Fixes were also backported to older versions, so users should check the revision details for patch status.

    WordPress administrators need to ensure, through their hosting provider, that Ghostscript has been upgraded to version 10.08.0 or later.

    If using Docker, it is recommended to rebuild and redeploy with an updated, patched base image.

    If unable to upgrade to a fixed Ghostscript release, it is recommended to block PDF uploads to the server or disable PDF rendering in ImageMagick.

    Wordfence said it has not seen any in-the-wild exploitation of CVE-2026-39919 yet.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    Flaw Ghostscript hackers hijack lets PDF Servers Uploads
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    OpenAI engineer arrested for allegedly planting spy device in office

    Anthropic Warns Small AI Models Could Soon Form Self-Propagating IoT Botnets

    Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days

    Microsoft: Windows 11 24H2 Home and Pro reached end of support

    Xandr Fined a Record €8.6 Million for Relaying Grindr Data Revealing Sexual Orientation

    GitHub Tightens npm Publishing After Flaw Left 1,500+ Packages Vulnerable to Hijacking

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    TB 26-08 Complex Modes in Lightly Damped Structural Systems: A Two-Mode Interaction Perspective

    October 14, 2026

    Winning entries for Wildlife Photographer of the Year 2026

    October 14, 2026

    Talarico’s Campaign-Trail Absence Sparks False Rumor

    October 14, 2026

    Arsenal thrash Lille as Atletico Madrid beat Manchester United

    October 14, 2026
    Latest Posts

    How viable are plans to free up prison space in England and Wales? | Prisons and probation

    August 11, 2026

    Ex-Marine Robert Gilman Is Freed by Russia After 4 Years in Prison

    August 11, 2026

    An Electric Motorcycle Revolution – The New York Times

    August 11, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    TB 26-08 Complex Modes in Lightly Damped Structural Systems: A Two-Mode Interaction Perspective

    October 14, 2026

    Winning entries for Wildlife Photographer of the Year 2026

    October 14, 2026

    Talarico’s Campaign-Trail Absence Sparks False Rumor

    October 14, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.