

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Abercynon woman, 93, waits 10 hours on floor for an ambulance

    October 24, 2026

    Almost 1,000 arrested as clashes follow another day of mass protests across France

    October 24, 2026

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    October 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Abercynon woman, 93, waits 10 hours on floor for an ambulance
    • Almost 1,000 arrested as clashes follow another day of mass protests across France
    • Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads
    • Scientists discover a hidden switch that burns fat and blocks new fat cells
    • Mass sloth deaths prompt US bill calling for import ban
    • Brussels shops boarded up amid fears of repeat of last week’s looting
    • Your blood could reveal inflammatory bowel disease 10 years before diagnosis
    • Sri Lanka mourns iconic tusker amid renewed calls to address human-elephant conflict
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 2, 2026 Cybersecurity No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Swati KhandelwalSep 02, 2026Vulnerability / Web Security

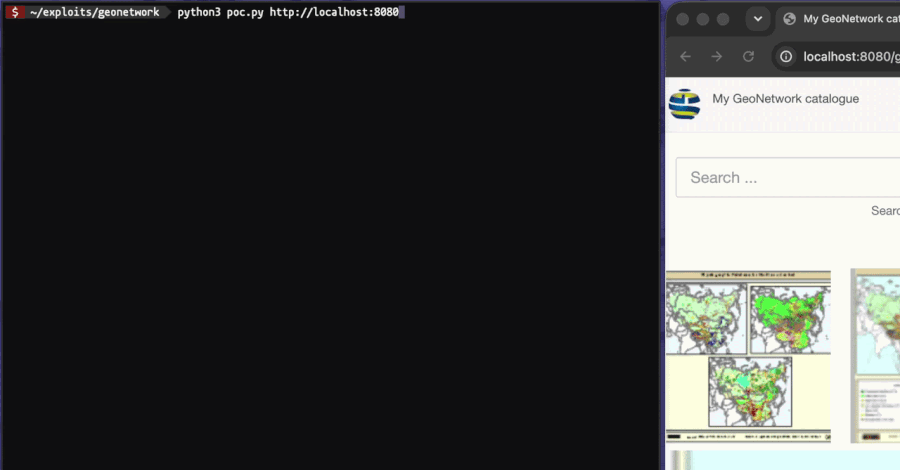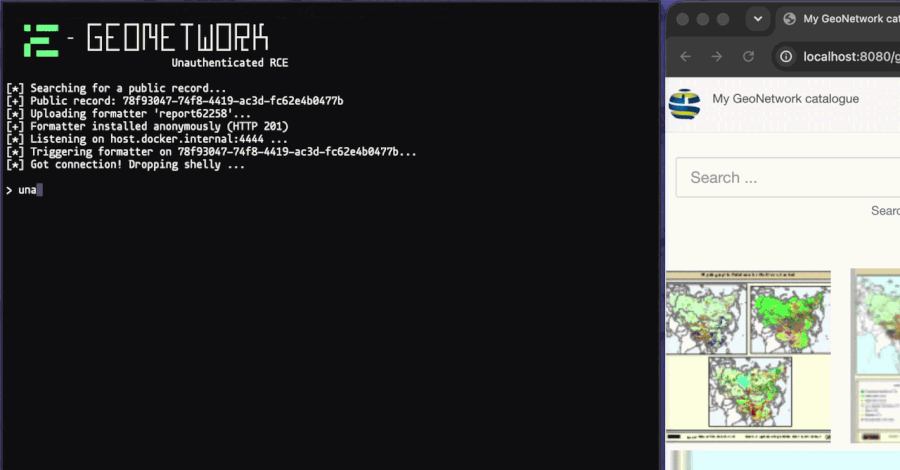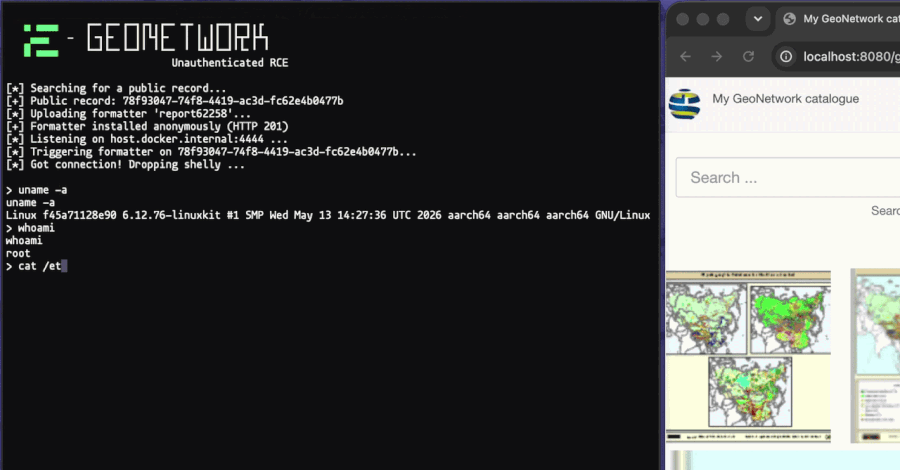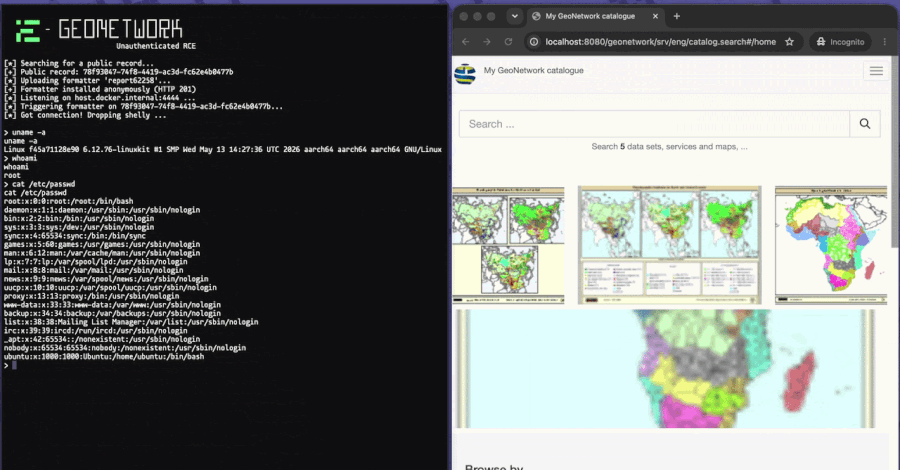
    Two vulnerabilities in GeoNetwork can be chained to achieve unauthenticated remote code execution (RCE) on the open-source geospatial metadata catalog, which sits behind many government and agency geoportals.

    The project shipped fixes in versions 4.4.12 and 4.2.17 on July 8, 2026, and published the vulnerability details on August 31.

    GeoNetwork originated at the United Nations Food and Agriculture Organization and is maintained under the Open Source Geospatial Foundation (OSGeo). It is a core component of many Spatial Data Infrastructure deployments across Europe and beyond, including the backend of the European INSPIRE geoportal.

    The chain combines a missing authorization check with an unsafe transformation engine. The first flaw, CVE-2026-63219 (CVSS score: 8.6), is a missing authorization check on the formatter upload endpoint.

    The unauthenticated file upload flaw allows an anonymous user to write arbitrary .xsl or .zip formatter files to the GeoNetwork formatter directory, which, on its own, constitutes unauthorized write access to server storage.

    “An unauthenticated attacker can upload arbitrary .xsl or .zip formatter files to the server,” the project said in the advisory.

    Cybersecurity

    The second flaw, CVE-2026-58400 (CVSS score: 9.1), is an unsafe configuration of the Saxon Extensible Stylesheet Language Transformations (XSLT) processor used to render formatters.

    The engine runs with secure processing enabled and Java extension functions disabled, so any stylesheet it loads can call java.lang.Runtime.exec() or java.lang.ProcessBuilder and run operating-system commands as the GeoNetwork process user.

    On its own, that second flaw requires privileges to upload a formatter, which is why it is scored as needing high privileges. Chaining it with the upload flaw removes that precondition, because the upload is reachable without authentication.

    An attacker first uploads a malicious formatter through the unprotected endpoint. A follow-up GET request to a public record then triggers the Saxon engine to execute the stylesheet, which delivers code execution. Security vendor Ethiack, whose researcher Rafael Castilho reported the flaws, said the chain is reachable starting with version 4.0.6, when the formatter endpoint was refactored, and the authorization line was dropped.

    Ethiack said it fingerprinted 121 internet-exposed GeoNetwork deployments running affected versions across 39 countries, and that 89 percent of them were government-, military-, or national-agency-related.

    Those figures describe exposed instances running vulnerable versions, not confirmed victims or compromises, and the fingerprinting is single-sourced to the vendor.

    All 4.4.x releases up to and including 4.4.11 and all 4.2.x releases up to and including 4.2.16 are affected, and the flaws are fixed in 4.4.12 and 4.2.17.

    “All users are strongly encouraged to upgrade to 4.4.12 or 4.2.17 as soon as possible,” the project said in its release announcement.

    Cybersecurity

    Until the update is applied, administrators can block write methods to the formatter endpoint at the reverse proxy, thereby blocking legitimate formatter uploads through the admin console.

    The advisory lists the following interim rules –

    • Apache httpd – deny POST, PUT, and PATCH requests to the /geonetwork/srv/api/formatters location.
    • Nginx – restrict the same location to GET, HEAD, and OPTIONS methods.

    The flaws were fixed roughly eight weeks before the advisories were published. The Hacker News found no reference to the GeoNetwork flaws in CISA’s Known Exploited Vulnerabilities catalog as of the disclosure, and no public reporting of exploitation in the wild.

    The disclosure follows a run of security issues across the wider geospatial stack. Last year, a critical GeoServer flaw (CVE-2024-36401, CVSS score: 9.8) was exploited into botnets, cryptocurrency miners, and the SideWalk backdoor, and a GeoServer XML External Entity (XXE) flaw (CVE-2025-58360) was added to CISA’s KEV catalog in December 2025 after evidence of active exploitation. Last month, a separate unauthenticated SQL injection to RCE in GeoServer, disclosed as a GeoServer zero-day, came under active probing shortly after it went public.

    Affecting Backends chain Fixes GeoNetwork Geoportal government RCE unauthenticated
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    Machine speed attacks require machine speed detection and response

    LiteLLM release pipeline hacked to distribute info-stealer malware

    HPE patches eight max severity RCE and auth bypass AOS flaws

    A Landmark Youth Climate Trial Against the Canadian Government Is About to Begin 

    Leaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release Pipeline

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Abercynon woman, 93, waits 10 hours on floor for an ambulance

    October 24, 2026

    Almost 1,000 arrested as clashes follow another day of mass protests across France

    October 24, 2026

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    October 24, 2026

    Scientists discover a hidden switch that burns fat and blocks new fat cells

    October 24, 2026
    Latest Posts

    Google AI health coach to use Abbott glucose data

    August 14, 2026

    CMF hit the balance between cheap and good clip earbuds

    August 14, 2026

    David Hearn’s Lawyers Ask Court to Bar Future Reflecting Pool Charges

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Abercynon woman, 93, waits 10 hours on floor for an ambulance

    October 24, 2026

    Almost 1,000 arrested as clashes follow another day of mass protests across France

    October 24, 2026

    Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads

    October 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.