

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Allseas books ABL for 60,000-ton topside single-lift ops in next North Sea decom chapter

    September 23, 2026

    The Consumer Financial Protection Bureaus’ Business-Friendly Move — ProPublica

    September 23, 2026

    What Machiavelli Would Say About Trump

    September 23, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Allseas books ABL for 60,000-ton topside single-lift ops in next North Sea decom chapter
    • The Consumer Financial Protection Bureaus’ Business-Friendly Move — ProPublica
    • What Machiavelli Would Say About Trump
    • Israel blasts ‘grotesque absurdity’ of Macron’s UN remarks on West Bank
    • Farmers’ race for £233m funding like ‘scramble for Oasis tickets’
    • UK to launch military squadron to protect satellites in space | Defence policy
    • 8 Best Space Heaters (2026): Tested, Measured, and Mistreated
    • Kyutai Releases Voice of Reason: A Speech-Native Model that Solves Spoken Math with Reinforcement Learning
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Wednesday, September 23
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 23, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    F5 has released security updates to address a critical BIG-IP APM zero-day vulnerability being exploited in remote code execution attacks.

    BIG-IP APM (short for Access Policy Manager) is the company’s centralized access management proxy solution that helps admins secure access to their organizations’ networks, applications, cloud, and application programming interfaces (APIs).

    Tracked as CVE-2026-94127, the flaw affects instances configured as an OAuth Authorization Server when a BIG-IP APM access policy and an OAuth profile are configured on a virtual server.

    “We have learned that this vulnerability has been exploited,” F5 warned in a security advisory published on Tuesday. “Deployments using APM strictly as an OAuth Client / Resource Server (without OAuth authorization server profiles configured) are not affected by this vulnerability.”

    The company advised customers to review systems for indicators of compromise if they detect a combination of multiple OAuth authentication failures and suspicious commands, shortly followed by a TMM SIGABRT.

    F5 also shared mitigation measures for admins who can’t immediately install the security updates, which require applying an iRule (available from F5 Support) to the affected BIG-IP APM virtual server.

    Internet threat monitoring non-profit Shadowserver currently tracks over 14,700 IP addresses with BIG-IP APM fingerprints. However, there is no information on how many have already been patched or are honeypots.
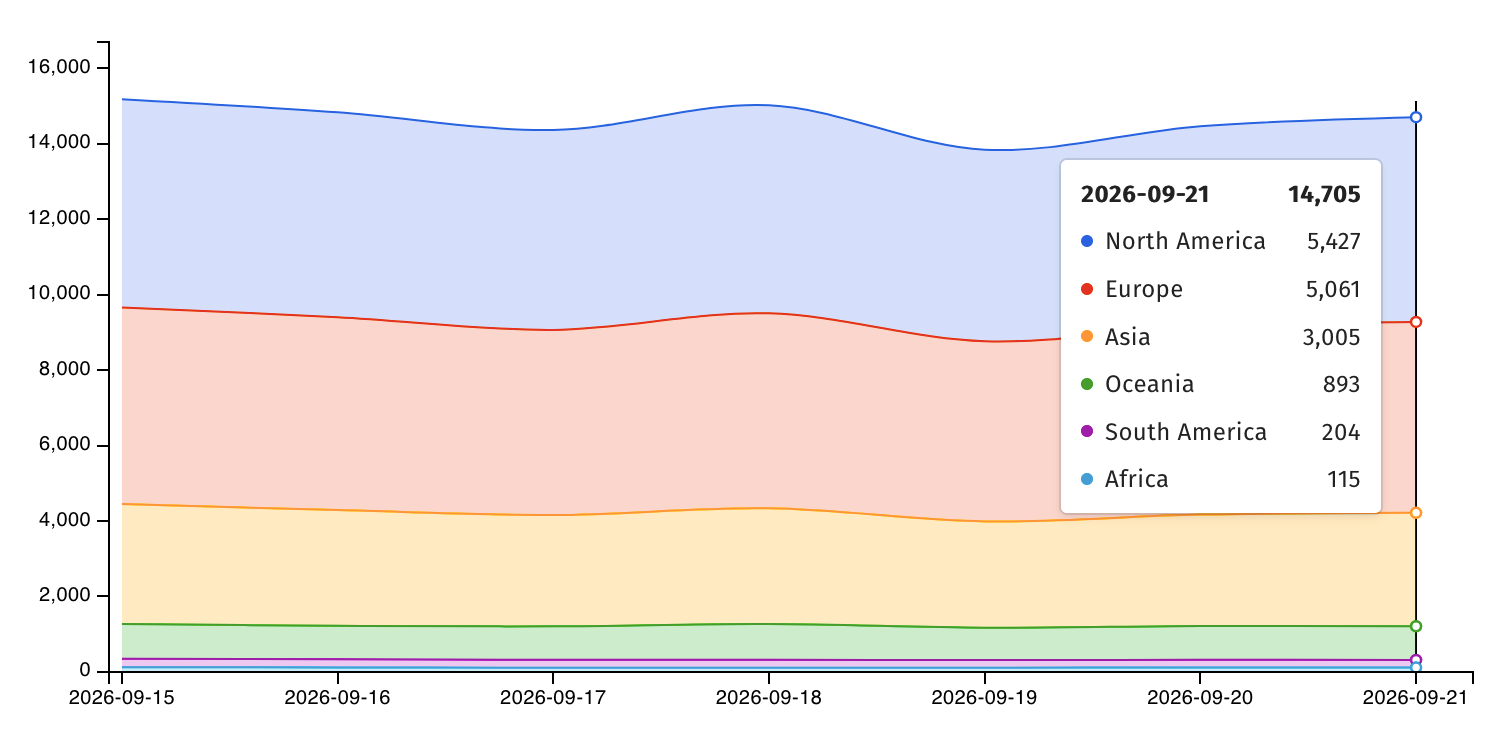
    F5 BIG-IP APM exposed online
    F5 BIG-IP APM exposed online (Shadowserver)

    On Tuesday, the Cybersecurity and Infrastructure Security Agency (CISA) also added CVE-2026-94127 to its Known Exploited Vulnerabilities (KEV) Catalog and ordered U.S. federal agencies to secure their networks against this flaw by Friday.

    “These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise,” the cybersecurity agency warned.

    Cybercrime and state-backed threat groups have often exploited F5 vulnerabilities in recent years. For instance, attackers have targeted security flaws in F5 products to breach corporate networks, hijack devices, ​​​​​​map internal servers, deploy data-wiping malware, and steal sensitive documents.

    F5 also disclosed in October 2025 that state-sponsored hackers breached its systems in August 2025 and stole undisclosed BIG-IP security source code and vulnerabilities.

    Since November 2021, CISA has flagged eight actively exploited F5 vulnerabilities, four of which have also been abused in ransomware attacks.

    F5 is a Fortune 500 company that provides cybersecurity, application delivery networking (ADN), and other services to more than 23,000 customers worldwide, including 48 of the Fortune 50 companies and 80% of the Fortune Global 500.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat

    APM attacks BIGIP Exploited Flaw Patches RCE ZeroDay
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Ryuk ransomware member sentenced to 24 months in prison

    Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input

    ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants

    Check Point warns of Management Server zero-day exploited in attacks

    Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials

    Only 13% of OT Network Segments Are Fully Isolated: Analysis

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Allseas books ABL for 60,000-ton topside single-lift ops in next North Sea decom chapter

    September 23, 2026

    The Consumer Financial Protection Bureaus’ Business-Friendly Move — ProPublica

    September 23, 2026

    What Machiavelli Would Say About Trump

    September 23, 2026

    Israel blasts ‘grotesque absurdity’ of Macron’s UN remarks on West Bank

    September 23, 2026
    Latest Posts

    COLDCARD security audit phishing attack installs remote access tool

    August 5, 2026

    Reddit aims to make ‘karma’ less important for first-time posters with shift to AI moderation tools

    August 5, 2026

    Right turn on green: is the Telegraph changing its tune on the climate? | Daily Telegraph

    August 5, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Allseas books ABL for 60,000-ton topside single-lift ops in next North Sea decom chapter

    September 23, 2026

    The Consumer Financial Protection Bureaus’ Business-Friendly Move — ProPublica

    September 23, 2026

    What Machiavelli Would Say About Trump

    September 23, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.