


The EvilTokens platform that compromised more than 12,000 Microsoft accounts at over 10,000 organizations has been disrupted in an effort led by Microsoft’s Digital Crimes Unit (DCU).
The phishing-as-a-service (PhaaS) operation emerged in February and was the first to support device code authentication at scale and offer cybercriminals AI-powered features for customizing lures and sifting through compromised inboxes to identify high-value targets.
In an announcement today, Microsoft said it coordinated the takedown of EvilTokens’ infrastructure, an action that involved the Health-ISAC, law enforcement, and SpyCloud, an identity threat protection company based in Austin, Texas.
Following the investigation, two men, aged 32 and 38, suspected of being administrators of the EvilTokens website were arrested in the U.K.
The Metropolitan Police Service received information about the suspects in August and executed warrants on Friday at addresses in Canary Wharf and Nine Elms. Both suspects were released on bail pending further investigation.
“The Met remains committed to holding people to account who facilitate criminal enabling functions and think they can remain undetected. We will find you and take action,” Detective Inspector Serena D’Adamo told BleepingComputer.
Microsoft tracks the EvilTokens threat actor as Storm-2992, stating that campaigns using the PhaaS platform impacted organizations in wholesale distribution, construction, financial services, real estate, higher education, and healthcare sectors.
The researchers say that the cybercriminal service specializes in device-code phishing, a technique that abuses the device-code authentication flow to obtain authentication tokens despite MFA protections, allowing attackers to compromise accounts without needing credential theft.
This led to a surge in device code phishing this year as multiple threat actors have adopted the method. By April, there were at least 10 phishing platforms supporting the capability.
Microsoft says in a report today that EvilTokens compromised more than 12,000 inboxes across over 10,000 organizations worldwide, fueling “sophisticated business email compromise (BEC) campaigns.”
SpyCloud’s recaptured phished data shows more than 8,708 compromised accounts across 6,585 corporate email domains in 79 countries.
EvilTokens abuses Microsoft’s legitimate OAuth 2.0 device-authorization flow, which is designed for devices with limited input capabilities, such as smart TVs, printers, conferencing equipment, and some Teams devices.
Source: Microsoft
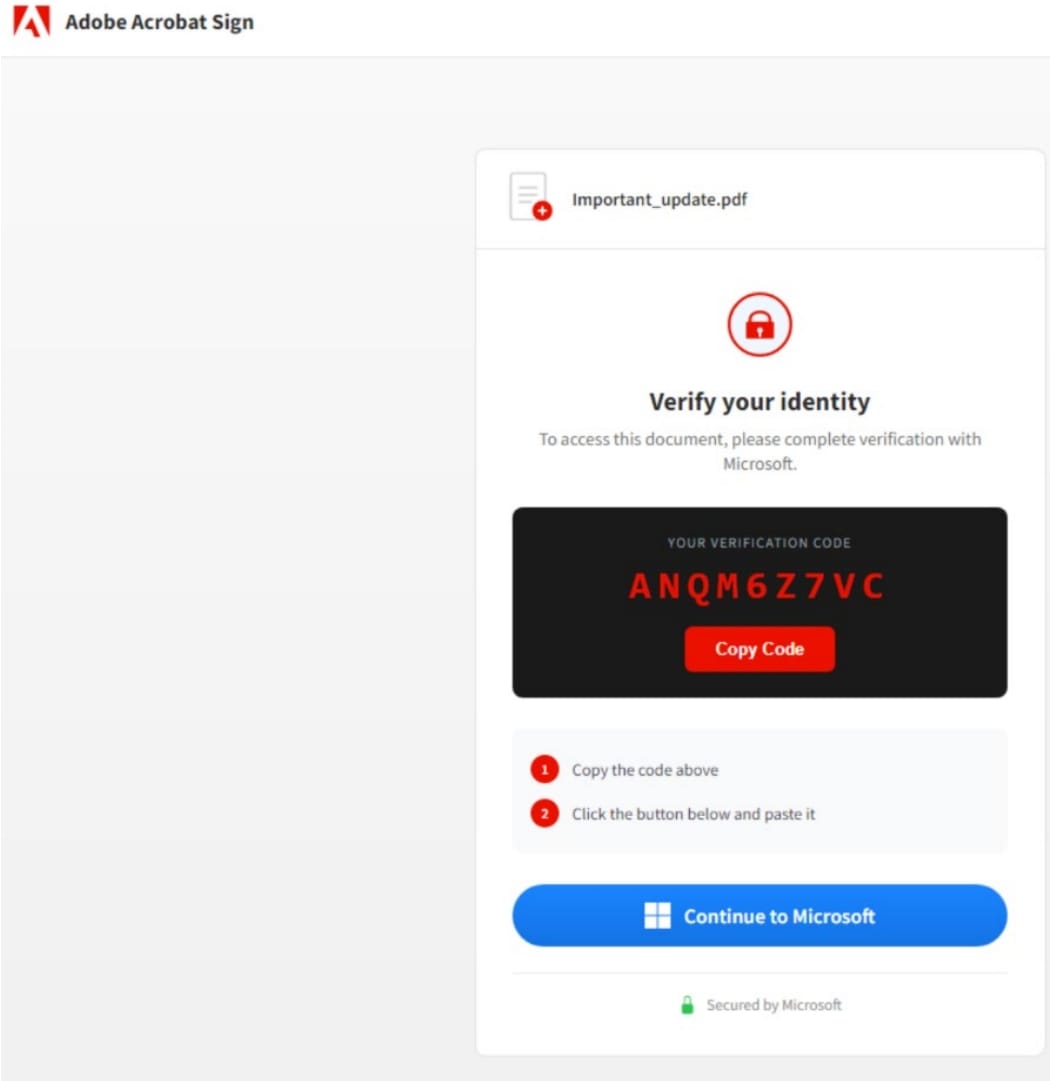
A device code phishing attack starts with the attacker initiating a device-code request and sending the received code to a target as part of a phishing lure.
The victim is directed to a page that displays the code and a button that links to Microsoft’s legitimate login portal, where they are prompted to authenticate.
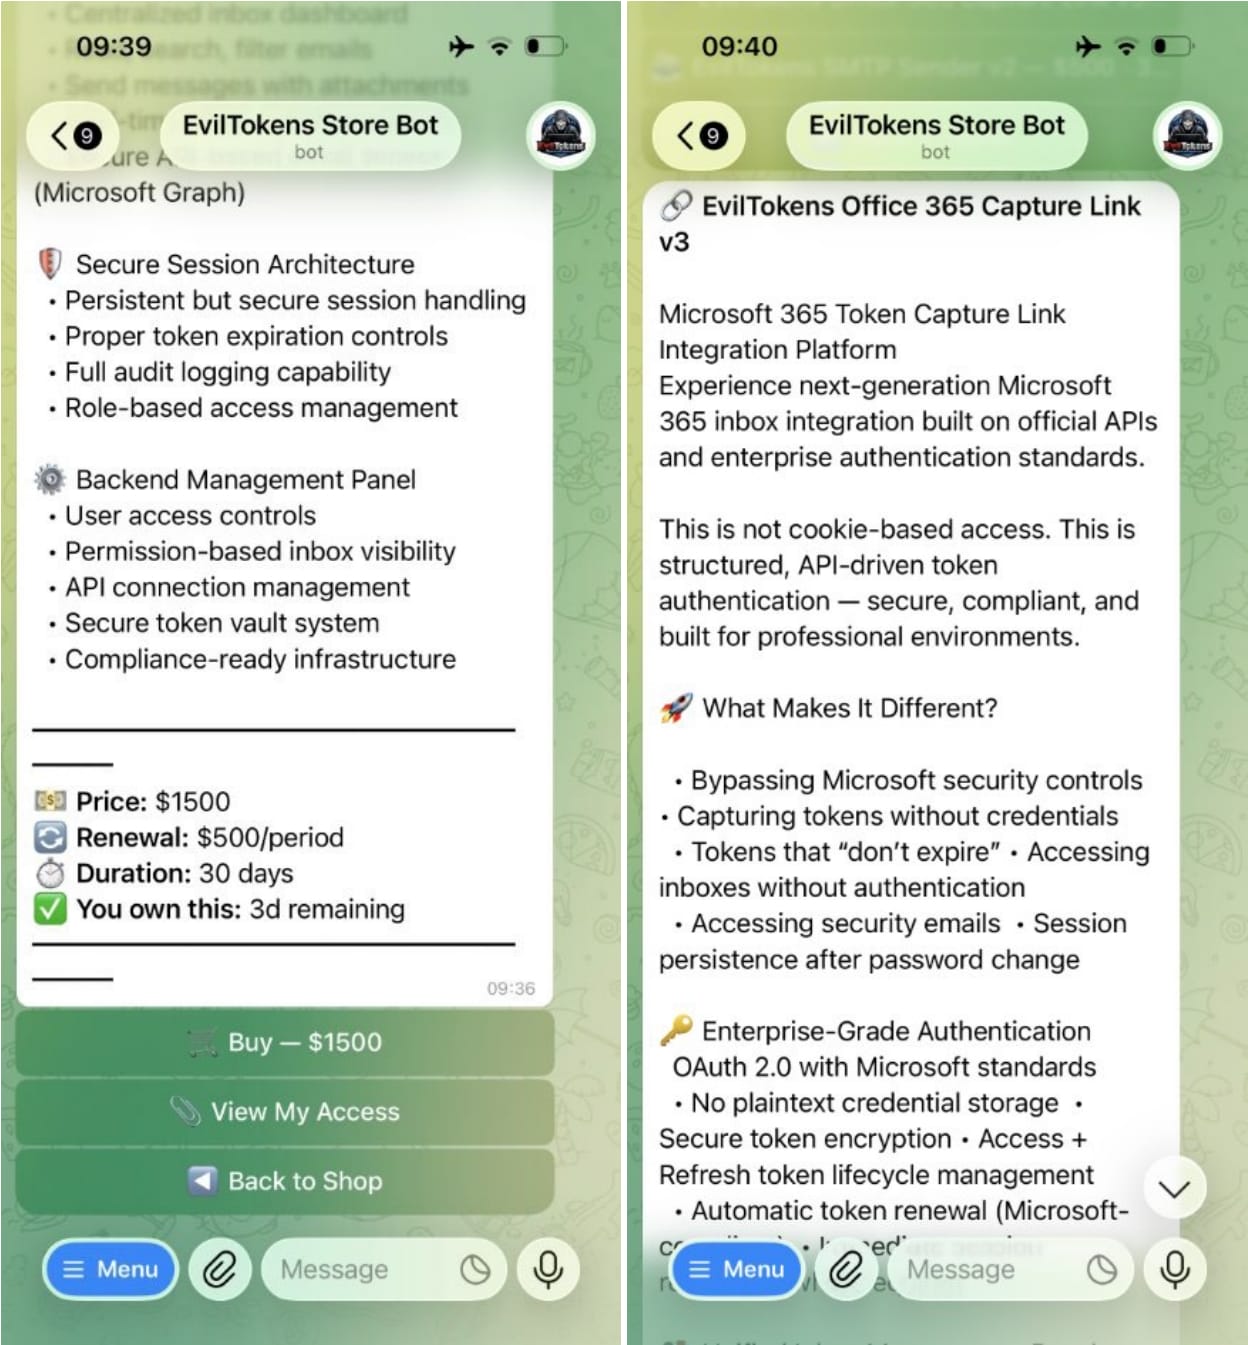
Storm-2992 promoted and supported EvilTokens through Telegram, where it offered access to the service for $500/month or a one-time fee of $1,500.
Source: Microsoft
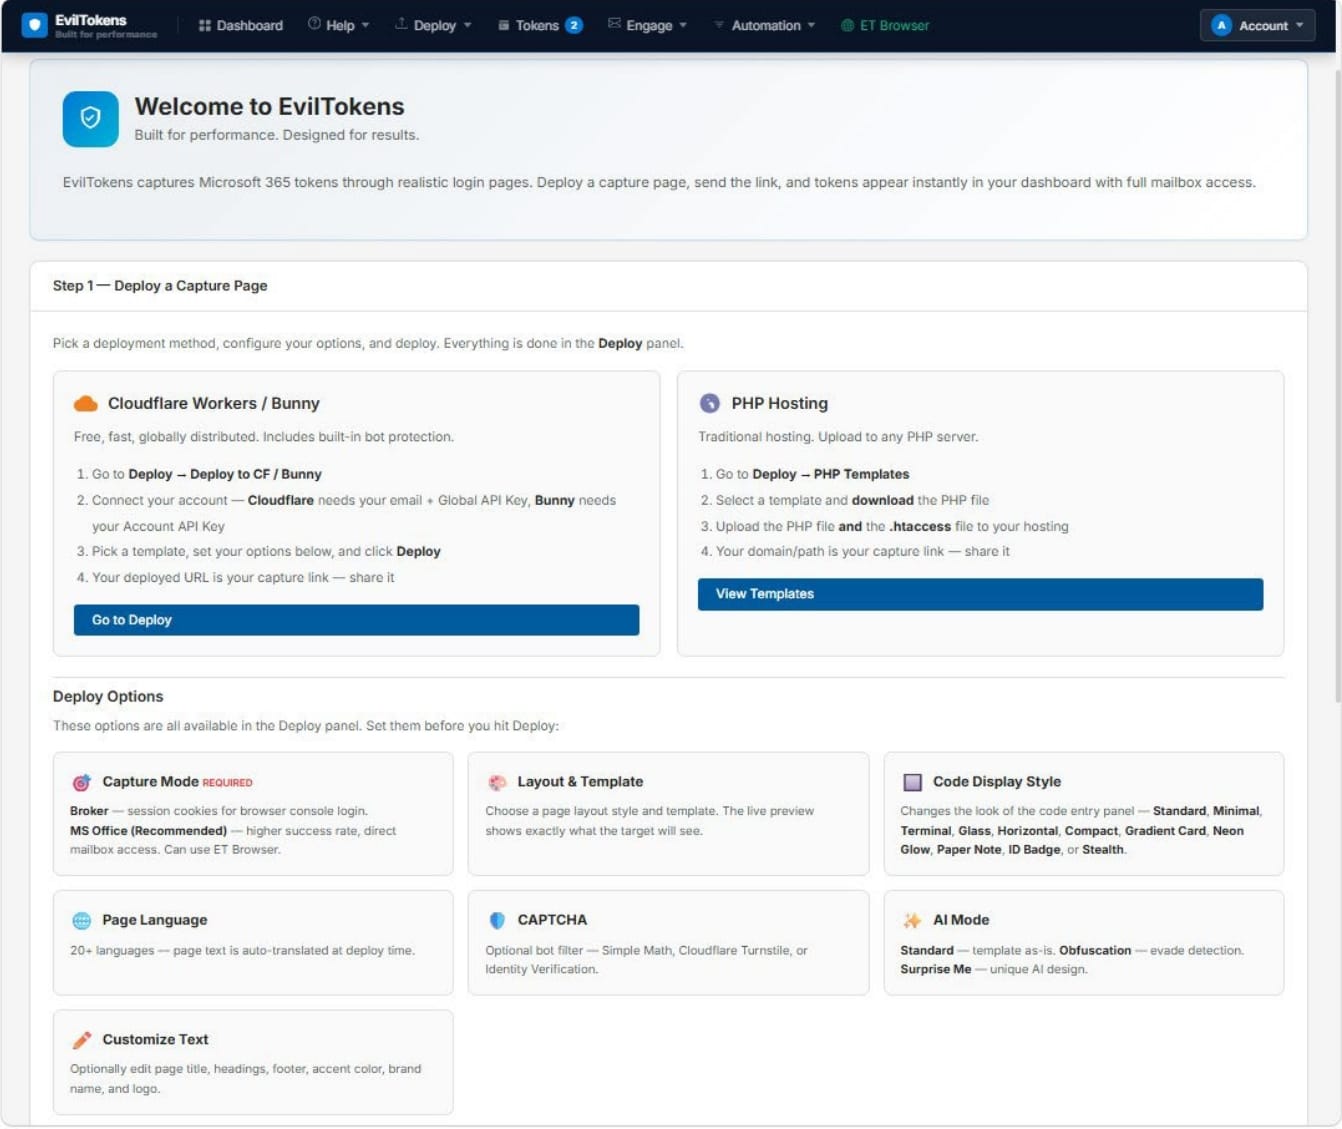
Add-ons such as anti-bot redirectors, B2B and SMTP sending tools, and an Office 365 capture-link tool were sold separately, and the service provides 44 customizable phishing kits.
The Lures impersonated document-signing platforms, Microsoft services, cloud identity and file-sharing providers, invoicing systems, voicemail, and eFax services.
The subject in the phishing emails varies from construction bids, partnership agreements, compensation and benefits notices to requests for proposals, shared files, invoices, and password-expiration warnings.
Source: Microsoft
After gaining access to an account, EvilTokens uses Microsoft Graph to map organizational relationships and AI-powered tools to analyze mailbox content and identify high-value targets within the breached environment.
The platform can search messages for wire-transfer information, pending invoices, and executive correspondence, then generate contextually relevant business email compromise (BEC) messages.
To evade detection, EvilTokens uses multi-stage redirects, PDFs, HTML attachments, and fake CAPTCHA pages to impede automated analysis, while routing traffic through compromised sites and legitimate cloud platforms such as Vercel, Cloudflare Workers, and AWS Lambda.
SpyCloud’s dataset shows that EvilTokens was focused on businesses, with roughly 97.5% of compromised accounts belonging to enterprise domains.
The most targeted countries are the United States, followed by Canada, Australia, the United Kingdom, and Saudi Arabia.
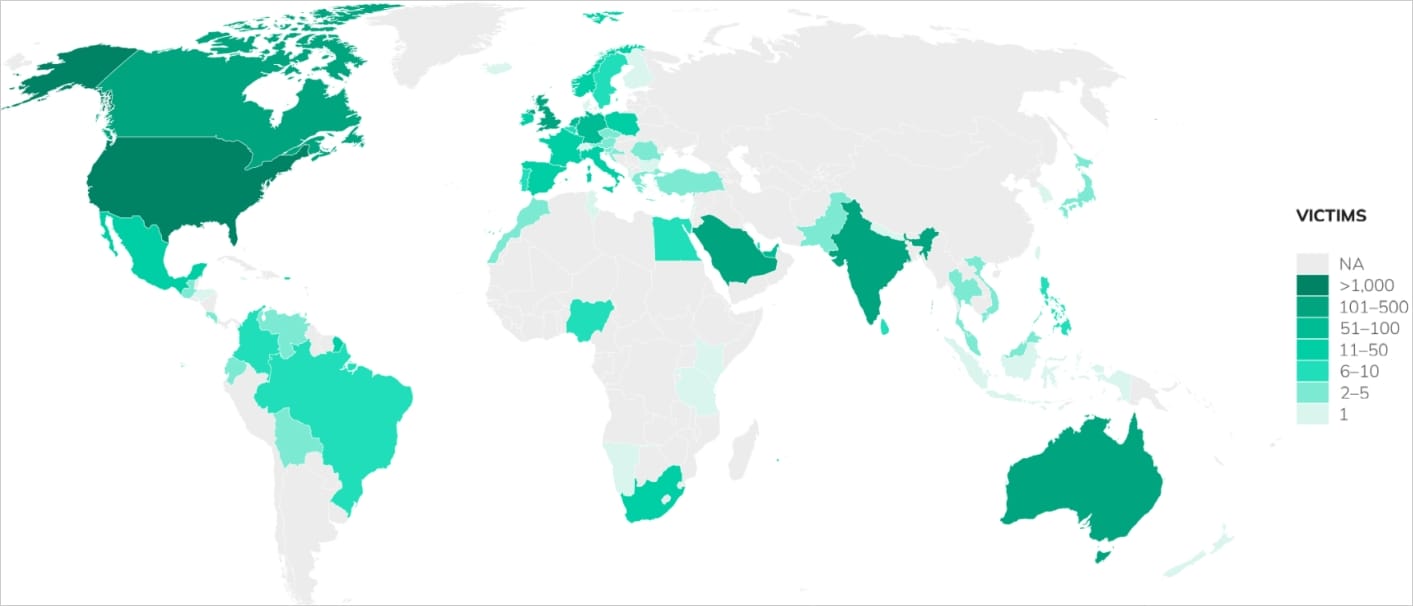
Source: SpyCloud
Microsoft and its partners disrupted EvilTokens by obtaining legal authority to seize active infrastructure associated with the phishing service; however, this was not a takedown operation, and the threat remains active, though attacks should noticeably decrease in volume.
EvilTokens is far from the only device-code phishing platform, and affiliates have already created “clones” such as APToken.
To defend against these attacks, organizations should disable device-code authentication when it is not required and block the device-code flow wherever possible.
Users should also verify the application they are authenticating to and avoid proceeding if they are not signing in to an expected app.
Mitigation and protection guidance also include monitoring for suspicious login activity and using phishing-resistant authentication methods like FIDO2 security keys or passkeys.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
