

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Amazon’s Ring wants to replace local WhatsApp groups. It’s a recipe for curtain-twitching disaster | Imogen West-Knights

    September 26, 2026

    Athens explosion: At least two dead in blast near Acropolis in Plaka district

    September 26, 2026

    US rejects pleas from OpenAI, Anthropic for global AI standards

    September 26, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Amazon’s Ring wants to replace local WhatsApp groups. It’s a recipe for curtain-twitching disaster | Imogen West-Knights
    • Athens explosion: At least two dead in blast near Acropolis in Plaka district
    • US rejects pleas from OpenAI, Anthropic for global AI standards
    • Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
    • Google Built an AI That Hunts Its Own Security Bugs
    • A plan to save Bali’s lost fireflies
    • Does video show Netanyahu saying ‘America deserved 9/11’ in UN speech? We examined footage
    • ChatGPT says its rogue AI agents posted users’ images online, entered federal website
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, September 26
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 26, 2026 Cybersecurity No Comments2 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananSep 26, 2026Vulnerability / Web Security

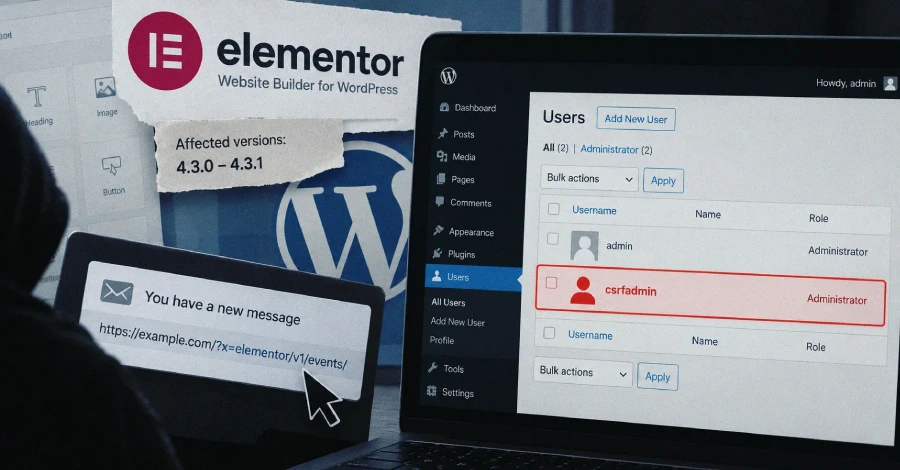
    Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site.

    The cross-site request forgery (CSRF) vulnerability, which has yet to be assigned a CVE identifier, carries a CVSS score of 8.8 out of 10.0. It only affects versions 4.3.0 and 4.3.1 of the plugin, which is active on over 10 million WordPress sites. Statistics from WordPress.org show that the two impacted versions alone have been installed on more than 2 million sites.

    “One link, opened by a logged-in WordPress user, makes that user carry out any REST API action their account is permitted to perform,” Patchstack said. “On a stock installation, an administrator clicking the link creates a second administrator account for the attacker.”

    The WordPress security company said the attack does not hinge on any prerequisite, such as JavaScript, a submitted form, or a web page under the threat actor’s control. The link can even be a plain anchor tag embedded in an email, a chat message, or a comment.

    Following responsible disclosure, the issue has been addressed in version 4.3.2 released earlier this week. A security researcher going by the alias “Saggre” has been credited with discovering and reporting the bug.

    Cybersecurity

    Patchstack said the vulnerability stems from the Editor Events module skipping CSRF protection for cookie-authenticated REST API requests every time the literal string “elementor/v1/events/” appears anywhere in the request URI.

    “Because the request URI includes the query string, and the query string is written by whoever composes the link, any REST request can opt itself out of that protection by appending a harmless-looking parameter,” it added.

    The bypass applies to the entire REST API surface of a site, including WordPress core routes and the routes of every other plugin installed on it. An attacker could exploit this loophole to create an administrator account through “/wp/v2/users” using a request like below –

    https://example.com/wp-json/wp/v2/users
    ?_method=POST
    &username=csrfadmin
    &email=csrfadmin%40example.test
    &password=...
    &roles%5B%5D=administrator
    &x=elementor/v1/events/

    Because Elementor releases before 4.3.0 do not ship the Editor Events proxy, they are not affected by the flaw. Users of the plugin are advised to apply the latest update as soon as possible to counter any potential threat.

    Admin Attackers Clicks Crafted CSRF Elementor Flaw lets link sites
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Microsoft plans to deprecate Windows Deployment Services

    Kosovar Owner of Rydox Marketplace Pleads Guilty in US Court

    With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

    CISA Election Security Plan Flags Patching Barriers, Voter Database Attacks

    North Korea Suspected in $351 Million Bitget Crypto Heist

    In Other News: Clop Leak Site Takeover, Docker Botnet Hunts AI Keys, Water Utility Exposure

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Amazon’s Ring wants to replace local WhatsApp groups. It’s a recipe for curtain-twitching disaster | Imogen West-Knights

    September 26, 2026

    Athens explosion: At least two dead in blast near Acropolis in Plaka district

    September 26, 2026

    US rejects pleas from OpenAI, Anthropic for global AI standards

    September 26, 2026

    Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

    September 26, 2026
    Latest Posts

    A Growing Number of Election Deniers Hold Key Local Roles in Midterms

    August 6, 2026

    Lithuania warns Russia could be considering possible ‘false flag’ strike on the Baltics – Europe live | Europe

    August 6, 2026

    Will Mamdani’s city-run grocery stores require ID to shop? Here’s the truth

    August 6, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Amazon’s Ring wants to replace local WhatsApp groups. It’s a recipe for curtain-twitching disaster | Imogen West-Knights

    September 26, 2026

    Athens explosion: At least two dead in blast near Acropolis in Plaka district

    September 26, 2026

    US rejects pleas from OpenAI, Anthropic for global AI standards

    September 26, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.