

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7

    October 22, 2026

    Just 4 minutes a day can dramatically improve strength after 65

    October 22, 2026

    Diabetes and ADHD drugs to be tested on Alzheimer’s patients in new study

    October 22, 2026
    Facebook X (Twitter) Instagram
    Trending
    • High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7
    • Just 4 minutes a day can dramatically improve strength after 65
    • Diabetes and ADHD drugs to be tested on Alzheimer’s patients in new study
    • What Congo’s New Rebel Alliance Means for the Country’s Conflict
    • Does video show Trump neglecting to salute US Marines after departing Marine One?
    • Publishers want Brussels and London to stop Meta’s new AI terms – POLITICO
    • Aneurin Bevan’s personal security file was ‘remarkably tame’ – National Archives | Labour
    • Recursive Releases Flint, an Open-Weight 40B MoE Local Coding Model for Agents with 2.5B Active Params
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Thursday, October 22
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 1, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    Ravie LakshmananAug 31, 2026Cyber Espionage / IoT Botnet

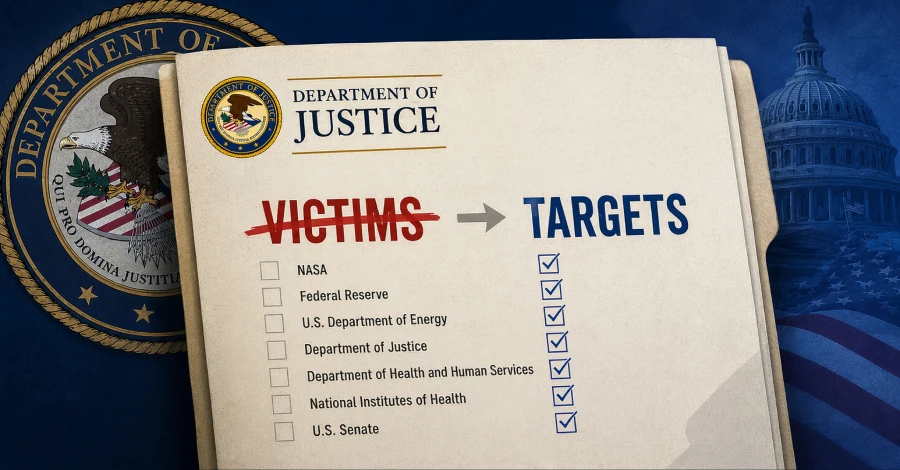
    The U.S. Department of Justice (DoJ) on Friday corrected a previously issued press statement that several of its agencies were victims of attacks carried out by Chinese threat actors, instead now pointing out that they were among those targeted.

    Last week, the DoJ said the National Aeronautics and Space Administration, Federal Reserve, Department of Energy, Department of Justice, Department of Health and Human Services, National Institutes of Health, and the U.S. Senate were some of the victims of “computer intrusion activity” orchestrated by QTFY, a state-sponsored group affiliated with the People’s Republic of China (PRC).

    In the newly updated statement, the aforementioned agencies have been listed as “among the targets of QTFY.” The update was reported by Reuters over the weekend.

    “Edits have been made to ensure this press release accurately reflects the government’s allegations in the affidavit in support of the domain seizures,” the DoJ said in a note.

    Cybersecurity

    According to the affidavit, QTFY (aka QT AND QTCYBER) works for a private Chinese company known as Nanjing Xinjiuwei Network Technology Co, adding payments from the Ministry of State Security (MSS) suggest that the company conducts malicious cyber activities on behalf of Beijing.

    The threat actor is believed to have been active since 2018. Infrastructure linked to the adversary has been used to compromise critical and sensitive networks in the U.S. and abroad. Besides targeting U.S. federal government networks, the group has singled out hospitals, telecom operators, power companies, financial institutions, and defense contractors.

    Described as a technical quartermaster, QTFY has provided reconnaissance, proxy management, and operational routing capabilities to facilitate Chinese cyber espionage activities. Two of the core products in its arsenal are QScan, a vulnerability scanning and exploitation platform, and QTRouter, which is an obfuscation network.

    In one case dating back to 2019, the threat actor is said to have attempted to break into the National Aeronautics and Space Administration by exploiting CVE-2019-11510, a critical vulnerability impacting Pulse Secure VPN.

    The change in wording is significant as it suggests that while the activity may have targeted a broad range of organizations, only some of them were actually compromised.

    The U.S. Federal Bureau of Investigation (FBI) has since disrupted the domains connected to QScan and QTRouter (qtproxy[.]xyz, qt-proxy[.]org, and qt-team[.]com), effectively neutralizing the malware’s functions.

    Lumen Black Lotus Labs has revealed that the threat actor has industrialized the creation of Operational Relay Box (ORB) networks for China-linked espionage operations, creating a decentralized botnet of infected IoT devices and leased VPSs that enables them to obscure the true origins of the malicious activity.

    Cybersecurity

    QTFY sells access to QScan and QTRouter for other actors to identify and exploit vulnerable IoT devices. This, in turn, allows both QTFY actors and its customers to enlist those devices as botnet nodes in QTRouter.

    The network also comprises nodes operated by the Chinese commercial proxy service fastlink[.]ws. The entire architecture underpins Fast Labyrinth, an encrypted relay network that blends malicious traffic with legitimate network activity.

    “By routing their malicious internet traffic through IoT devices (compromised by QScan) local to their victims, these Chinese hackers can blend in with legitimate users and remain undetected when scanning and attacking critical infrastructure and other targets,” the affidavit alleged.

    agencies China claim corrects DoJ hacking targets U.S Victims
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7

    LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor

    A lifesaving medication is not behind the drop in U.S. overdose deaths

    China Sees Exports Growth Amid AI Boom and Easing U.S. Trade Tensions

    ‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets

    PHP2Shell Patches Land as First Exploitation Attempts Hit Sensors

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7

    October 22, 2026

    Just 4 minutes a day can dramatically improve strength after 65

    October 22, 2026

    Diabetes and ADHD drugs to be tested on Alzheimer’s patients in new study

    October 22, 2026

    What Congo’s New Rebel Alliance Means for the Country’s Conflict

    October 22, 2026
    Latest Posts

    Leavitt to depart the White House

    August 13, 2026

    Israeli troops force families from homes amid settler terror campaign in West Bank | West Bank

    August 13, 2026

    Video of children being taught Muslim prayers does not show a school in England – Full Fact

    August 13, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7

    October 22, 2026

    Just 4 minutes a day can dramatically improve strength after 65

    October 22, 2026

    Diabetes and ADHD drugs to be tested on Alzheimer’s patients in new study

    October 22, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.