

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

    October 24, 2026

    Nearly 20% of Switzerland’s glacier ice has vanished in just five years

    October 24, 2026

    Amazon communities lose water as mining and deforestation reshape rivers

    October 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws
    • Nearly 20% of Switzerland’s glacier ice has vanished in just five years
    • Amazon communities lose water as mining and deforestation reshape rivers
    • Why Putin’s American Defenders Look Like Stalin’s Fellow Travelers
    • Does video show Trump making strange noise during South Carolina rally?
    • France bolsters security as businesses fear renewed unrest during Saturday protests
    • Andy Bloke appears vaguely normal on Gogglebox – but Kemi dodged a bullet | John Crace
    • Moonshot AI Releases Kimi K3.1 Pro: A 2.8T Total/104B Active Params (MoE) Model with 1M Context
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Crypto & Blockchain

    Cosmos misjudged a critical bug for 4 months before hackers stole nearly $6 million across 6 chains

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 28, 2026 Crypto & Blockchain No Comments4 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A Cosmos EVM vulnerability exploited across six networks, including MANTRA, exposed a security gap spanning around 40 blockchains.

    On Aug. 28, Cosmos Labs said the same accounting flaw was exploited on six networks, including MANTRA, TAC, and KiiChain, before an emergency response spread across the broader Cosmos EVM ecosystem.

    Attackers converted about $2.87 million through decentralized exchanges and an estimated $2.85 million through centralized venues, according to a Cosmos security postmortem. Accounts connected to the centralized-exchange activity have since been frozen.

    MANTRA suffered the largest publicly detailed hit. An unprivileged wallet moved about 720.9 million tokens from two addresses that had not authorized the Aug. 20 transactions, without compromising validator, administrator, governance, or multisig keys.

    Related Reading

    MANTRA Chain is back online, but silent code changes spark developer concerns

    The vulnerability affected the broader Cosmos/EVM ecosystem, which is a shared software layer that gives Cosmos SDK chains Ethereum-compatible functionality. After the attacks began, Cosmos Labs contacted 40 networks and said 13 other potentially exposed chains patched, halted, or applied mitigations before they were exploited.

    The response also uncovered 11 Cosmos EVM deployments that Cosmos Labs had not previously known about through its security-communication channels.

    That potential reach sits within a broader Cosmos ecosystem valued at more than $7 billion, according to CryptoSlate’s data. Meanwhile, this figure includes projects that might not have used the vulnerable software and does not represent the amount directly exposed.

    Cosmos initially underestimated the vulnerability

    Cosmos Labs revealed that the flaw had been reported months before attackers exploited it.

    The firm said it received the initial report about the vulnerability on April 25 but concluded after testing that the vulnerability affected six-decimal networks, while known production Cosmos EVM chains used 18 decimals. Engineers therefore believed deployed networks were not at risk.

    According to the firm:

    “Based on that assessment, Cosmos Labs addressed the vulnerability through its silent, public patch process rather than the private patch distribution process used when a vulnerability is believed to threaten live user funds.”

    A fix was merged into the main codebase on May 15 and handled as a silent public patch rather than an emergency security release. At the same time, it was not immediately backported to older branches because the change was state-breaking and required coordinated upgrades.

    The Daily Brief

    The signal, before the noise.

    Start your day with the crypto stories moving markets, decoded by CryptoSlate’s editors.

    One email. Everything that matters.

    Free to join. Unsubscribe any time.

    Whoops, looks like there was a problem. Please try again.

    You’re on the list. Your next Daily Brief is on its way.

    That assessment changed in early August when further research showed Cosmos EVM deployments were vulnerable regardless of their decimal configuration.

    Patched v0.6.2 and v0.7.2 releases arrived late on Aug. 19. The next morning, a public pull request in another project’s fork described the vulnerability and exploitation path. MANTRA’s first known unauthorized transaction followed less than 12 hours later.

    The flaw combined two accounting failures. An attacker could trigger an unsigned-integer underflow that created an abnormally large balance, then use that state to overflow another account and extract its legitimate balance without increasing total token supply.

    TAC reported exploitation roughly 45 hours after MANTRA, with KiiChain following soon afterward. Cosmos Labs subsequently recommended that Cosmos EVM chains halt and upgrade while it coordinated the broader response.

    MANTRA absorbed the biggest disclosed hit

    On MANTRA, the attacker moved roughly 600 million tokens from a burn address and another 120.9 million from a legacy genesis-era multisig.

    No new tokens were minted. Instead, previously inert balances became transferable, increasing circulating supply by about 720.9 million MANTRA.

    The project valued the movement at roughly $3.6 million using the pre-incident price. As of Aug. 28, no tokens had been recovered. About 38 million remained immobilized in the attacker account, while the remainder had been traced through exchange routes and referred to platforms and law enforcement.
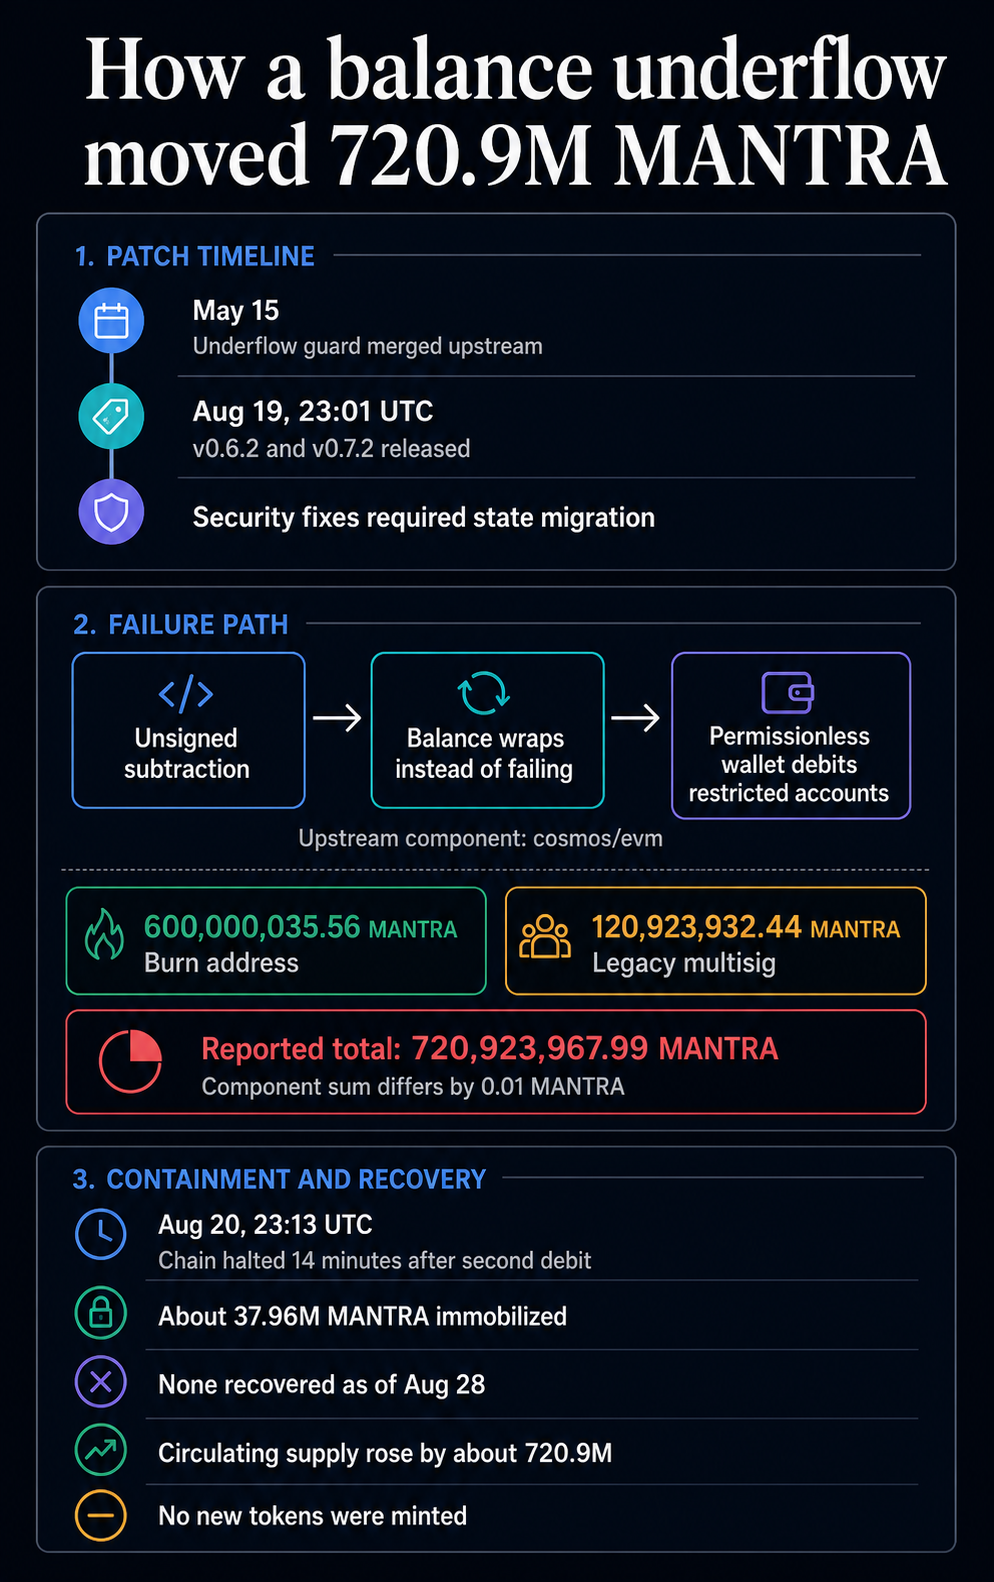
    Timeline showing the cosmos/evm underflow patch, two MANTRA debits, chain halt and recovery status

    MANTRA also acknowledged that its monitoring failed to flag the first transaction for almost four hours because it treated the burn address as incapable of moving funds. The chain halted 14 minutes after a second unauthorized debit, resulting in an outage of about 30 hours.

    MANTRA fell to an all-time low following the attack before rebounding about 14% to roughly $0.004744 after the postmortem.

    The wider fallout has pushed Cosmos Labs to revise its vulnerability triage and disclosure procedures after a flaw initially judged unlikely to threaten production chains ultimately reached six networks and forced emergency action across dozens more.

    Bug Chains Cosmos critical hackers Million misjudged months stole
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

    Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials

    Critical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted Image

    Capcom confirms data breach affecting 11.7 million accounts

    Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks

    Indurex Raises $8 Million to Expand Industrial Cybersecurity Platform

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

    October 24, 2026

    Nearly 20% of Switzerland’s glacier ice has vanished in just five years

    October 24, 2026

    Amazon communities lose water as mining and deforestation reshape rivers

    October 24, 2026

    Why Putin’s American Defenders Look Like Stalin’s Fellow Travelers

    October 24, 2026
    Latest Posts

    ‘This is hell’: British widow ‘sick’ with worry over threat of being removed from Sweden | Sweden

    August 14, 2026

    Prichard Colon dies from boxing injury that resulted in 221-day coma | Boxing News

    August 14, 2026

    Weather forecasts once gave Britons something safe to chat about. Not any more | Andy Beckett

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

    October 24, 2026

    Nearly 20% of Switzerland’s glacier ice has vanished in just five years

    October 24, 2026

    Amazon communities lose water as mining and deforestation reshape rivers

    October 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.