

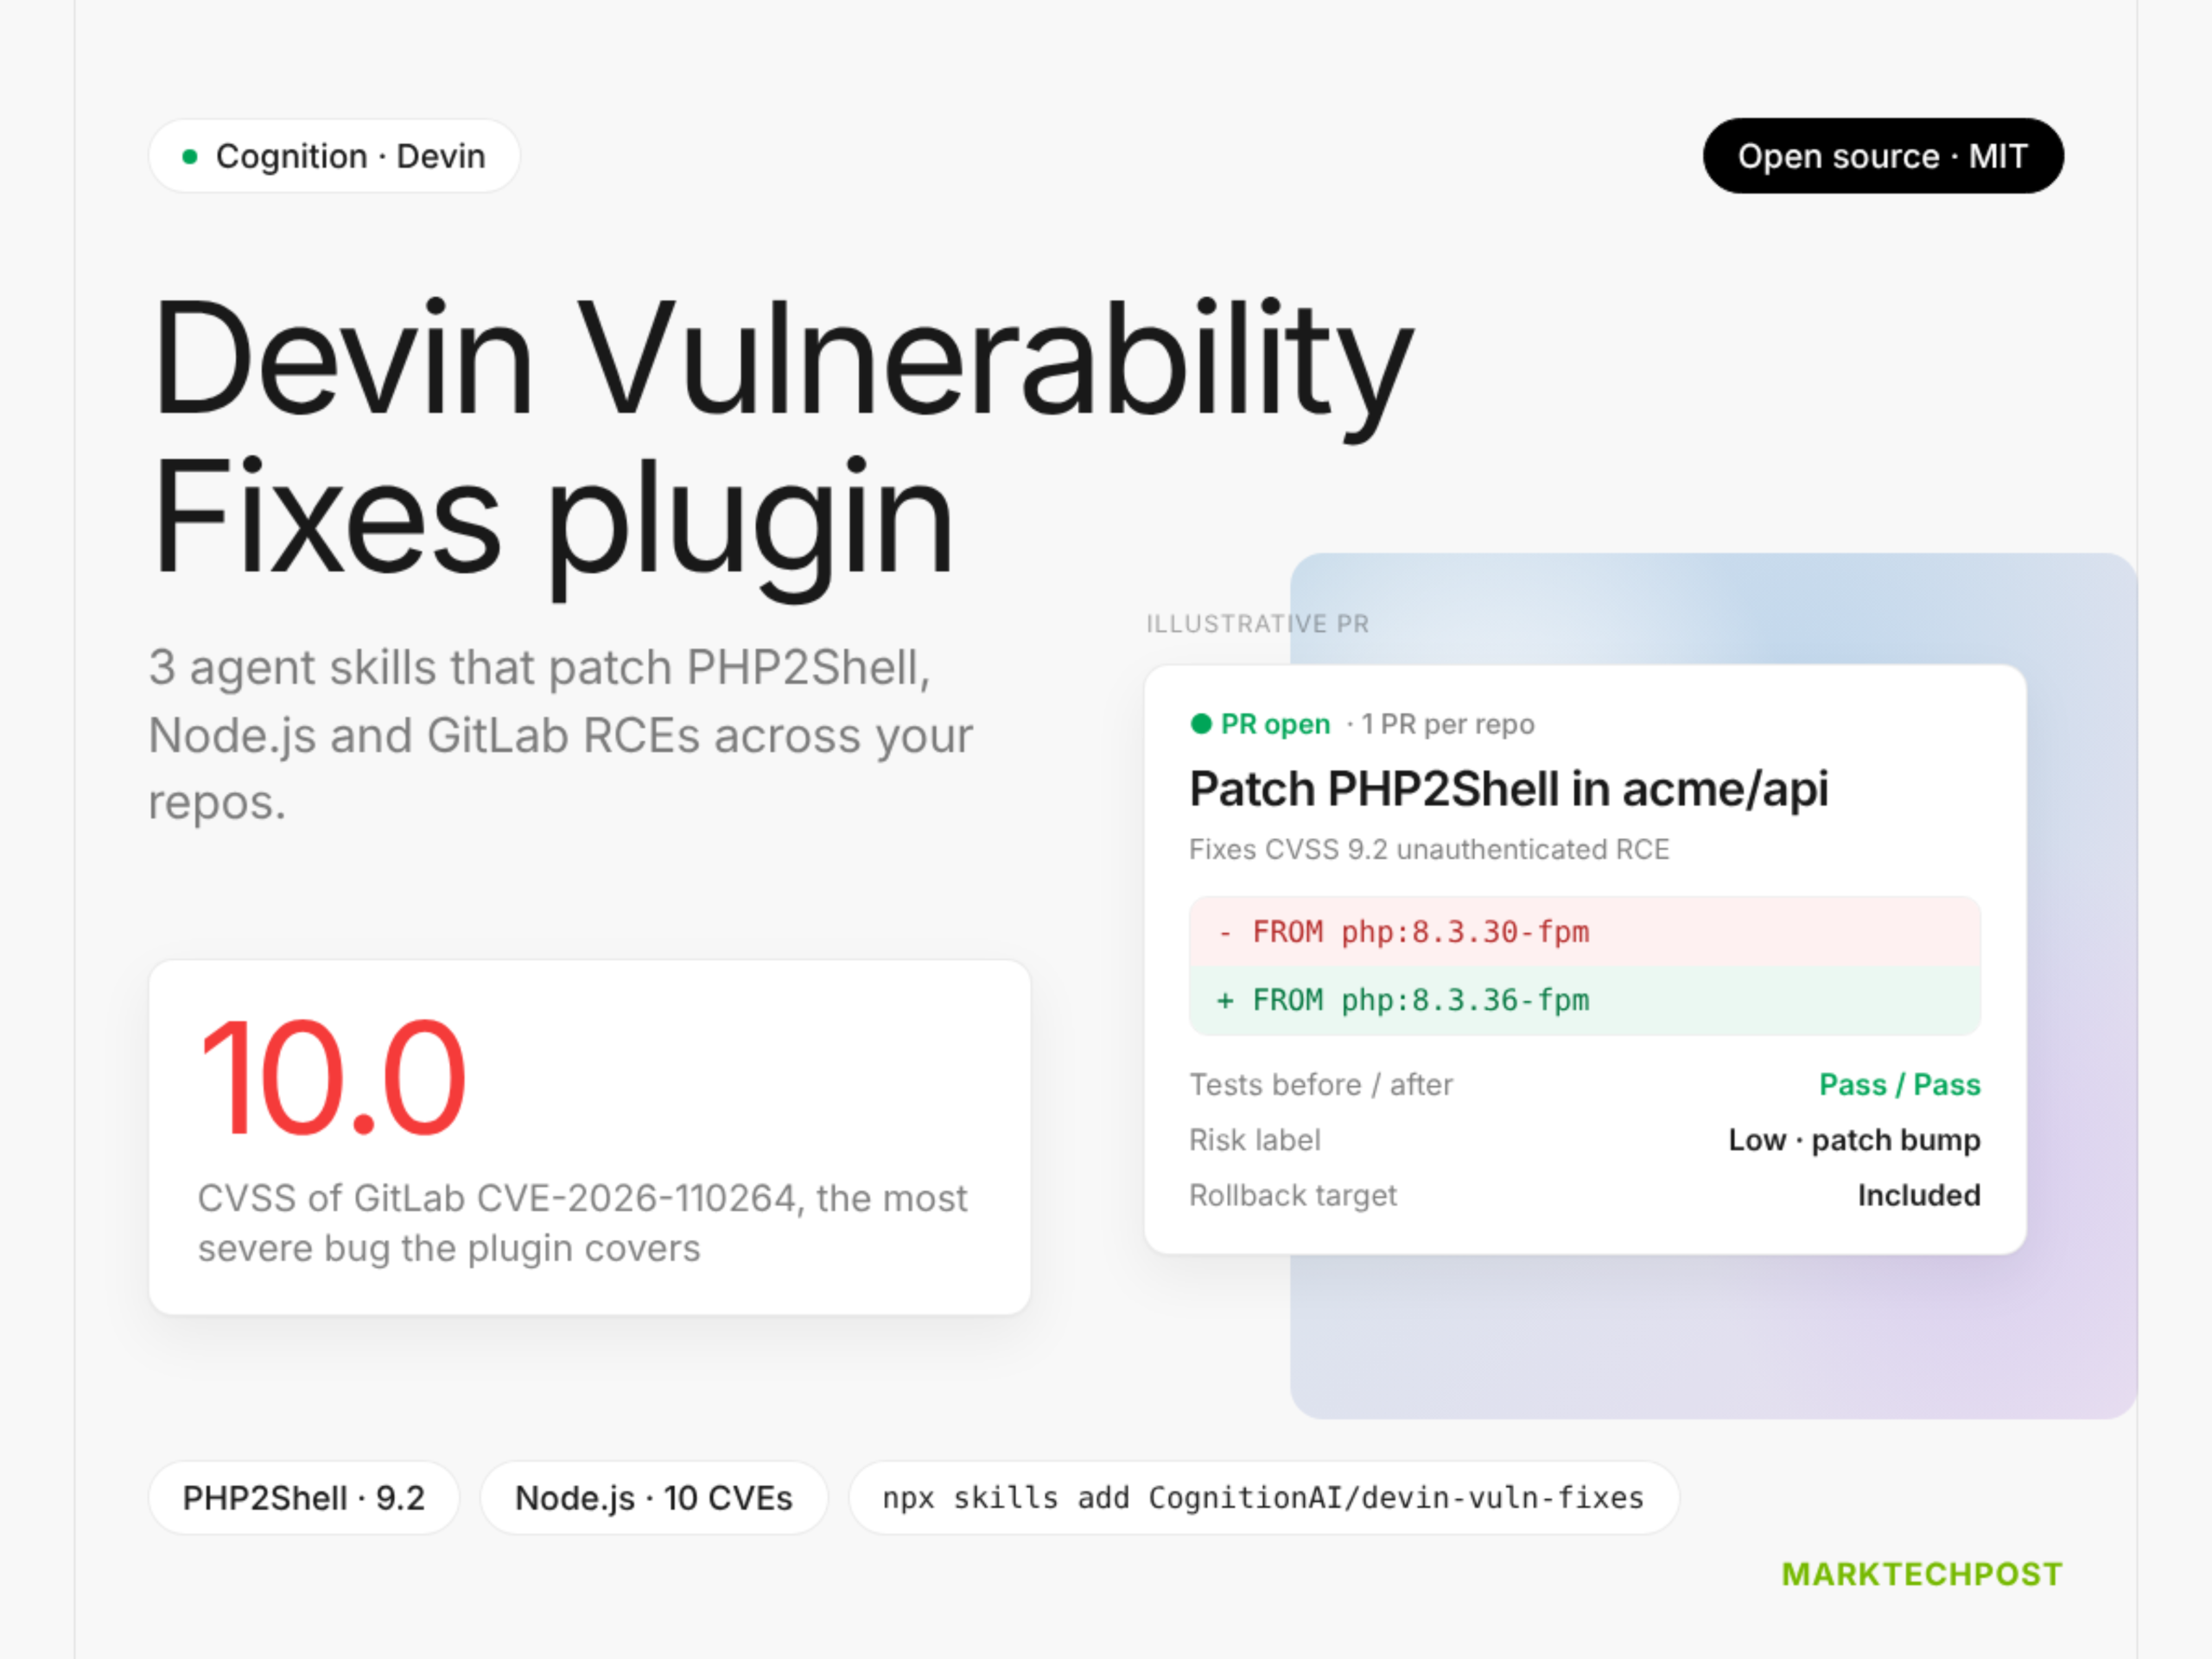
Cognition has released the Devin Vulnerability Fixes plugin, a free, open-source set of agent skills. It targets three critical remote code execution (RCE) advisories. They cover PHP2Shell, the Node.js October 21, 2026 security release and a CVSS 10.0 self-managed GitLab bug. The skills run in Devin and in any coding agent that reads SKILL.md files. Cognition packaged the remediation workflow it used internally. Developers can do inventory, approve, patch, test, then ship 1 pull request per repository.
TL;DR
- Size: Three skills (
fix-php-vuln,fix-node-vuln,fix-gitlab-vuln), MIT license. - Runs on: Devin, Claude Code, Codex, Cursor, Factory Droid, GitHub Copilot, Gemini CLI, OpenCode and Windsurf. Needs git, a shell, Docker and registry access. The
npx skillsinstall needs Node.js 22.20 or later. - Performance: No remediation benchmark or fix-rate number is published for the plugin.
- Best: Covers the week’s most severe bug, GitLab CVE-2026-110264, rated CVSS 10.0.
- Worst: Validation is only as strong as your tests. Managed runtimes, appliances and Electron apps are flagged, not patched.
What is the Devin Vulnerability Fixes plugin?
The Devin Vulnerability Fixes plugin is a set of three Agent Skills from Cognition. They find and patch vulnerable PHP, Node.js and self-managed GitLab deployments. The source is on GitHub under the MIT license. Cognition’s product page lists it as free and open source.
Which vulnerabilities does it fix?
- PHP2Shell (CVE-2026-109618, CVE-2026-109619): PHP rates both flaws CVSS v4.0 9.2. The first corrupts memory after an out-of-memory condition. The second lets stale global state from one request reach the next. PHP says every web-serving setup is at risk, with mod_php rated highest risk. Fixed versions are 8.2.35, 8.3.36, 8.4.27 and 8.5.12. PHP 8.1 and older get no releases, only source backports for 7.4, 8.0 and 8.1.
- Node.js October 2026 release: It fixes 10 CVEs, 4 rated High. The lead bug, CVE-2026-111497, is a Brotli decoder out-of-bounds write that can enable RCE. Fixed versions are 22.23.4, 24.22.1 and 26.12.1. Node.js 20 and older are end-of-life and get no fix.
- GitLab CVE-2026-110264: An integer overflow in the regular expression compiler allows unauthenticated code execution. It affects GitLab CE/EE from 7.0 onward and scores CVSS 10.0. GitLab.com and GitLab Dedicated are already patched.
How does the plugin work?
Every skill follows the same five-step shape:
- Read-only inventory: The agent scans Dockerfiles, base images, distro packages, CI, Helm, Terraform, Packer, Lambda and config management.
- Approval gate: Nothing changes until you pick repos. Riskier minor or major upgrades are called out first.
- Verified target: Every tag, digest, package version and checksum is confirmed against the official source before editing.
- Test before and after: The suite runs on the current version, then inside the new production image. Regressions stop the run.
- One PR per repo: Each PR carries versions, test results, runtime diffs, a risk label and a rollback plan.
The skills also encode known patching traps. Debian and Ubuntu backport fixes without changing upstream versions, so php -v can mislead. Ubuntu 24.04’s fixed package is 8.3.6-0ubuntu0.24.04.13. Digest-pinned images need a new digest. Changing Composer’s require.php patches nothing.
‘+s[1]+’
‘+s[2]+’
‘;
s[3].forEach(function(c,i){h+=’‘+c+’‘});card.innerHTML=h+’
‘;
dots.forEach(function(d,i){d.className=”dot”+(i
dots.forEach(function(d){d.onclick=function(){cur=+d.getAttribute(‘data-s’);draw()}});
function bars(on){R.querySelectorAll(‘.bug[data-w] .bar i’).forEach(function(b){b.style.width=on?b.parentNode.parentNode.getAttribute(‘data-w’)+’%’:’0′});
R.querySelectorAll(‘.seg b’).forEach(function(b){b.style.width=on?b.getAttribute(‘data-w’)+’%’:’0′})}
R.querySelectorAll(‘.bug’).forEach(function(b){b.onclick=function(){b.classList.toggle(‘open’);resize()}});
var V={php:[[“8.2.35″,”8.3.36″,”8.4.27″,”8.5.12″],”PHP 8.1 and older get no new releases. PHP published source backports for 7.4, 8.0 and 8.1. Distro packages keep old version numbers, so check the vendor changelog, not php -v.”],
node:[[“22.23.4″,”24.22.1″,”26.12.1″],”Node.js 20 and older are end-of-life and stay exploitable. They need a major upgrade to 22 or later.”],
gl:[[“19.5.1″,”19.4.3″,”19.3.6″,”19.2.9″,”19.1.9″,”19.0.10″,”18.11.13″],”Self-managed only (Omnibus, Docker, Helm, Operator). GitLab.com and GitLab Dedicated are already patched.”]};
function vers(k){var v=V[k],h=””;v[0].forEach(function(x,i){h+=’‘+x+’‘});
document.getElementById(‘mtp-dvf-vers’).innerHTML=h;document.getElementById(‘mtp-dvf-note’).textContent=v[1];
R.querySelectorAll(‘[data-r]’).forEach(function(b){b.className=”btn”+(b.getAttribute(‘data-r’)===k?’ pri’:”)});resize()}
R.querySelectorAll(‘[data-r]’).forEach(function(b){b.onclick=function(){vers(b.getAttribute(‘data-r’))}});
var A=[[“devin plugins install CognitionAI/devin-marketplace#plugins/devin-vuln-fixes”,”Or in the Devin web app: Customize, Plugins, Browse Marketplace, search Vulnerability Fixes.”],
[“npx skills add CognitionAI/devin-vuln-fixesnn# pick agents explicitlynnpx skills add CognitionAI/devin-vuln-fixes -a claude-code -a codex -a cursor”,”Requires Node.js 22.20 or later. Run npx skills update to pick up new fixed versions.”],
[“/plugin marketplace add CognitionAI/devin-vuln-fixesn/plugin install vuln-fixes@cognition-skills”,”Commands are namespaced, e.g. /vuln-fixes:fix-php-vuln.”],
[“droid plugin marketplace add https://github.com/CognitionAI/devin-vuln-fixesndroid plugin install vuln-fixes@cognition-skills”,”Agent needs git, a shell, read access to repos, Docker, and your CI’s registry or package mirror.”]];
function cmd(i){document.getElementById(‘mtp-dvf-cmd’).textContent=A[i][0];document.getElementById(‘mtp-dvf-req’).textContent=A[i][1];
R.querySelectorAll(‘[data-a]’).forEach(function(b){b.className=”btn”+(+b.getAttribute(‘data-a’)===i?’ pri’:”)});resize()}
R.querySelectorAll(‘[data-a]’).forEach(function(b){b.onclick=function(){cmd(+b.getAttribute(‘data-a’))}});
document.getElementById(‘mtp-dvf-copy’).onclick=function(){var t=document.getElementById(‘mtp-dvf-cmd’).textContent,b=this;
try{navigator.clipboard.writeText(t).then(function(){b.textContent=”Copied”;setTimeout(function(){b.textContent=”Copy”},1200)})}catch(e){}};
R.querySelectorAll(‘.tb’).forEach(function(t){t.onclick=function(){var n=t.getAttribute(‘data-t’);
R.querySelectorAll(‘.tb’).forEach(function(x){x.classList.toggle(‘on’,x===t)});
R.querySelectorAll(‘.pn’).forEach(function(p){p.classList.toggle(‘on’,p.getAttribute(‘data-p’)===n)});
bars(false);if(n===’1′)setTimeout(function(){bars(true)},60);if(n===’0′)draw();resize()}});
draw();vers(‘php’);cmd(0);
window.addEventListener(‘resize’,function(){draw()});window.addEventListener(‘load’,resize);setTimeout(resize,300);
})();


