

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    PHP shares mitigation for new RCE vulnerability with no patch

    October 24, 2026

    Yes, There Is Some Global Action on Phasing Out Fossil Fuels

    October 24, 2026

    70,000 police forces deployed in France for tense day of protests – POLITICO

    October 24, 2026
    Facebook X (Twitter) Instagram
    Trending
    • PHP shares mitigation for new RCE vulnerability with no patch
    • Yes, There Is Some Global Action on Phasing Out Fossil Fuels
    • 70,000 police forces deployed in France for tense day of protests – POLITICO
    • Between quick wins and big dreams lies Burnham’s biggest test, starting with the Budget
    • No unions, low taxes: why some of Britain’s top chefs are opening outposts in Gulf states | Restaurants
    • Stateful Agentic Engineering Copilots with Letta: Core Memory, Shared State, Semantic Retrieval, Custom Tools, Streaming, and Portable Agent Workflows
    • Quest Diagnostics confirms data breach exposed patient records
    • People are taking an unapproved weight-loss drug. AI found something surprising
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 24
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    CISA orders urgent patching of actively exploited Zimbra flaw

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKAugust 24, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies to patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days.

    The Zimbra security team patched the security flaw (tracked as CVE-2026-73570) in version 10.1.20, released on July 20.

    Successful exploitation allows unauthenticated attackers to gain remote code execution by exploiting a command injection weakness in the SNMP monitoring component when SNMP notifications are enabled on the targeted system.
    image

    “Due to improper sanitization of untrusted input during SNMP notification processing, an unauthenticated attacker can send specially crafted SMTP requests that may result in execution of arbitrary operating system commands as the Zimbra user,” it explained.

    CISA’s warning comes after CERT Polska, the Polish Computer Emergency Response Team (CERT), first flagged the vulnerability as targeted in the wild last Monday.

    While threat security watchdog Shadowserver tracks more than 12,000 Zimbra servers exposed on the Internet, there is no information on how many are honeypots or have already been secured against attacks exploiting the CVE-2026-73570 flaw.
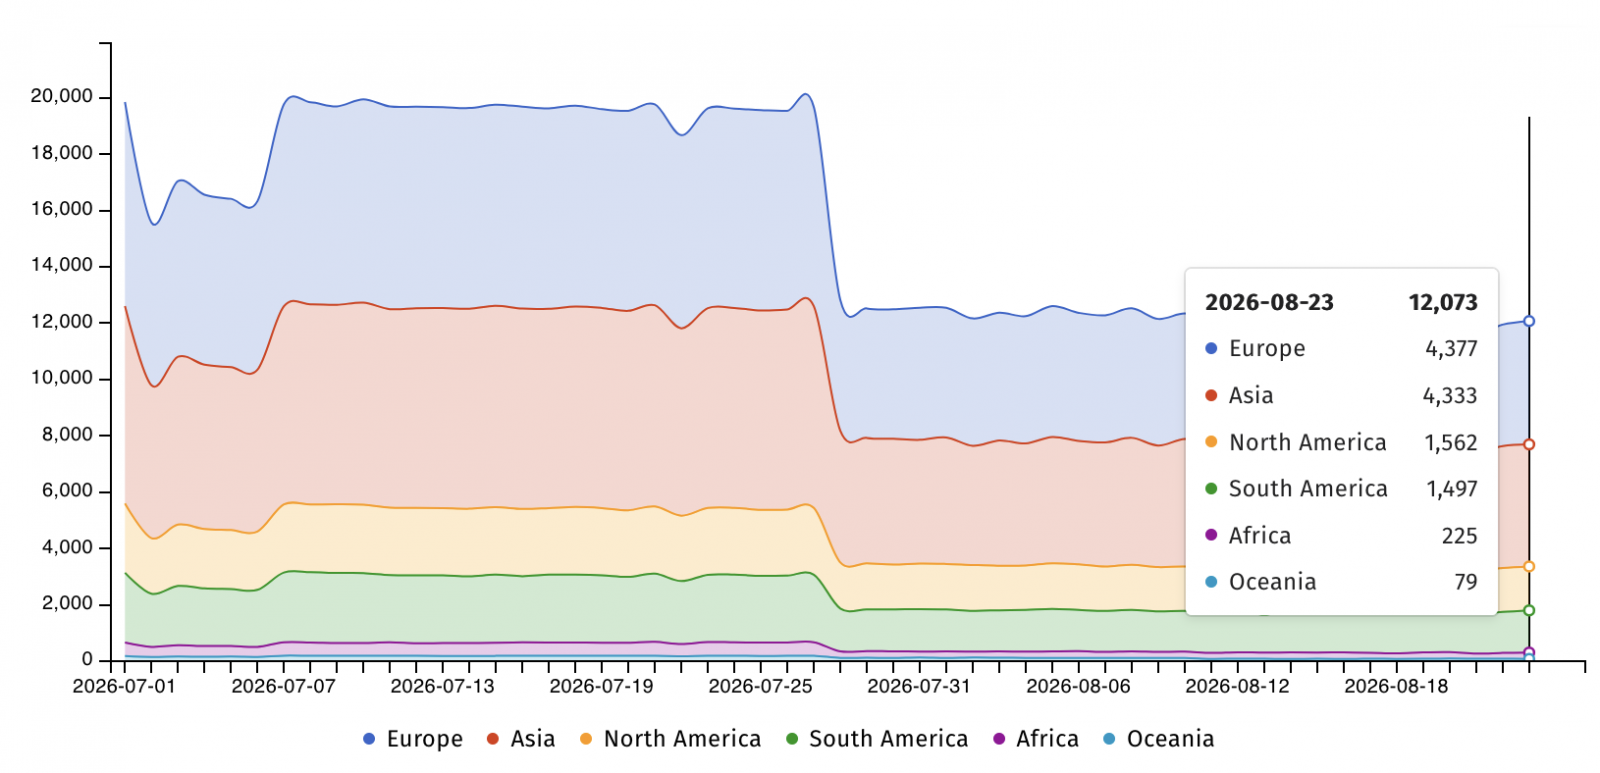
    Zimbra Collaboration Suite servers exposed online
    Zimbra Collaboration Suite servers exposed online (Shadowserver)

    ​On Friday, CISA confirmed CERT Polska’s alert, added the flaw to its KEV catalog, and ordered U.S. Federal Civilian Executive Branch (FCEB) agencies to secure their systems within three days, by August 24.

    Although CISA didn’t share any information on these ongoing attacks, the Polish CERT team asked security teams to check logs for suspicious activity, such as the Zimbra service restarting unexpectedly, and for files created in the /opt/zimbra/jetty/webapps/, /opt/zimbra/jetty_base/webapps/, and /tmp/ folders by user zimbra over the last 30 days.

    ZCS is a popular email and collaboration suite used by hundreds of millions of organizations and people worldwide, including hundreds of government agencies and thousands of businesses.

    Zimbra security issues are commonly targeted in the wild and have been used to steal sensitive data from vulnerable email servers in recent years.

    Most recently, Seqrite Labs researchers revealed in March that APT28 (a state-sponsored threat group linked to Russia’s military intelligence service) was exploiting a stored cross-site scripting (XSS) vulnerability in attacks targeting Ukrainian government ZCS servers.

    In October 2024, U.S. and UK cyber agencies warned that APT29 hackers (tracked as Midnight Blizzard and Cozy Bear) linked to Russia’s Foreign Intelligence Service were targeting Zimbra servers using a flaw previously exploited to steal email account credentials.

    Russian Winter Vivern cyber spies have also abused a reflected Cross-Site Scripting (XSS) vulnerability to steal emails belonging to NATO-aligned individuals and organizations via Zimbra webmail portals.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    actively CISA Exploited Flaw orders Patching urgent Zimbra
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    PHP shares mitigation for new RCE vulnerability with no patch

    Quest Diagnostics confirms data breach exposed patient records

    Researchers Push Over 2 Million Updates to Remotely Disable Popcorn Time Updater That Could Fuel a Botnet

    Atlassian Patches 75 Flaws in Data Center and Server Products

    Microsoft Teams to get AI-powered, context-aware phishing detection

    CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloud

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    PHP shares mitigation for new RCE vulnerability with no patch

    October 24, 2026

    Yes, There Is Some Global Action on Phasing Out Fossil Fuels

    October 24, 2026

    70,000 police forces deployed in France for tense day of protests – POLITICO

    October 24, 2026

    Between quick wins and big dreams lies Burnham’s biggest test, starting with the Budget

    October 24, 2026
    Latest Posts

    ‘This is hell’: British widow ‘sick’ with worry over threat of being removed from Sweden | Sweden

    August 14, 2026

    Prichard Colon dies from boxing injury that resulted in 221-day coma | Boxing News

    August 14, 2026

    Weather forecasts once gave Britons something safe to chat about. Not any more | Andy Beckett

    August 14, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    PHP shares mitigation for new RCE vulnerability with no patch

    October 24, 2026

    Yes, There Is Some Global Action on Phasing Out Fossil Fuels

    October 24, 2026

    70,000 police forces deployed in France for tense day of protests – POLITICO

    October 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.