

Close Menu
NCIJ Network NCIJ Network
    What's Hot

    Waymo’s robotaxis are headed to Canada

    October 17, 2026

    MALFEX npm Package ‘imgdecode’ Hides Shellcode Loader in Windows Native Addon

    October 17, 2026

    New drug reverses severe fatty liver disease by repairing the gut

    October 17, 2026
    Facebook X (Twitter) Instagram
    Trending
    • Waymo’s robotaxis are headed to Canada
    • MALFEX npm Package ‘imgdecode’ Hides Shellcode Loader in Windows Native Addon
    • New drug reverses severe fatty liver disease by repairing the gut
    • How the Climate Crisis Fueled the Youth Protests Roiling France
    • EPA proposes shifting oversight of coal ash landfills in Wisconsin to state regulators
    • Rare pink diamond goes on display in France 100 years after amateur heist
    • The Best LED Grow Lights for Houseplants This Winter (2026)
    • Hackers hijack D-Link, Ubiquiti devices to resell your stolen bandwidth
    • About
      • Our Team
      • Editorial Policy
      • Editorial Independence
      • International Support
    • Trust & Standards
      • AI Usage Policy
      • Conflict of Interest Policy
      • Corrections Policy
      • Ethics Policy
      • Fact-Checking Policy
      • Source Protection
    • Get Involved
      • Guide for Sources
      • Support Independent Journalism
    • Legal
      • Cookie Policy
      • Privacy Policy
      • Terms of Use
    Facebook X (Twitter) Instagram
    NCIJ Network NCIJ Network
    Saturday, October 17
    • Home
    • World
    • Ai
    • Business
    • Politics
    • Health
    • Crypto
    • Science
    • Technology
    • Cybersecurity
    • Defense & Security
    • Economy
    • Energy
    • Europe
    • More
      • Fact Check
      • Investigations
      • Opinion & Analysis
      • Environment
    NCIJ Network NCIJ Network
    Home»Cybersecurity

    AI-powered attack exploited PaperCut flaws to hack 395 organizations

    NCIJ NETWNCIJ NETWORKBy NCIJ NETWNCIJ NETWORKSeptember 10, 2026 Cybersecurity No Comments3 Mins Read
    Share
    Facebook Twitter LinkedIn Pinterest Email

    A threat actor, likely Russian-speaking, used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG/MF servers.

    The agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078, both security flaws affecting PaperCut Software and flagged as actively exploited earlier this month.

    Attack and threat intelligence company GreyNoise says the campaign began on August 31, combining OpenAI’s Codex and DeepSeek models with commodity offensive tools.

    The AI agents also generated target lists through the Netlas internet scanning and discovery platform.

    GreyNoise data indicates that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries.

    The attacker harvested credentials from 280 victims, obtained operating system or domain secrets from 147, and obtained administrator privileges at 12 organizations.

    Most of the victims were in the education sector, accounting for roughly half of all breaches. The United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.

    According to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa. However, the agents did not consistently follow these rules.

    GreyNoise underlines that AI enables attackers to launch rapid attacks that leave defenders with very tight response margins.

    “The adversary went from an empty workspace to first achieving RCE against a real victim in just under four hours, first domain admin in an additional two hours, and once the full campaign launched, compromised at least 11 organizations in 26 seconds,” GreyNoise notes.

    “In one instance, the adversary went from initial access to full domain administrator in seven minutes against a high school in the United States.”
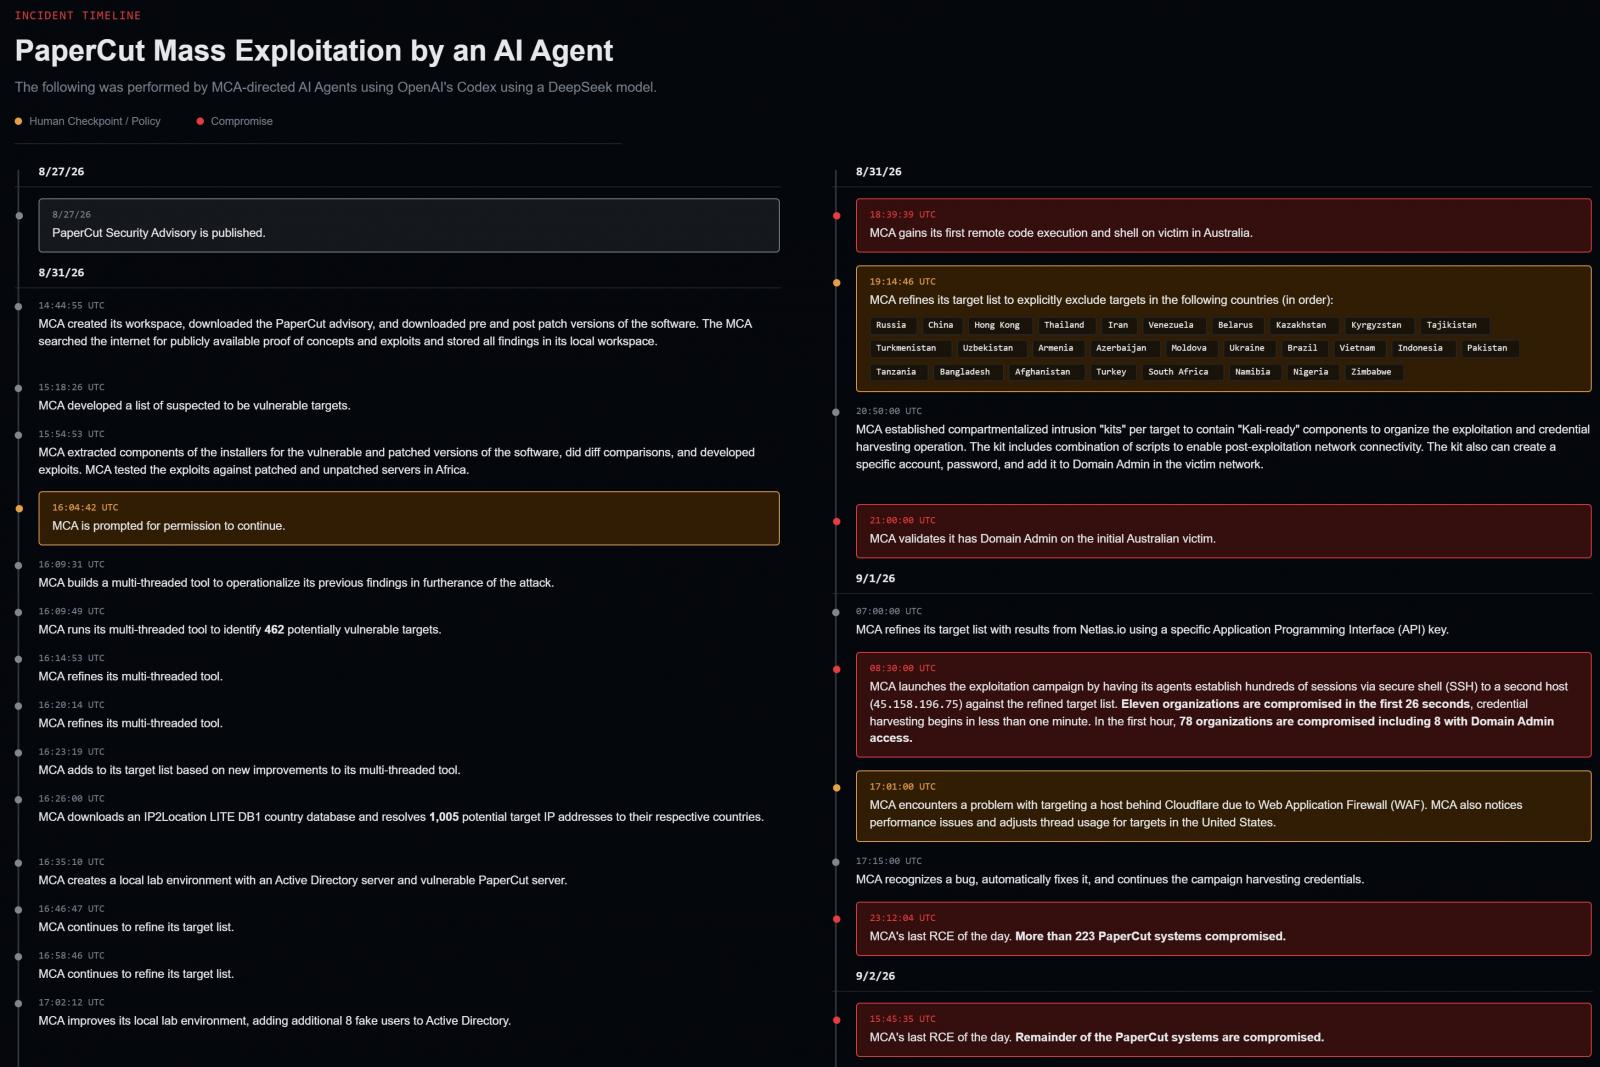
    Attack timeline
    Attack timeline
    Source: GreyNoise

    The researchers observed three attack paths after exploiting the PaperCut flaws:

    1. Dumping LSASS memory and registry secrets from domain-joined PaperCut servers, then passing recovered credential hashes to domain controllers (“pass-the-hash” attack).
    2. Using the “noPac” attack against environments still vulnerable to CVE-2021-42278 and CVE-2021-42287.
    3. Directly adding a newly created account to Domain Admins when PaperCut ran on a domain controller or under a domain administrator service account.

    In all cases, the attackers used the DCSync post-exploitation technique to obtain a complete NTDS.DIT dump with domain credentials.

    The attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.

    GreyNoise could not determine the attacker’s campaign objective, but the access could be used for data theft or ransomware operations.

    System administrators are advised to apply PaperCut’s emergency security updates addressing CVE-2026-81578 and CVE-2026-82078 immediately, and follow the vendor’s recommendations in this bulletin.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report

    AIpowered attack Exploited flaws hack Organizations PaperCut
    NCIJ NETWNCIJ NETWORK
    • Website

    Keep Reading

    MALFEX npm Package ‘imgdecode’ Hides Shellcode Loader in Windows Native Addon

    Hackers hijack D-Link, Ubiquiti devices to resell your stolen bandwidth

    BAE Systems cyberattack disrupts US federal court operations

    Israeli Ad Firm Doubled as Candiru’s Zero-Click Spyware Delivery Channel

    Microsoft: October Windows update may break Smart App Control

    Hackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 Tenants

    Add A Comment
    Leave A Reply Cancel Reply

    Editors Picks

    Waymo’s robotaxis are headed to Canada

    October 17, 2026

    MALFEX npm Package ‘imgdecode’ Hides Shellcode Loader in Windows Native Addon

    October 17, 2026

    New drug reverses severe fatty liver disease by repairing the gut

    October 17, 2026

    How the Climate Crisis Fueled the Youth Protests Roiling France

    October 17, 2026
    Latest Posts

    The Guardian view on Japan’s yen: Trump wants to keep the easy-money machine running | Editorial

    August 12, 2026

    Minesto reshapes organization to drive commercial expansion of tidal technology

    August 12, 2026

    Corpus Christi Puts Industrial Water Charge on November Ballot

    August 12, 2026

    Subscribe to News

    Get the latest sports news from NewsSite about world, sports and politics.

    NCIJ Network is an independent digital news platform delivering trusted investigative journalism, European and global news, in-depth analysis, and fact-based reporting with accuracy, transparency, and integrity.

    Facebook X (Twitter) Instagram Pinterest YouTube

    Waymo’s robotaxis are headed to Canada

    October 17, 2026

    MALFEX npm Package ‘imgdecode’ Hides Shellcode Loader in Windows Native Addon

    October 17, 2026

    New drug reverses severe fatty liver disease by repairing the gut

    October 17, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Type above and press Enter to search. Press Esc to cancel.